
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
272 results
CVE-2021-44827 preview

CVE-2021-44827

GitHubfull-disclosure/cve-2021-44827

Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…

embedded-systems-securityexploitationhardware-iot-security+4
4
4 years ago
f_hid-4.14-backports preview

f_hid-4.14-backports

GitHubjakestone594/f_hid-4.14-backports

Backports of three published f_hid fixes (incl. CVE-2026-31721, CVE-2026-31606) to an EOL Linux 4.14.190 Android vendor kernel, with on-device…

android-securityembedded-systems-securityhardware-iot-security+1
17 days ago
ane preview

ane

GitHubeiln/ane

Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…

ai-securitybinary-analysisembedded-systems-security+3
5072 years ago
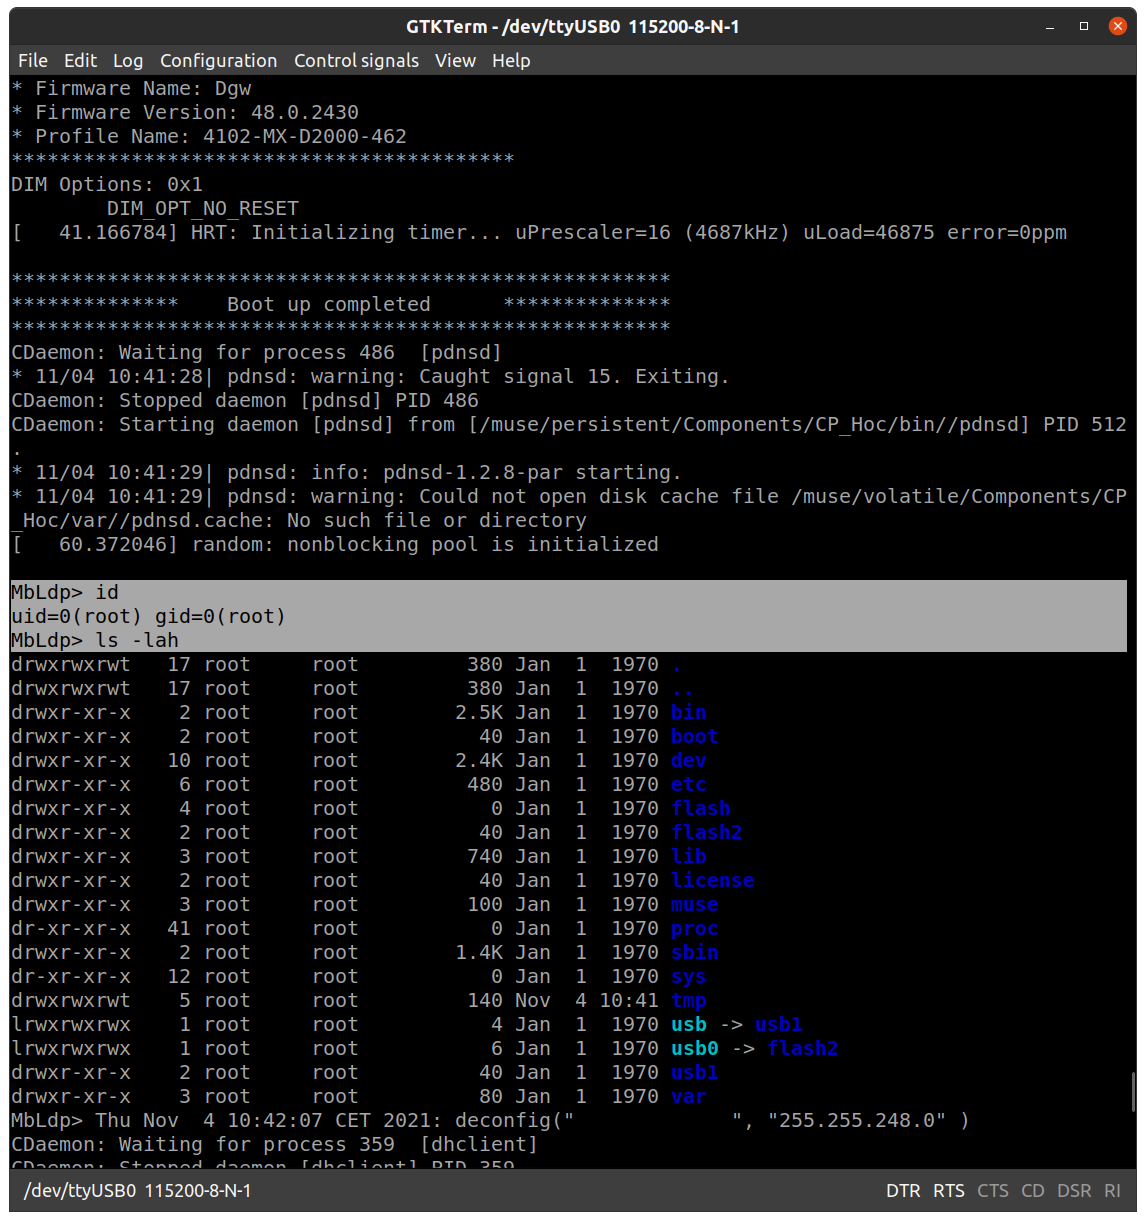
Mediatrix-CVE-2022-43096 preview

Mediatrix-CVE-2022-43096

GitHubproxystaffy/mediatrix-cve-2022-43096

Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.

embedded-systems-securityexploitationhardware-security+3
13 years ago
PoC_CVE-2025-48507 preview

PoC_CVE-2025-48507

GitHubjdbonfils/poc_cve-2025-48507

Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

binary-exploitationembedded-systems-securityexploitation+5
210 months ago
CVE-2024-33676 preview

CVE-2024-33676

GitHubdersecure/cve-2024-33676

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

authentication-authorizationeducationembedded-systems-security+9
1 year ago
Zhilly preview

Zhilly

GitLabsacriphanius/zhilly

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

embedded-systems-securityhardware-hackingiot-security+6
21 month ago
lights-out preview

lights-out

GitHubxairy/lights-out

Tools for controlling webcam LED on ThinkPad X230

embedded-systems-securityexploitationfirmware-analysis+3
5041 year ago
signy preview

signy

GitHubgolioth/signy

Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…

authentication-authorizationcryptographyembedded-systems-security+3
705 months ago
tesla-security-research preview

tesla-security-research

GitHubanalyticeth/tesla-security-research

Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…

command-and-controldata-exfiltrationeducation+7
53 months ago
CVE-2024-5633 preview

CVE-2024-5633

GitHubadikso/cve-2024-5633

PoC for CVE-2024-5633

binary-analysisembedded-systems-securityexploitation+3
12 years ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

embedded-systems-securityexploitationiot-security+3
21 year ago
nec_aterm_tools preview

nec_aterm_tools

GitHubinfobyte/nec_aterm_tools

Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.

embedded-systems-securityexploitationfirmware-analysis+4
34 years ago
CVE-2025-69821-Beat-XP-Vega-Smartwatch-Security-Assessment preview

CVE-2025-69821-Beat-XP-Vega-Smartwatch-Security-Assessment

GitHubcipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment

A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…

bluetooth-securityembedded-systems-securityexploitation+6
5 months ago
CVE-2026-23004-Automotive-UDS-Authentication-Bypass-via-Replay-Attack preview

CVE-2026-23004-Automotive-UDS-Authentication-Bypass-via-Replay-Attack

GitHubgeorge0papasotiriou/cve-2026-23004-automotive-uds-authentication-bypass-via-replay-attack

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

authentication-authorizationembedded-systems-securityexploitation+4
1 month ago
Privilege-escalation-ASKEY preview

Privilege-escalation-ASKEY

GitHubleoservalli/privilege-escalation-askey

Privilege escalation vulnerability on ASKEY routers

educationembedded-systems-securityexploitation+4
103 years ago
CVE-2023-33781 preview

CVE-2023-33781

GitHubs0tr/cve-2023-33781

Proof-of-concept exploit for CVE-2023-33781 enabling arbitrary binary execution on D-Link DIR-842V2 routers via telnet and backup/restore…

binary-exploitationembedded-systems-securityexploitation+3
16 months ago
ip-camera-research preview

ip-camera-research

GitHubamiraliuks/ip-camera-research

Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).

embedded-systems-securityexploitationexploit-frameworks+6
11 month ago
Previous12…16Next