bd-alaris-firmware-analysis

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…

PrISM: A Scalable Probabilistic RowHammer Mitigation (ISCA 2026). Ramulator2 source code and evaluation scripts.

Interactive cybersecurity scenario simulating a Tesla TPMS to VCSEC to CAN Bus attack chain, teaching vehicle security concepts through gamified…

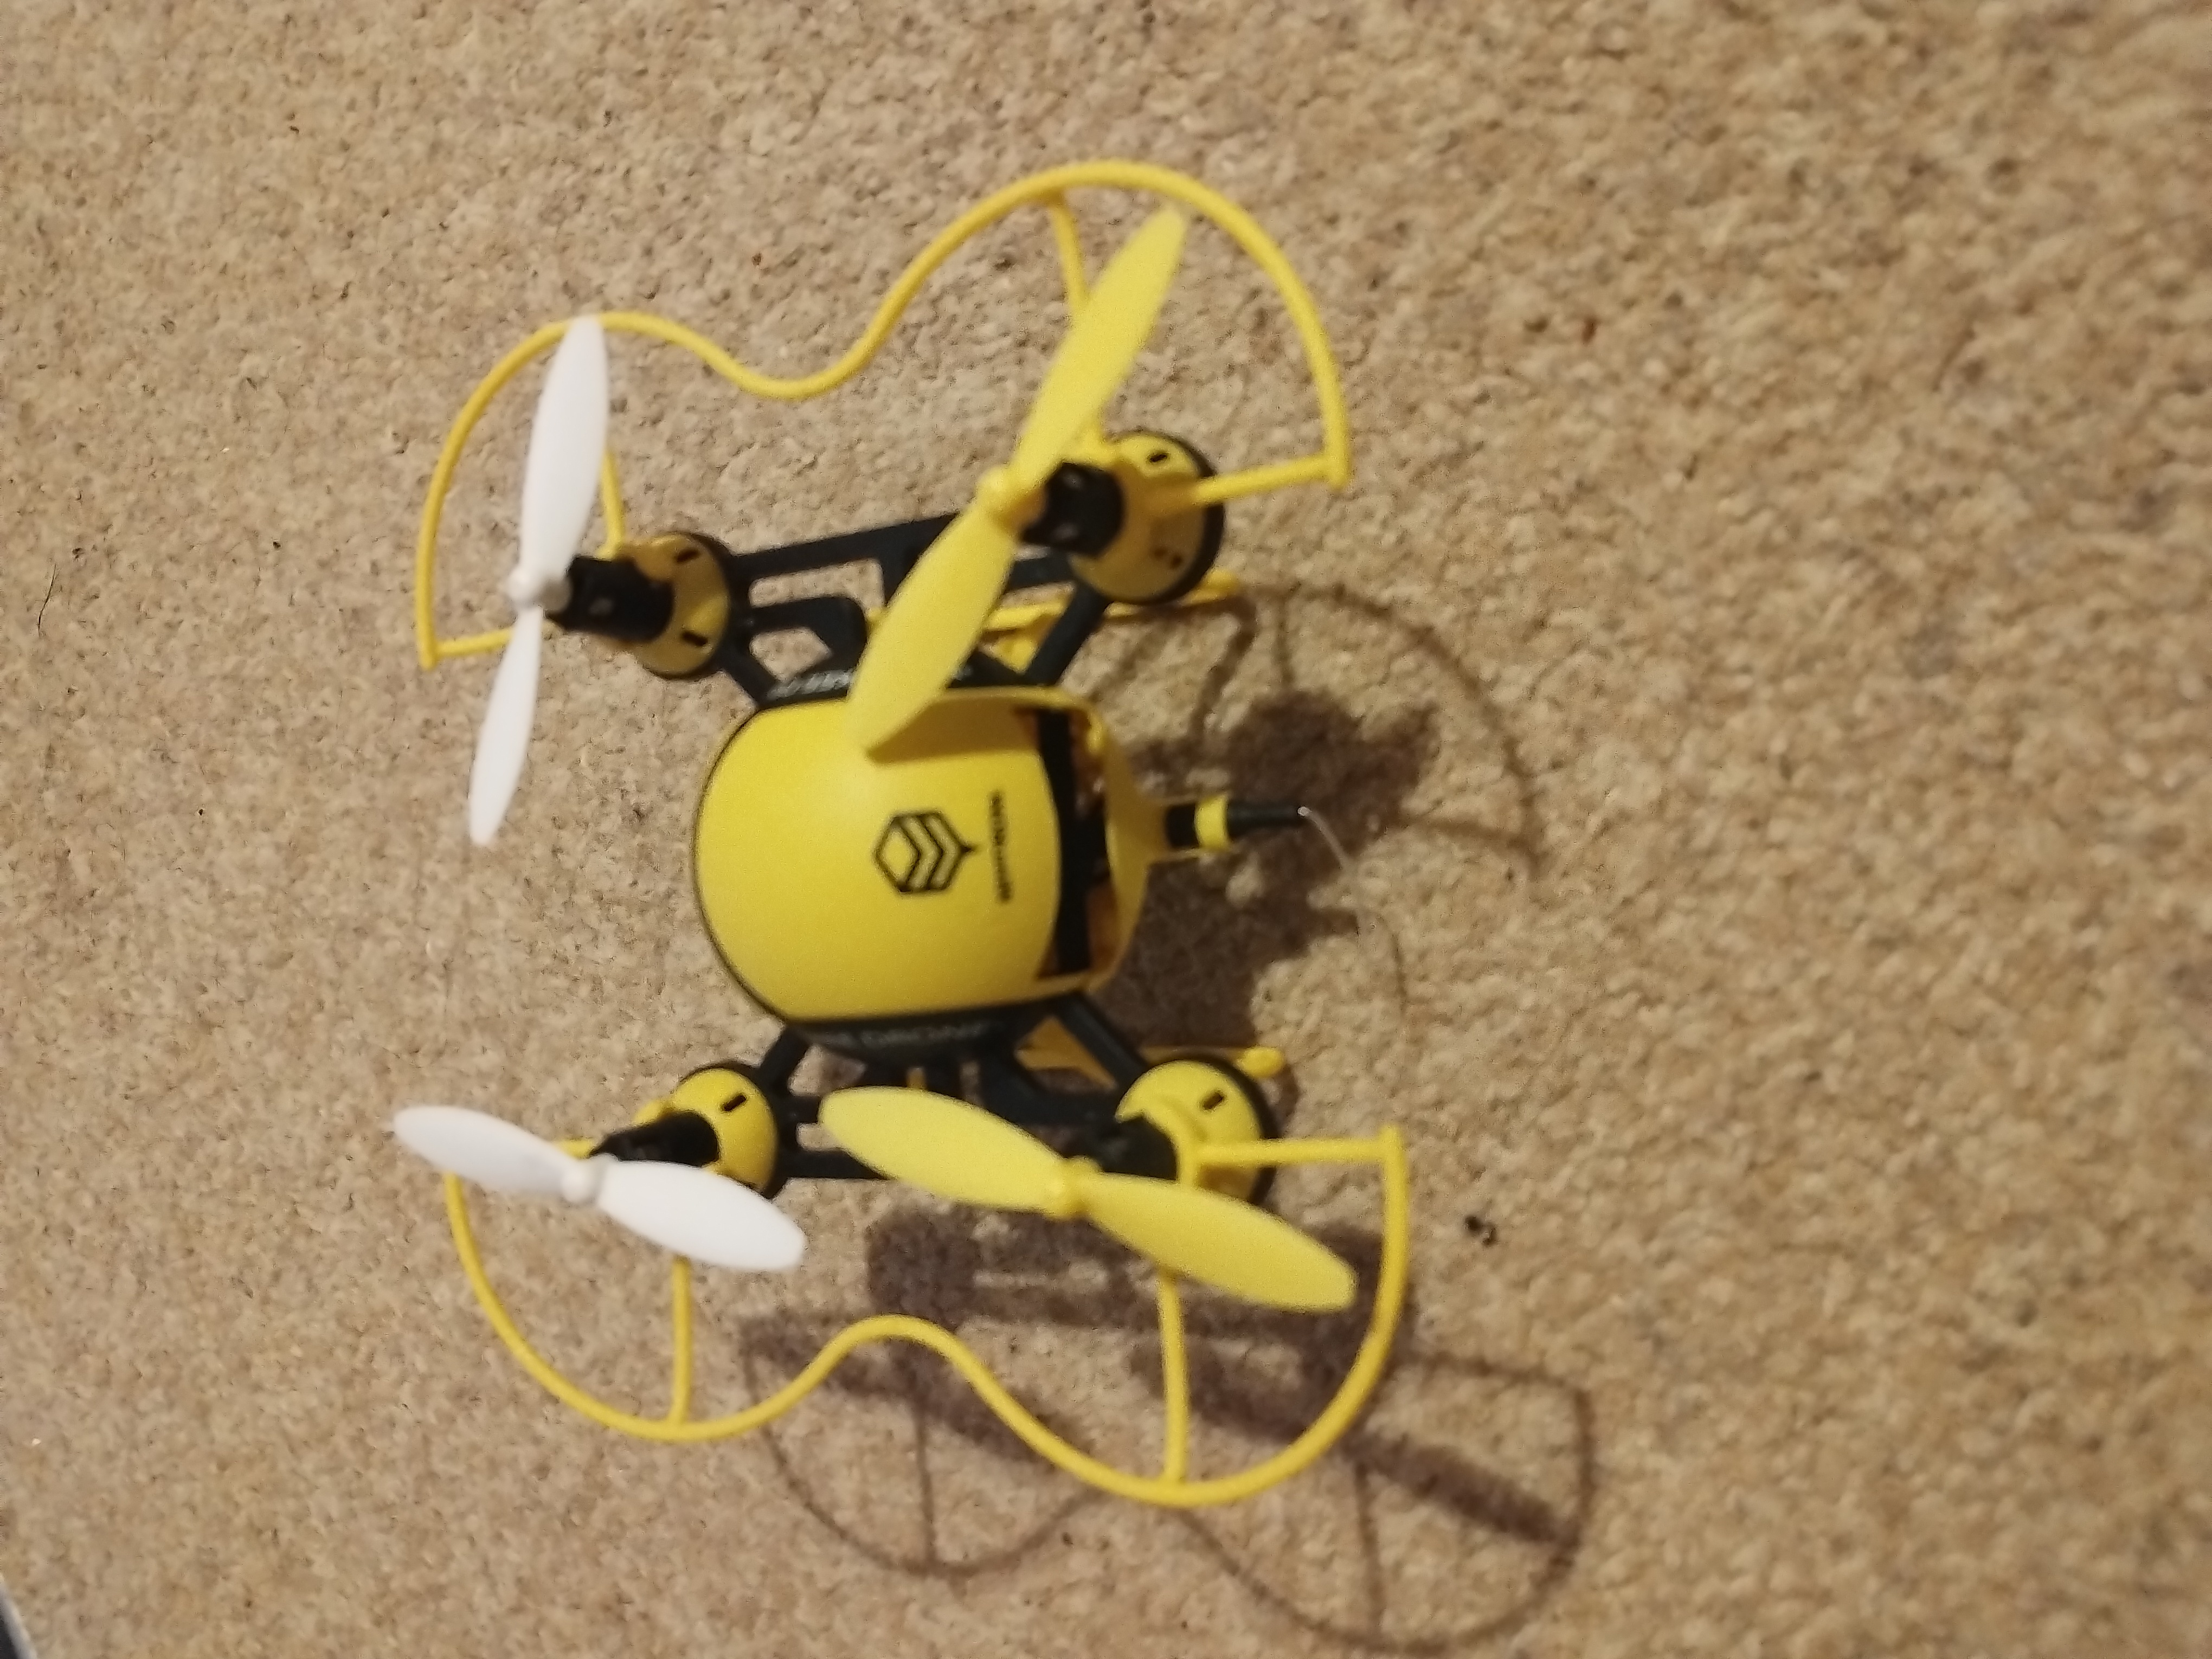
Drone HASAKEE FPV video app for Android

Scientific investigation of hardware vulnerabilities (CVE-2025-6202, CVE-2023-39910) enabling ECDSA key recovery from Bitcoin infrastructure via…

Simplifies D-Link DCS-932L firmware emulation with pre-patched components and includes a Proof-of-Concept exploit for CVE-2024-37606."

The firmware engineering home of the Cryptohack electronic badge project.

Analyzes and demonstrates the Linux kernel vulnerability CVE-2023-28772, providing a patched or vulnerable kernel source for security research and…

Python port of the Linksys tmUnblock.cgi RCE exploit

Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…

ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…

Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.

Lets have fun by digging into a Zyxel router firmware and MIPS Arch

Simulação educacional de exploração de falha em dispositivos IoT com base no CVE-2017-17761

Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.

Lets have fun by digging into a Zyxel router firmware and MIPS Arch