
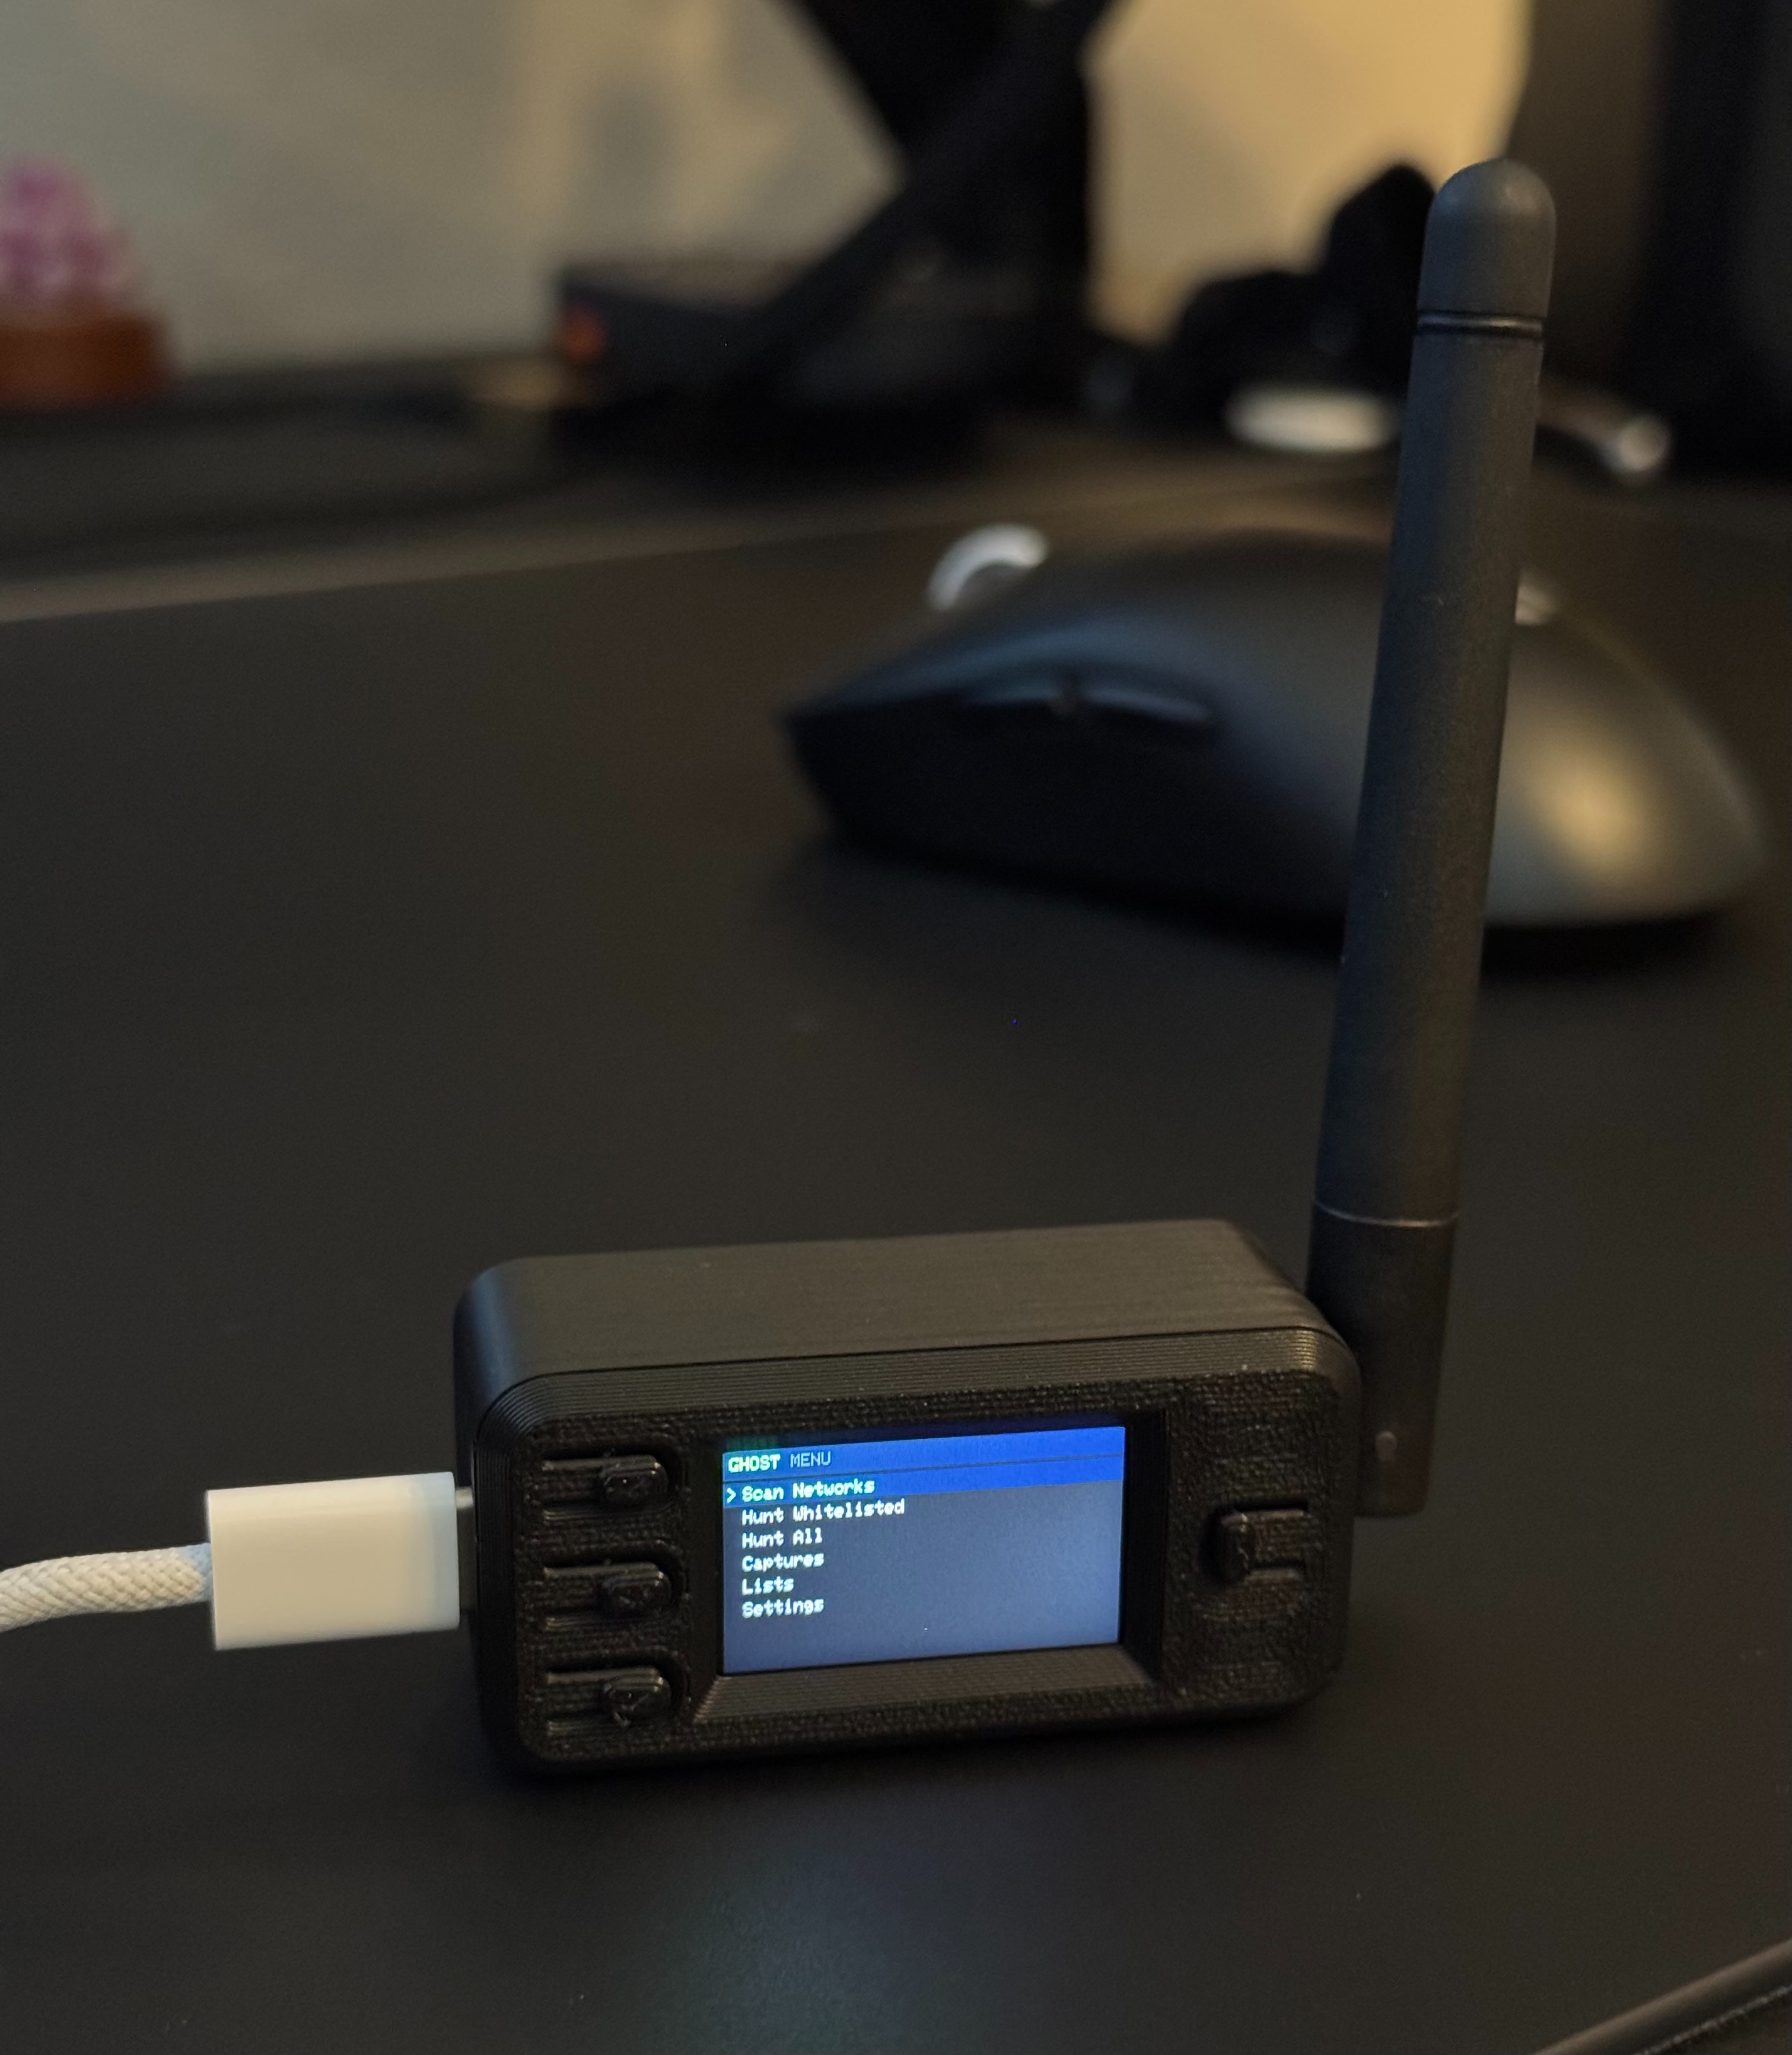
GHOST
 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
educationembedded-systems-securityhardware-iot-security+3
28
razkom/ghostESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
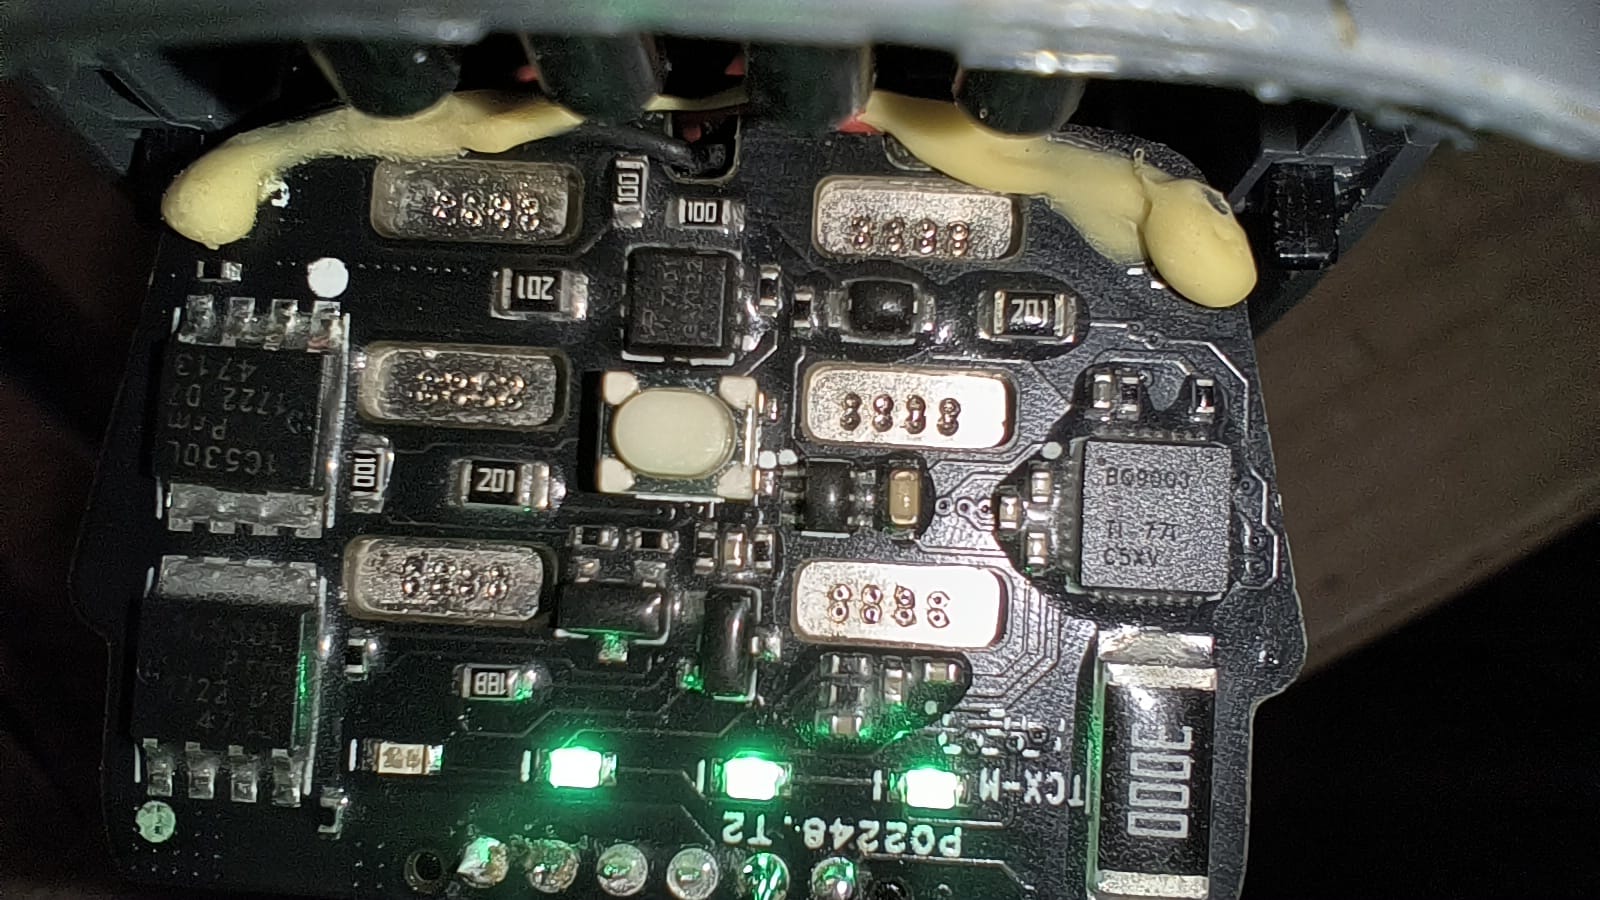 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
 hydrausb3/wch-ch56x-lib
Library for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
 tc3650/cve-2026-43499-armv7
ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…
 k-o-n-t-o-r/ghostlock-sabrina
CVE-2026-43499 GhostLock root exploit for Chromecast with Google TV (sabrina)
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 nccgroup/binja_arch_ref
A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
 makelinux/cve-2015-0235-workaround
A shared library wrapper with additional checks for vulnerable functions gethostbyname2_r gethostbyname_r (GHOST vulnerability)
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 yt2w/cve-2025-9961
Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
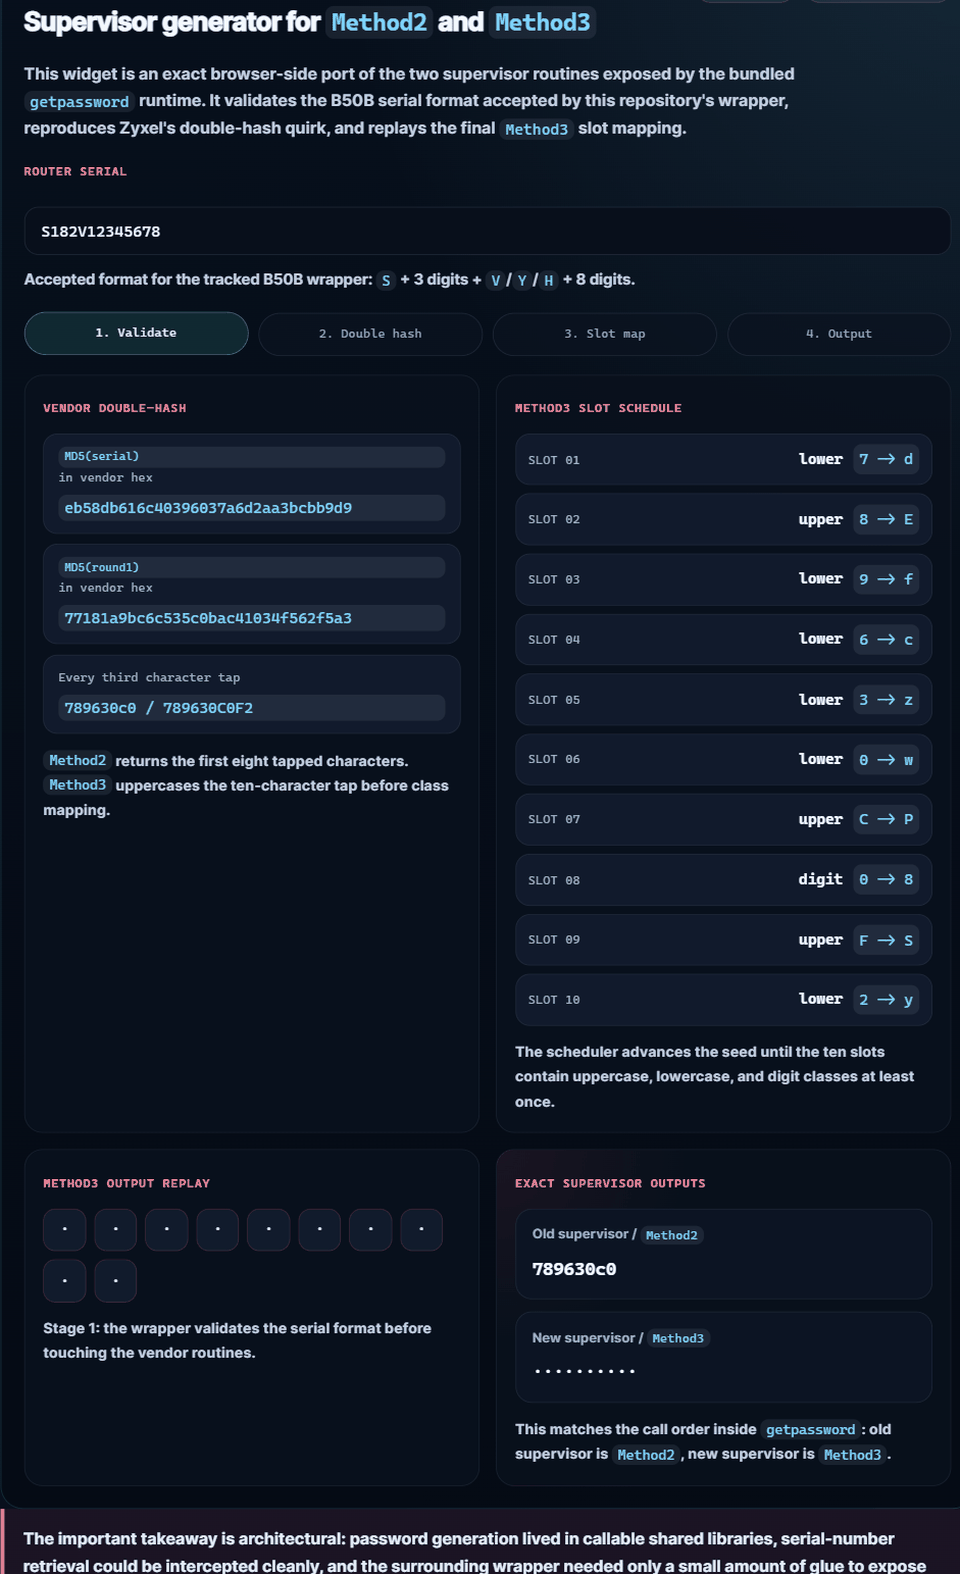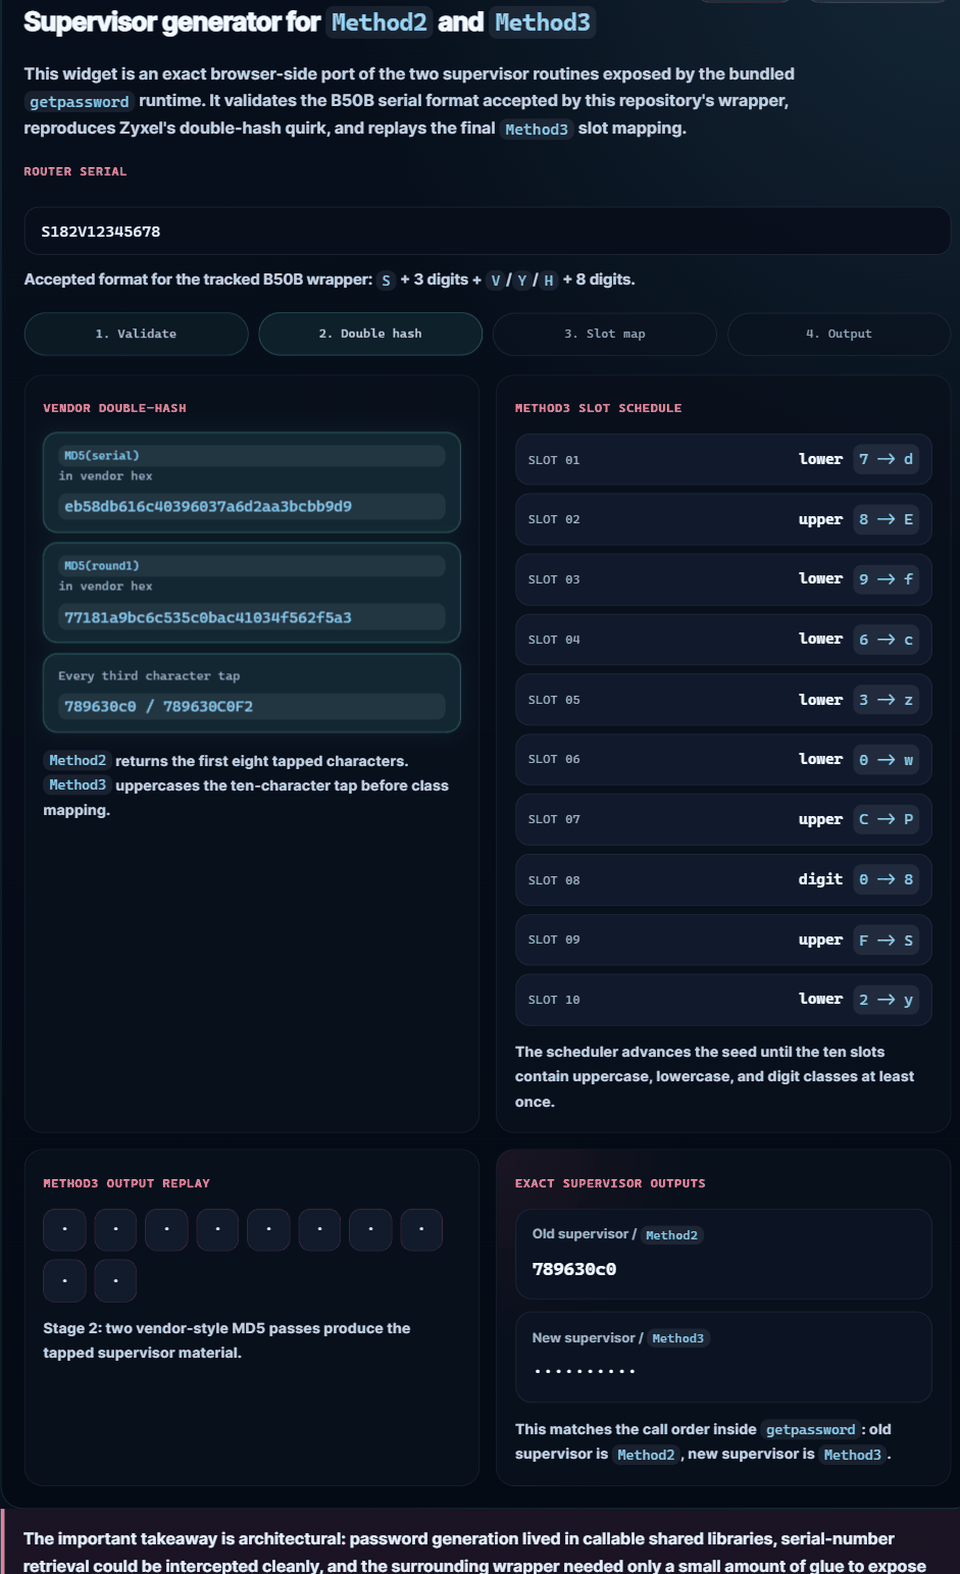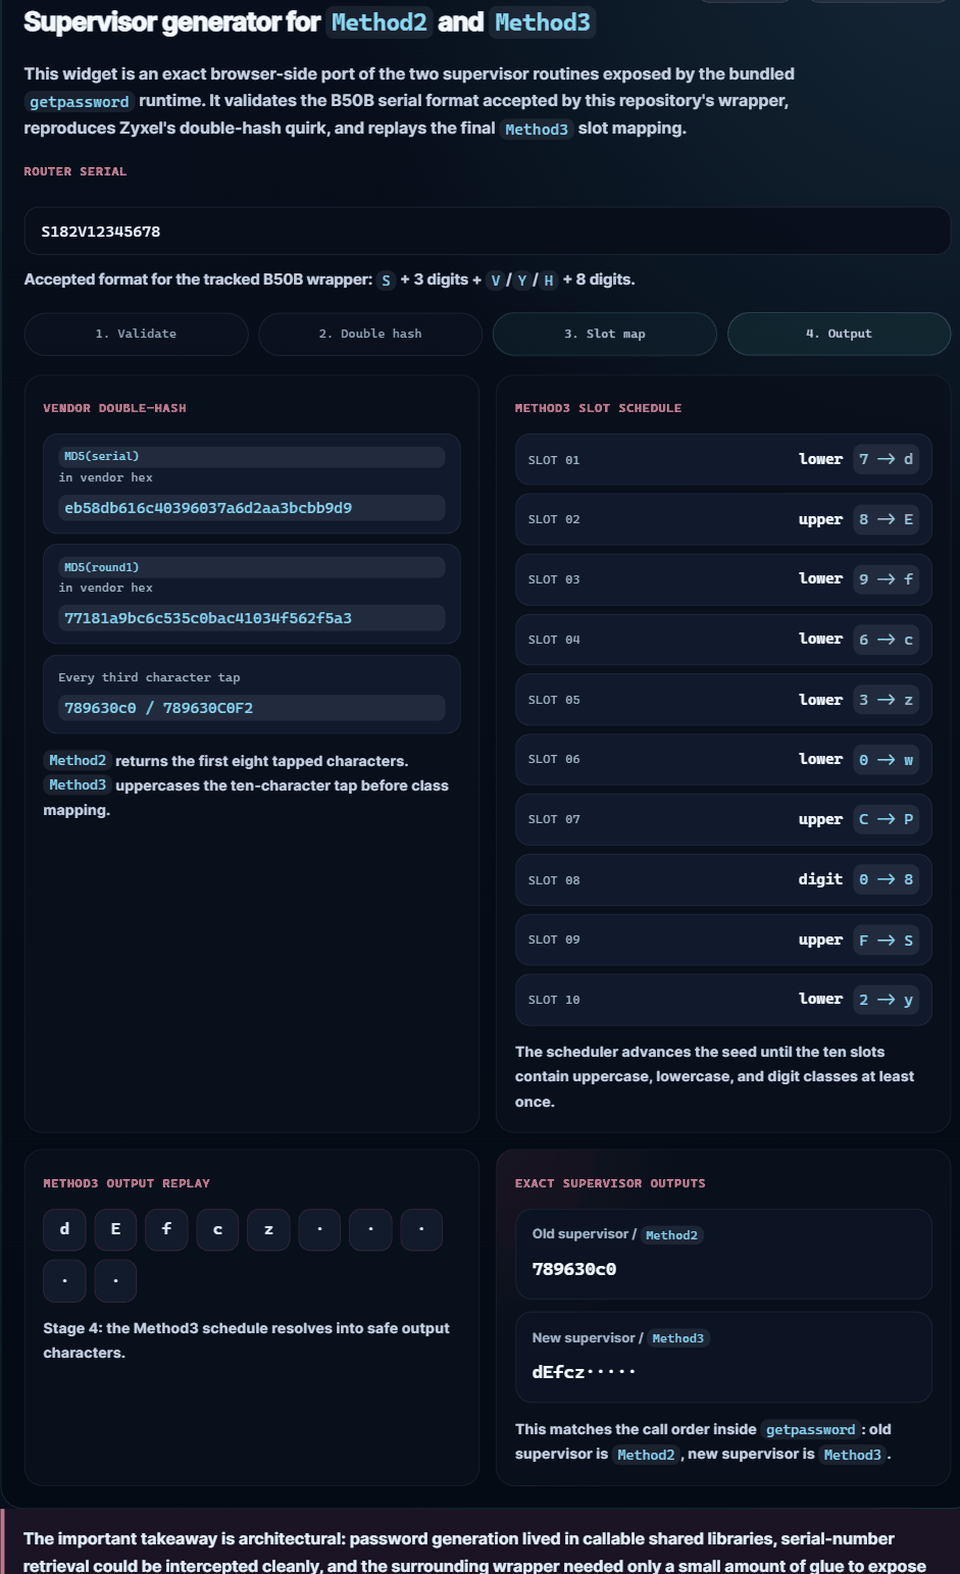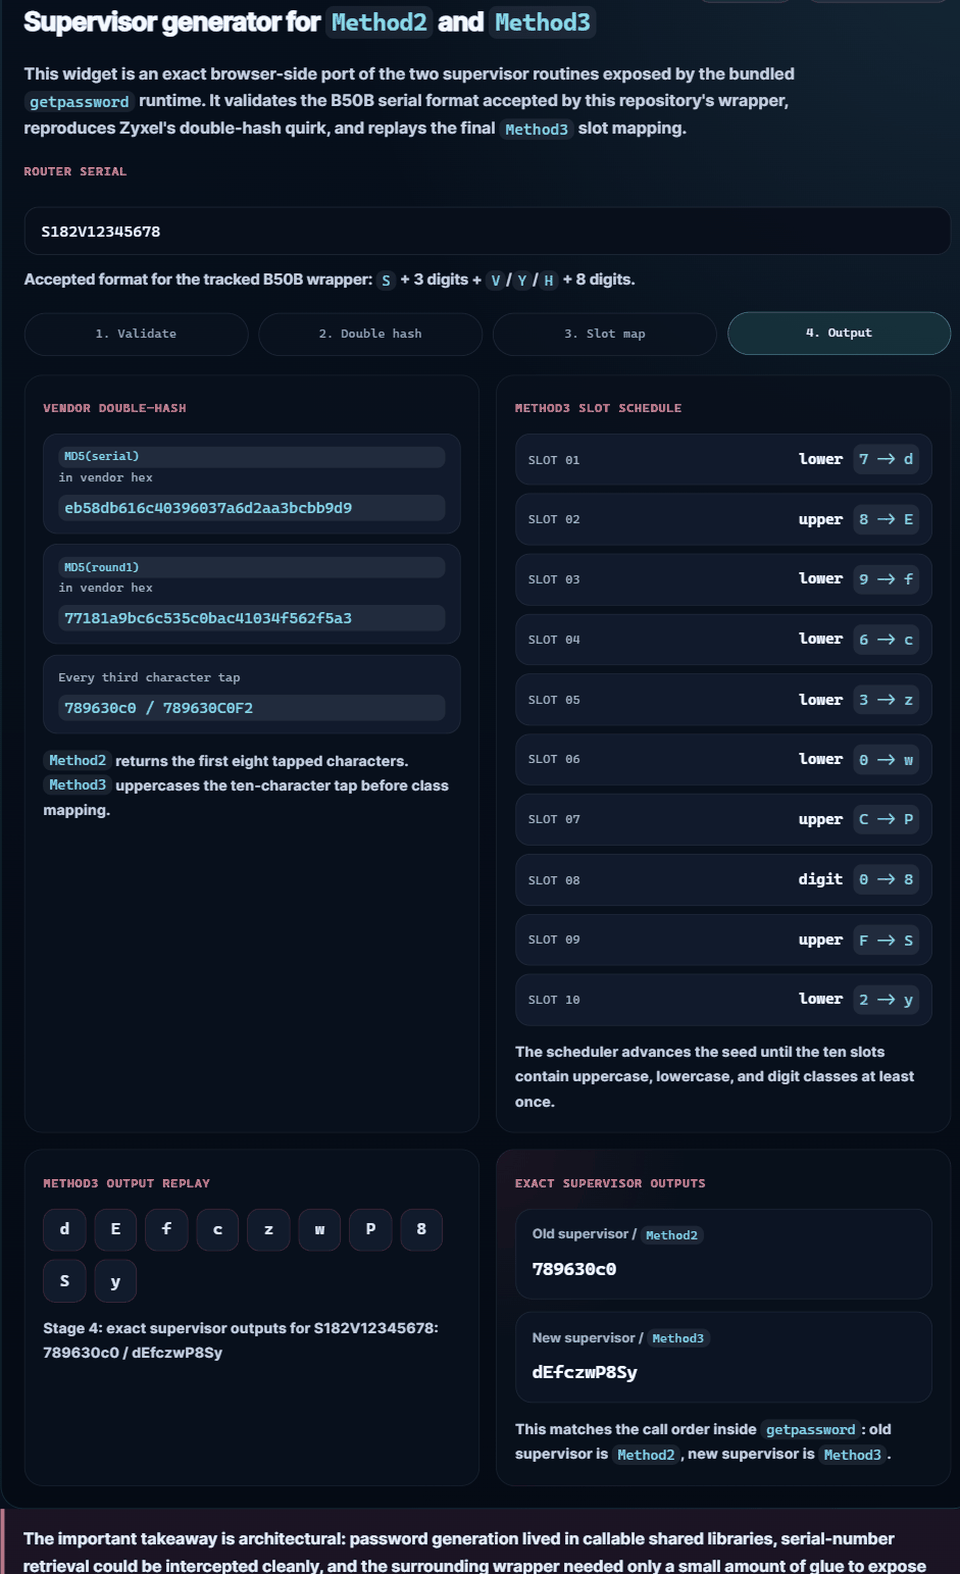 minanagehsalalma/zyxel-cve-2021-35036-super-admin-password-leak
Zyxel super-admin credential exposure write-up across CPE/ONT/LTE/5G firmware, with an adapted VMG8825-B50B genpass lab.