

cve-2016-1555
 ide0x90/cve-2016-1555
Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…
embedded-systems-securityexploitationexploit-frameworks+5
2
ide0x90/cve-2016-1555Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…
 safelock-d2e/quiksand-cve-2023-24012
Proof-of-concept demonstrating a permission bypass in ROS 2 SROS2 security framework, allowing unauthorized topic subscription via modified…
 resi-le/nxloader
An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability
 murrez/asus-aicloud-rce
SETROOTCERTIFICATE (write /etc/cert.pem.1) + APPLYAPP (RC_SERVICE execution). Refs: CVE-2025-2492, CVE-2024-12912, CVE-2025-59366; runZero;…
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 vital-information-resource-under-siege/cve-2026-38698-and-cve-2026-38699
Technical details and publication about CVE-2026-38698 and CVE-2026-38699
 pwnonu/t3-technology-cpe-advisories
CVE-2026-35904 / CVE-2026-35905 / CVE-2026-35906 — Unauth RCE, Hardcoded Root Creds & Telnet Enable in T3 Technology CPE
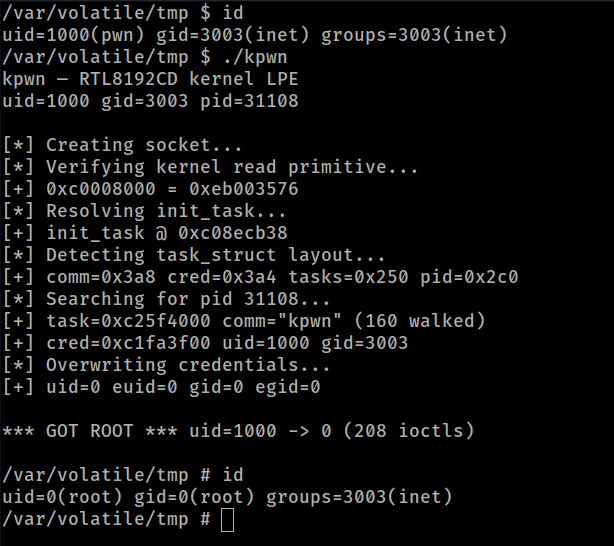 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 xernary/cve-2025-63821
Proof-of-concept of vulnerability found in Totolink A720R router
 kensh1k/cve-2026-36438
Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 yanissec/cve-2018-7849
CVE-2018-7849
 spiralbl0ck/poc
Idk Figure it out by name fuck you L$user
 yanissec/cve-2018-7845
CVE-2018-7845