

moria
 nmatt0/moria
IoT firmware identification and extraction
binary-analysisdigital-forensicsembedded-systems-security+7
nmatt0/moriaIoT firmware identification and extraction
 qkaiser/awind-research
This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 ejfkdev/reyee_decrypt
Decrypt Ruijie ReyeeOS firmware (v1/v2) and encrypted config backups; recover plaintext passwords
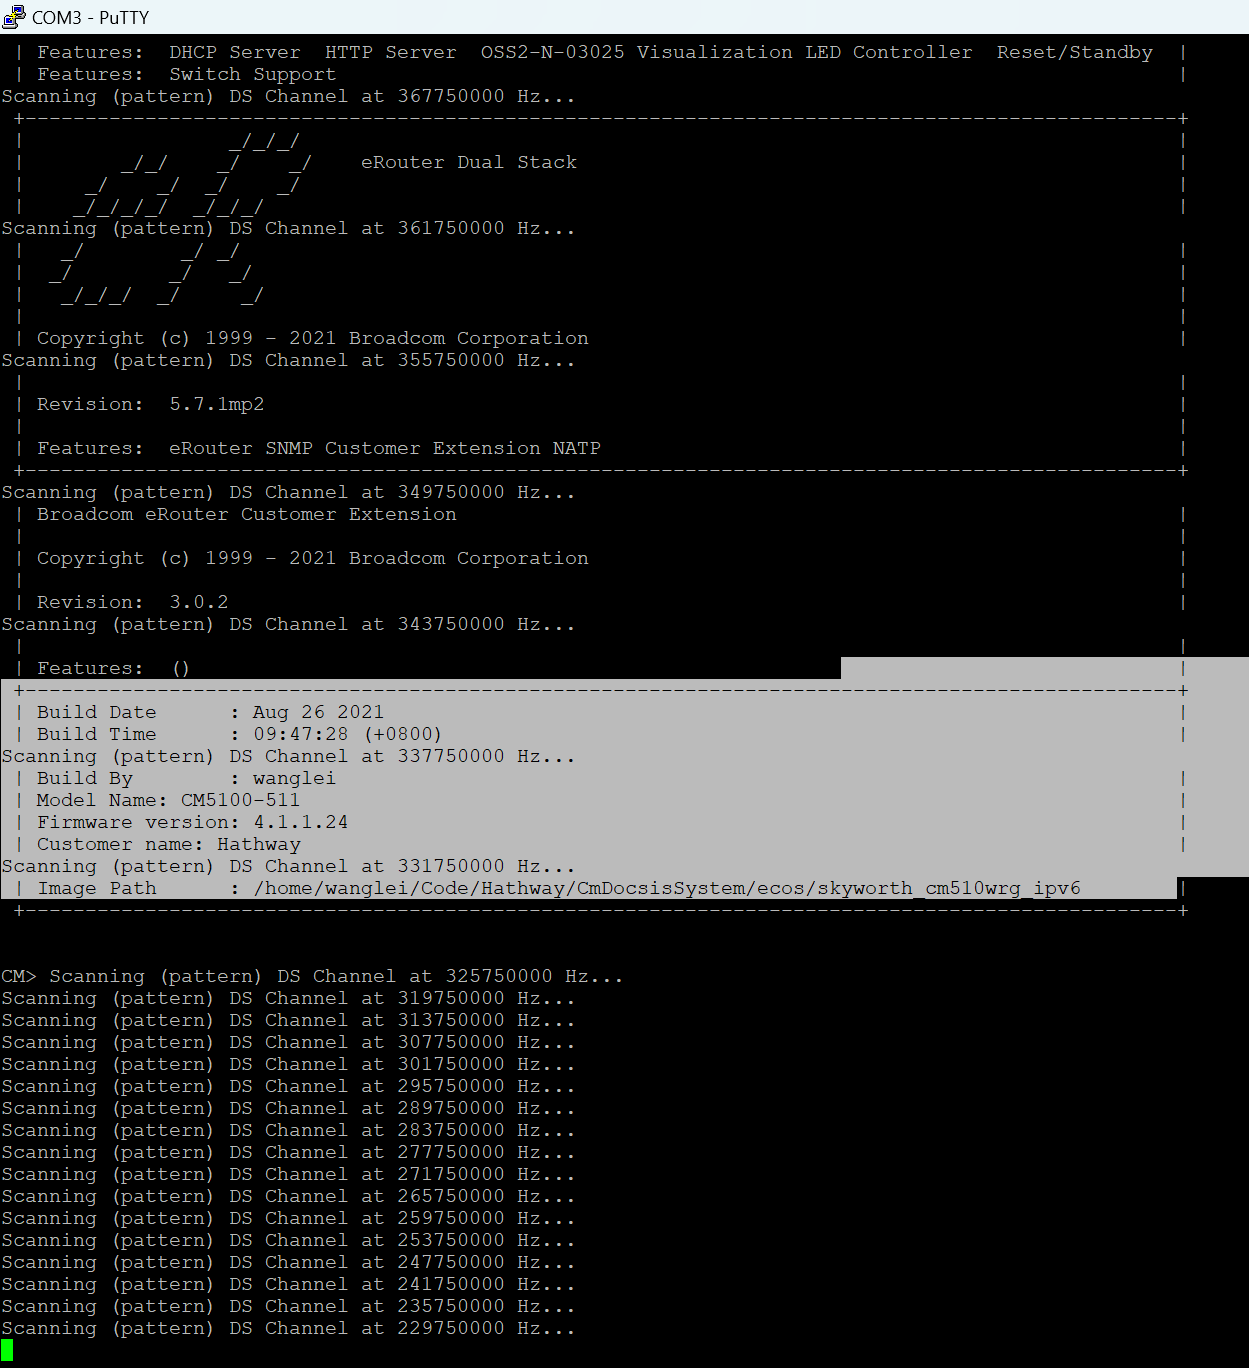 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
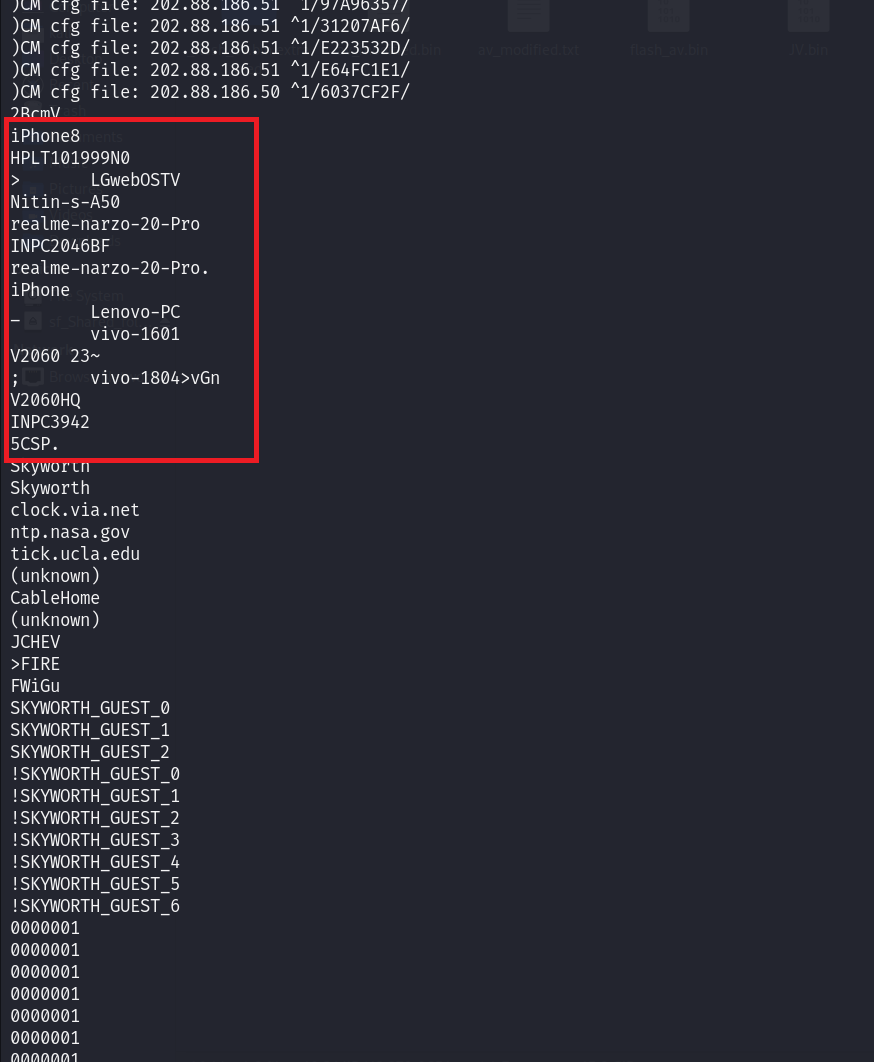 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 elvanderb/tcp-32764
some codes and notes about the backdoor listening on TCP-32764 in linksys WAG200G.
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 cantoolz/cantoolz
CANToolz - Black-box CAN network analysis framework
 luispl77/433screen-signalhacker
Full duplex 433 MHz Signal jammer, recorder, decoder and hacking multitool device based on ESP32 microcontroller and RFM69HW radios. This version of…
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
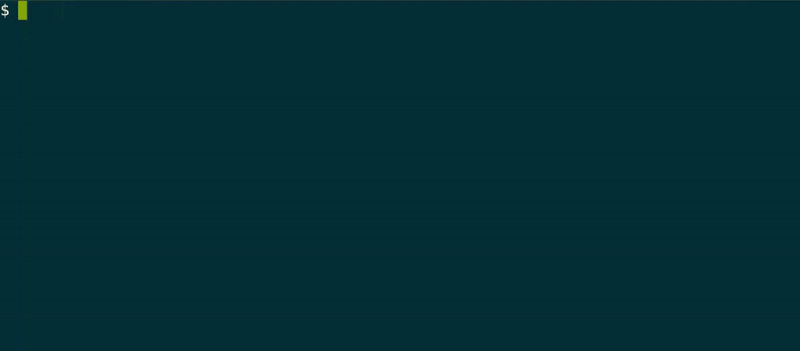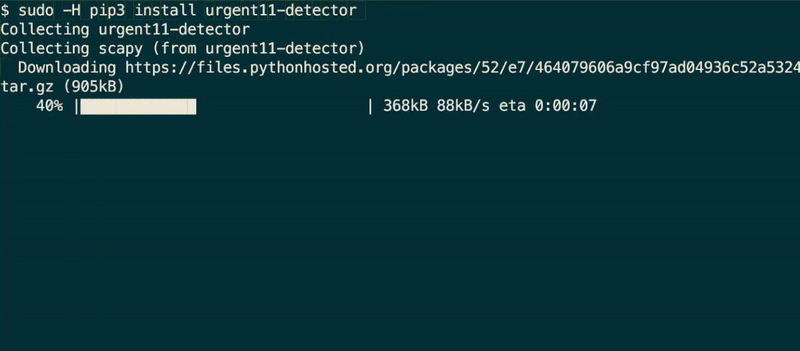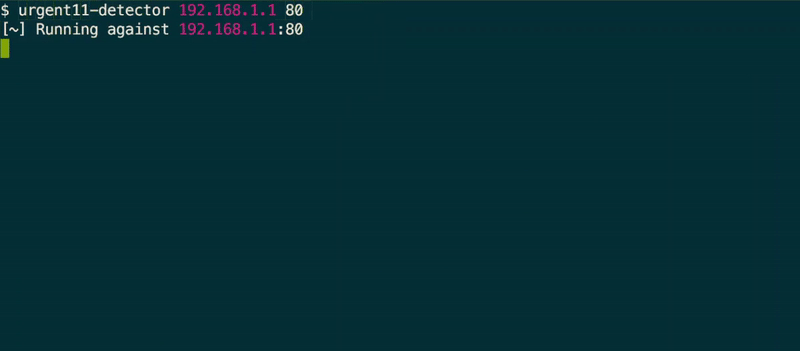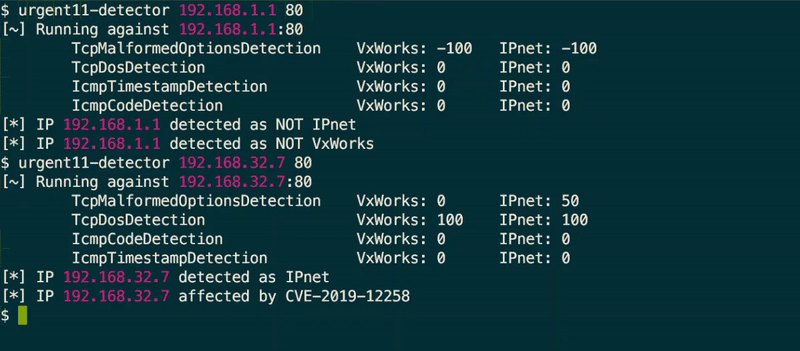 armissecurity/urgent11-detector
URGENT/11 detection tool by Armis
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…