
ESP32-Bit-Pirate
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
bluetooth-securitydebuggersembedded-systems-security+5
5.9k
geo-tp/esp32-bit-pirateA Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 yosyshq/nextpnr
nextpnr portable FPGA place and route tool
 renode/renode
Open-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
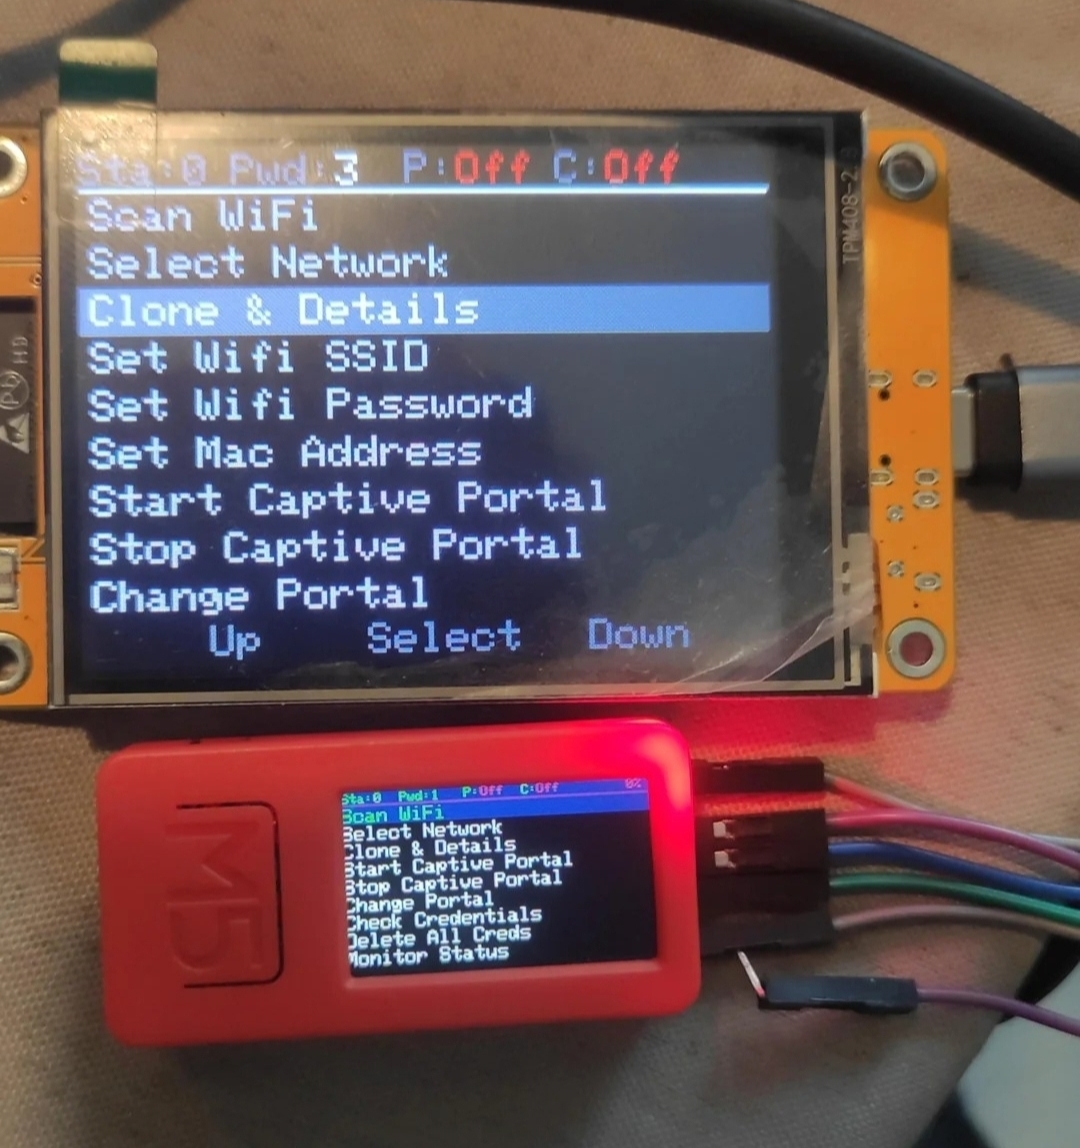 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 bkerler/mtkclient
Mediatek Flash and Repair Utility
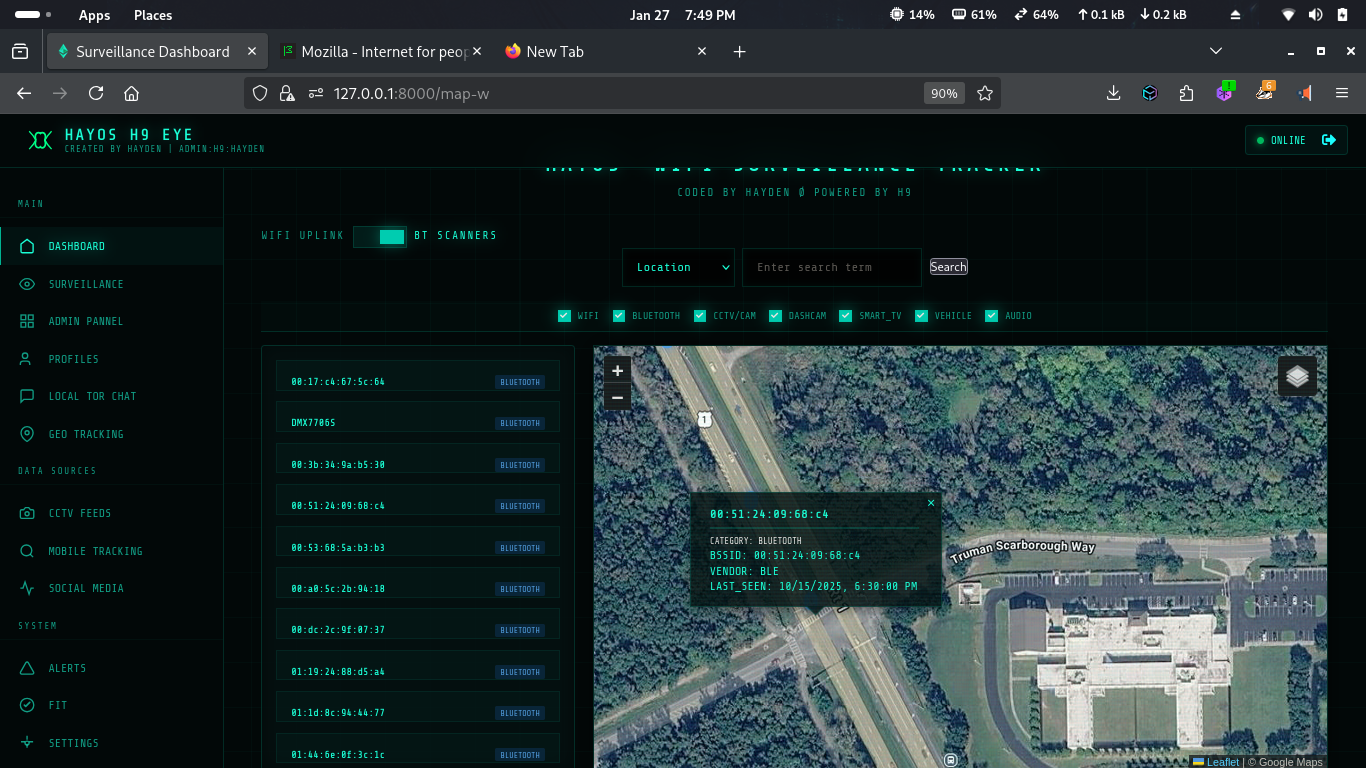 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 nikameru/nxboot
Payload injection tool for Nintendo Switch consoles vulnerable to CVE-2018-6242 ("Fusée Gelée")
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…

 george0papasotiriou/cve-2026-23004-automotive-uds-authentication-bypass-via-replay-attack
Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
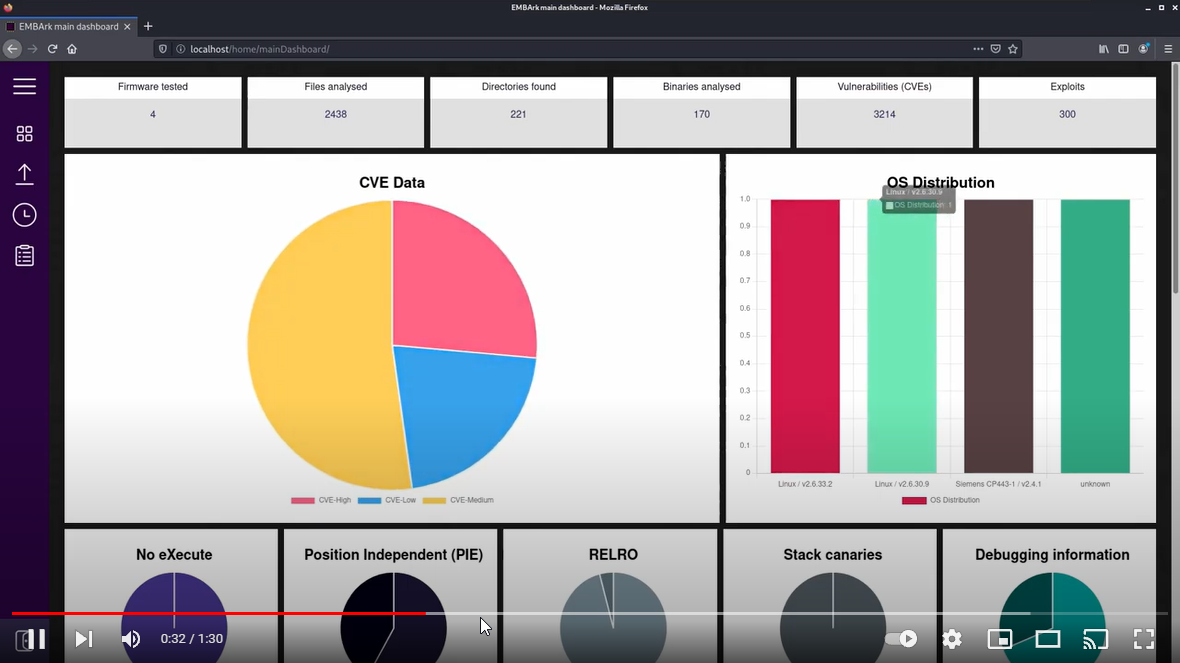 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.