
static-arm-bins
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis
binary-analysisdebuggersdynamic-analysis-sandboxing+6
528
therealsaumil/static-arm-binsStatically compiled ARM binaries for debugging and runtime analysis
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 uthrasri/cve-2021-21401_nanopb-c_aosp10_r33
Lightweight Protocol Buffers implementation in ANSI C for microcontrollers and memory-restricted embedded systems, enabling efficient serialization…
 ret2c/cve-2026-8023
PoC for CVE-2026-8023: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
 thorat-shubham/jxl_infotainment_cve-2025-69515
Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 florianmattana/sass-king
Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
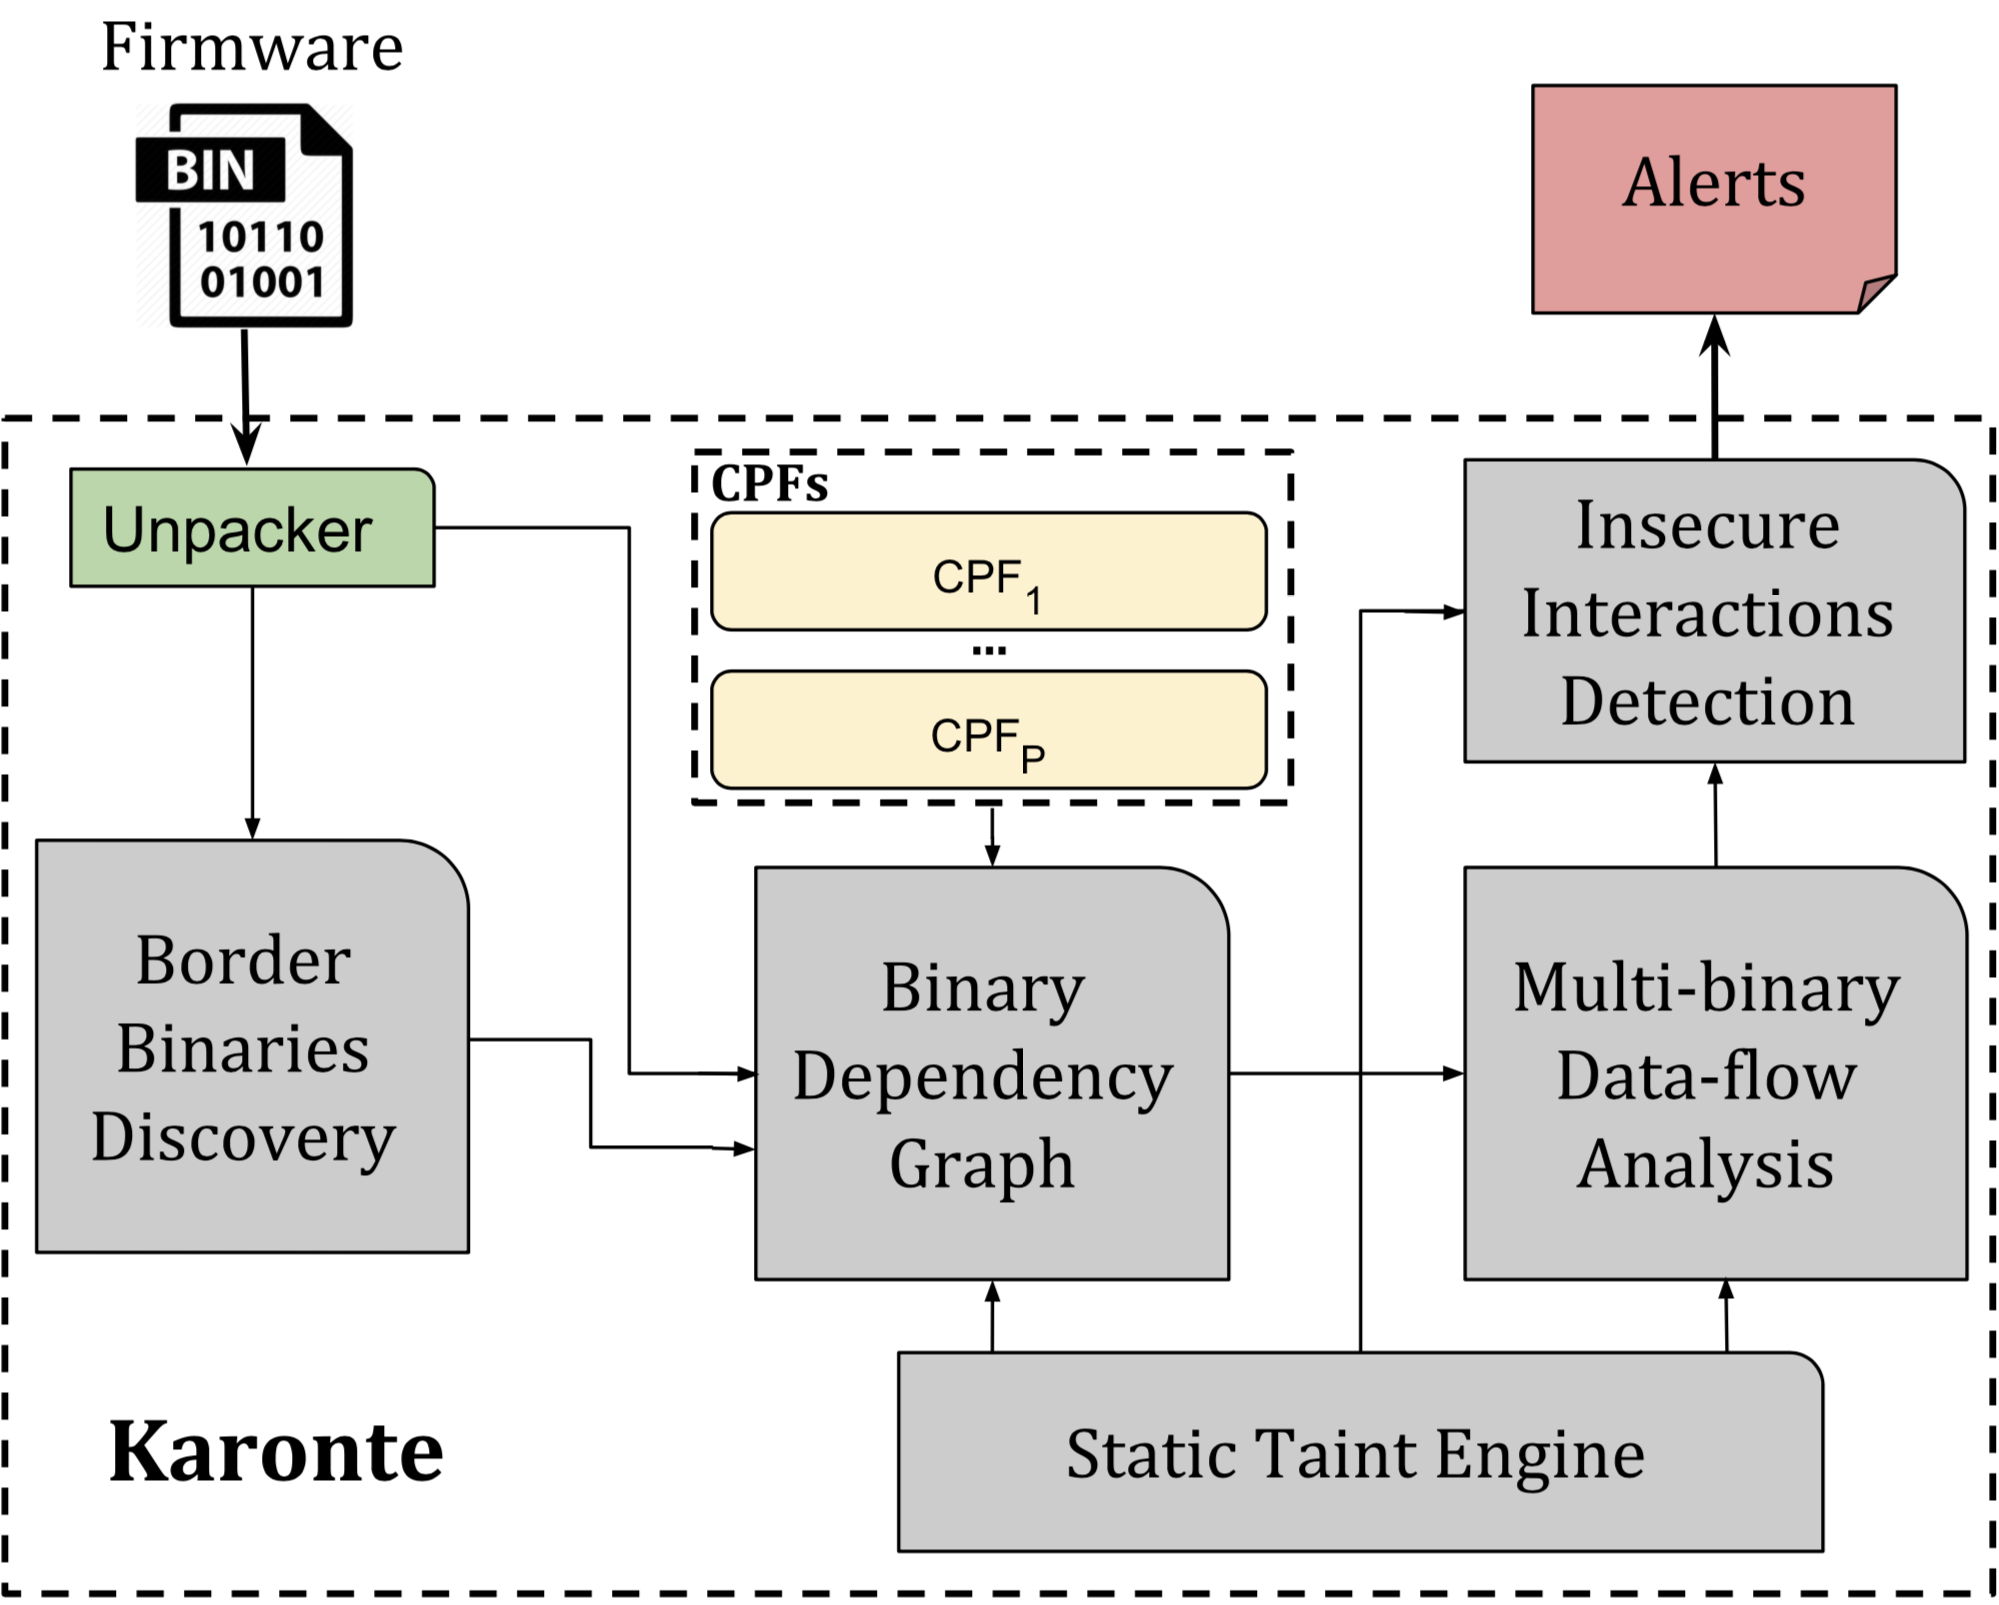 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware