
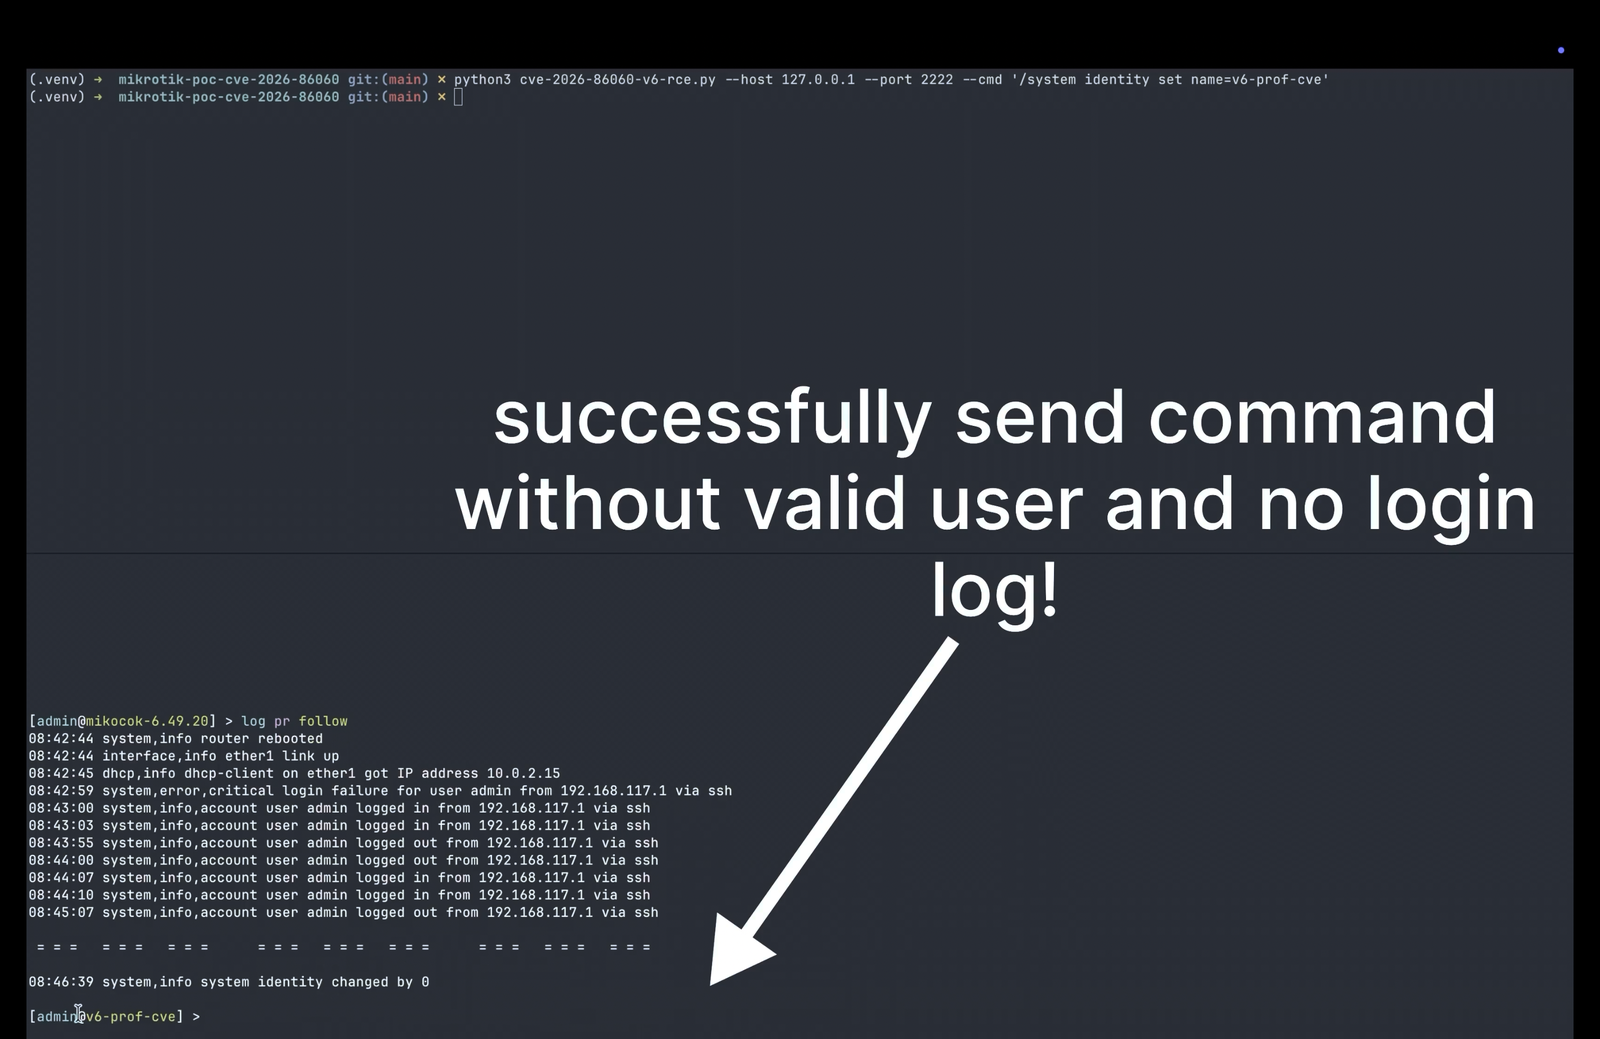
cve-2026-86060
 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
defensive-toolsembedded-systems-securityexploitation+4
1
bahirul/cve-2026-86060Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 tc3650/cve-2026-43499-armv7
ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…
 fi01/libmsm_cameraconfig_exploit
C exploit for CVE-2013-2595 targeting a kernel memory corruption in Qualcomm MSM camera driver on Android devices, enabling local privilege…
 satheesh575555/libhwbinder_aosp10_r33_cve-2020-0136
Exploit for CVE-2020-0136, a use-after-free vulnerability in Android's libhwbinder, demonstrating memory corruption and potential privilege…
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 laginimaineb/cve-2015-6639
QSEE Privilege Escalation Exploit using PRDiag* commands (CVE-2015-6639)
 fi01/libmsm_acdb_exploit
Exploit for CVE-2013-2597, a stack-based buffer overflow in the Qualcomm ACDB audio driver, enabling privilege escalation on affected Android devices.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
 lukejenkins/cve-2022-24693
Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
 leoservalli/privilege-escalation-askey
Privilege escalation vulnerability on ASKEY routers
 laginimaineb/cve-2016-2431
Qualcomm TrustZone kernel privilege escalation