
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…

A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32

Mediatek Flash and Repair Utility

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…

ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32

shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing

Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…

Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…

Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.

Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing

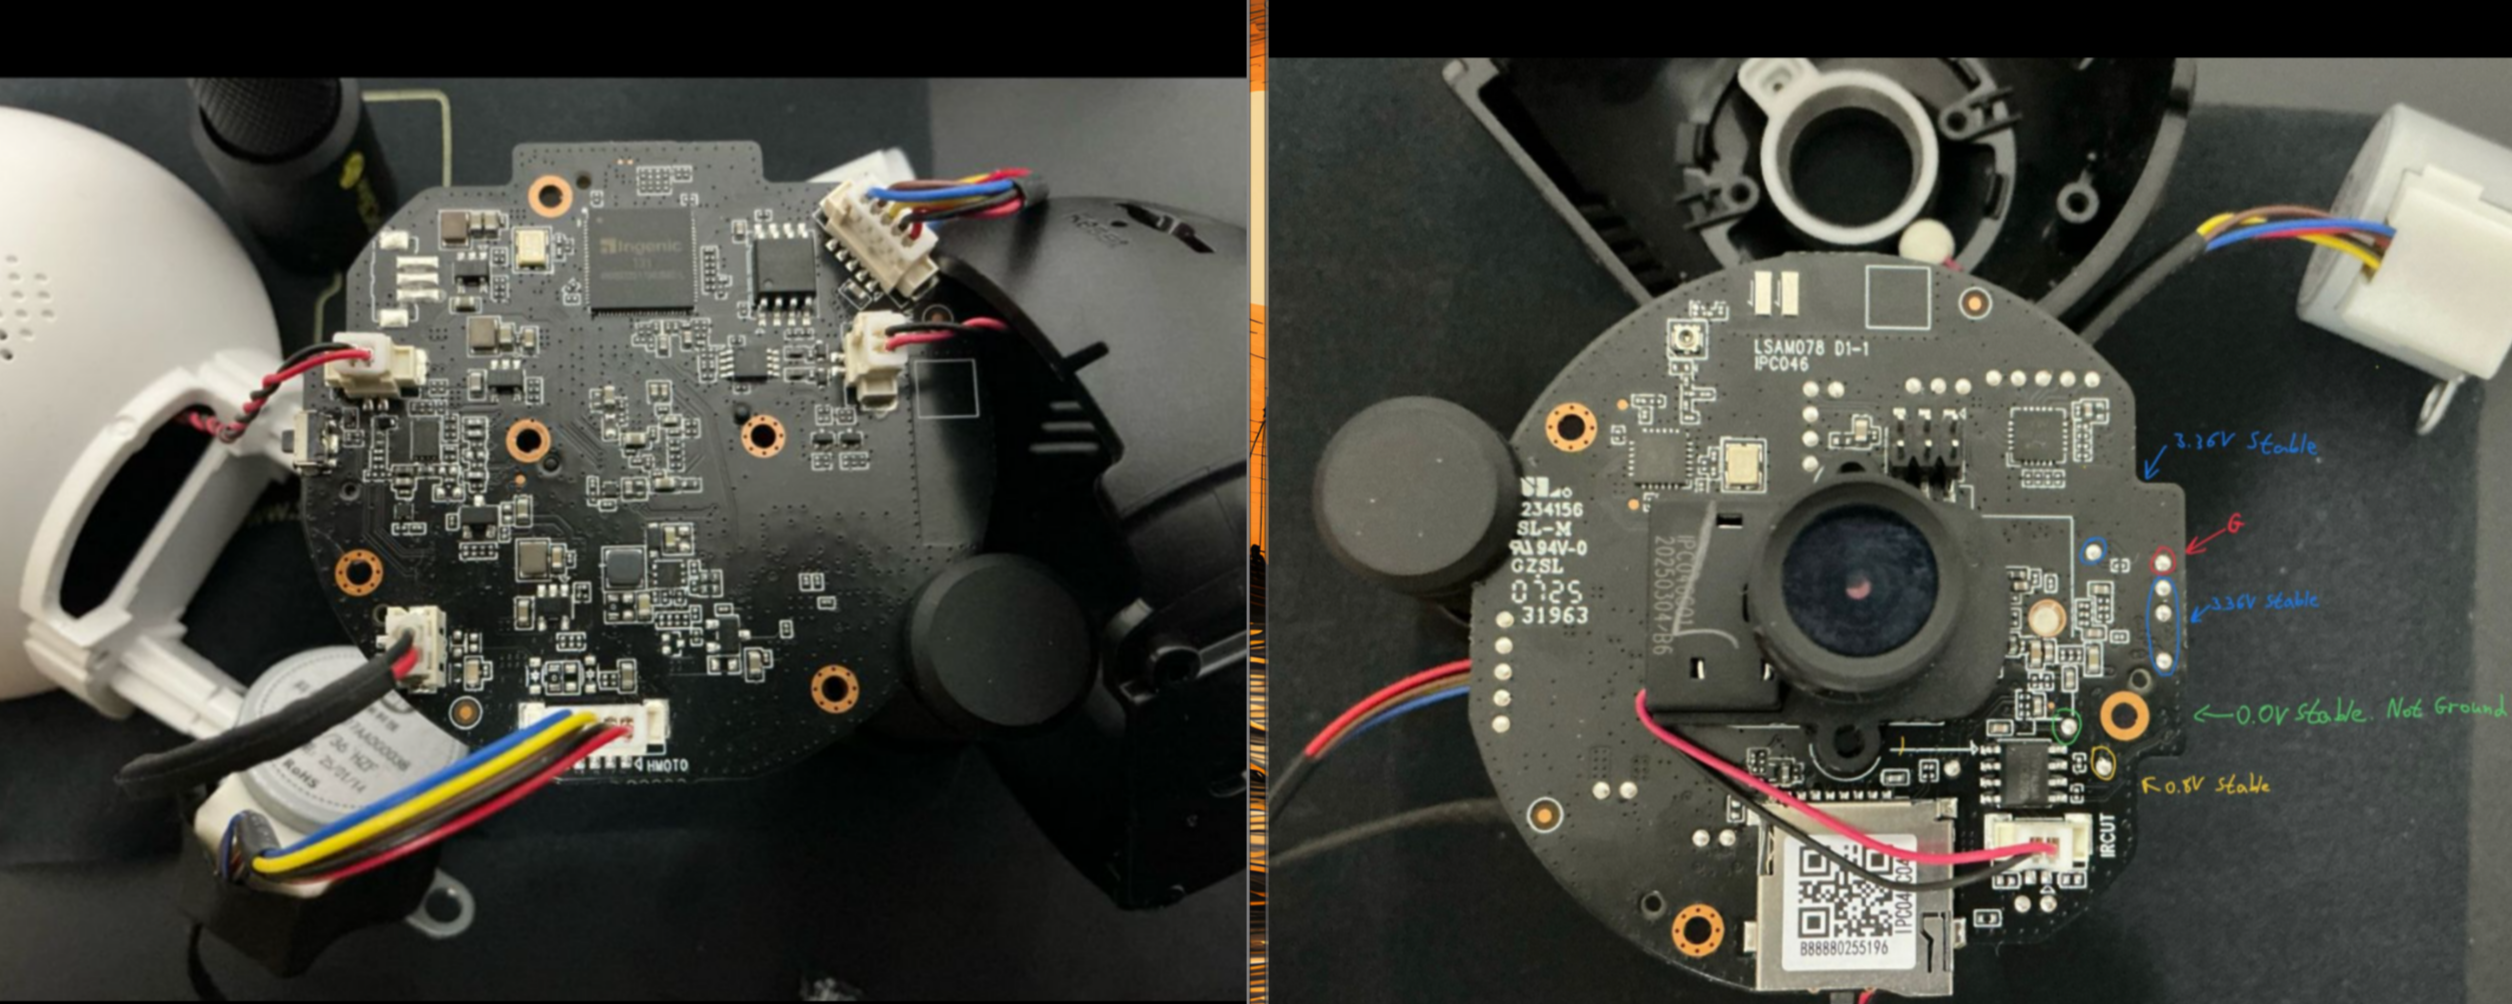
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

Low-level kernel modules and device tree source for the OnePlus 11 (sm8550), enabling hardware bring-up, driver analysis, and embedded system…

Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…

AirPods liberated from Apple's ecosystem.

Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).

Flipper Zero firmware source code

:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…