
CVE-2024-39929
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
educationemail-securityexploitation+3
42 years ago
michael-david-fry/cve-2024-39929POC to test CVE-2024-39929 against EXIM mail servers
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 simonschoeni/cve-2020-7247-poc
Proof of concept for CVE-2020-7247 for educational purposes.
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
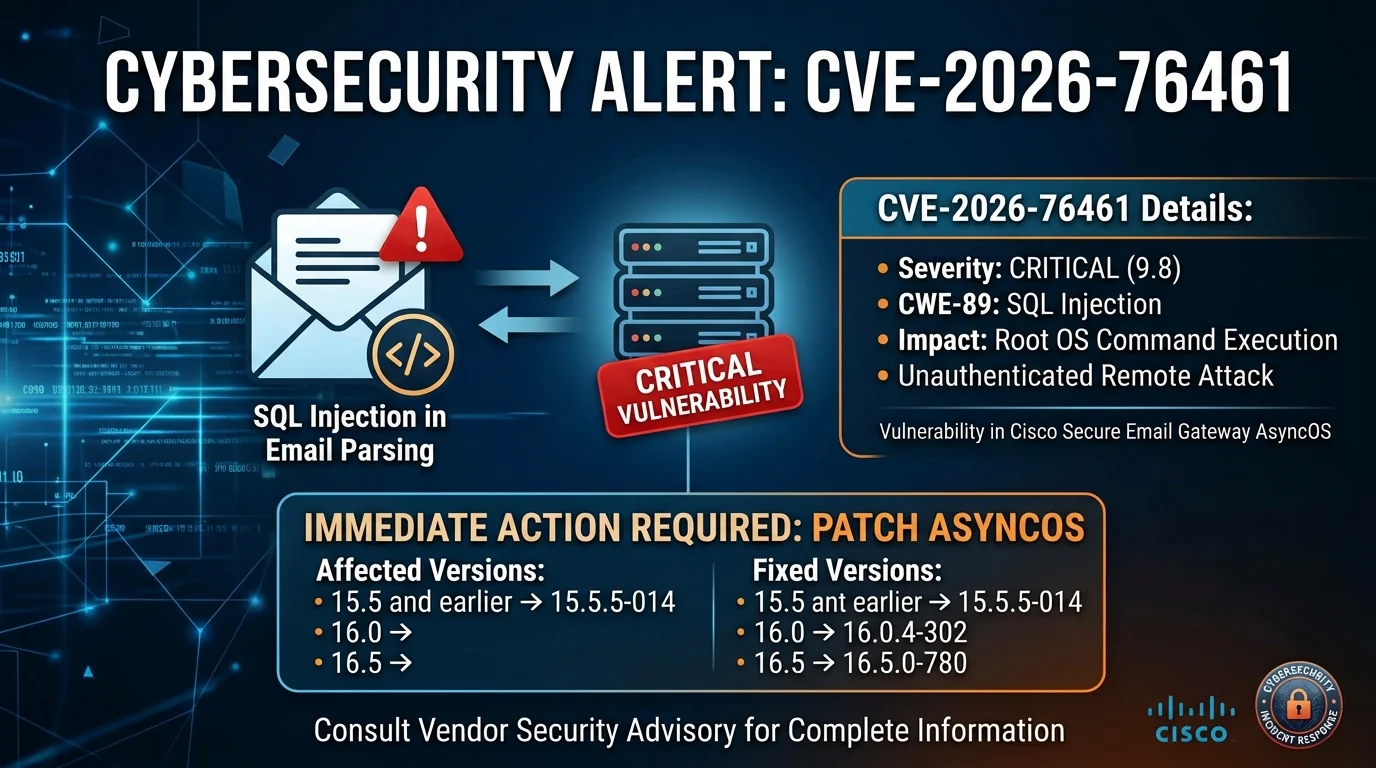 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 brets0150/stickyexim
Exim Honey Pot for CVE-2019-10149 exploit attempts.
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…