

mailMeta
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
175
gr33nm0nk2802/mailmetaAn forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
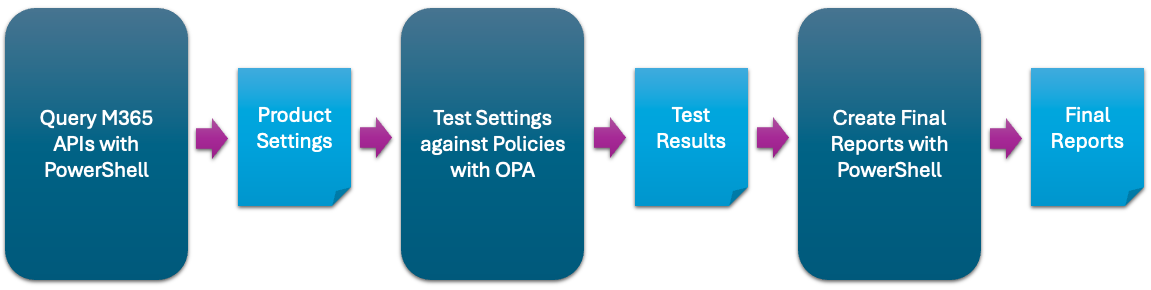 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 xfreed0m/smtptester
small python3 tool to check common vulnerabilities in SMTP servers
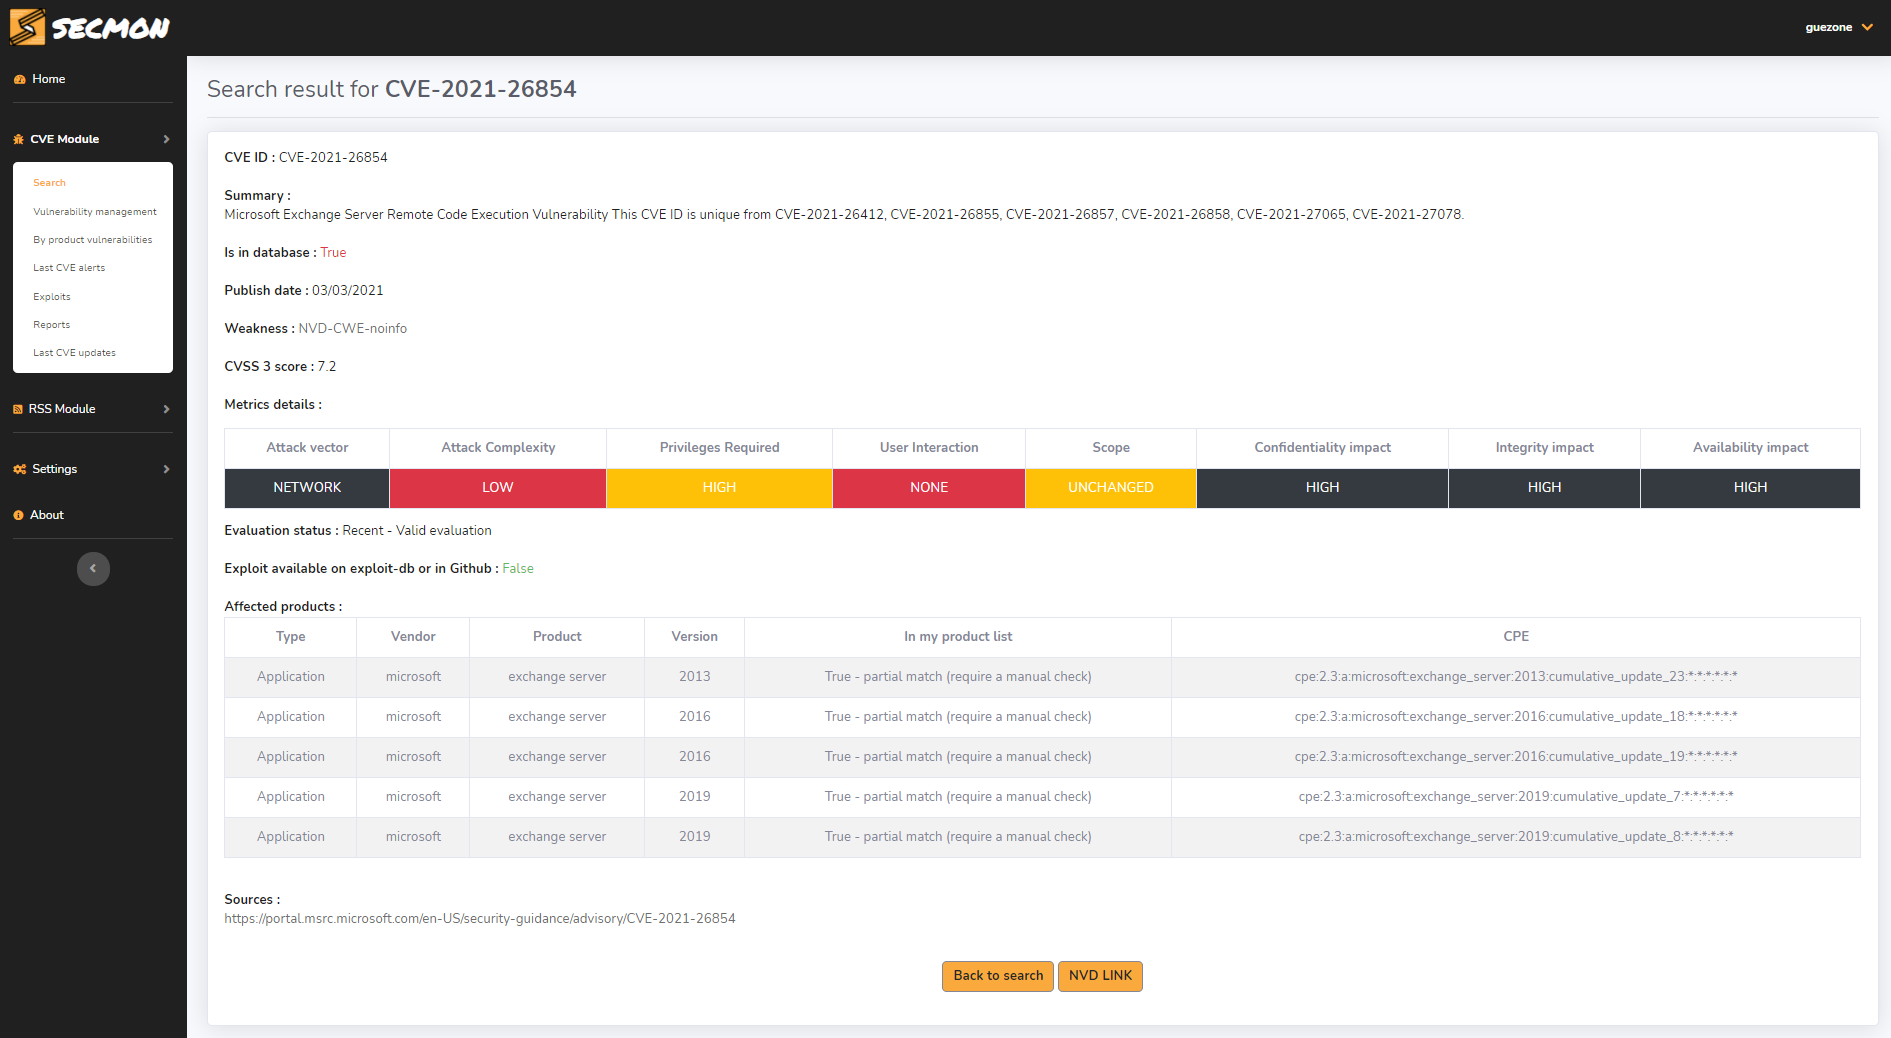 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 sensepost/ruler
A tool to abuse Exchange services
 byt3bl33d3r/spamchannel
Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 rxerium/cve-2024-39929
Detection method for Exim vulnerability CVE-2024-39929
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 loseys/oblivion
Data leak checker & OSINT Tool
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 defrancescojp/cve-2013-2977
Proof-of-concept exploit for CVE-2013-2977: IBM Lotus Notes PNG integer overflow leading to arbitrary code execution when a malicious email is opened…