
msmailprobe
 busterb/msmailprobe
Enumerate valid users on Office 365 and Exchange via time-based and error-based techniques across multiple exposed services, including OWA,…
email-securityinformation-gatheringosint+2
205
busterb/msmailprobeEnumerate valid users on Office 365 and Exchange via time-based and error-based techniques across multiple exposed services, including OWA,…
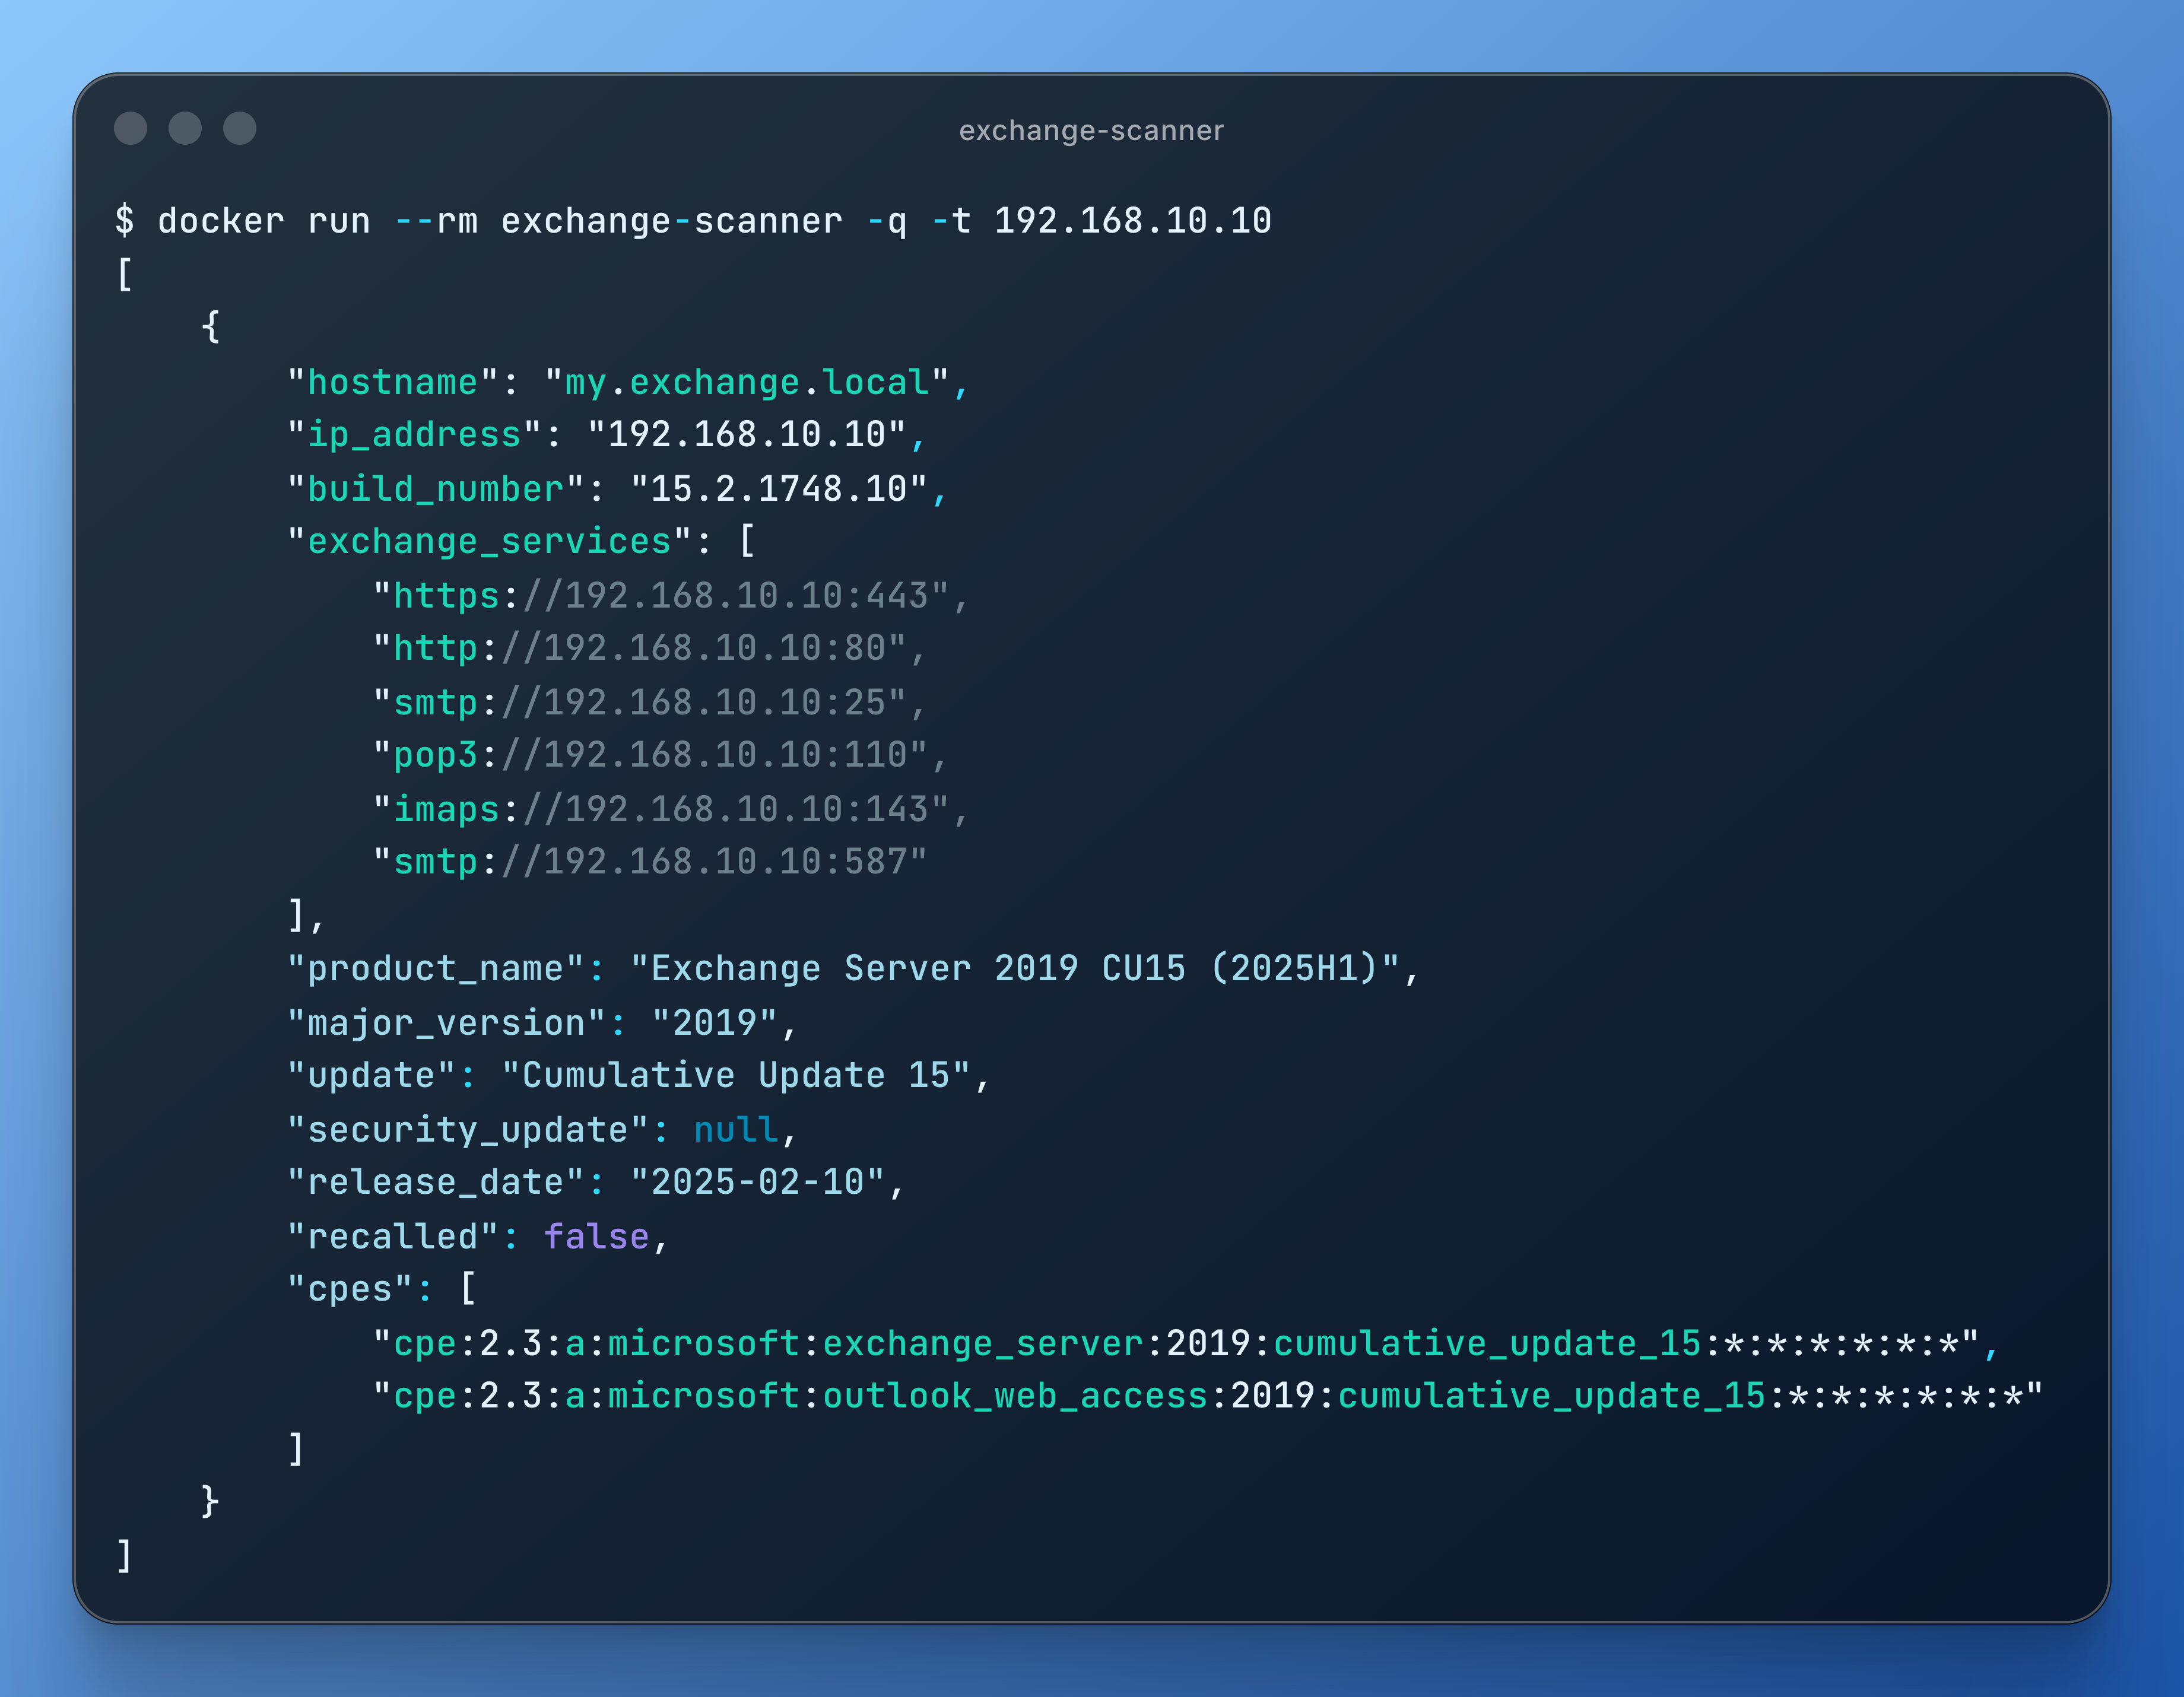 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
 uilicious/inboxkitten
Disposable email inbox powered by serverless mailgun kittens
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
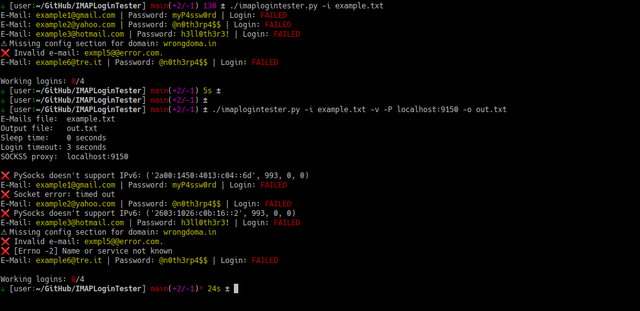 rm1984/imaplogintester
A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…
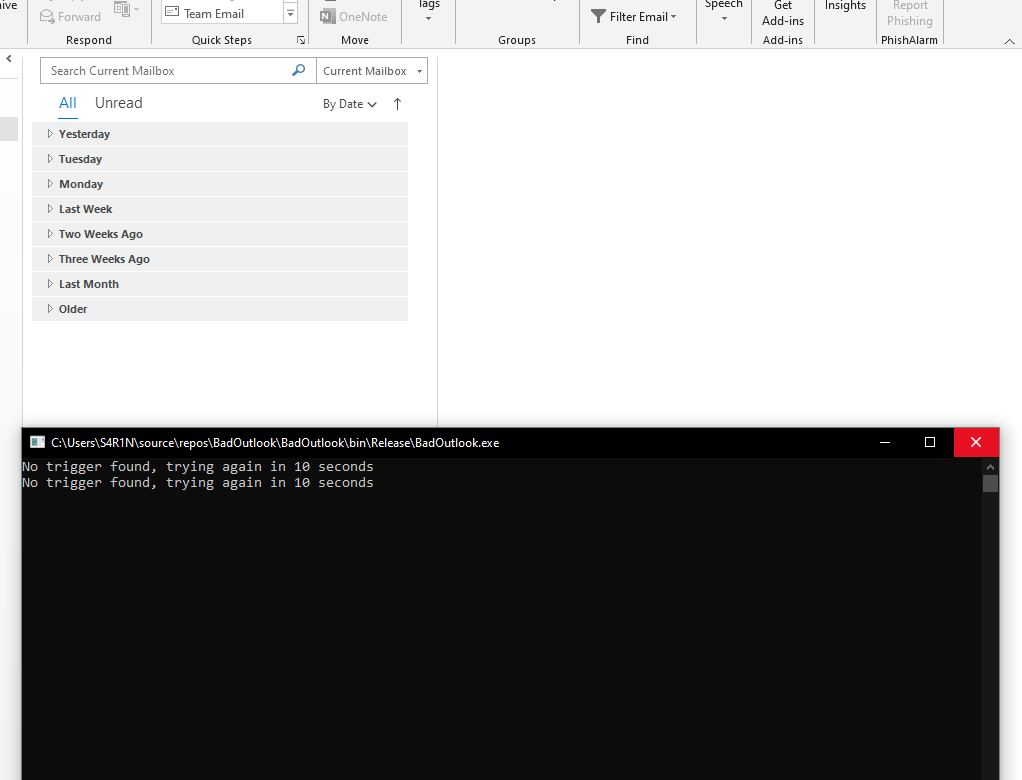 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 mattkeeley/spoofy
Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.