Email-exploit-Moniker-Link-CVE-2024-21413-

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…

Proof-of-concept exploit for CVE-2023-23397, a Microsoft Outlook privilege escalation vulnerability. Sends a crafted email with a malicious UNC path…

Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…

FiercePhish is a full-fledged phishing framework to manage all phishing engagements. It allows you to track separate phishing campaigns, schedule…

Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…

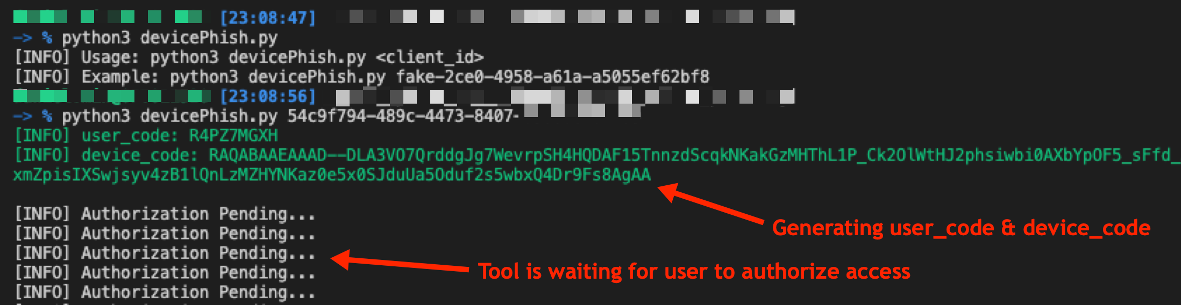
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow

Exploit for the CVE-2023-23397

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

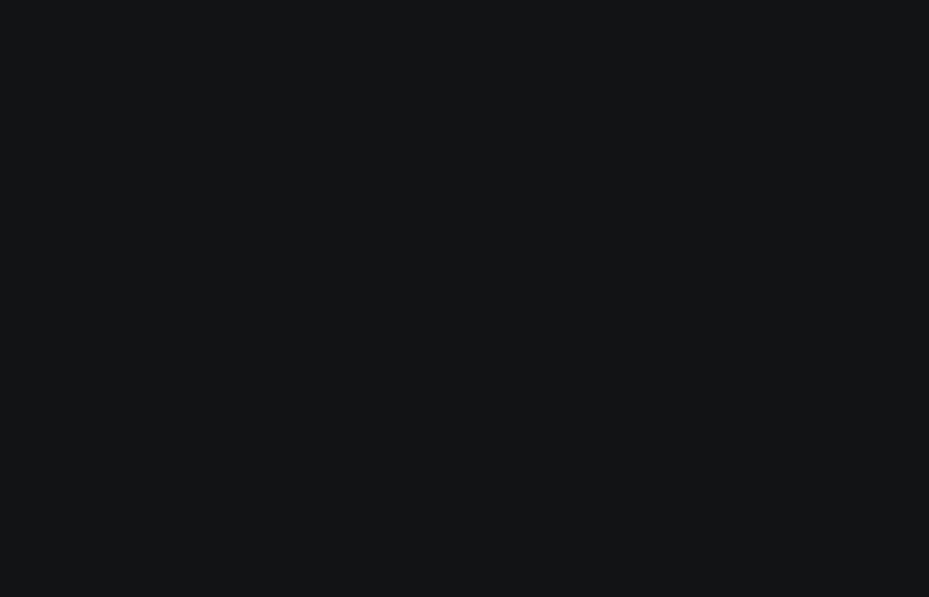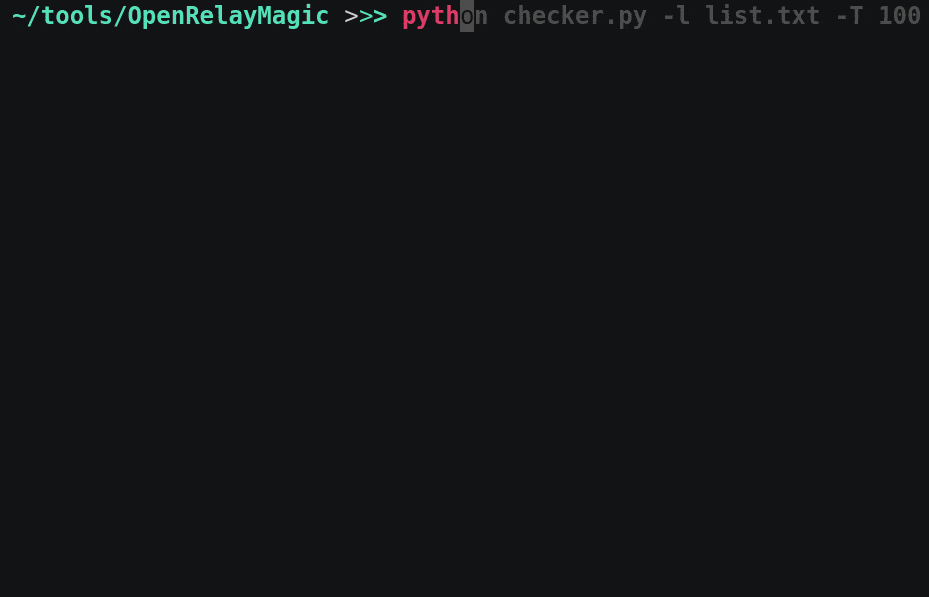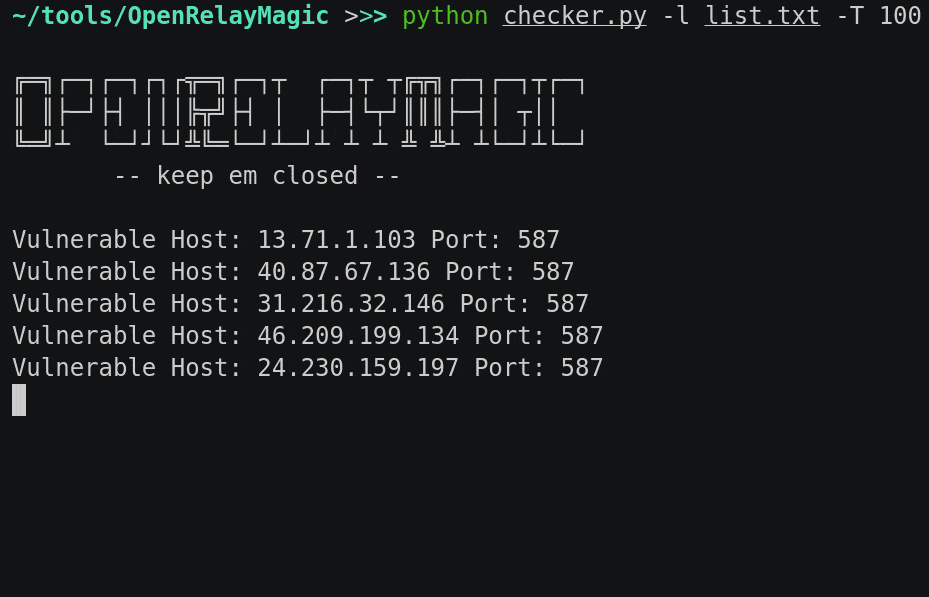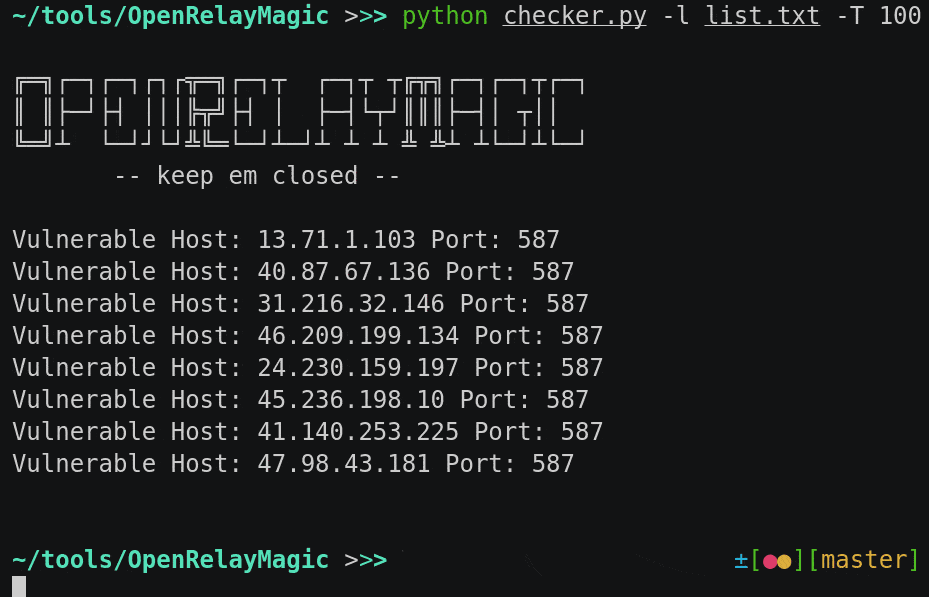
Tool to find SMTP servers vulnerable to open relay

Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…

Proof-of-concept exploit for CVE-2023-51764 SMTP smuggling vulnerability in Postfix, enabling email spoofing and message injection via crafted SMTP…


Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…

Detection method for Exim vulnerability CVE-2024-39929

Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.

CVE-2026-28289

PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…