
CVE-2020-16947
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
binary-exploitationemail-securityexploitation+3
122
0neb1n/cve-2020-16947Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 0neb1n/cve-2020-1493
Technical analysis and PoC details for CVE-2020-1493, a zero-click Outlook RCE triggered by malformed MS-TNEF attachments leading to remote code…
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
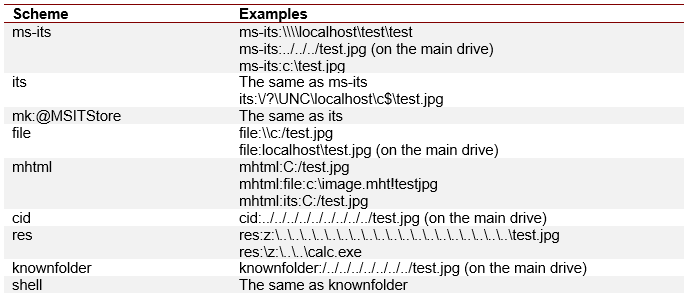 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
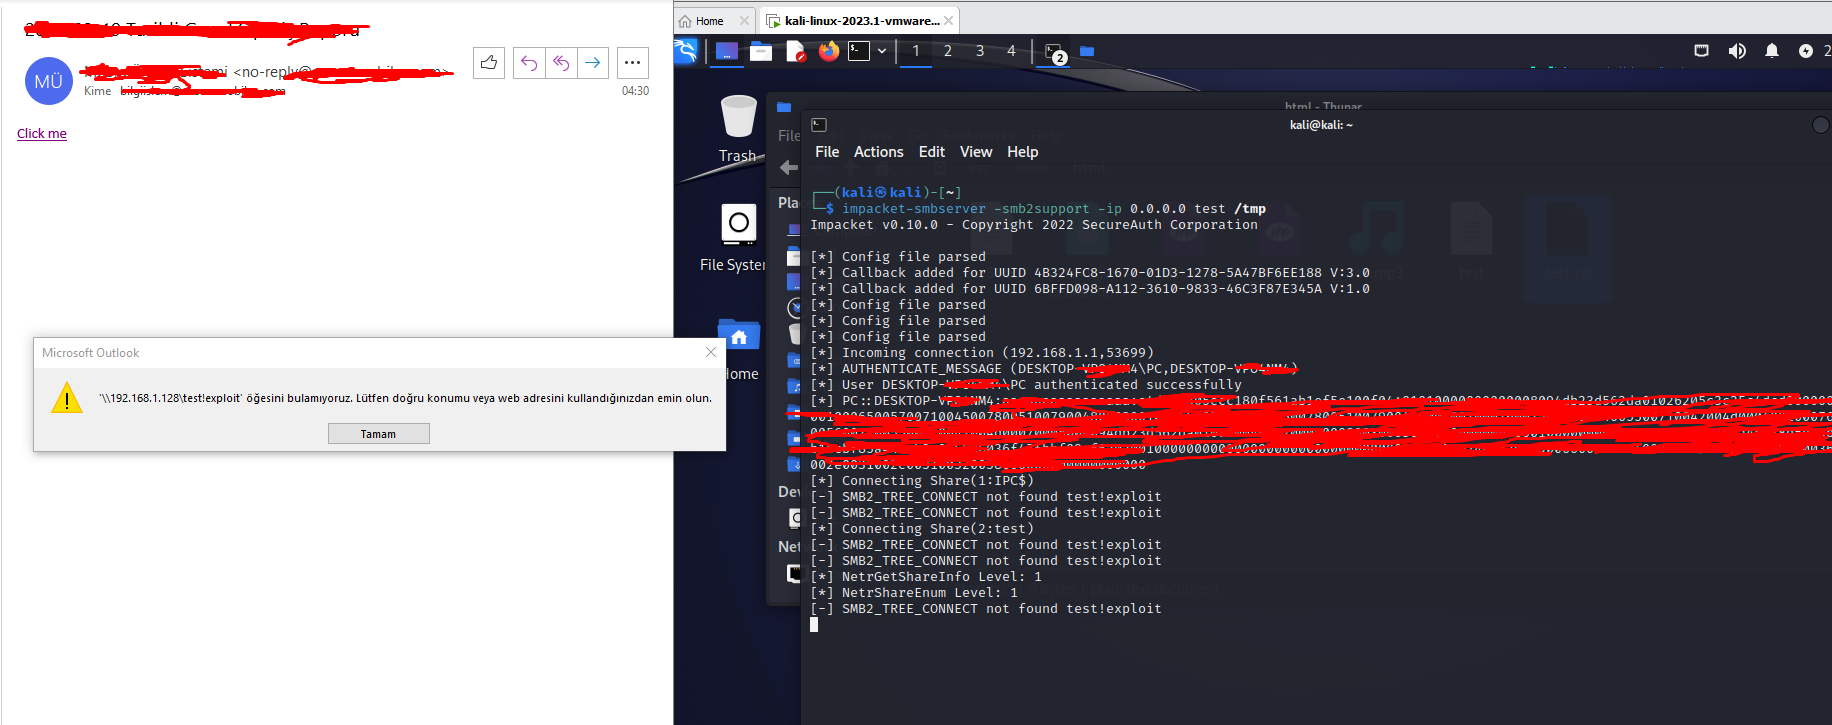 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 sensepost/ruler
A tool to abuse Exchange services
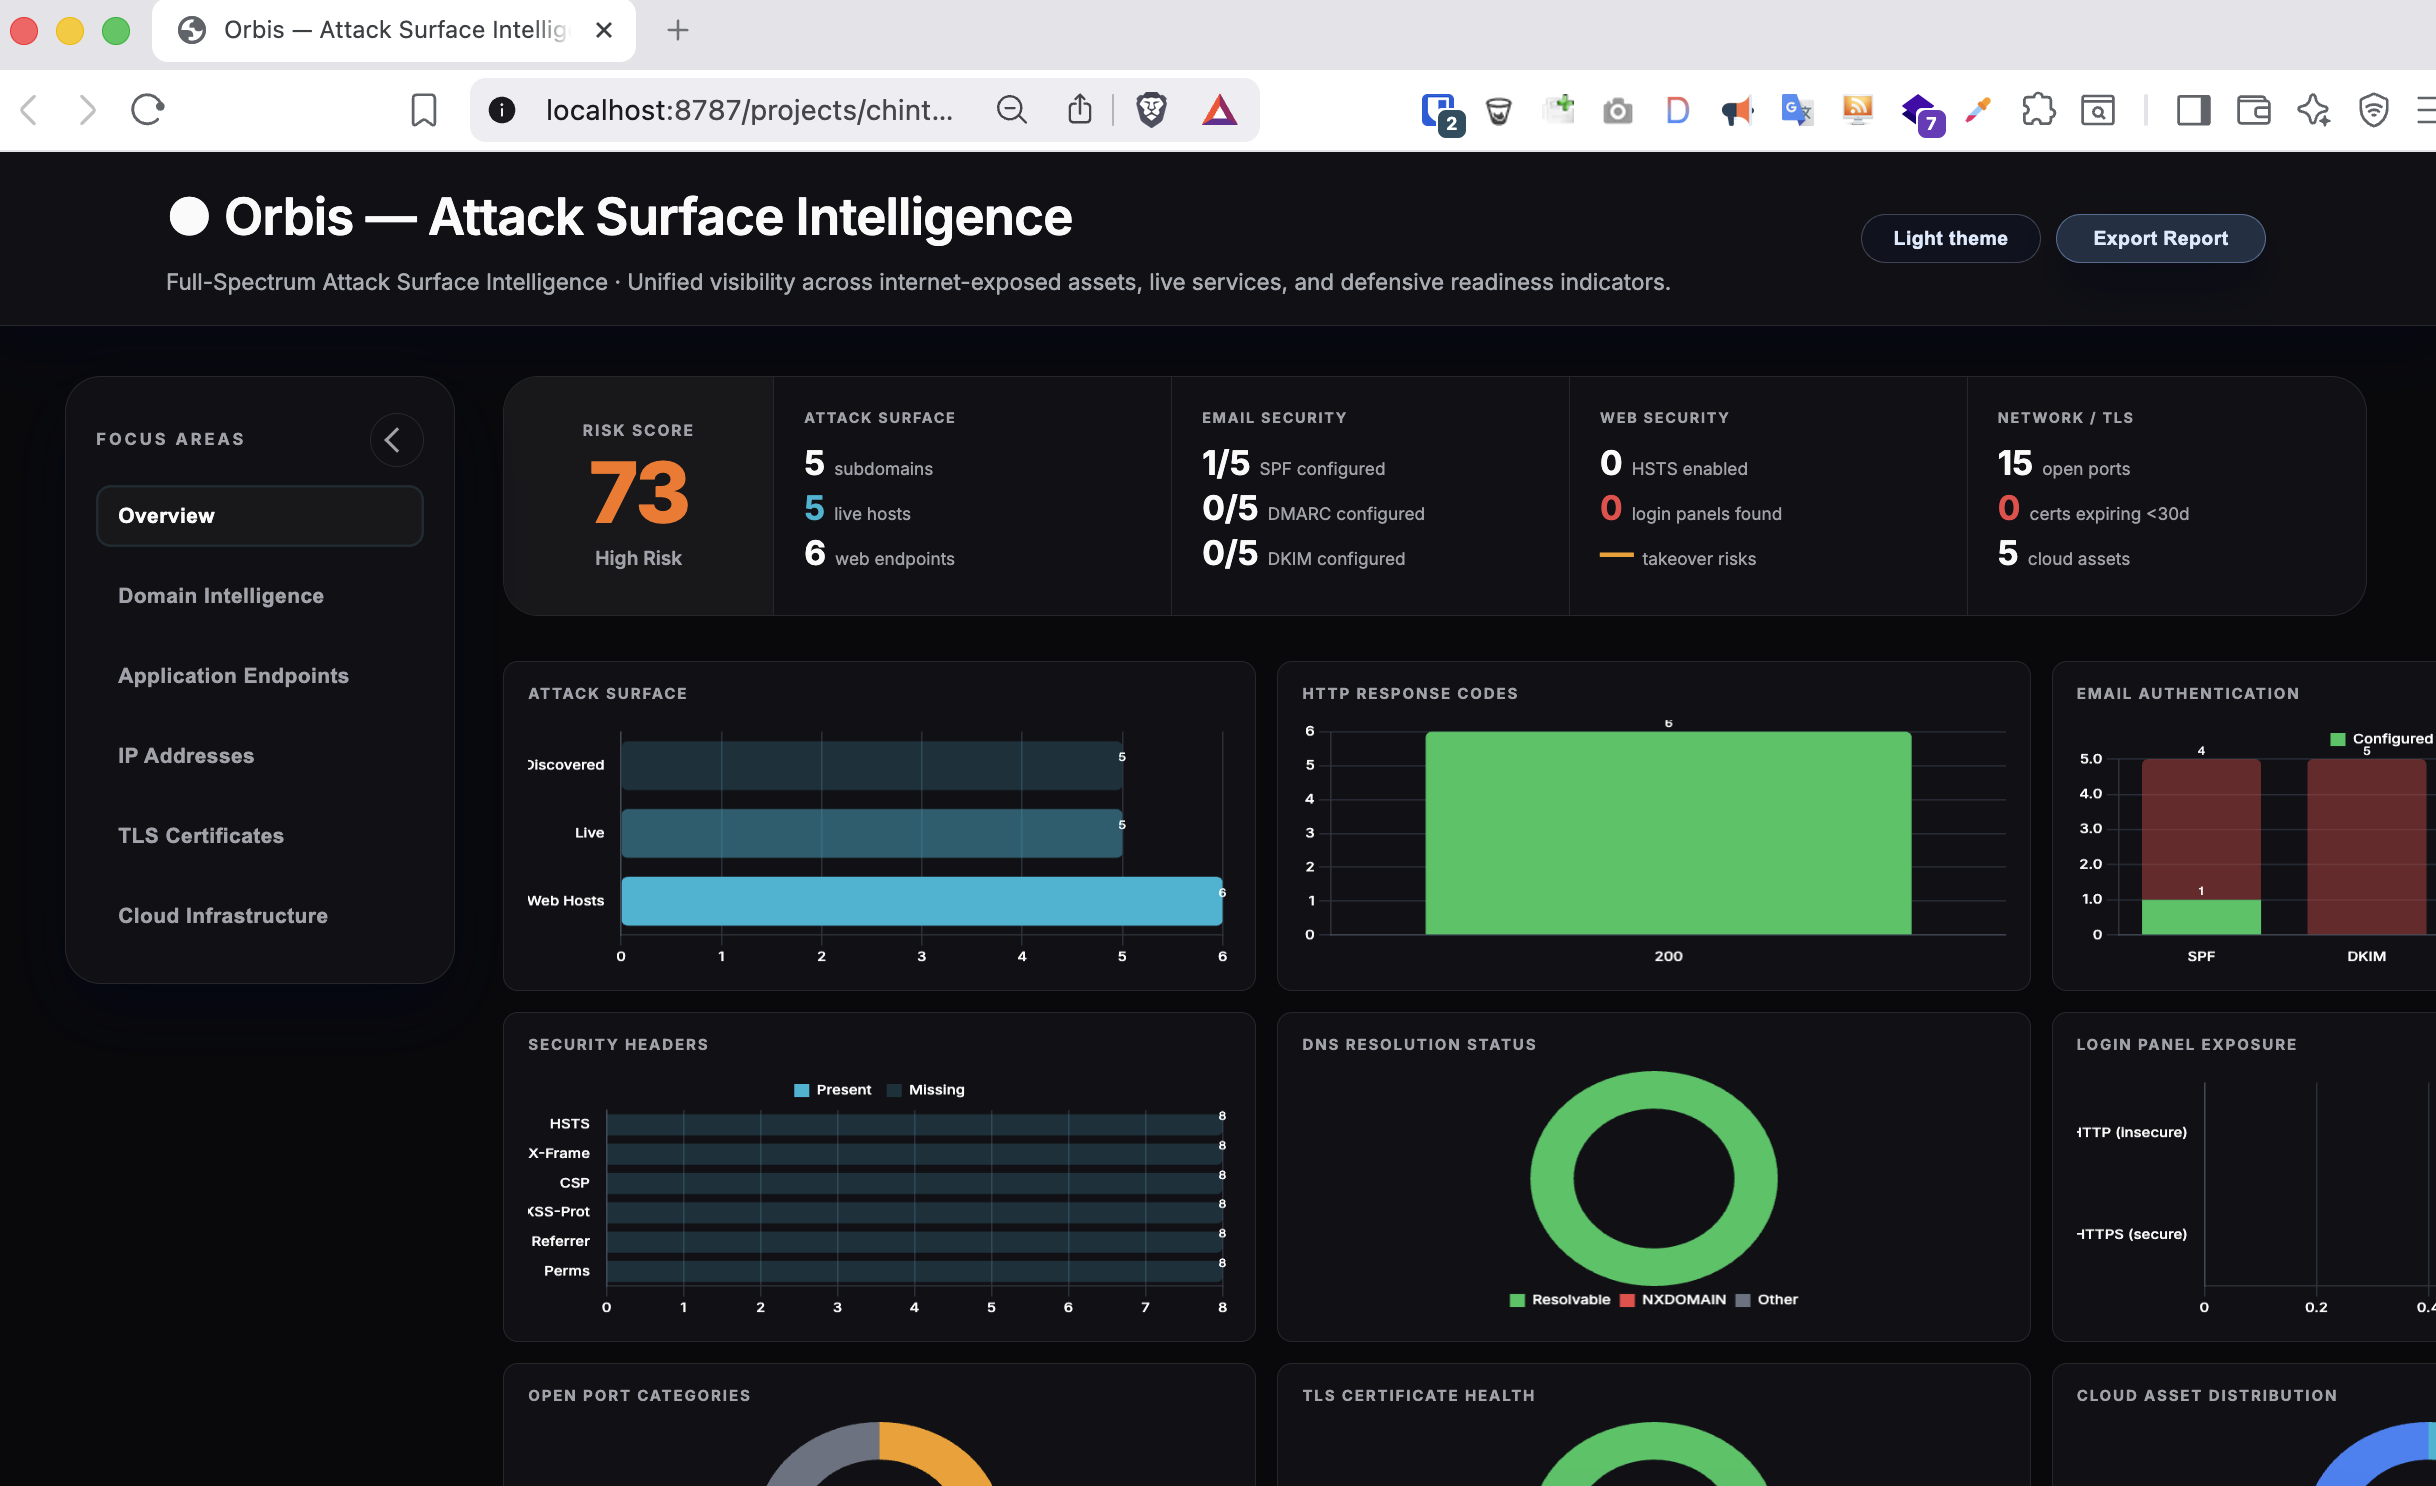 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…