
ExchangeRelayX
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
authenticationemail-securityexploitation+7
304
quickbreach/exchangerelayxAn NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 sublime-security/sublime-rules
Sublime rules for email attack detection, prevention, and threat hunting.
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
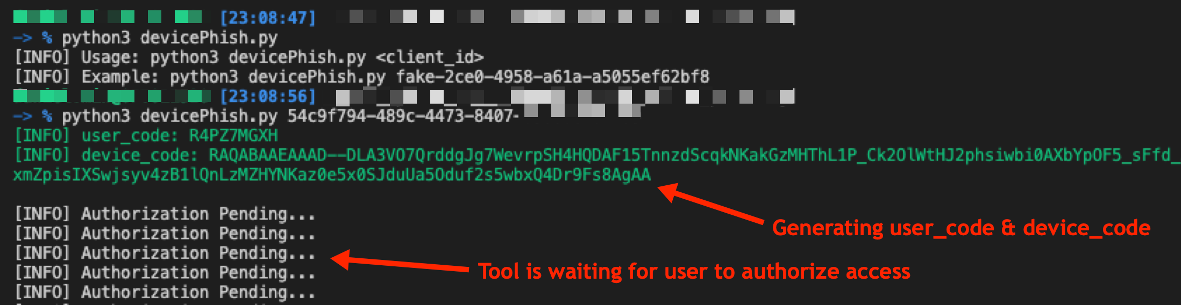 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 brets0150/stickyexim
Exim Honey Pot for CVE-2019-10149 exploit attempts.
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365