

CVE-2023-23397_EXPLOIT_0DAY
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
email-securityexploitationmalware-analysis+3
158
sqrtzeroknowledge/cve-2023-23397_exploit_0dayExploit for the CVE-2023-23397
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
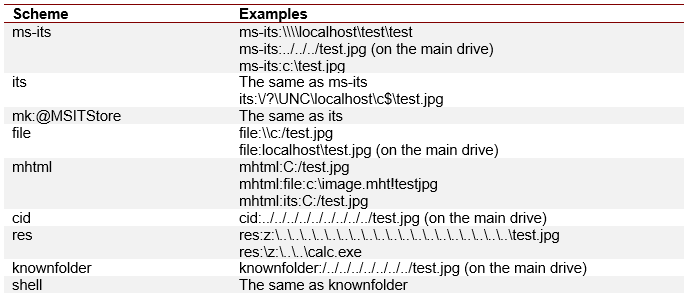 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
 jacquesquail/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, a Microsoft Outlook privilege escalation vulnerability. Sends a crafted email with a malicious UNC path…
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
 wslyvh/paperweight
Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.
 darsigovrustam/cve-2019-10149
Instructions for installing a vulnerable version of Exim and its expluatation
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
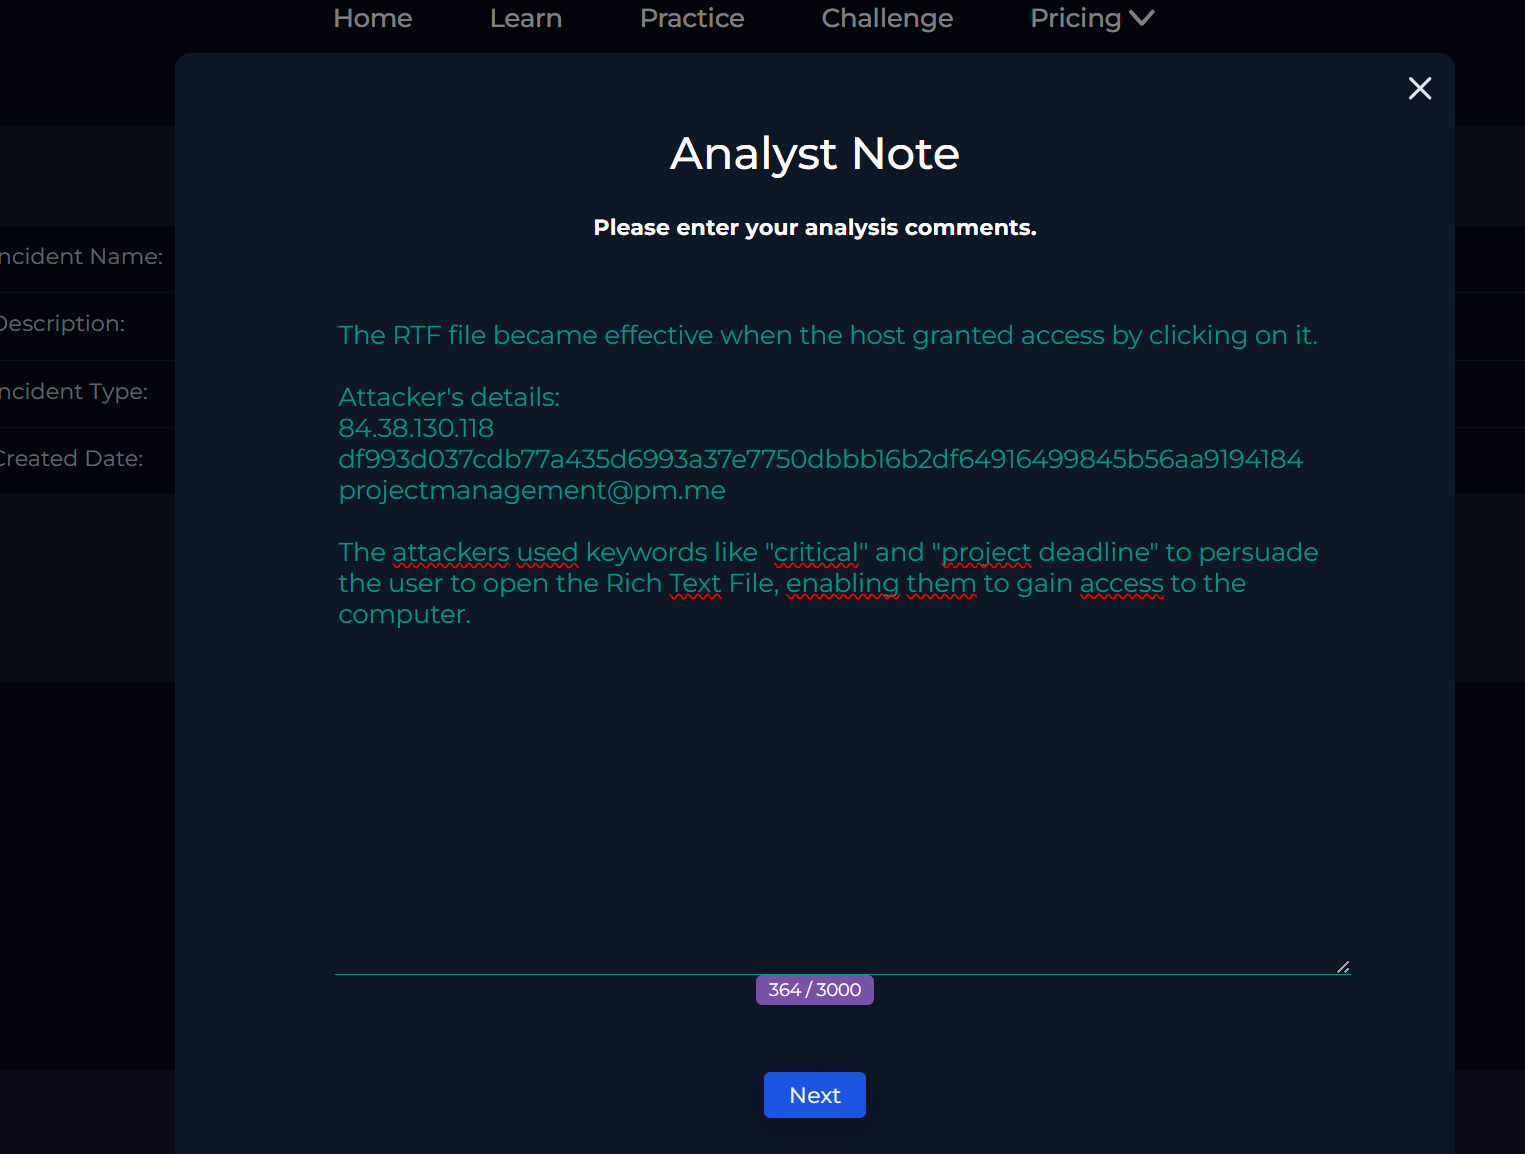 arkha-corvus/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298-
We are expected to investigate a critical alert reporting a Windows OLE zero-click RCE exploitation (CVE-2025-21298) delivered via a malicious RTF…
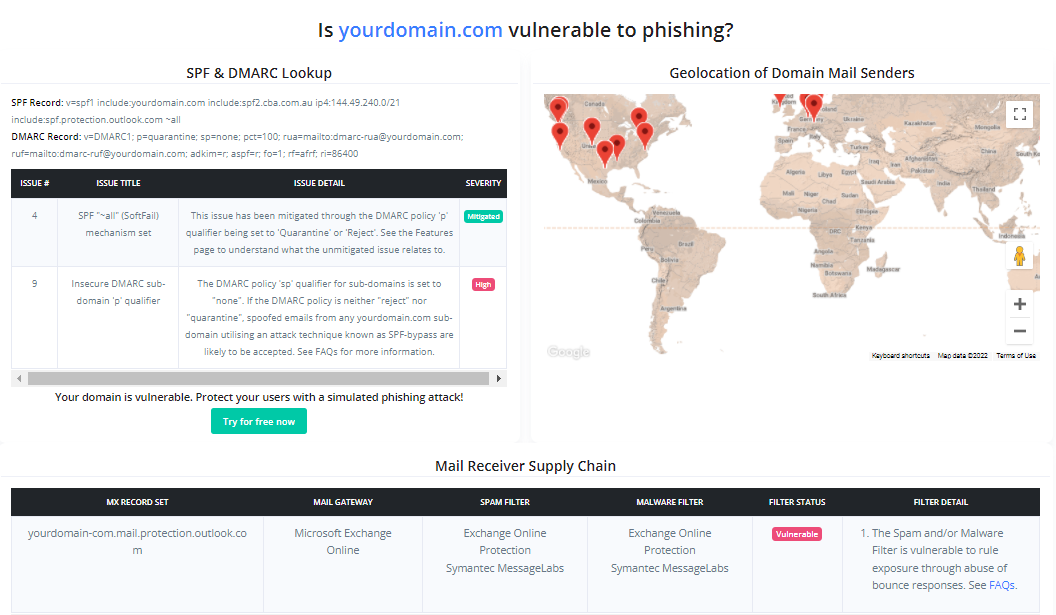 caniphish/phishious
An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC