
CVE-2024-21413-POC
 r00tb1t/cve-2024-21413-poc
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC
educationemail-securityexploitation+3
17
r00tb1t/cve-2024-21413-pocMicrosoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 darsigovrustam/cve-2019-10149
Instructions for installing a vulnerable version of Exim and its expluatation
 all3xj/fixing-google-secops-detections
Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
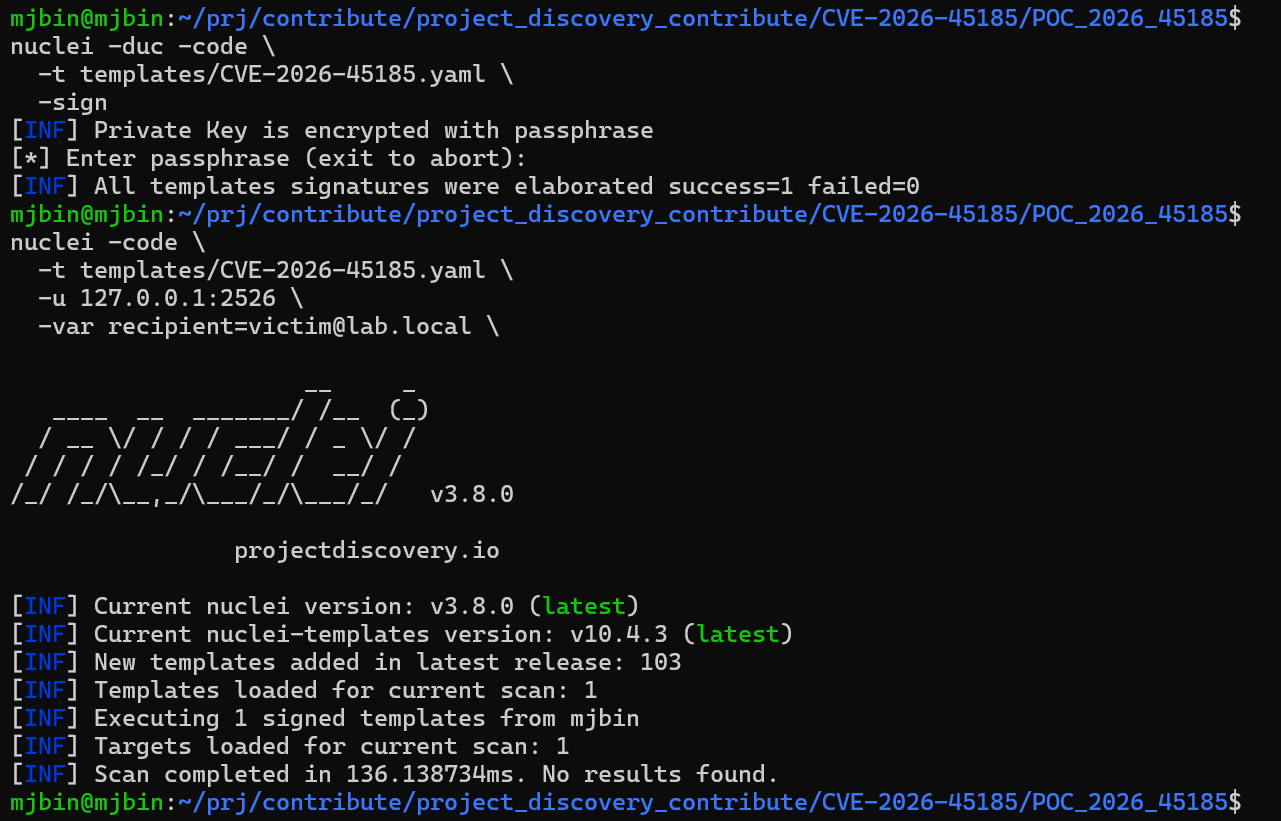 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
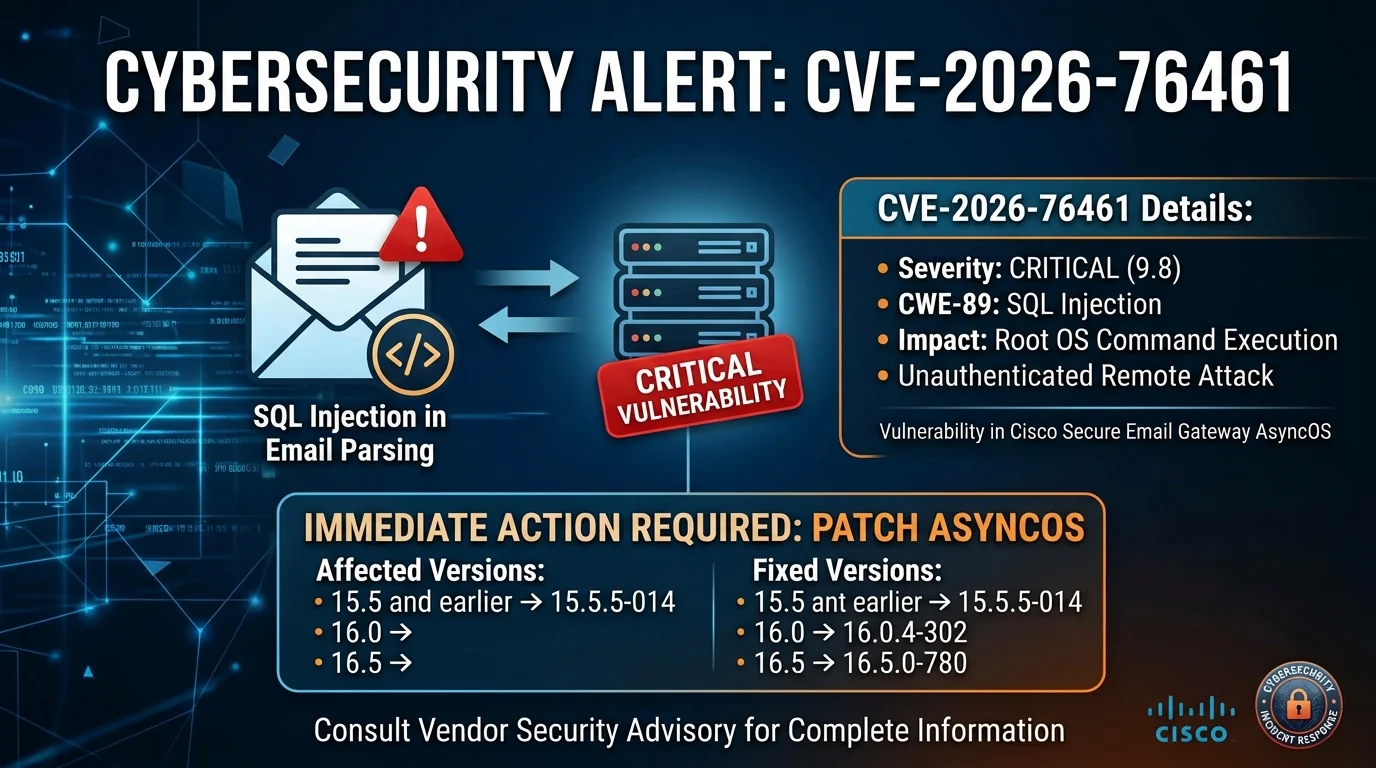 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 alicangnll/cve-2023-23397
CVE-2023-23397 - Microsoft Outlook Vulnerability
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 michael-david-fry/cve-2024-39929
POC to test CVE-2024-39929 against EXIM mail servers
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 simonschoeni/cve-2020-7247-poc
Proof of concept for CVE-2020-7247 for educational purposes.
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.