
CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
577
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
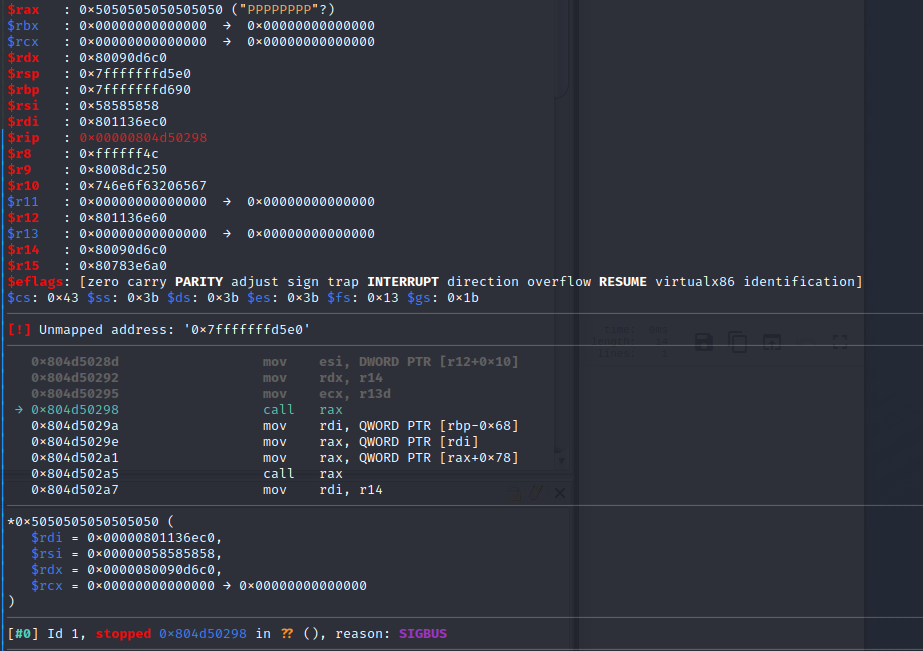 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
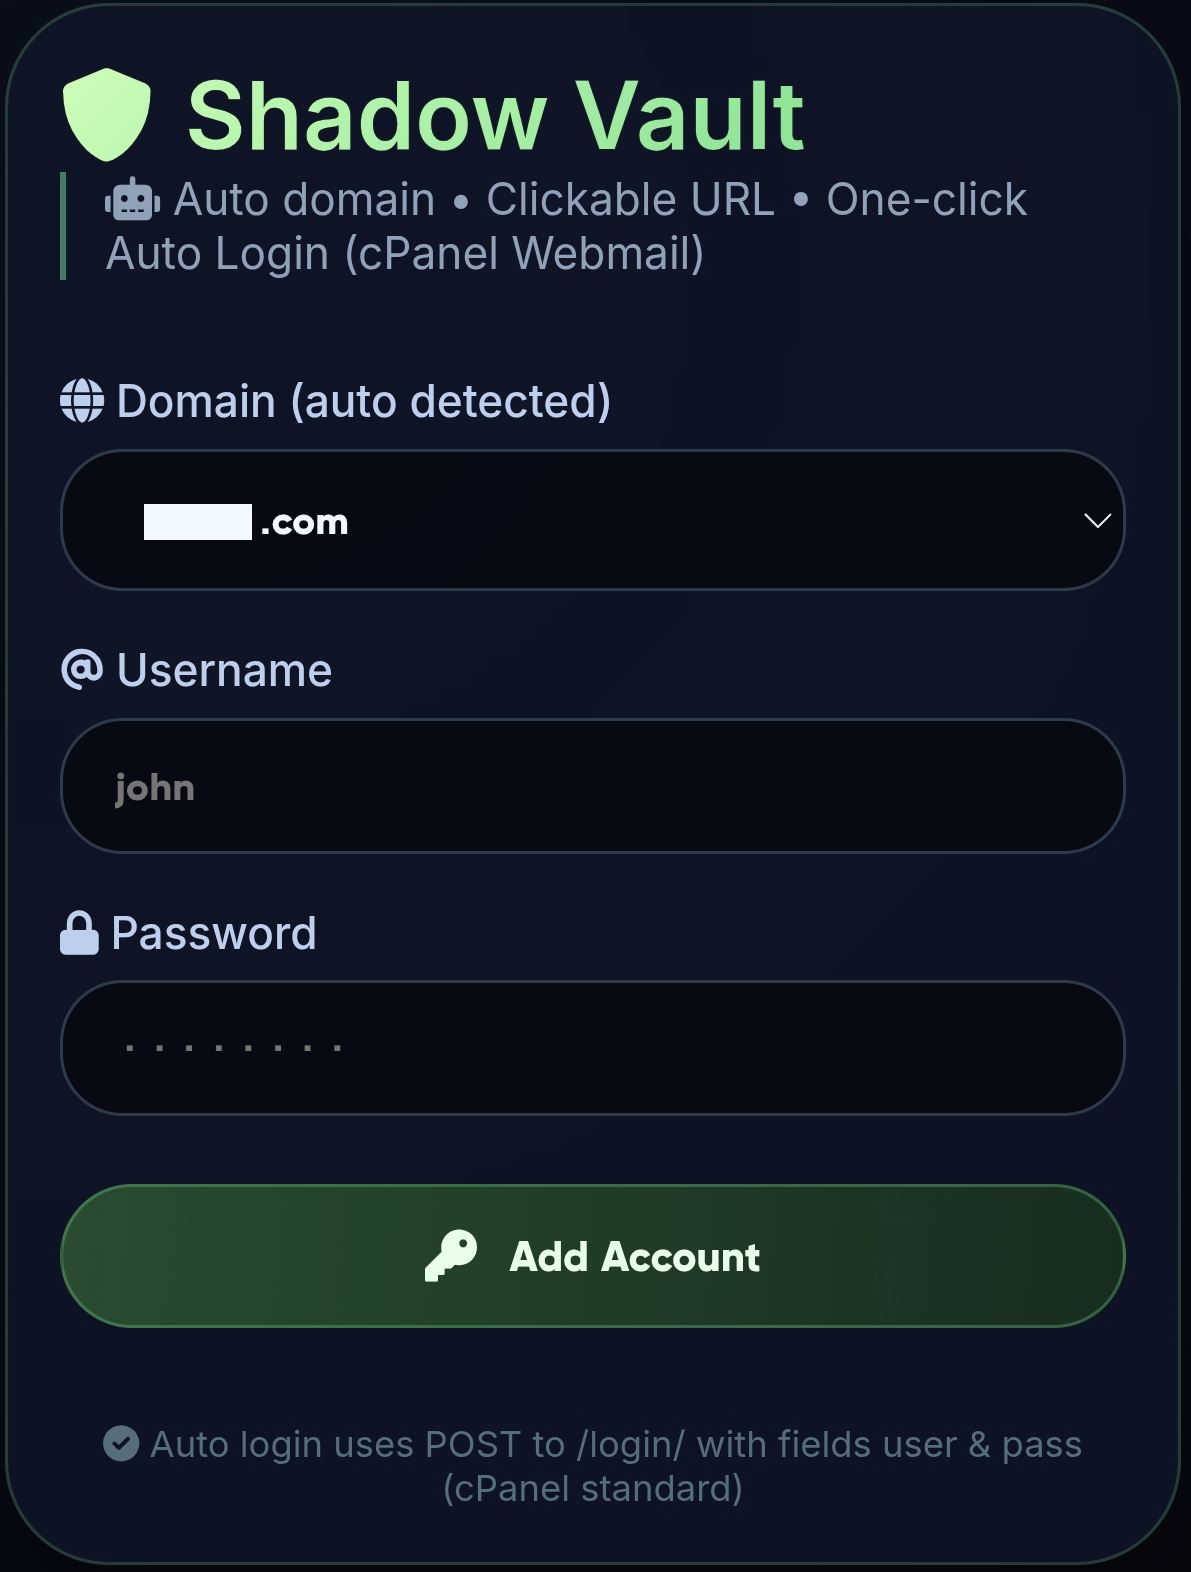 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
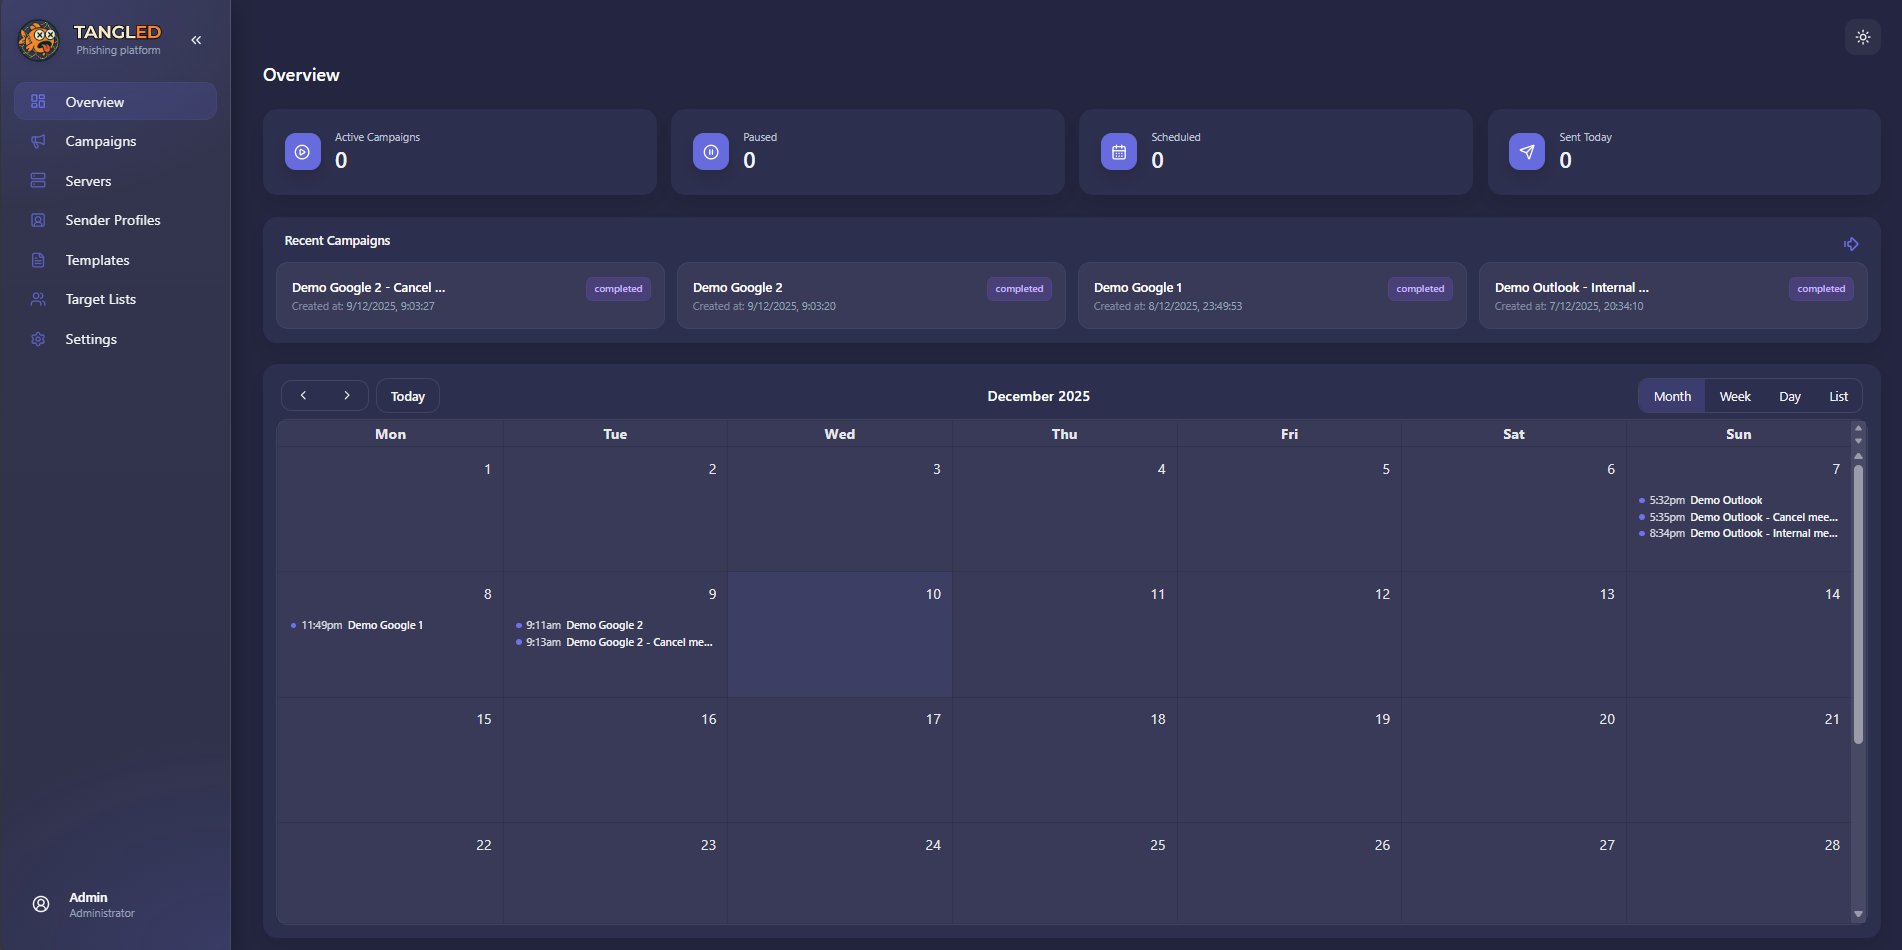 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 sensepost/ruler
A tool to abuse Exchange services
 th3hellion/cve-2024-21413
Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 p4x1s/cve-2023-23397-poc
CVE-2023-23397漏洞的简单PoC,有效载荷通过电子邮件发送。