CVE-2026-25916-Roundcube-Webmail-DOM-based-XSS-Exploit-via-SVG-href-Attribute

Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…

Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…

CVE-2026-28289

CVE-2023-23397漏洞的简单PoC,有效载荷通过电子邮件发送。

Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload

Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…

Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.

Proof of Concept for CVE-2023-23397 in Python

Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…

Python 3 proof-of-concept for CVE-2023-51764 SMTP smuggling vulnerability, enabling email spoofing via crafted SMTP sessions.

对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。

C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.

Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.

CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC

Python script to create a message with the vulenrability properties set

Python script for sending e-mails with CVE-2023-23397 payload using SMTP

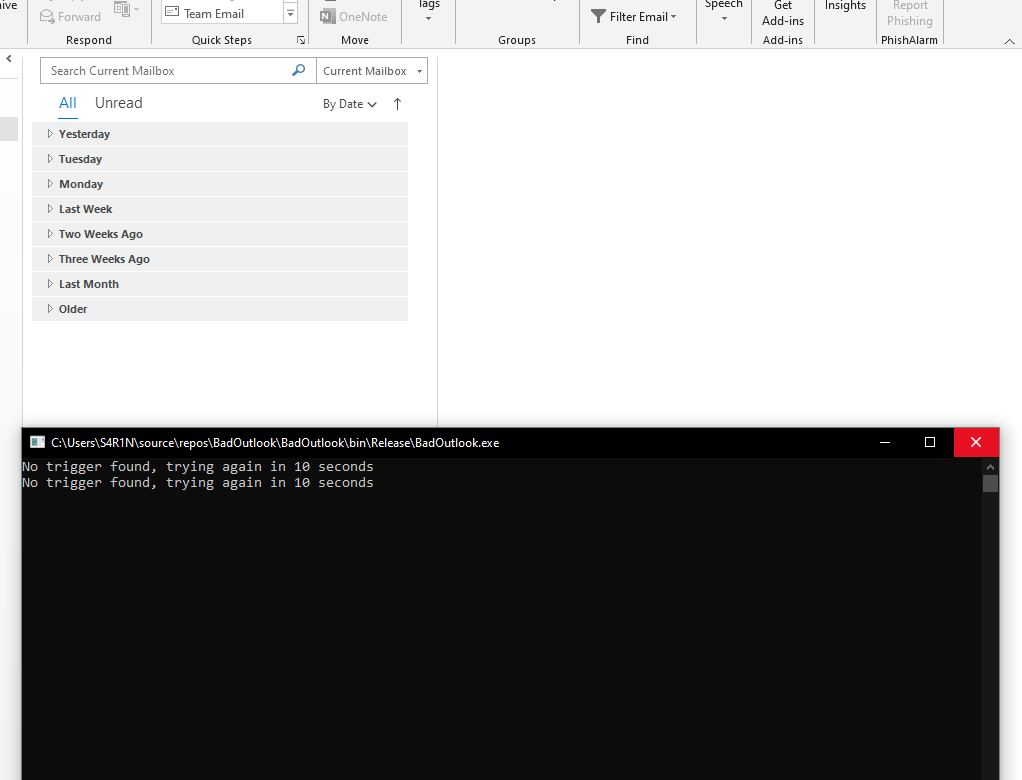
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…