
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers

 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 digininja/dvwa
Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
 aperikube/aperisite
CTF team website aggregating writeups and resources for web security challenges including XSS, SQLi, CSRF, SSRF, and XXE.
 mbrandner-group/webgoat.net
Deliberately vulnerable .NET web application for learning common web security flaws through hands-on exercises covering XSS, SQL injection, and other…
 gracenolan/notes
Curated study notes and interview preparation guide for security engineering roles, covering networking, web security, cryptography, malware…
 psiinon/open-source-web-scanners
Curated list of open-source web security scanners, including general-purpose scanners, infrastructure scanners, and fuzzers, ordered by GitHub stars.
 yavuzlar/vulnlab
Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
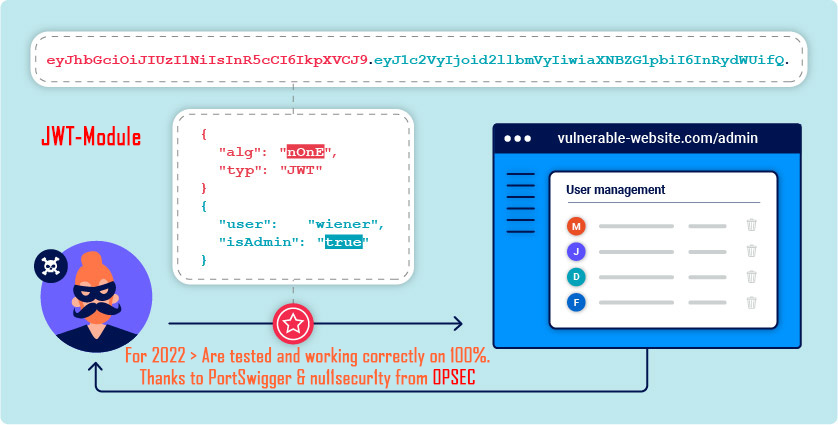 nu11secur1ty/portswigger-web-security-academy
Curated solutions and walkthroughs for PortSwigger Web Security Academy labs, covering web vulnerabilities, JWT attacks, and exploitation techniques…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.