
poc-cve-2026-32255
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
educationexploitationpenetration-testing+3
2
koadt/poc-cve-2026-32255This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
 jf-gondim/mcp-pwn
PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…
 thanhlam-attt/cve-2023-25690
Proof-of-concept exploit for CVE-2023-25690 HTTP Request Smuggling in Apache mod_proxy. Includes lab environment with Docker, BurpSuite walkthrough,…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 george0papasotiriou/cve-2026-22019-libcurl-http-2-connect-tunnel-mixup
Simulates CVE-2026-22019, a libcurl HTTP/2 CONNECT tunnel stream-isolation failure, demonstrating cross-stream data injection and response smuggling…
 george0papasotiriou/cve-2025-15556-notepad-wingup-updater-rce
Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 anantaakotal/agentcyte
Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…
 federella/cve-2023-41717
Detailed write-up and proof of concept for CVE-2023-41717, demonstrating bypass of Zscaler proxy file download/upload restrictions via HTTP Range…
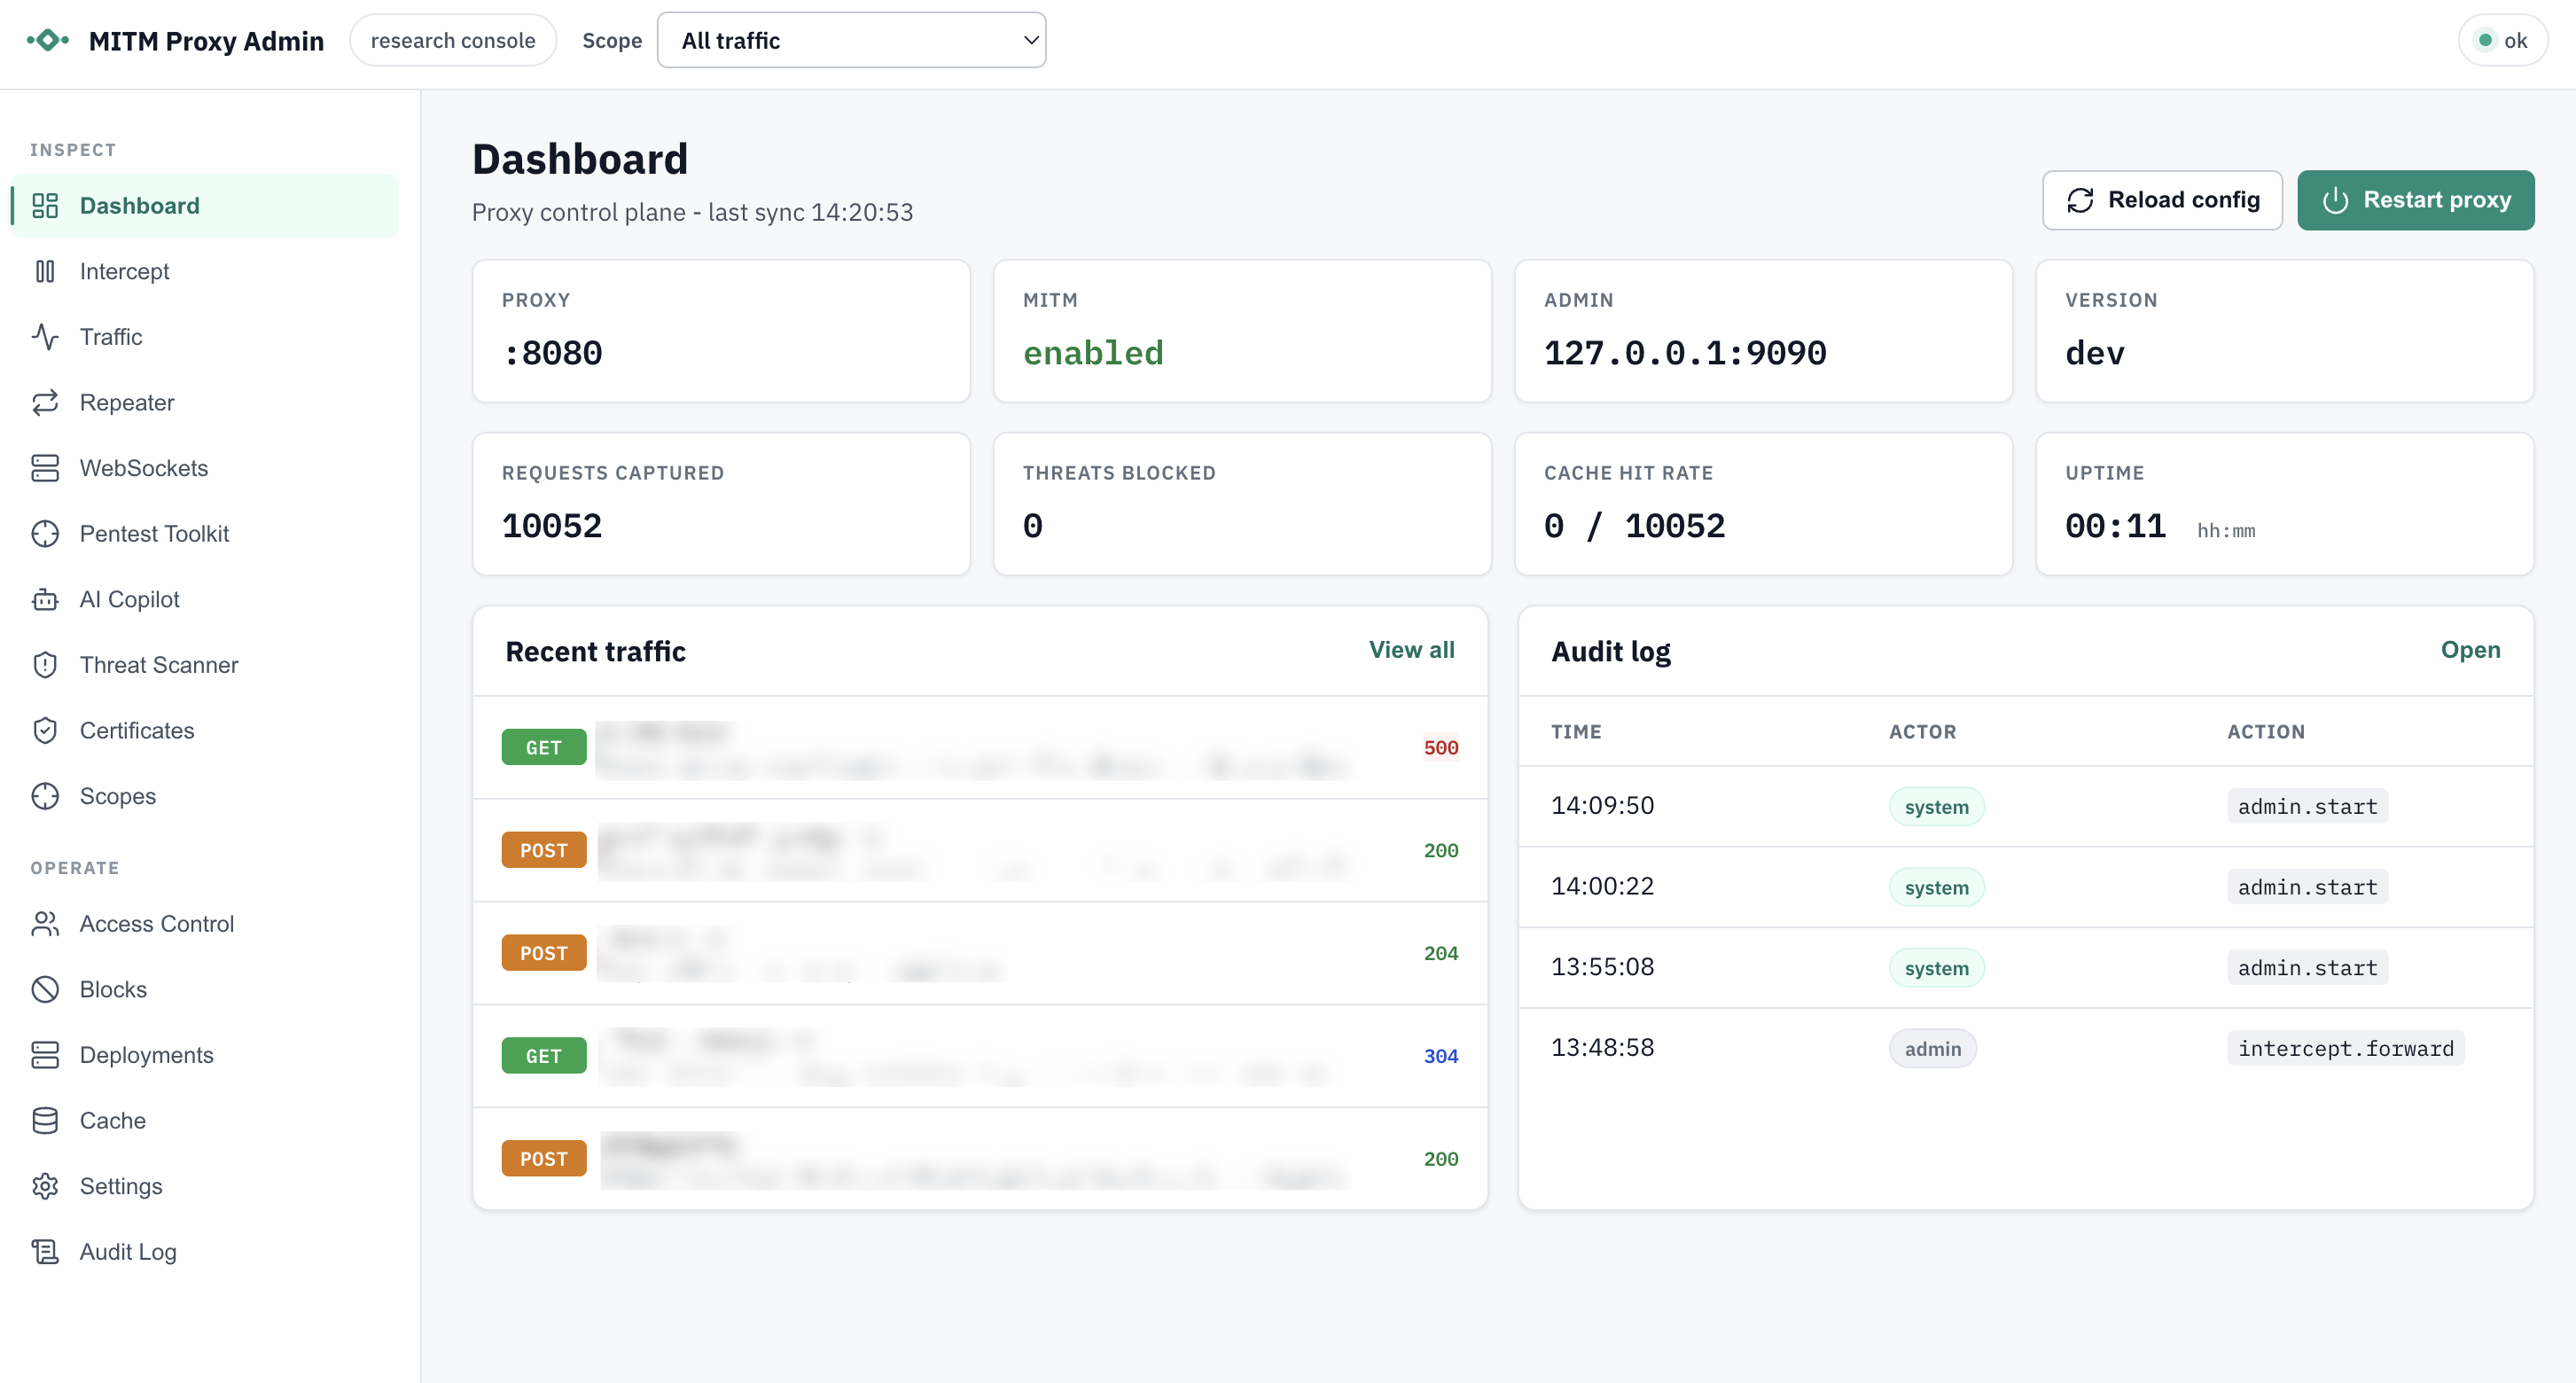 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 xxconi/cve-2026-6271
Automated scanner for CVE-2026-6271, a critical unauthenticated arbitrary file upload leading to RCE in the WordPress Career Section plugin. Supports…
 yugo-eliatrope/test-cve-2025-29927
Demo app to exploit CVE-2025-29927: NextJS middleware bypass via proxy-injected headers for unauthorized /admin access. Includes vulnerable app and…
 nles-crt/cve-2023-6895
Python script to scan websites for CVE-2023-6895 vulnerability. Sends crafted requests, checks responses, and logs exploitable URLs with progress bar…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 emredavut/cve-2025-55182
Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…