
conti-pentester-guide-leak
 forbiddenprogrammer/conti-pentester-guide-leak
Leaked pentesting manuals given to Conti ransomware crooks
curated-resourceseducationpenetration-testing+1
1.1k
forbiddenprogrammer/conti-pentester-guide-leakLeaked pentesting manuals given to Conti ransomware crooks
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events

 secml/secml
A Python library for Secure and Explainable Machine Learning Documentation available @ https://secml.gitlab.io Follow us on Twitter @…
 jmaddington/serious-sam---cve-2021-36934-mitigation-for-datto-rmm
PowerShell script to apply Microsoft and US CERT mitigation measures for CVE-2021-36934 (Serious SAM) via Datto RMM, with UDF-based status tracking.
 vxunderground/malwaresourcecode
Collection of malware source code for a variety of platforms in an array of different programming languages.
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
 droid-ash/finalrun-agent
AI-driven CLI for testing Android and iOS apps using natural language. Generates, runs, and fixes end-to-end tests on emulators/simulators with…
 nu11secur1ty/kali-linux
Kali Linux advanced setup
 raspberrypi/rp2350_hacking_challenge
Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…
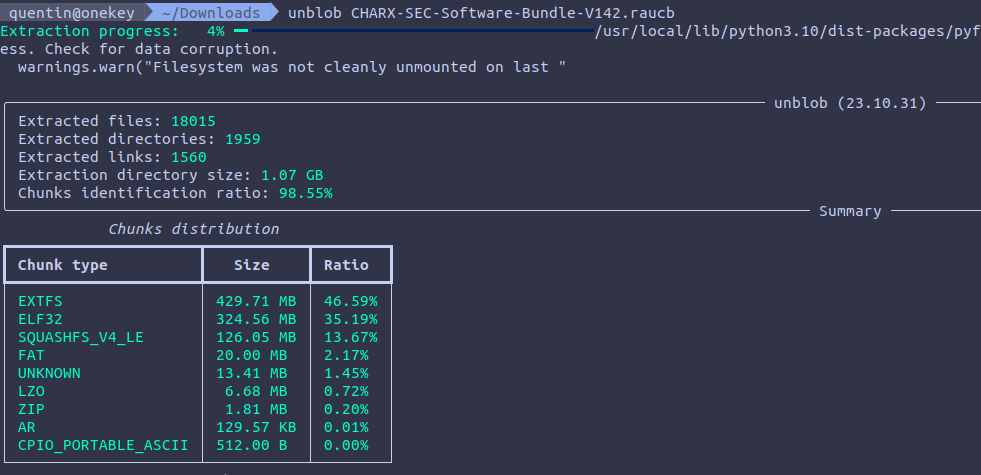 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 spyboy-productions/spyboy-productions
Discord bot providing cybersecurity tools, information gathering, and community-driven resources for security enthusiasts and CTF participants.
 argp/cve-2011-3026-firefox
Example of exploiting CVE-2011-3026 on Firefox (Linux/x86)
 aeyesec/cve-2023-22432
PoC for CVE-2023-22432 (web2py)
 khoatran107/cve-2024-58239
Linux kernel TLS subsystem exploit for CVE-2024-58239, achieving privilege escalation via a double-free vulnerability in tcp_rcv_state_process.…