
Paste2Web
 d4vinci/paste2web
A python3 script that uses cl1p website to send and receive secret messages
data-exfiltrationeducationencryption-decryption-tools+2
319 years ago
d4vinci/paste2webA python3 script that uses cl1p website to send and receive secret messages
 nxploited/cve-2025-8570
BeyondCart Connector <= 2.1.0 - Missing Configuration of JWT Secret to Unauthenticated Privilege Escalation
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…
 faridi-m/cve-2021-22911-rocketchat
Exploit for Rocket.Chat 3.12.1 RCE via pre-auth NoSQL injection, leaking admin TOTP secret and password reset token to achieve remote code execution…
 tar-xz/cve-2026-53519-poc
PoC exploit for CVE-2026-53519.
 oscerd/cve-2024-22369
CVE-2024-22369 Reproducer
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 raspberrypi/rp2350_hacking_challenge
Raspberry Pi RP2350 hacking challenge: extract a 128-bit OTP secret protected by secure boot and OTP lock, with setup scripts and firmware for Pico 2…
 pastea/cve-2017-1000486
Multi-step proof-of-concept exploit for CVE-2017-1000486 (PrimeFaces EL injection) with padding oracle secret retrieval and blacklist-bypassing…
 smalltown123/details-for-cve-2022-46505
MatrixSSL session resume bug
 cedricbonhomme/stegano
A pure Python steganography module.
 thewhiteh4t/llmreaper
Passive LLM Conversation Capture & Sensitive Data Exposure Research

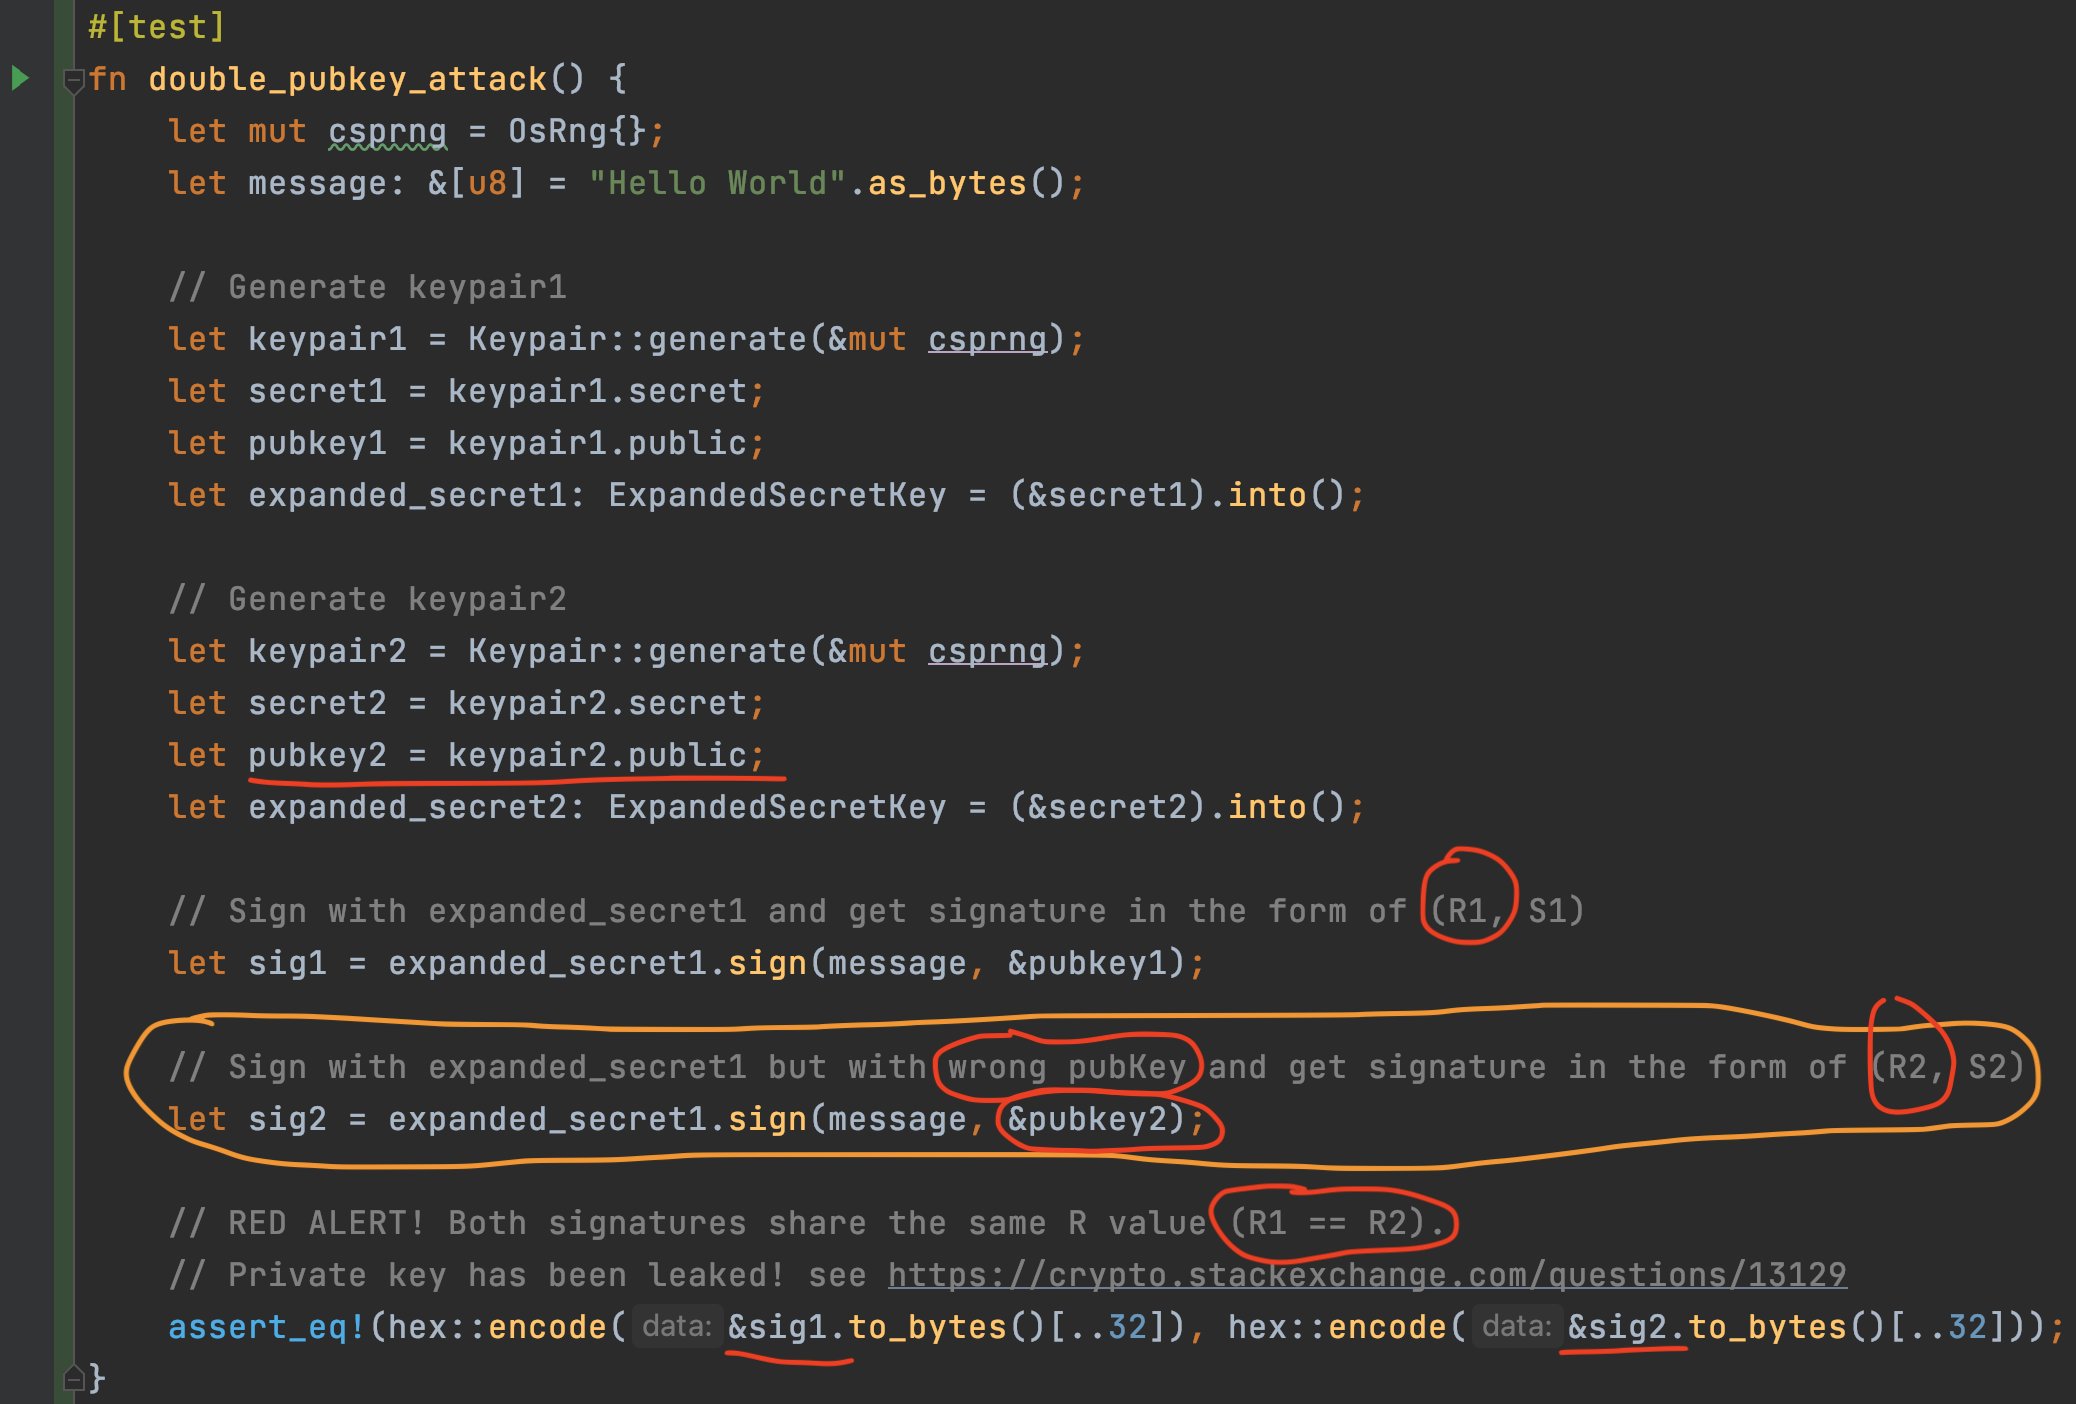 mystenlabs/ed25519-unsafe-libs
List of unsafe ed25519 signature libs
 tbrockman/recipe-blog-encoding
Hide valuable information where it's least expected
 toddmaustin/mojo-v
RISC-V ISA extension for hardware-enforced secret computation using ML-KEM-512 key encapsulation and SIMON-128 encryption, enabling data-oblivious…