
htb-ctf-walkthroughs
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
ctfeducationexploitation+6
rootsecnz/htb-ctf-walkthroughsWalkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
 sanasimran1403-jpg/log4shell
Log4Shell (CVE-2021-44228) research report — technical breakdown, root cause analysis, and end-to-end lab-reproduced exploit chain with evidence…
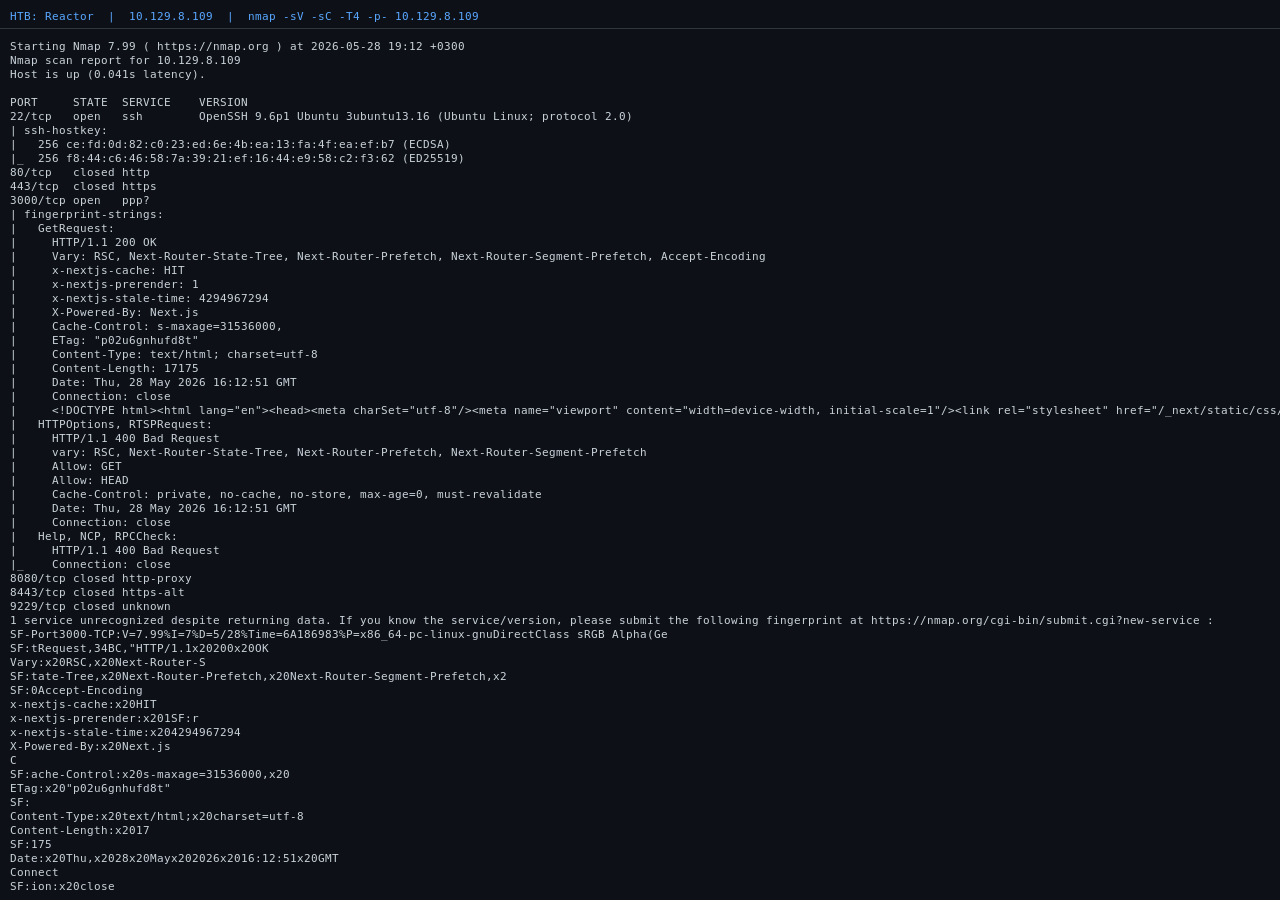 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 j0qq3r/cve-2025-52204
Coordinated disclosure of CVE-2025-52204: reflected XSS and HTML injection in Znuny OTRS customer.pl endpoint. Includes technical summary, affected…
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 tolu12wani/demonstration-of-cve-2023-38831-via-reverse-shell-execution
This project demonstrates a simulated exploitation of the WinRAR vulnerability CVE-2023-38831 to execute a reverse shell. The purpose of this task…
 kiruthikan99/it19115276
SNP Assignment 1 Report - Linux box exploitation ( Vulnerability CVE-2014-0038)
 taurusomar/pulsegram
Python-based keylogger with Telegram bot integration for capturing keystrokes, clipboard content, and screenshots in authorized security testing…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 sloden1977-lang/root-zte-x1001
Magisk root guide for ZTE Blade X1001 (Android 15, Unisoc UMS9230) using CVE-2022-38694 exploit. Contributions and screenshots welcome.
 adnansiyat/how-to-patch-cve-2025-32709
Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…
 calesthio/crucix
Your personal intelligence agent. Watches the world from multiple data sources and pings you when something changes.
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.