BLT
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
curated-resourcesdevsecopseducation+7
115h 20m ago
owasp/bltMonorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 janhalendk/react
A OSINT project that explores how to dump data from React
 0xk4rth1/cve-2025-2304
A critical mass assignment vulnerability in Camaleon CMS (< 2.9.1) allows authenticated low-privileged users to elevate their privileges to…
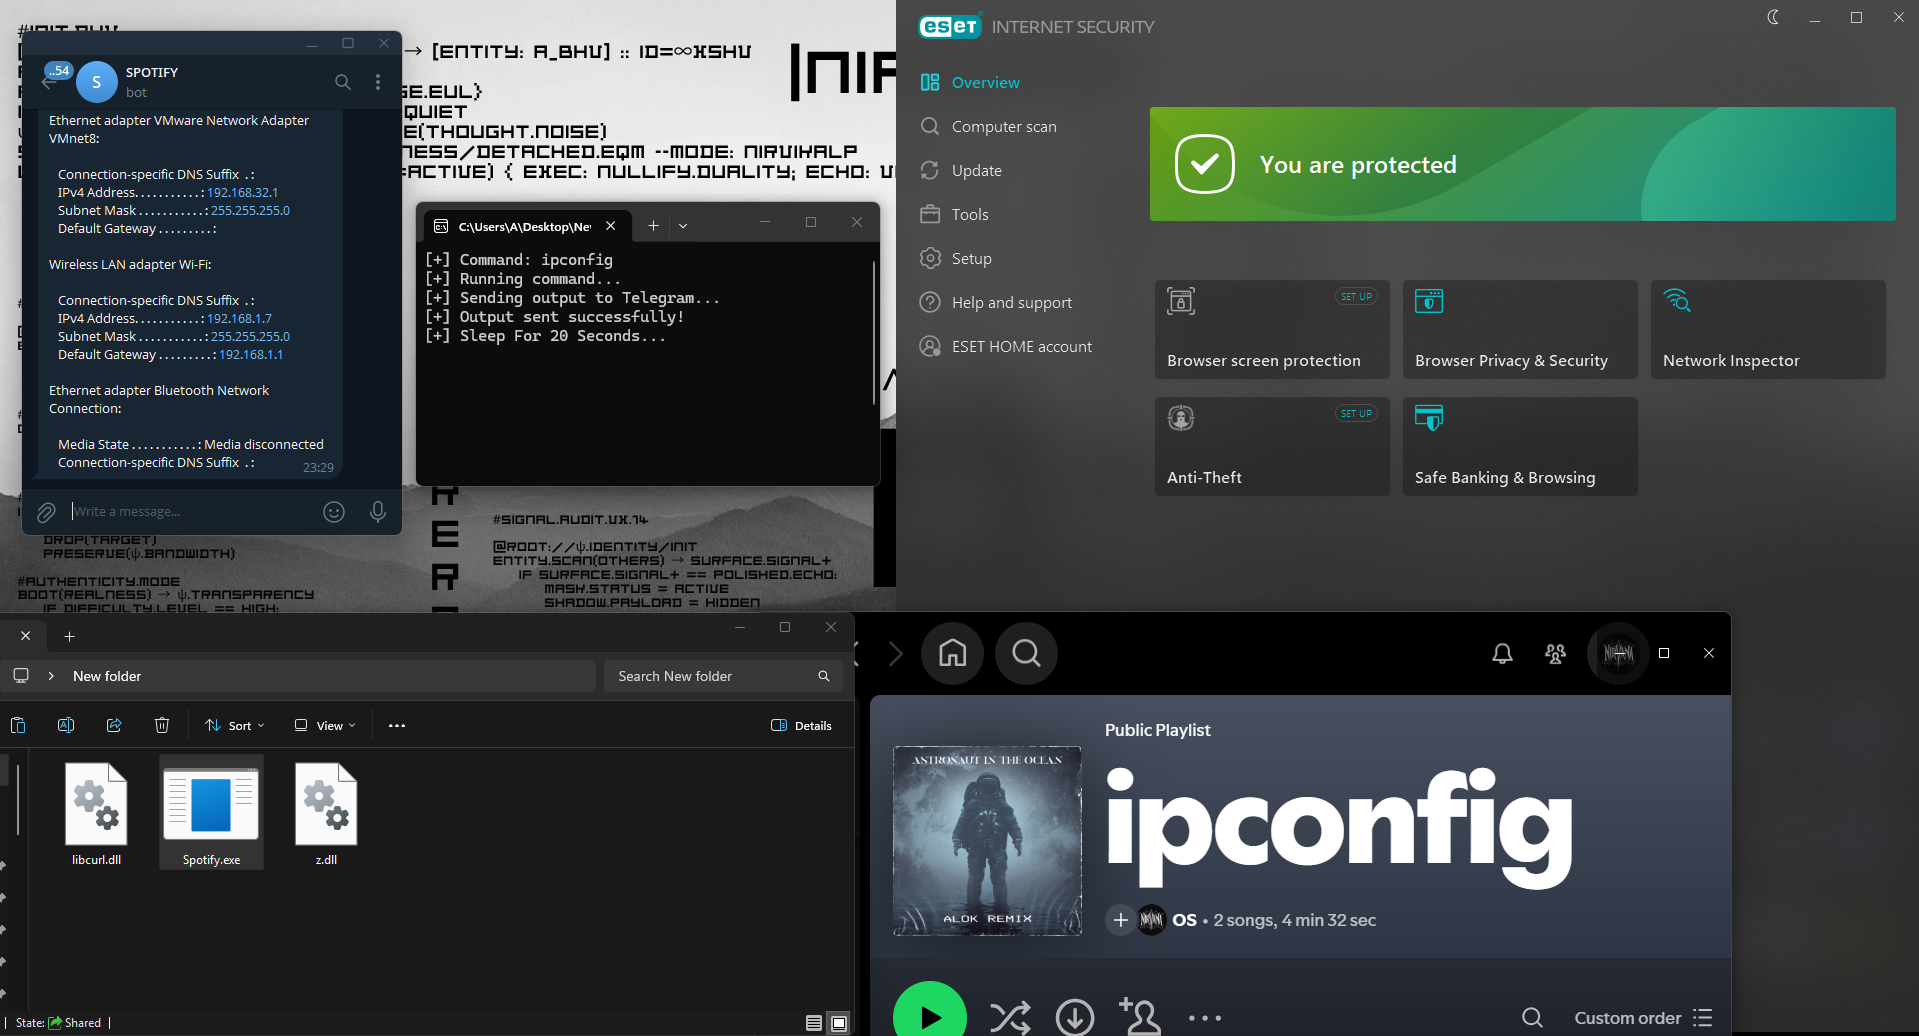 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 ricsirigu/cve-2025-29927
A deliberately Next.js app, vulnerable to CVE-2025-29927, Authorization Bypass
 prime-radiant-inc/superpowers-evals
Behavioral eval lab (Quorum) for the superpowers project that drives real coding-agent CLIs (Claude, Codex, Gemini, Kimi, and more) through a QA…
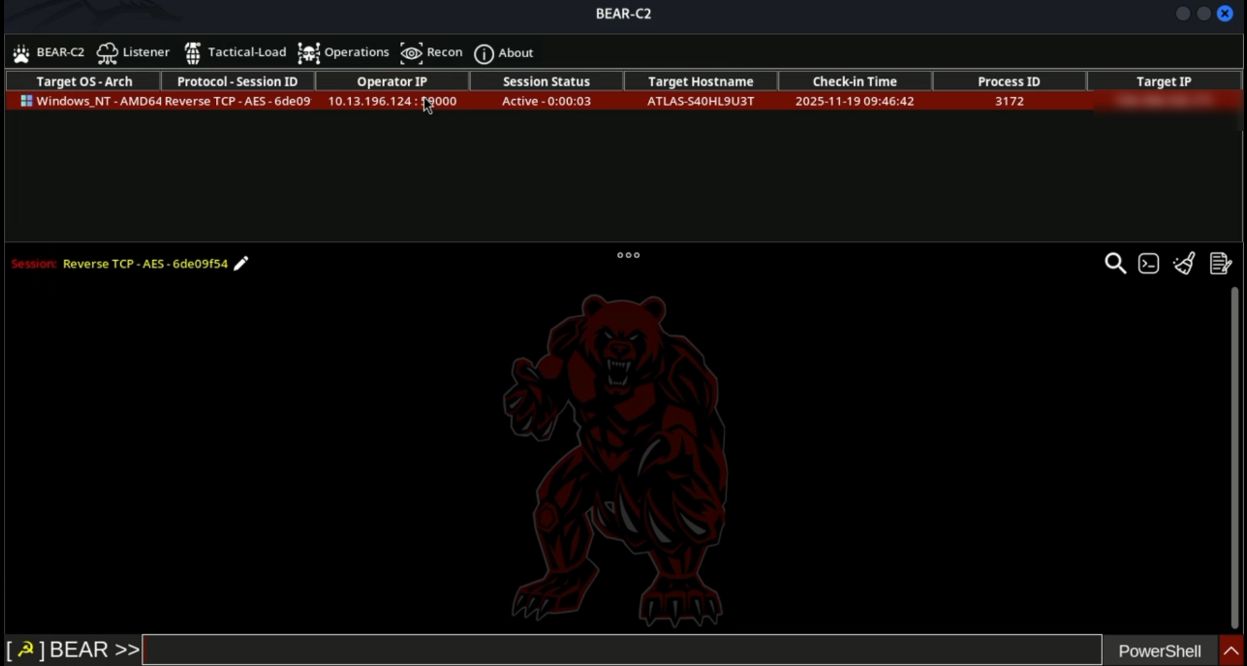 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
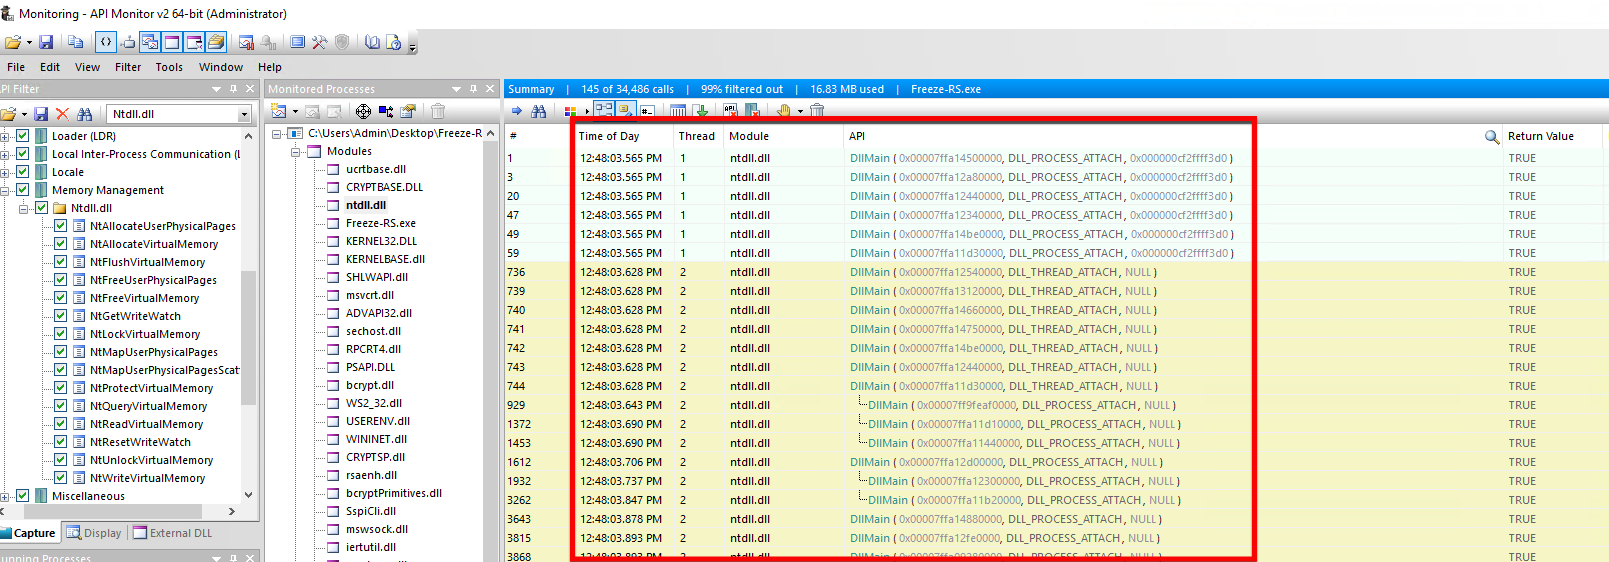
 edu0x01/hack-tools
Project that brings together several pentest tools
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 nhas/vulnerable-cve-2024-45337
An example project that showcases golang code vulnerable to CVE-2024-45337