
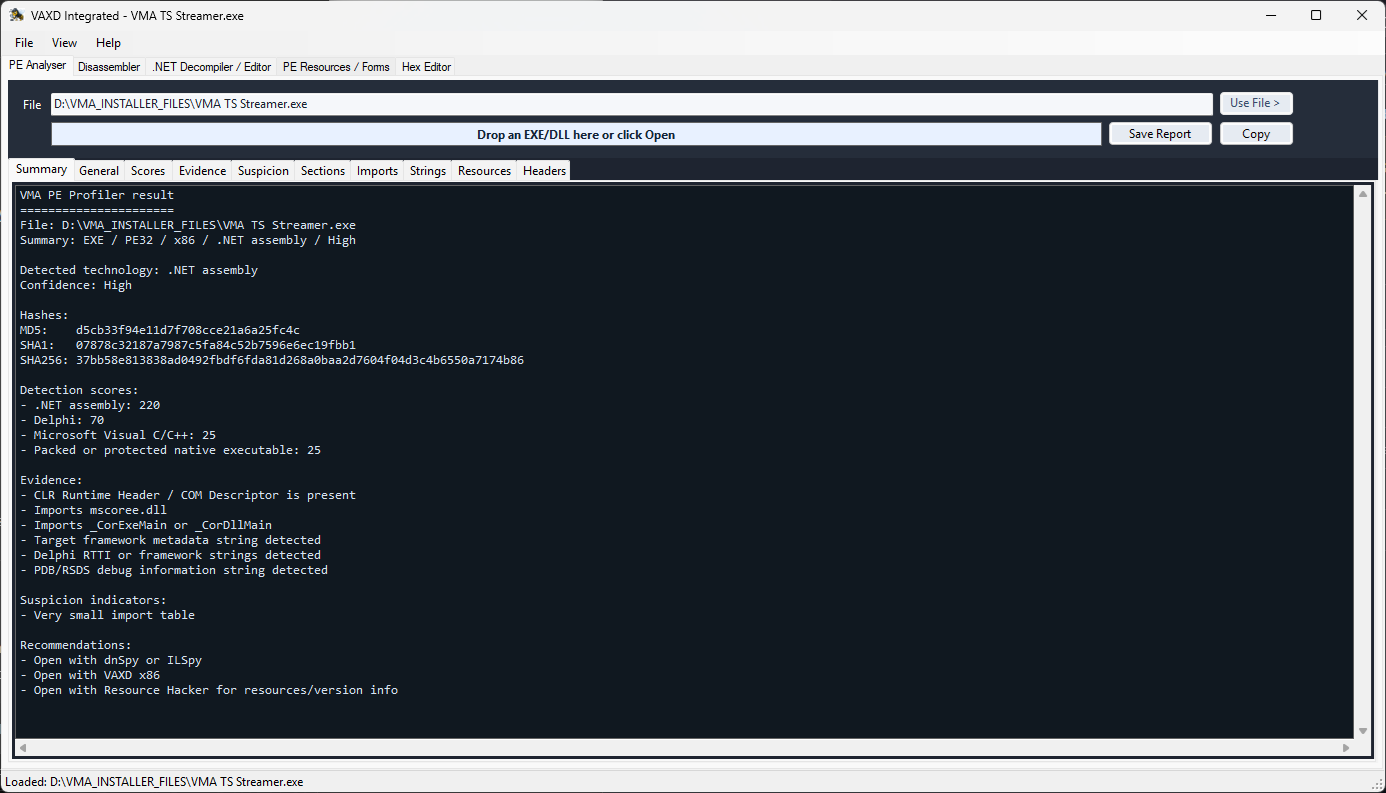
VAXD
 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
binary-analysisdebuggersdigital-forensics+7
bicurico/vaxdLightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]

 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
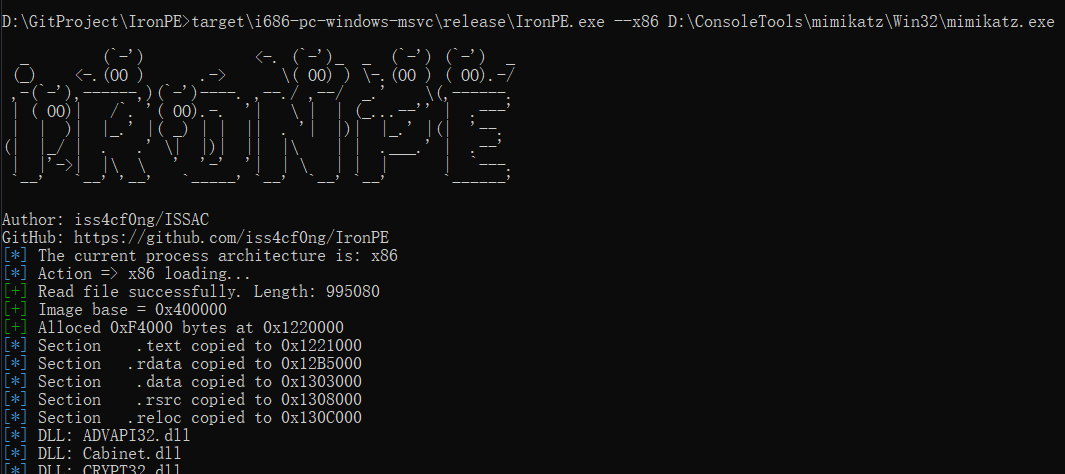 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 maldev-academy/ghostlyhollowingviatamperedsyscalls2
Implementing Ghostly-Hollowing using tampered syscalls for remote PE injection
 onhexgroup/tabpe
A monthly Windows PE baseline dataset for Cyber security researchers
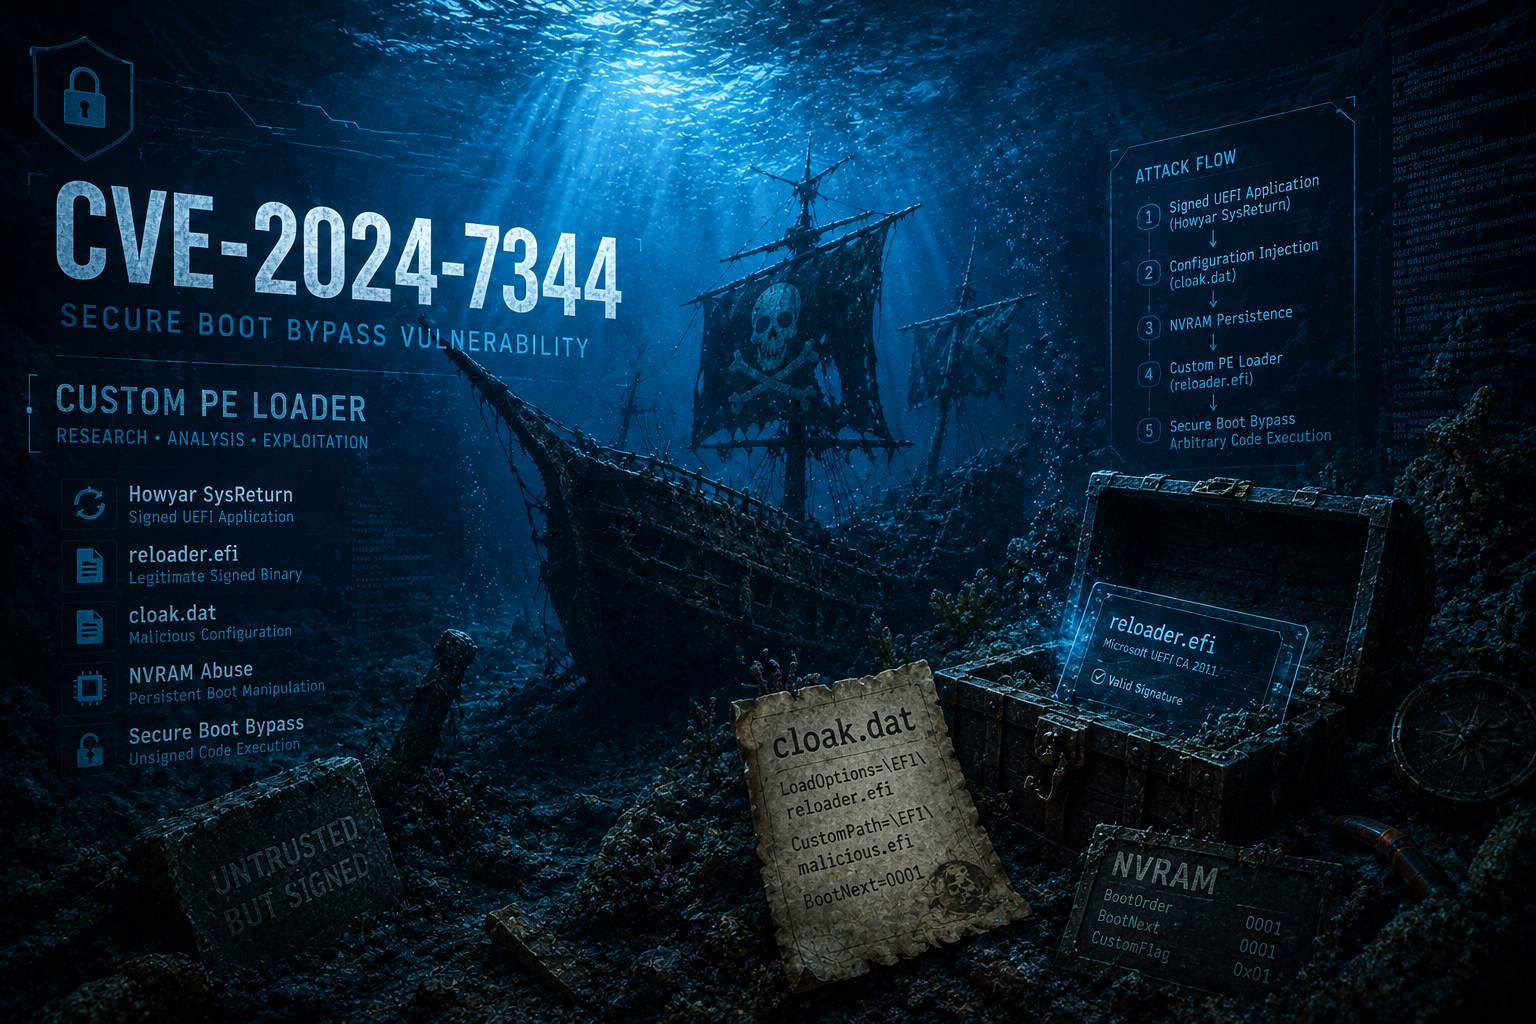 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
 eynaexp/copy-fail-cve-2026-31431-modernized
Proof-of-concept exploit for CVE-2026-31431, modernized from the original Copy Fail PE exploit. Demonstrates the vulnerability for educational…
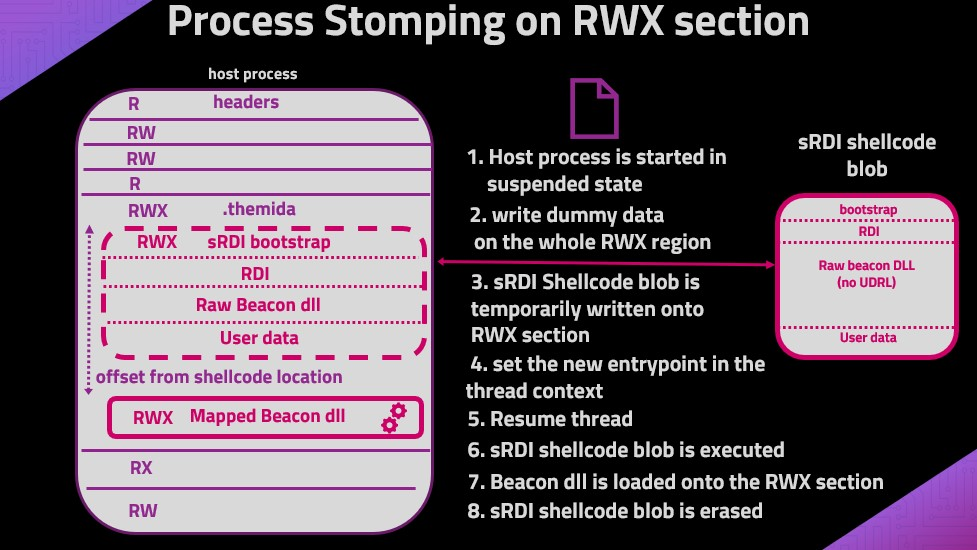 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery