
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
20 results
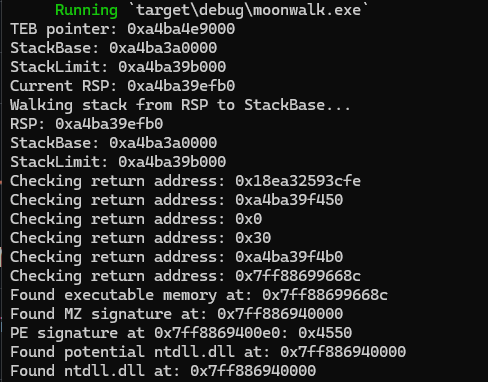
moonwalk preview

moonwalk

GitHubteach2breach/moonwalk

find dll base addresses without PEB WALK
binary-analysiseducationpayload-development+2
1701 year ago
CVE-2025-24076 preview

CVE-2025-24076

GitHubmbanyamer/cve-2025-24076

Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
binary-exploitationeducationexploitation+3
181 year ago
From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack preview

From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack

GitHubmrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack

It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
educationexploitationincident-response+4
1 year ago
CVE-2024-6769 preview

CVE-2024-6769

GitHubfortra/cve-2024-6769

Technical writeup and PoC for CVE-2024-6769, chaining DLL hijacking with activation cache poisoning to escalate from medium to high integrity on…
binary-exploitationeducationexploitation+3
782 years ago
CVE-2023-6401 preview

CVE-2023-6401

GitHubmekitoci/cve-2023-6401

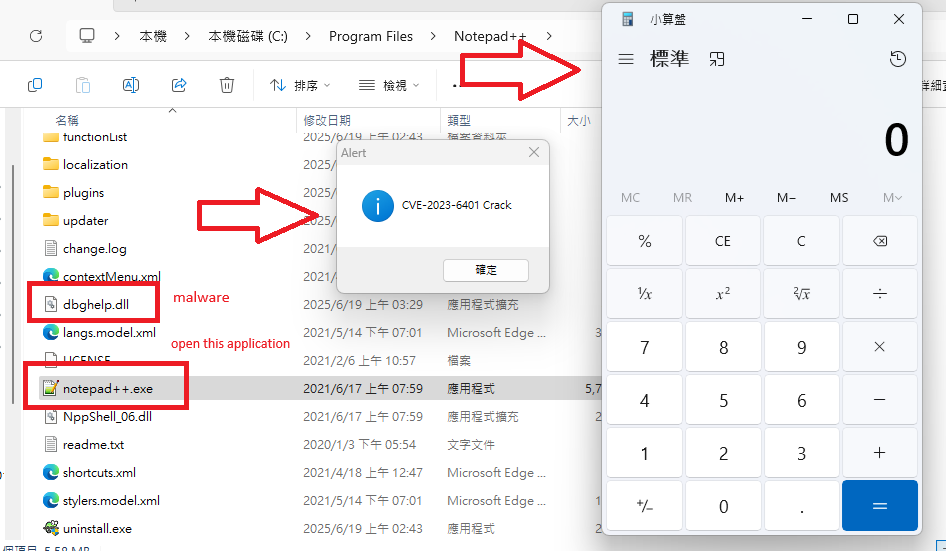
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
binary-exploitationeducationexploitation+2
1 year ago
HijackLibs preview

HijackLibs

GitHubwietze/hijacklibs

Project for tracking publicly disclosed DLL Hijacking opportunities.
curated-resourceseducationinformation-gathering+3
9273 days ago
CVE-2026-50343-InstallService-EoP preview

CVE-2026-50343-InstallService-EoP

GitHubrat5ak/cve-2026-50343-installservice-eop

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
binary-exploitationeducationexploitation+3
483 months ago
CVE-2021-36934 preview

CVE-2021-36934

GitHubwebsecnl/cve-2021-36934

SeriousSAM Auto Exploiter
educationexploitationpassword-cracking+2
25 years ago
TeamViewer_Permissions_Hook_V1 preview

TeamViewer_Permissions_Hook_V1

GitHubgellin/teamviewer_permissions_hook_v1

A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
educationexploitationlateral-movement+5
3108 years ago
CVE-2026-4255 preview

CVE-2026-4255

GitHubard33/cve-2026-4255

Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
binary-exploitationeducationexploitation+4
15 months ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.

binary-analysiseducationlabs-practice+6
1591 year ago
DLLHijackHunter preview

DLLHijackHunter

GitHubghostvectoracademy/dllhijackhunter

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
3961 month ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

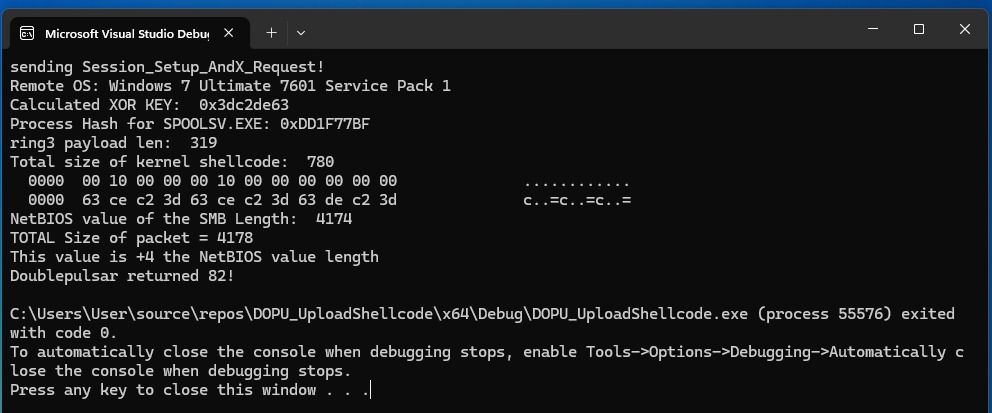
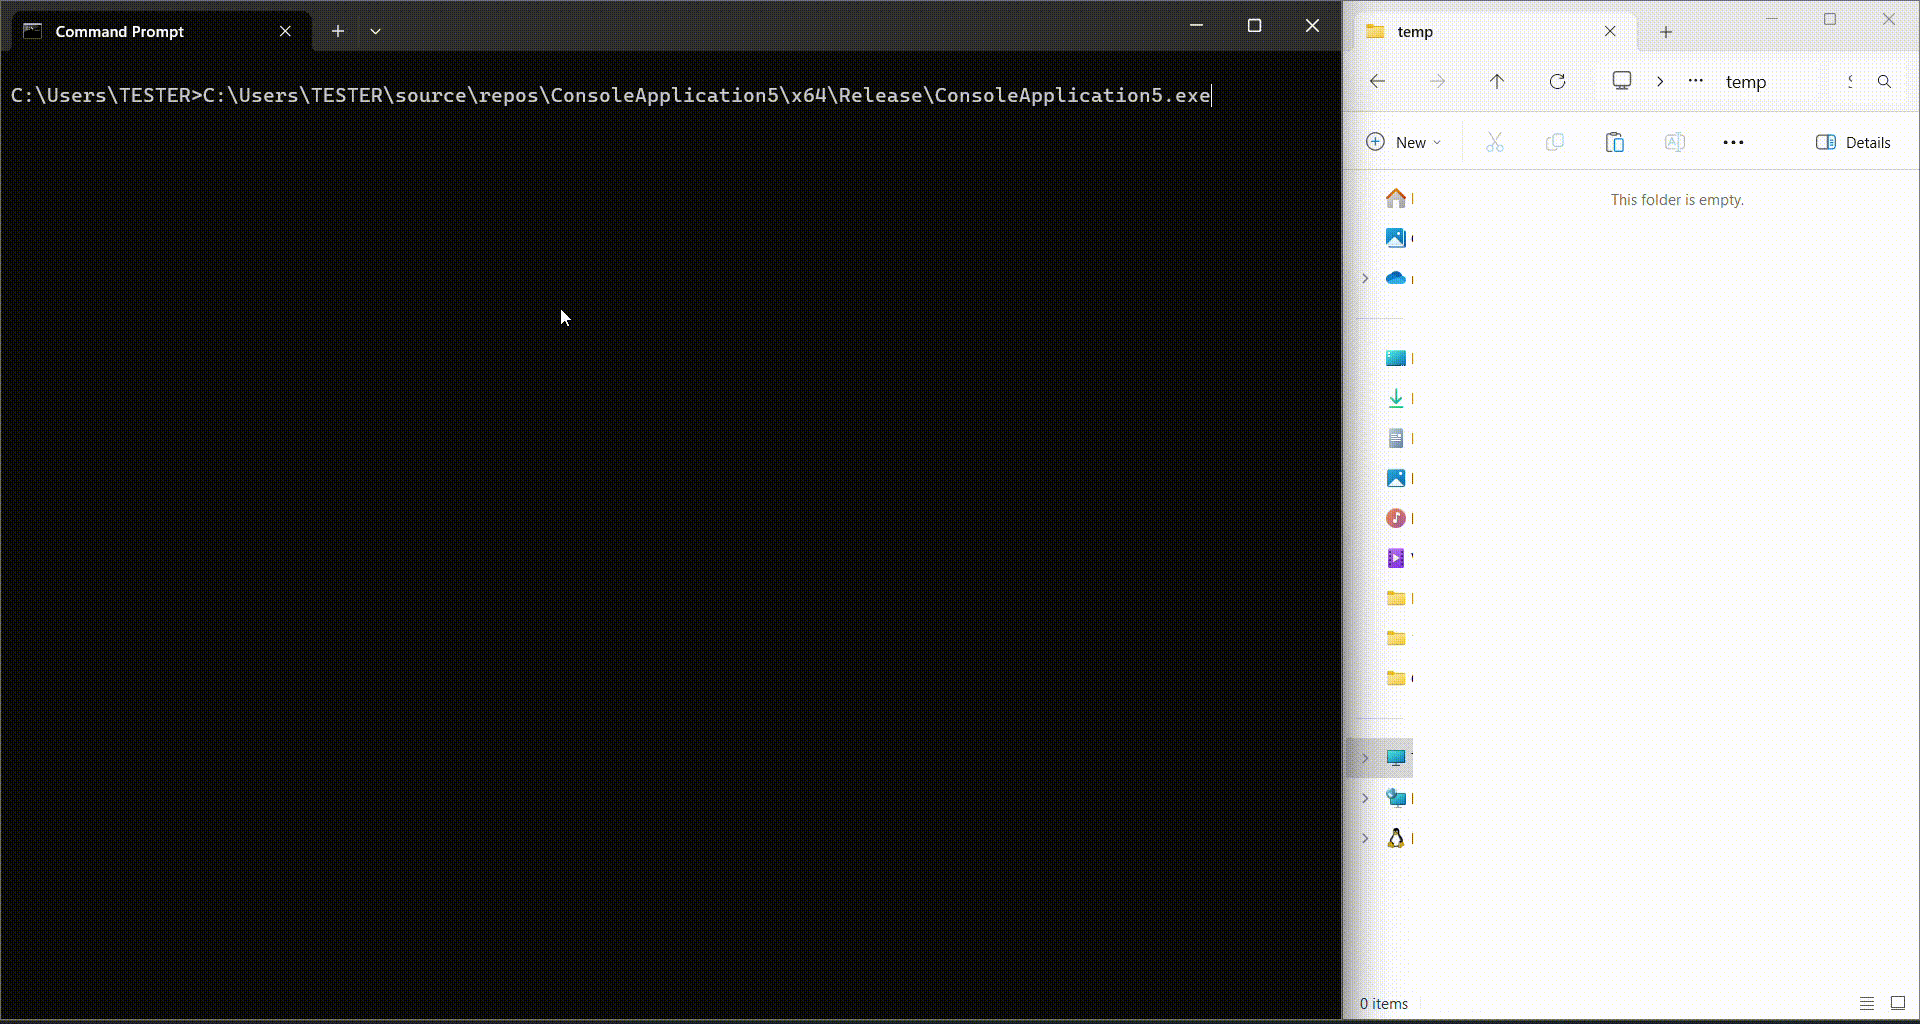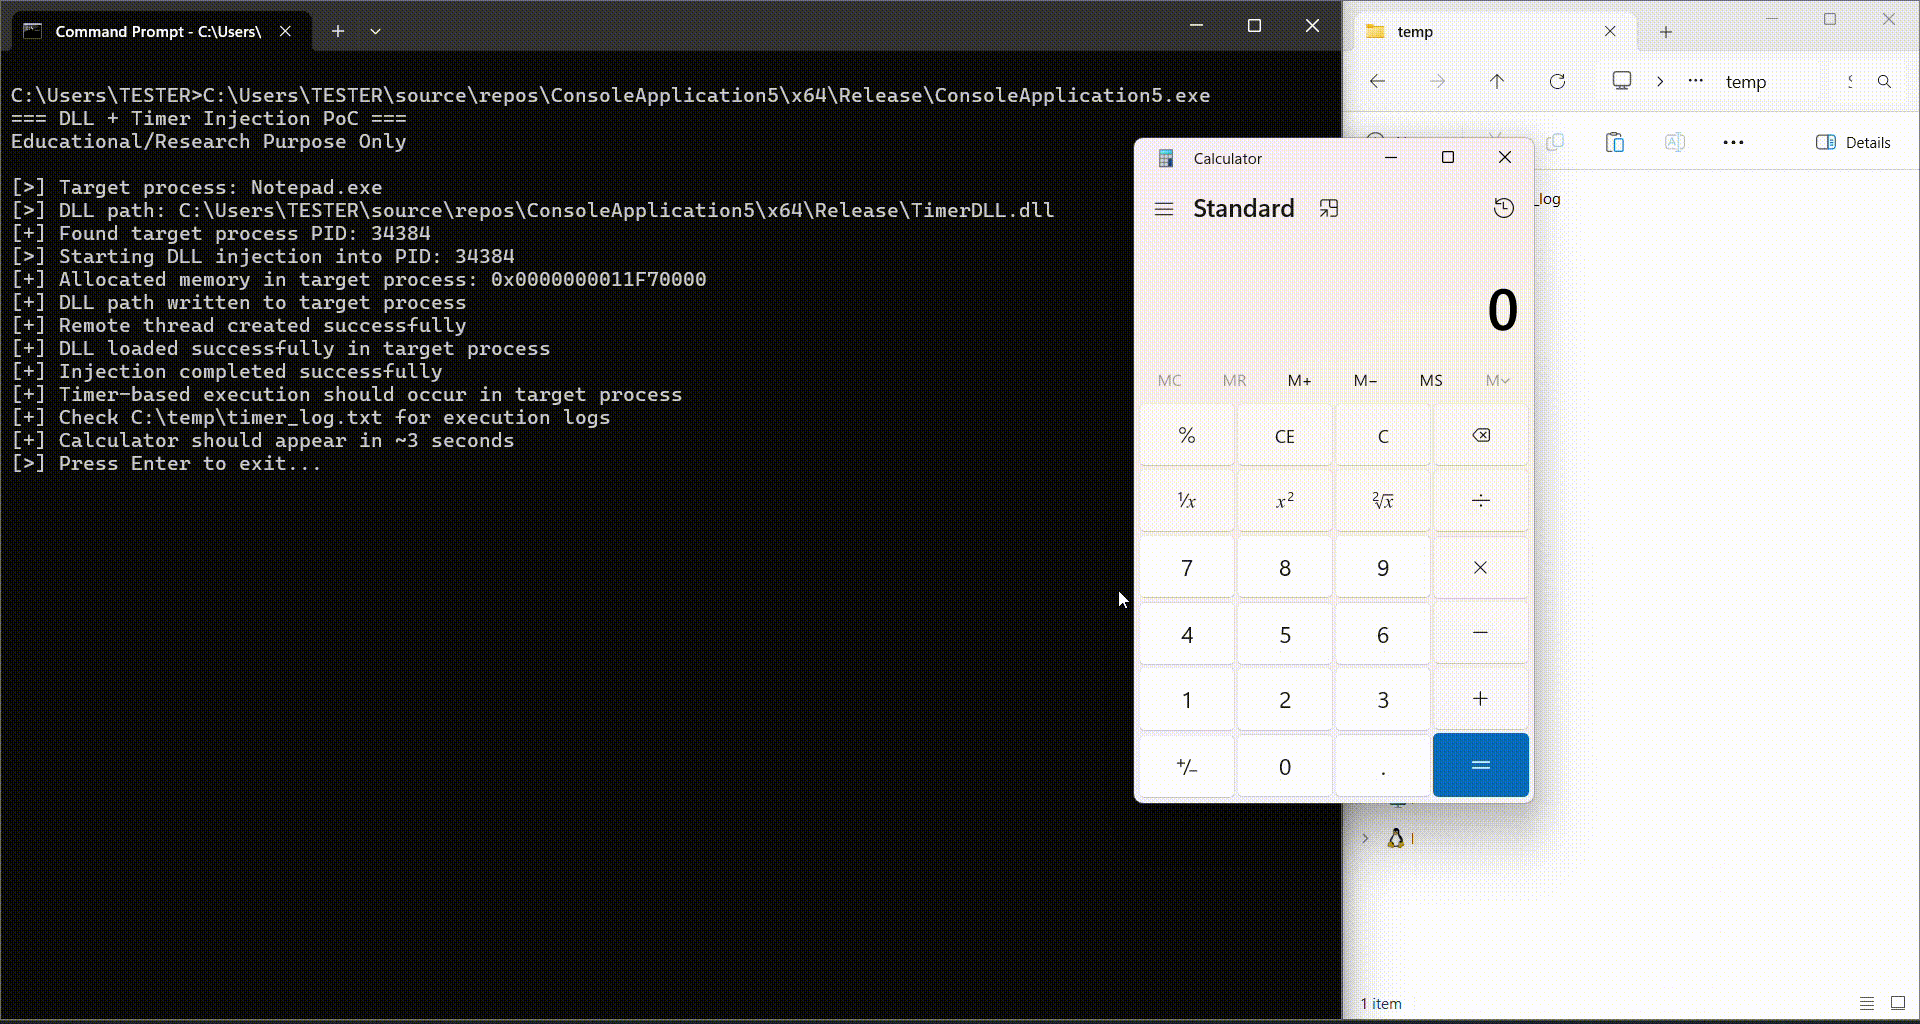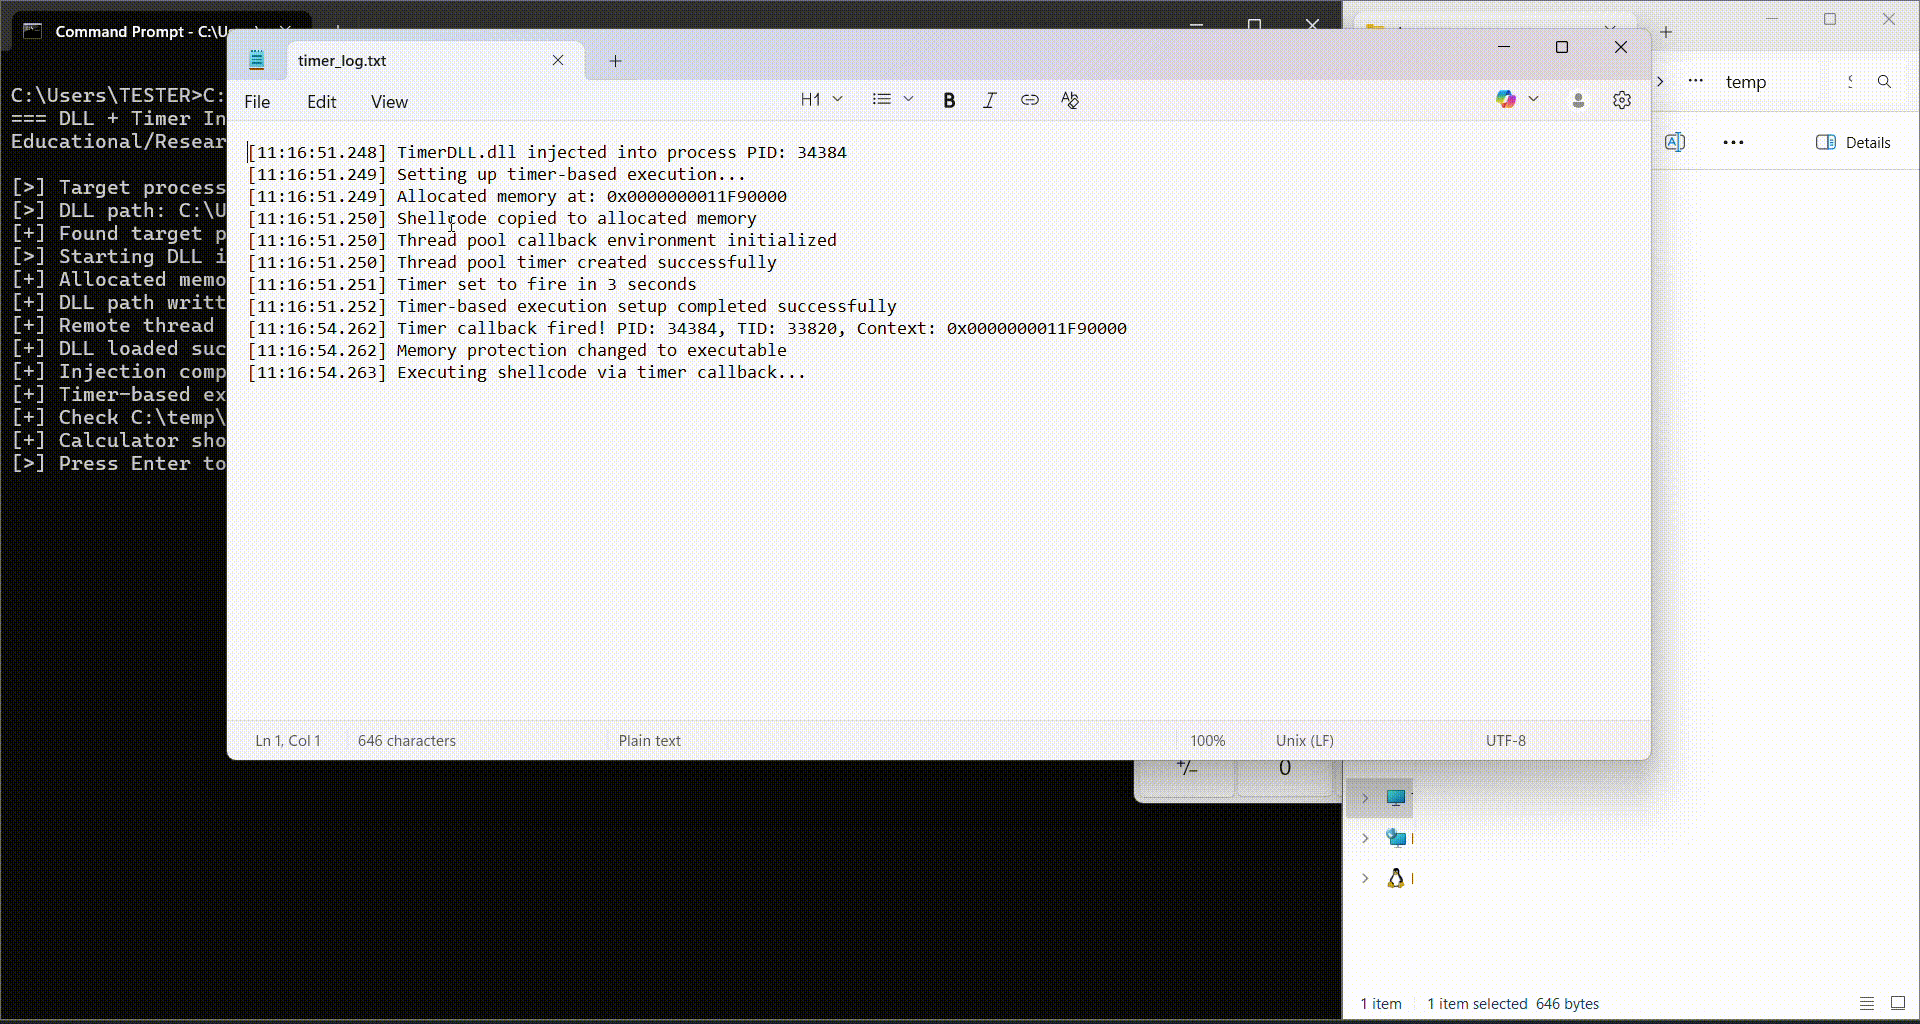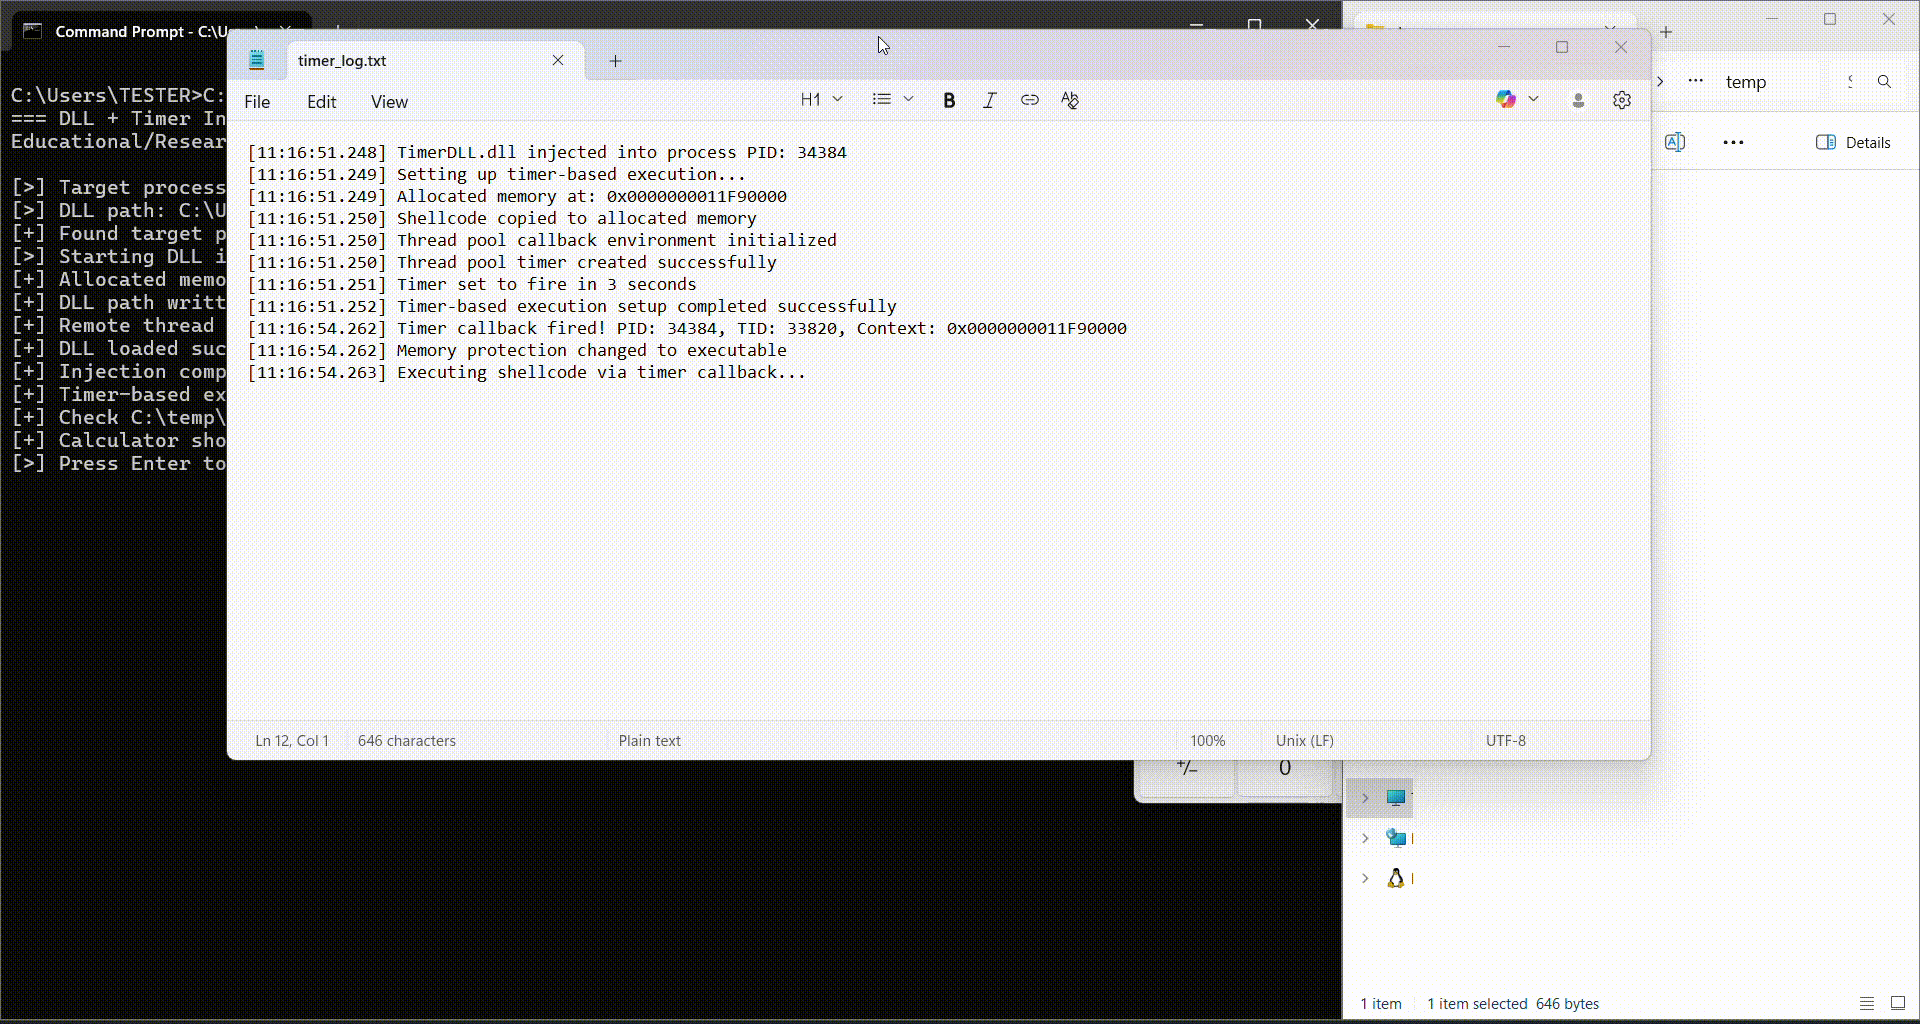
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
6131 month ago
Remote-DLL-Injection-with-Timer-based-Shellcode-Execution preview

Remote-DLL-Injection-with-Timer-based-Shellcode-Execution

GitHubandreisss/remote-dll-injection-with-timer-based-shellcode-execution

Remote DLL Injection with Timer-based Shellcode Execution
educationexploitationpayload-development+3
2161 year ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHubpaddycahil/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
curated-resourceseducationmalware-analysis+3
1212 years ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
educationexploitationlabs-practice+5
424 months ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
defensive-toolsdigital-forensicseducation+6
11 month ago
CVE-2024-38077-MadLicense-exploit preview

CVE-2024-38077-MadLicense-exploit

GitHubermensonx/cve-2024-38077-madlicense-exploit

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…

binary-exploitationeducationexploitation+6
110 months ago
Previous12Next