
vcamper
 rndhouse/vcamper
PoC: identify silent security patches before CVE
code-analysiseducationinformation-gathering+3
rndhouse/vcamperPoC: identify silent security patches before CVE
 pvharmo2/gha-lab-360f77d0d4
Reproduces CVE-2026-39866, a workflow_dispatch input template injection in a GitHub Actions workflow, using a pinned snapshot of the vulnerable…
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 franklinf25/cve-2026-42945
Analyzes CVE-2026-42945, an NGINX rewrite heap overrun, providing a differential detector, deterministic DoS PoC, and a credited RCE port with…
 halcy0nic/cve-2022-36234
Proof of concept for CVE-2022-36234
 markakd/cve-2022-2588
exploit for CVE-2022-2588
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
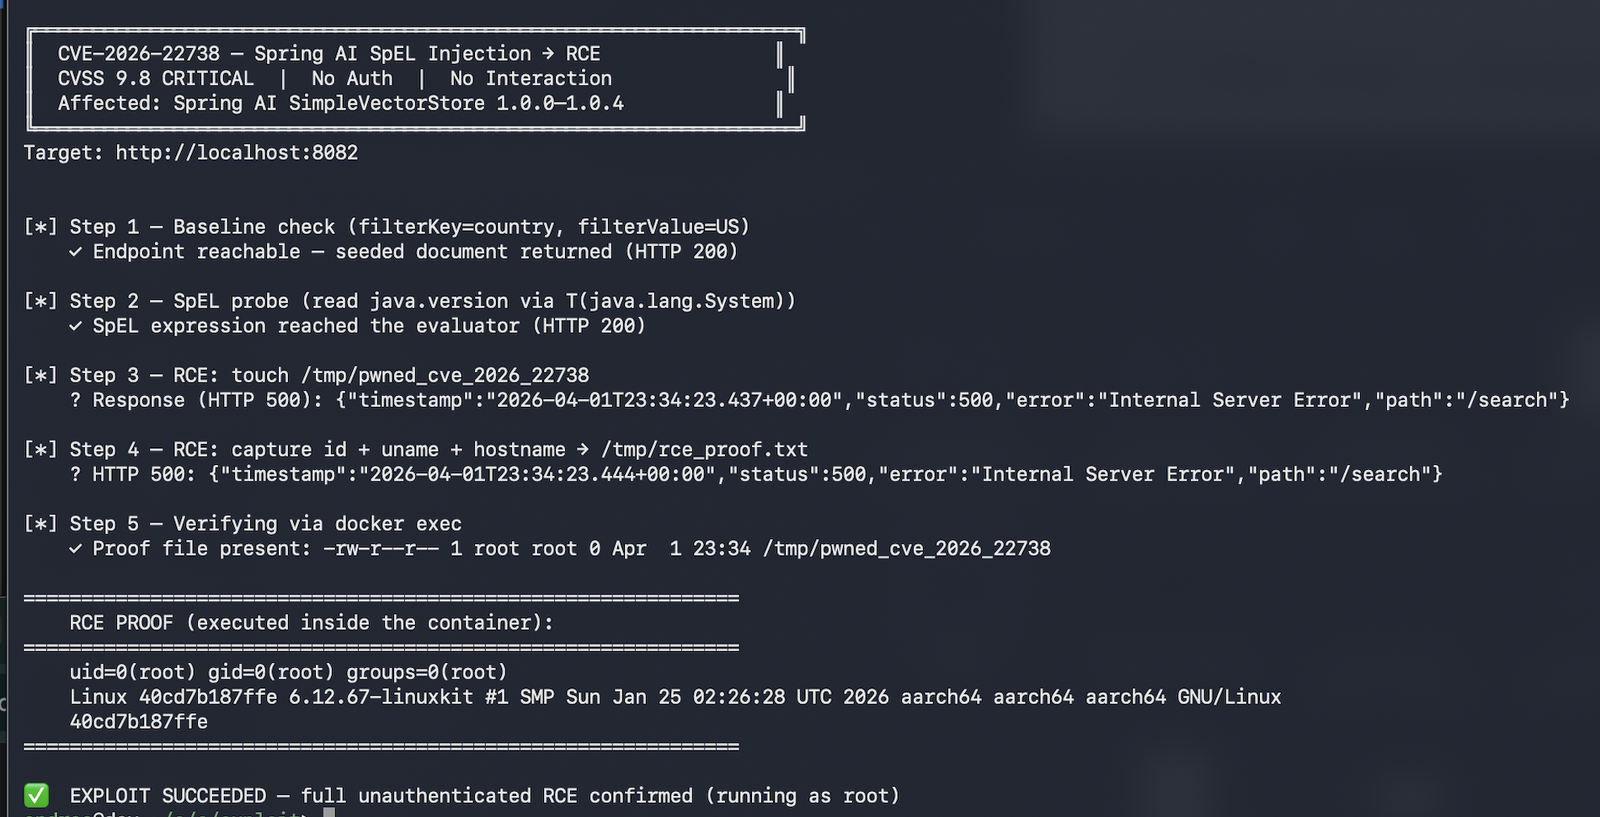 n0n4m3x41/cve-2026-22738-poc
Proof-of-concept exploit for CVE-2026-22738, a critical SpEL injection RCE in Spring AI SimpleVectorStore, demonstrating unauthenticated OS command…
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 dom4570/cve-2022-2588
Detailed write-up and exploit code for CVE-2022-2588, a Linux kernel use-after-free in route4_change leading to privilege escalation via double-free…
 igr1s-red/cve-2022-2588
Exploit code for CVE-2022-2588
 omar2535/cve-2022-39275
CVE-2022-39275 Setup and POC
 hikame/cve-2018-17144_poc
Put the *.py files to test/functional folder of bitcoin sourcecode (commit: 4901c00792c1dabae4bb01e6373c9b1ed9ef3008)
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 chuzhongyun/cve-2026-53359-kernel-fix
Linux 内核升级指南 - 修复 CVE-2026-53359
 pvharmo2/gha-lab-b16a4f3554
Security-research lab: CVE-2026-24480 pull_request_target pre-commit RCE in qgis/QGIS (snapshot at vulnerable commit)
 mohnad-al-saif/gitea-git-hooks-rce-cve-2020-14144-
Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…