
mutillidae
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
ctfeducationlabs-practice+3
1.5k
webpwnized/mutillidaeOWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 six2dez/wahh_extras
The Web Application Hacker's Handbook - Extra Content
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 digininja/dvwa
Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
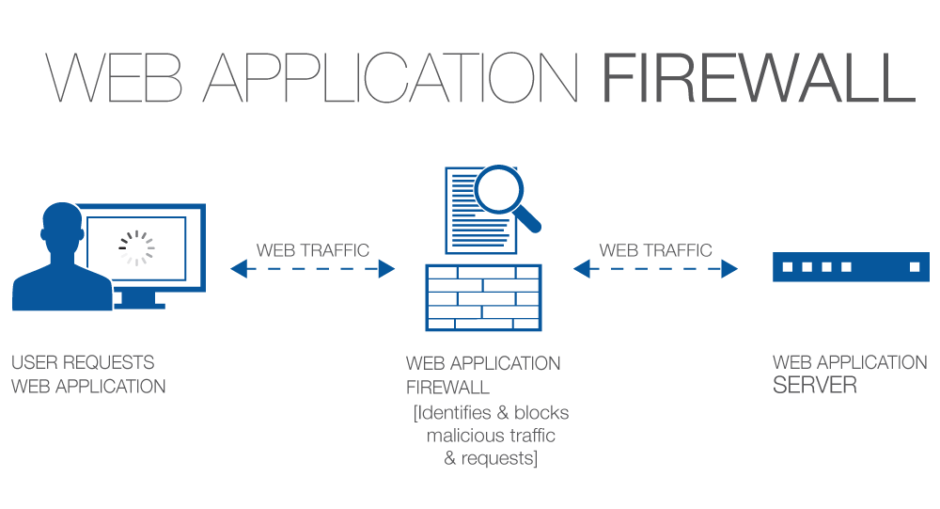 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
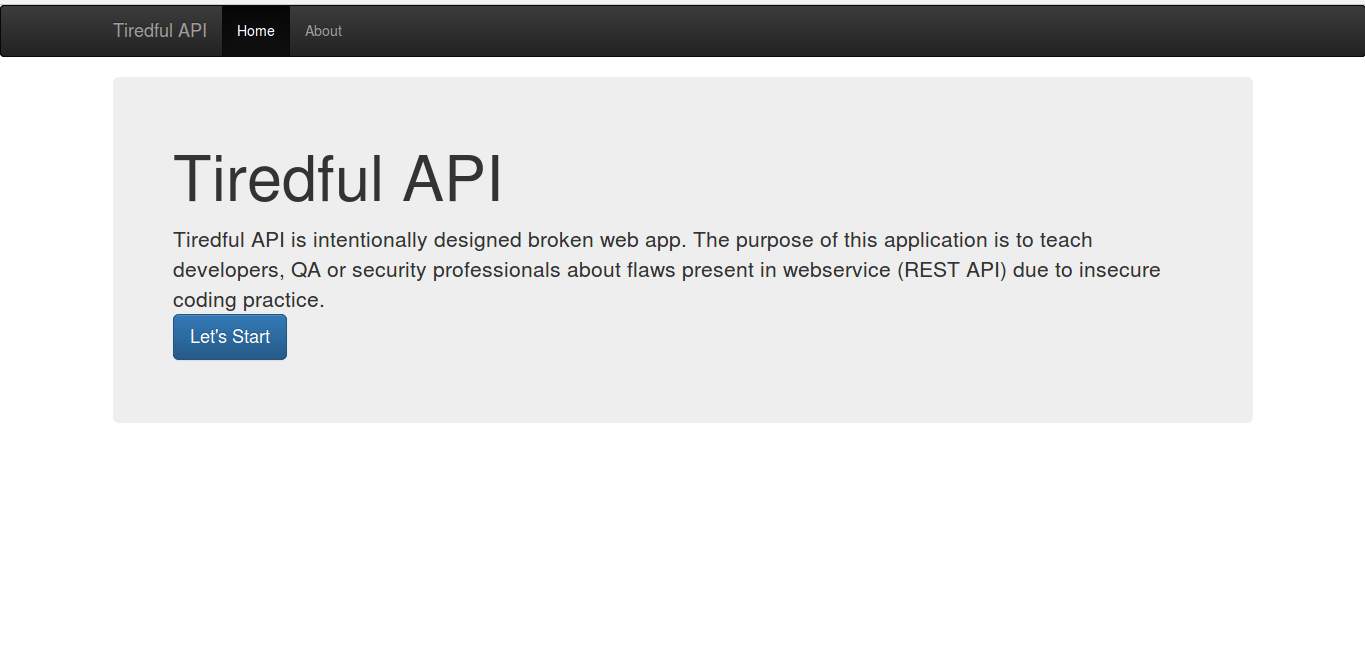 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
 adeyosemanputra/pygoat
intentionally vuln web Application Security in django
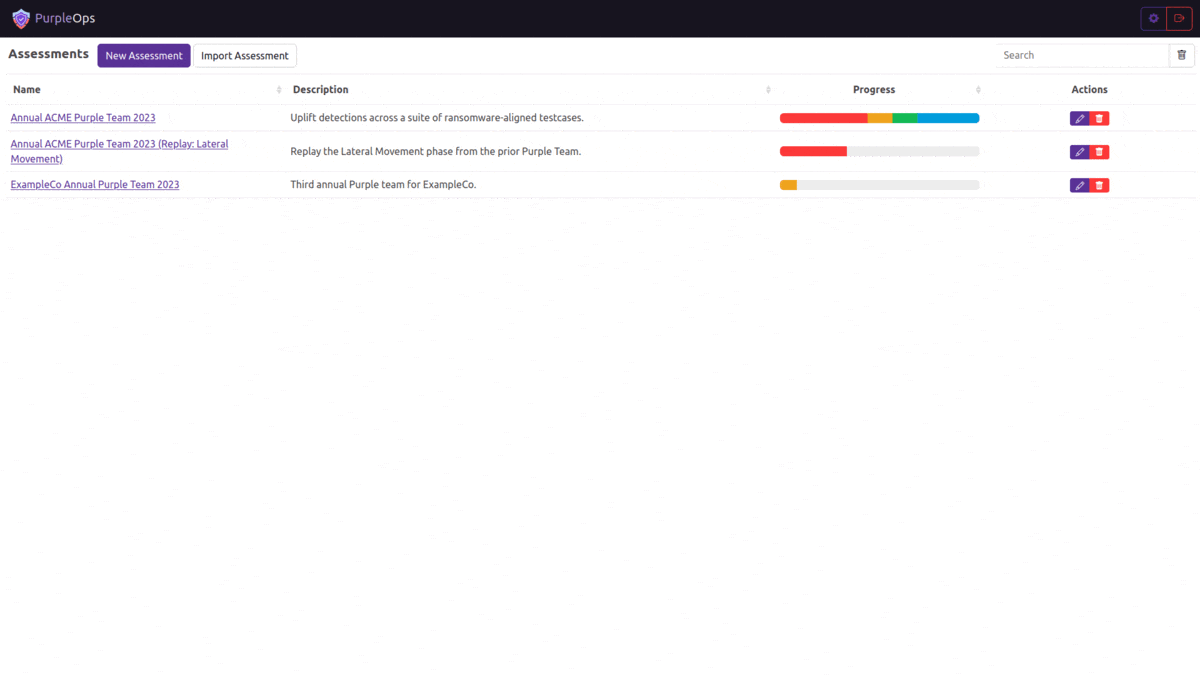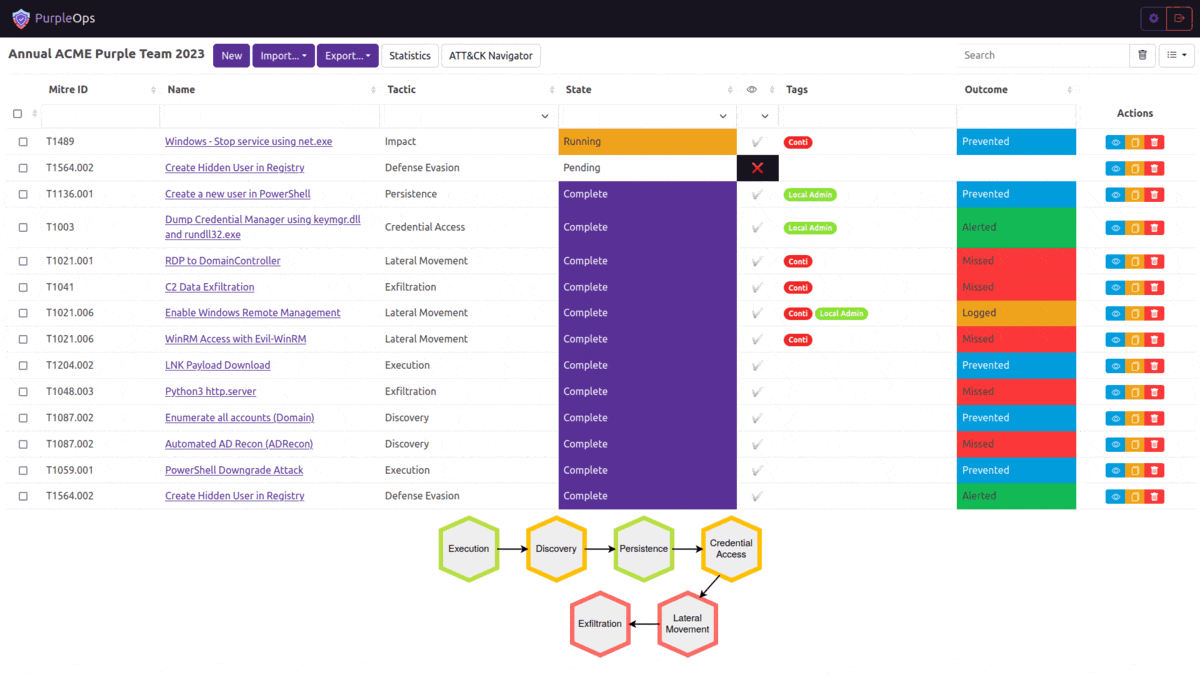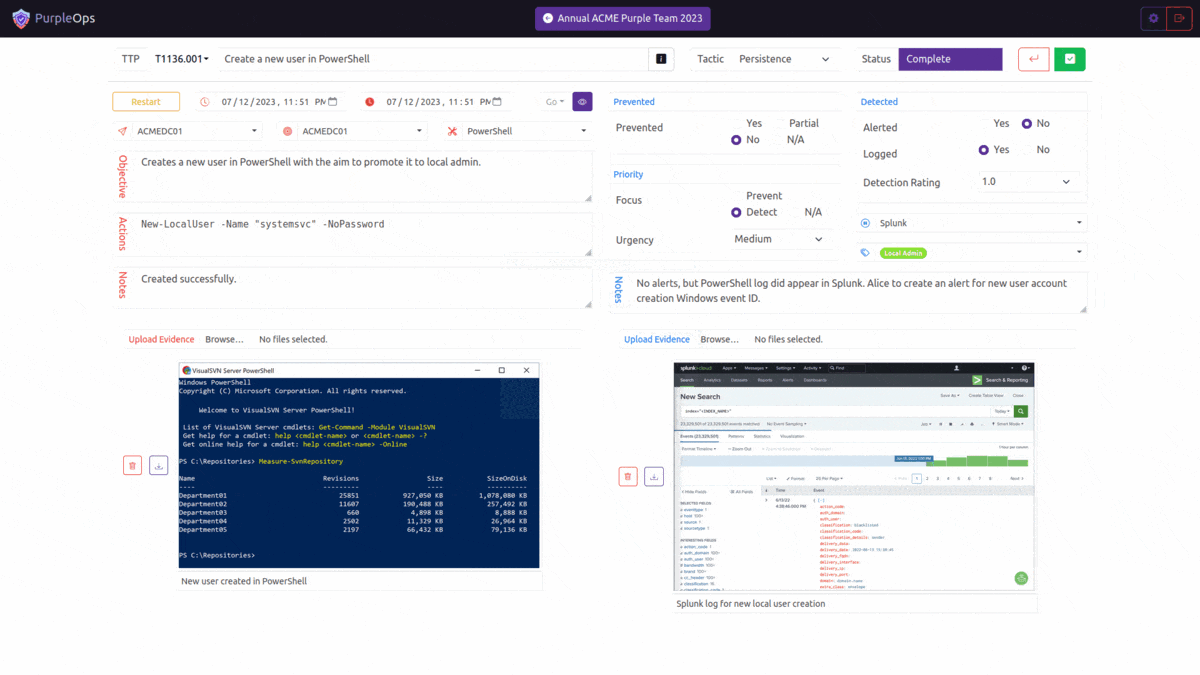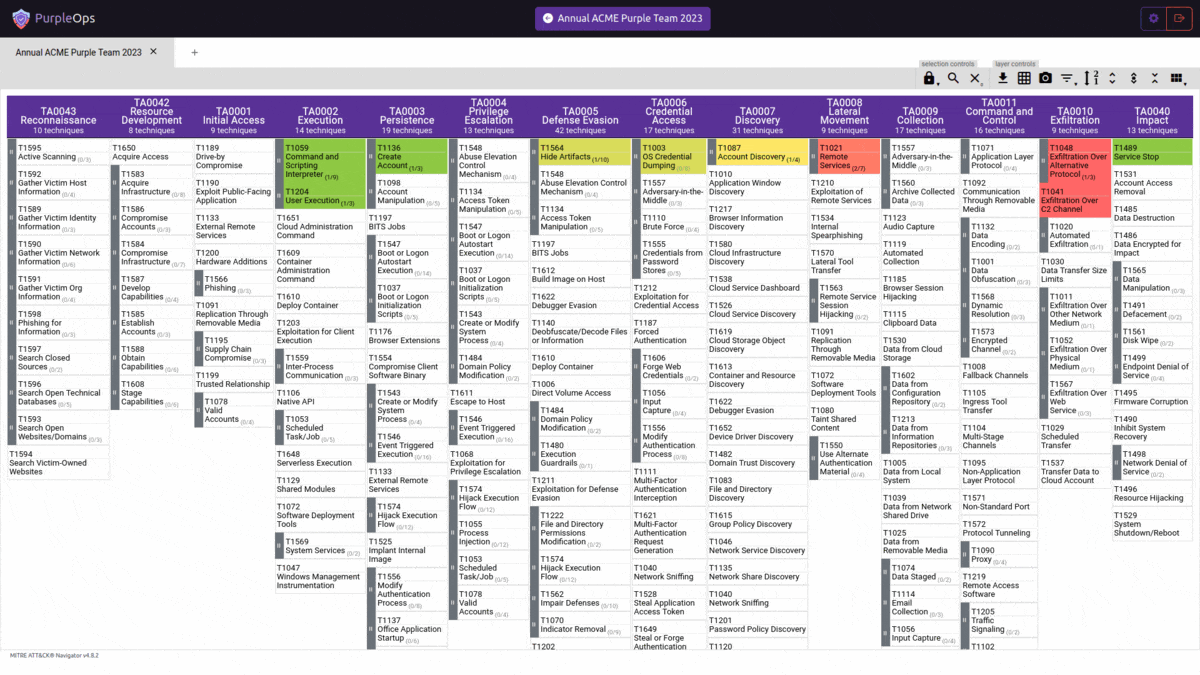 cybercx-sta/purpleops
An open-source self-hosted purple team management web application.