Alternative-Approach-Reverse-Shell-Callback-Test-InvokeAI-RCE

This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…

This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…

Erlang/OTP SSH Vulnerable to Pre-Authentication RCE

HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…

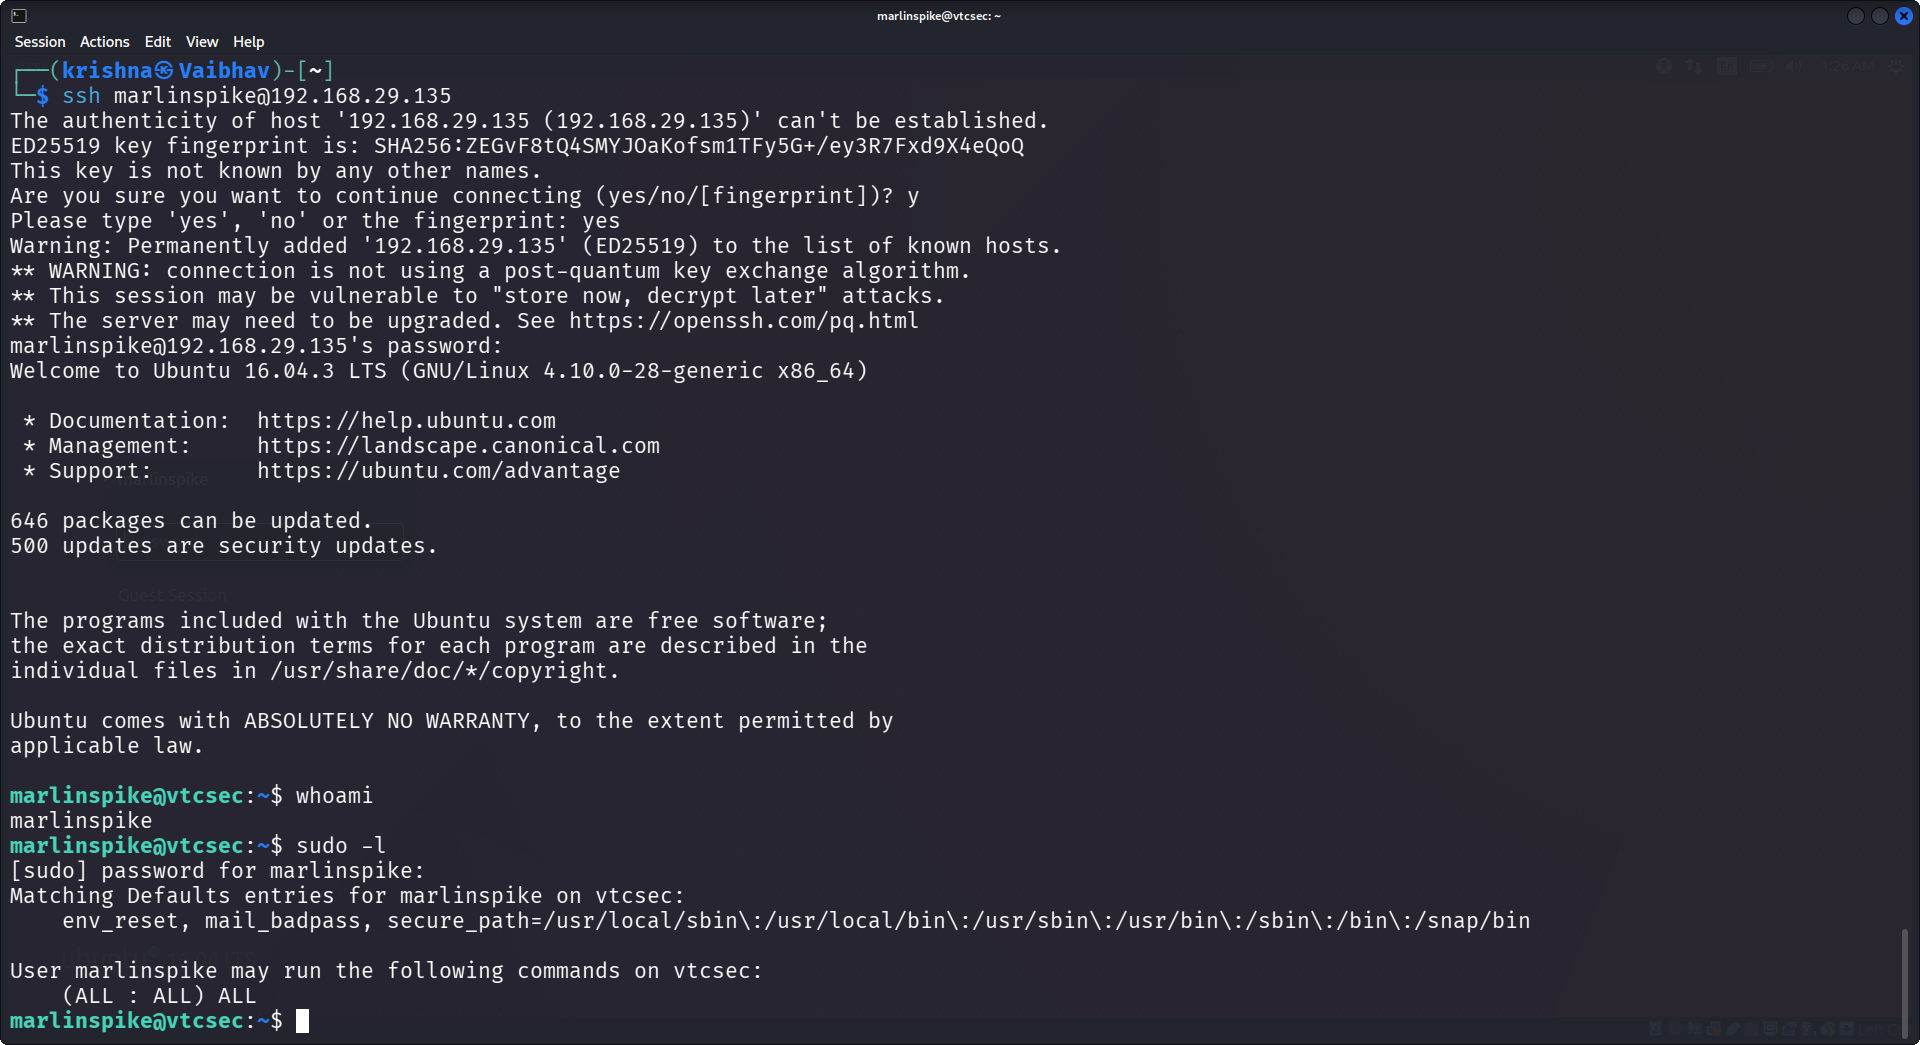
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)

HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.

Investigation into the XZ Utils backdoor (CVE-2024-3094): chronology, attack chain, risk to SSH, and supply-chain insights. Includes slides, sources,…

Proof-of-concept exploit for CVE-2017-1000117 (Git SSH command injection) that writes command output to a web-accessible file. Part of VulApps…

SSH username enumeration exploit targeting OpenSSH 2.3 through 7.7 (CVE-2018-15473). Enumerates valid users individually or from a wordlist via a…

Go-based exploit for CVE-2024-22274 that creates a new user via SSH and provides a root shell on the target machine for authorized penetration…

Check if a username is valid on the SSH server by attempting an authentication. The server response will indicate whether the username exists.

A compact guide to network pivoting for penetration testings / CTF challenges.

Patch-diff research for published urllib3 issues: pinned releases, original offline harnesses, before/after behavior and benign controls.

自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究

Proof-of-concept exploit for CVE-2024-6387 targeting vulnerable OpenSSH servers via heap manipulation and race condition to achieve remote code…

CVE-2017-1000117漏洞复现(PoC+Exp)

Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping

This script implements a lab automation where I exploit CVE-2021-43798 to steal user secrets and then gain privileges on a Linux system.