
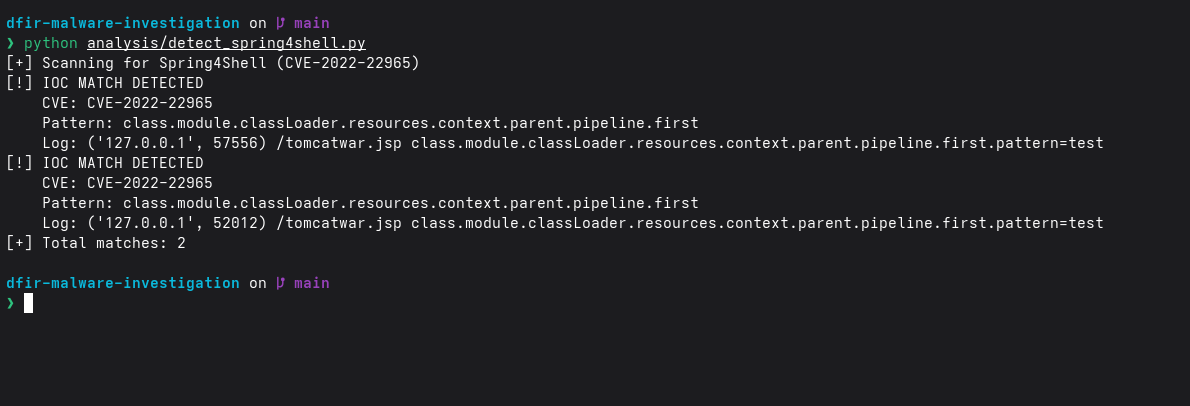
dfir-malware-investigation
 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
digital-forensicseducationincident-response+9
suyash-r-k/dfir-malware-investigationSpring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 lemonadern/poc-cve-2019-14287
Docker-based PoC demonstrating CVE-2019-14287 sudo privilege escalation via Runas user restriction bypass, with step-by-step reproduction…
 magpieryl/cve-2024-3094-backdoor-env-container
This is a container environment running CVE-2024-3094 sshd backdoor instance, working with https://github.com/amlweems/xzbot project. IT IS NOT…
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
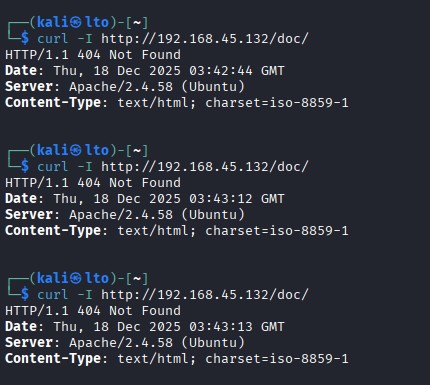 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 matanelgordon/docker-cve-2021-41773
A little demonstration of cve-2021-41773 on httpd docker containers
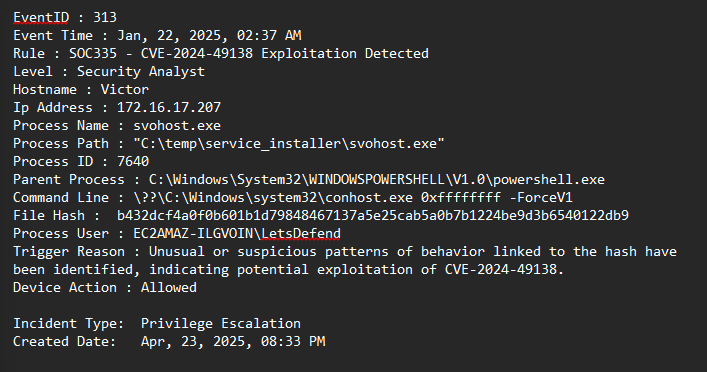 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
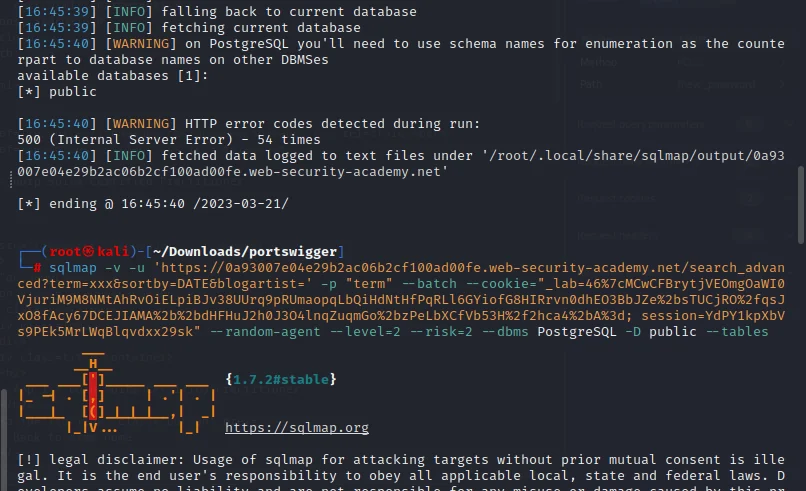 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 tiger-foxx/exploit-react-cve-2025-55182
This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…
 0xnslabs/cve-2024-25832-poc
PoC Script for CVE-2024-25832: Exploit chain reverse shell, information disclosure (root password leak) + unrestricted file upload in DataCube3
 astaruf/cve-2026-44590
Proof-of-concept exploit for CVE-2026-44590, a command injection in Sherlock's GitHub Actions workflow enabling RCE and GITHUB_TOKEN exfiltration via…
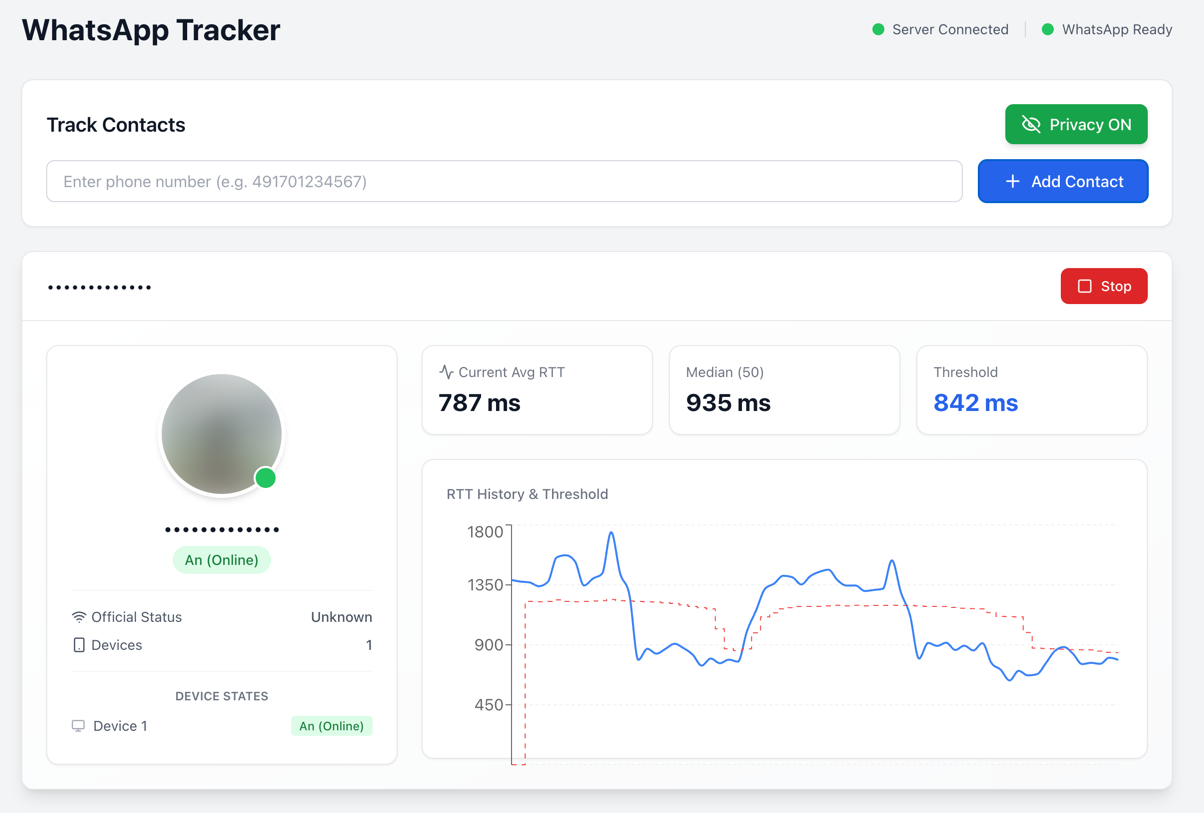 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
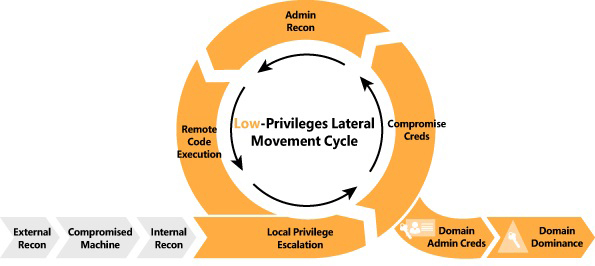 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 bardlaudian/cve-2023-23752
Python port of the CVE-2023-23752 exploit — Joomla! < 4.2.8 unauthenticated information disclosure (user list + DB credentials leak)