
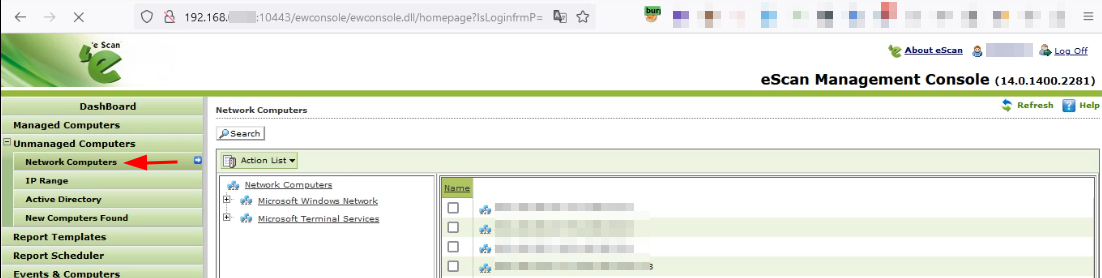
CVE-2023-34837
 sahiloj/cve-2023-34837
CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
educationpapers-researchpenetration-testing+2
sahiloj/cve-2023-34837CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
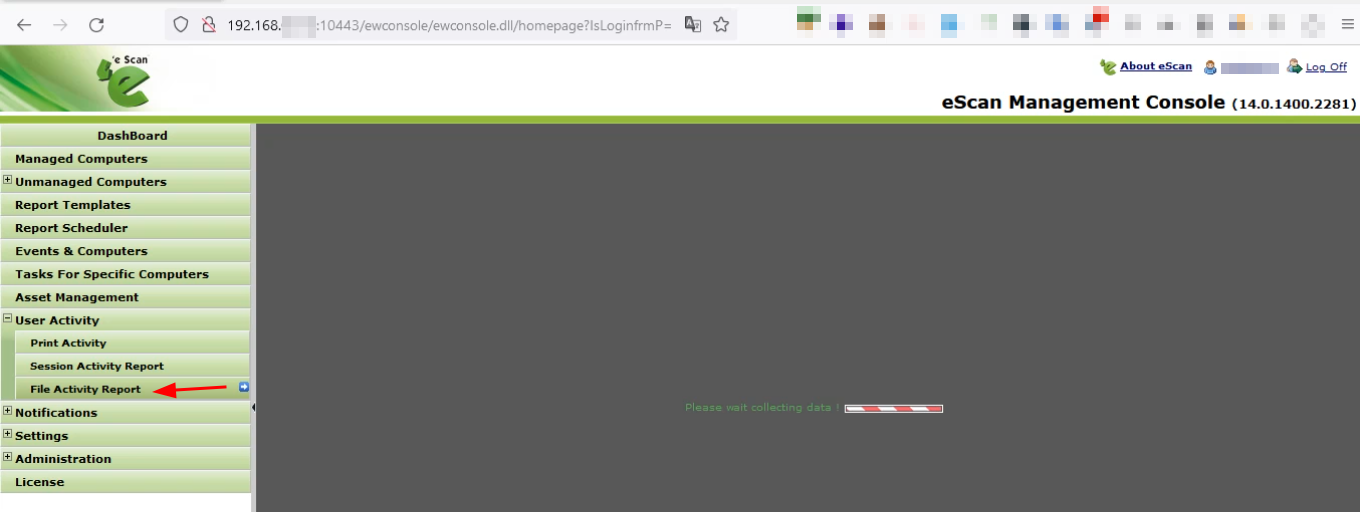 sahiloj/cve-2023-34836
A Reflected Cross-Site Scripting (XSS) vulnerability exists in Microworld Technologies eScan Management Console v14.0.1400.2281. The vulnerable…
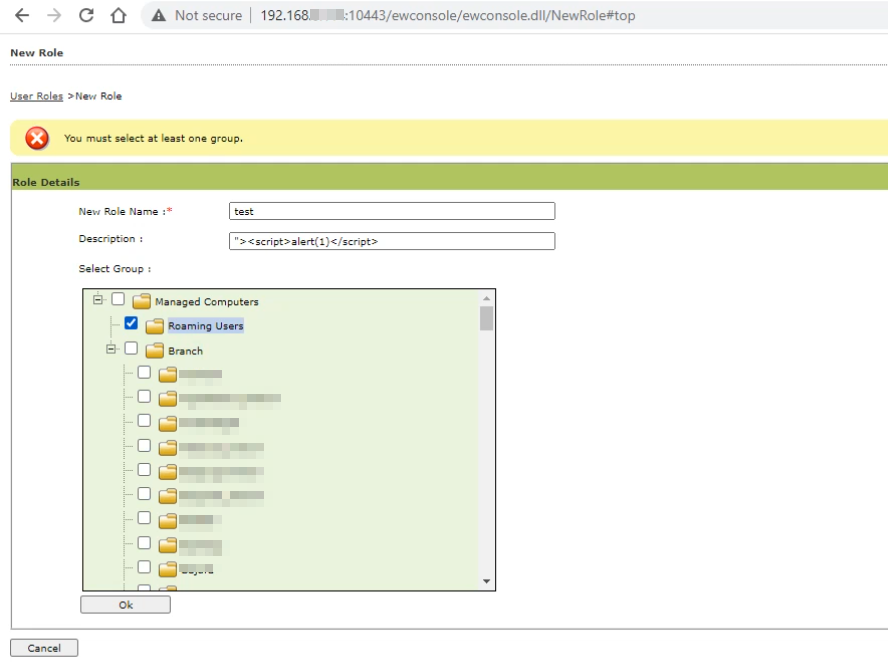 sahiloj/cve-2023-34838
Microworld Technologies eScan Management Console version 14.0.1400.2281 is vulnerable to a Stored Cross-Site Scripting (XSS) attack.
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
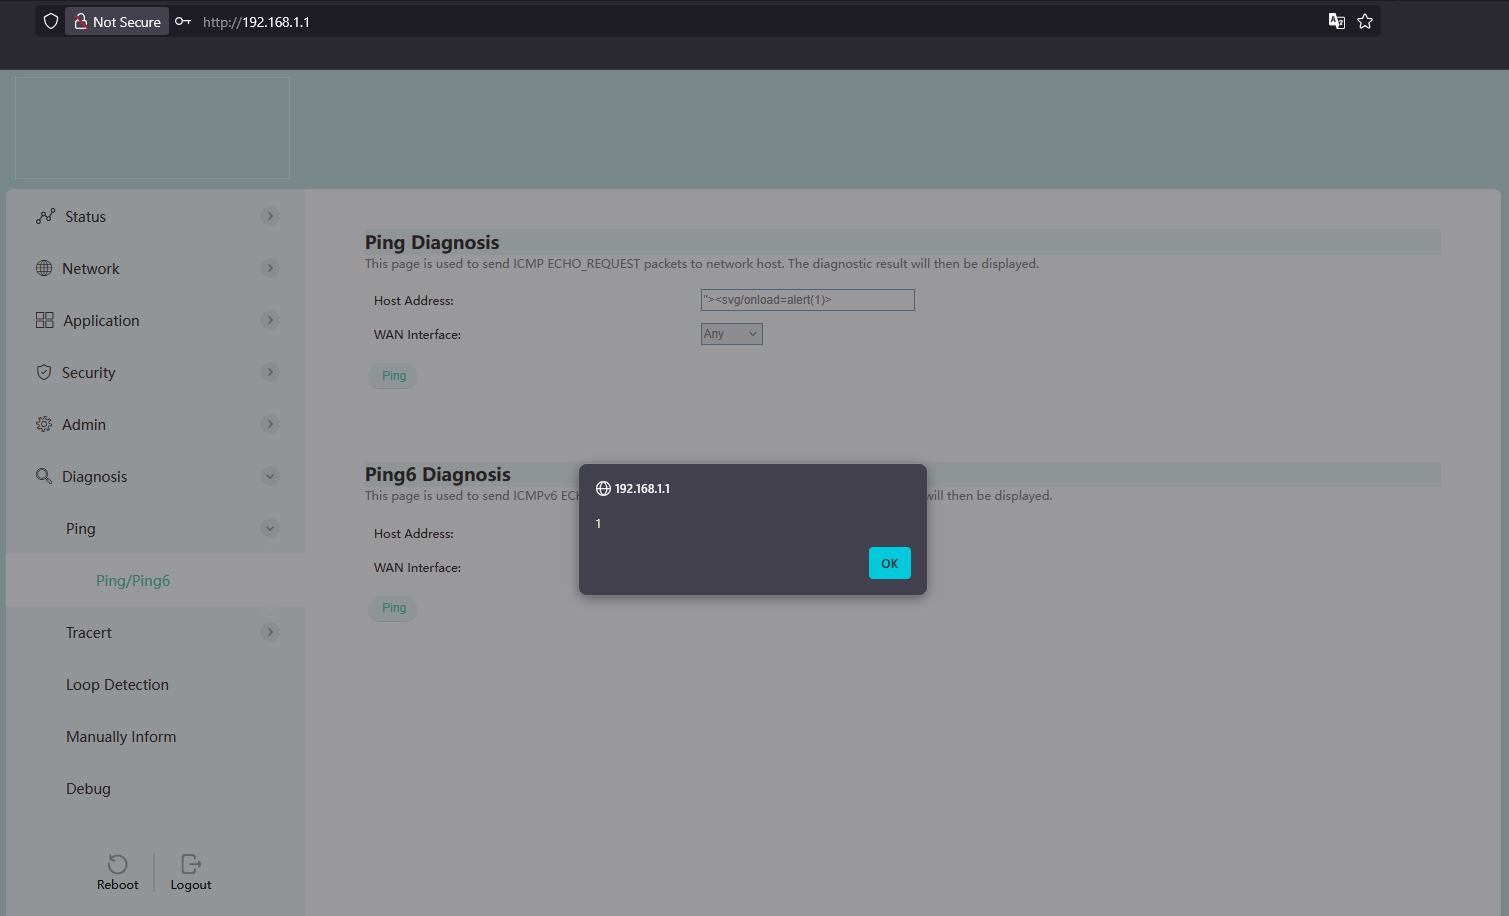 wrathfuldiety/cve-2025-52357
Proof of Concept and Security Advisory for XSS vulnerability in the FD602GW-DX-R410 fiber router’s admin console (firmware V2.2.14). Includes…
 h3lye/cve-2024-42448-rce
Veeam Service Provider Console (VSPC) remote code execution.
 asepsaepdin/cve-2023-32315
Python exploit for CVE-2023-32315, a path traversal in Openfire's admin console, allowing unauthenticated access to restricted pages. Includes Docker…
 idan5x/switcheroo
Exploiting CVE-2016-4657 to JailBreak the Nintendo Switch
 al1ex/cve-2021-2109
CVE-2021-2109 && Weblogic Server RCE via JNDI
 a0zhar/bad_hoist-writeup
A Writeup for Sleirsgoevy's version of the Exploit Implementation of CVE-2018-4386 by Fire30 called Bad_Hoist
 lucaspdiniz/cve-2020-14882
Takeover of Oracle WebLogic Server
 specializzazione-cyber-security/demo-cve-2021-29447-lezione
Proof-of-concept exploit for CVE-2021-29447, an authenticated XXE vulnerability in WordPress 5.6-5.7. Includes lab setup, malicious WAV generation,…