
TCASVS
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
code-analysisconfiguration-auditingcryptography+5
owasp/tcasvsOWASP Thick Client Application Security Verification Standard
 owasp/odtm
OWASP Ontology-driven Threat Modelling framework
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)
 thetorjancaptain/cve-2025-33053-checker-poc
CVE-2025-33053 Checker and PoC
 rsalmond/cve-2021-34824
reproducing an old istio bug
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 syntaxbearror/powershell-printnightmare
A collection of scripts to help set the appropriate registry keys for CVE-2021-34527
 grantzile/poc-cve-2024-33883
PoC of CVE-2024-33883, RCE vulnerability of ejs.
 localh0ste/cve-2025-4138
Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation
 lixterclarixe/cve-2020-11019
In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…
 huyvo2910/cve-2025-25749-weak-password-policy-in-hoteldruid-3.0.7
Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…
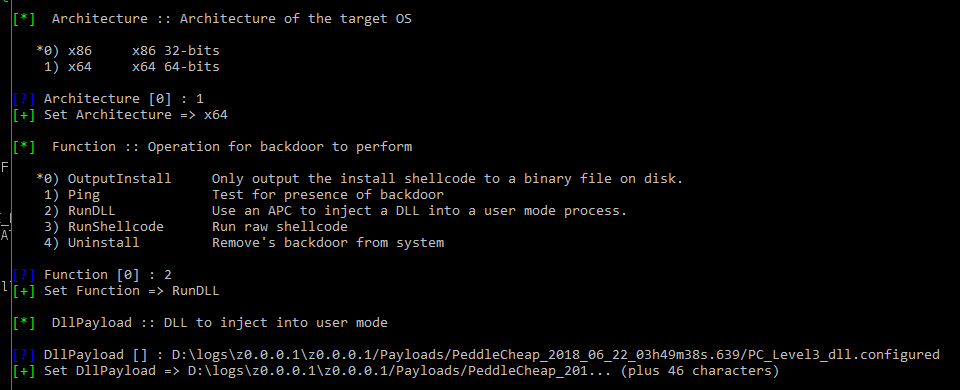 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 aashay221999/cve-2024-49368
Explorations of CVE-2024-49368 + Exploit Development