

CVE-2020-11019
 lixterclarixe/cve-2020-11019
In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…
curated-resourceseducationinformation-gathering+2
lixterclarixe/cve-2020-11019In FreeRDP less than or equal to 2.0.0, when running with logger set to "WLOG_TRACE", a possible crash of application could occur due to a read of an…
 lorenzodegiorgi/setup-cve-2015-8562
Docker-compose to set up a test environment for exploiting CVE-2015-8562
 syntaxbearror/powershell-printnightmare
A collection of scripts to help set the appropriate registry keys for CVE-2021-34527
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
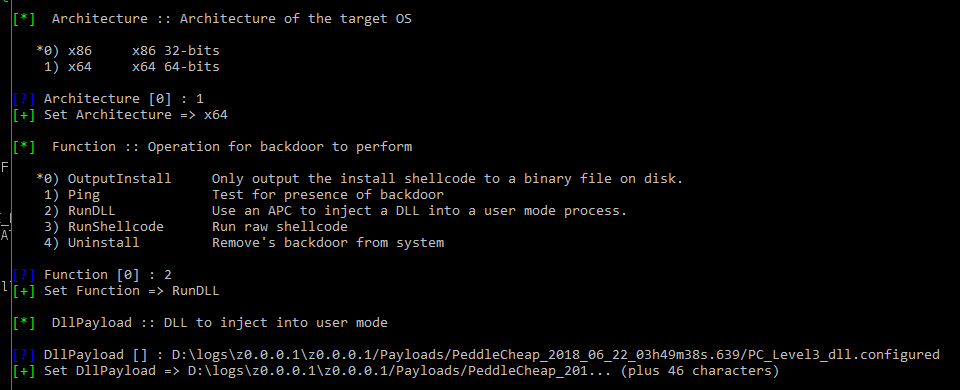 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)

 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 huntandhackett/concealed_code_execution
Tools and technical write-ups describing attacking techniques that rely on concealing code execution on Windows