
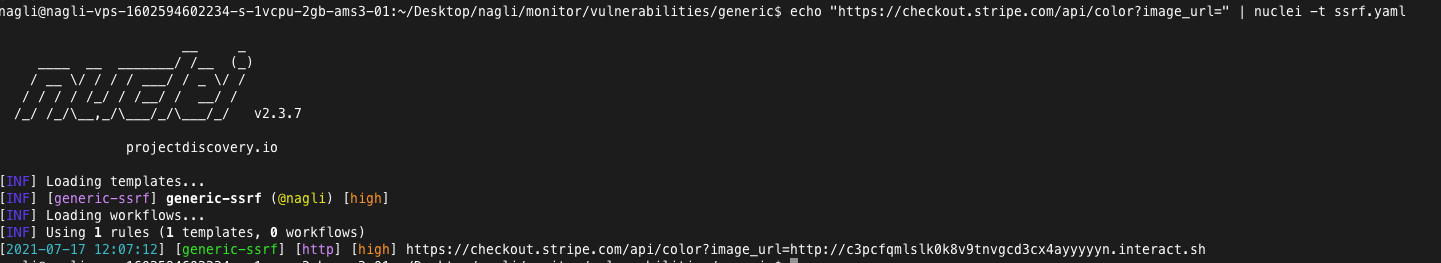
Shockwave-OSS
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
curated-resourceseducationfuzzing+9
750
gal-nagli/shockwave-ossCurated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 itres-labs/cve-2023-3350
Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]
 fofainfo/awesome-fofa
The FOFA Library collects usage tips, common scenarios, F&Q, and more for FOFA.
 nasroabd/zynos-attacker
ZynOS tool for automated attack on a range of IPs, find more informations at :
 ak-cybe/cve-2025-68613-n8n-rce-analysis
CVE-2025-68613 (n8n) Critical RCE analysis + defensive recommendations (patch validation, detection ideas, and hardening tips)
 jminis/cve-2023-50257
This repository is for research purposes (2025 Sejong Univ. Capstone Design)
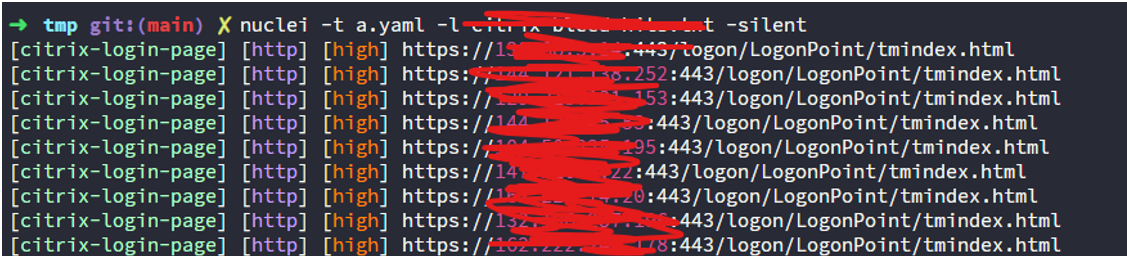 soltanali0/cve-2025-5777-exploit
Async-based exploit tool for CVE-2025-5777 that detects and extracts leaked authentication tokens, internal IPs, and hidden endpoint paths from…
 beraphin/cve-2017-16943
Technical analysis and proof-of-concept for CVE-2017-16943, a use-after-free in Exim's receive_msg function, demonstrating heap manipulation and RIP…
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
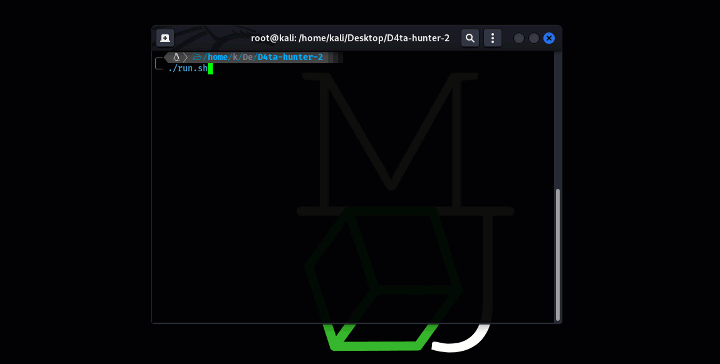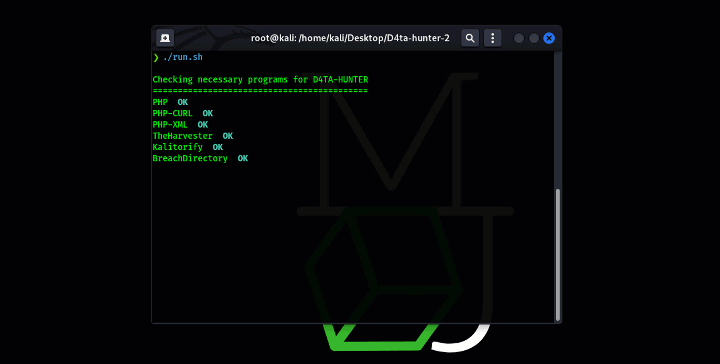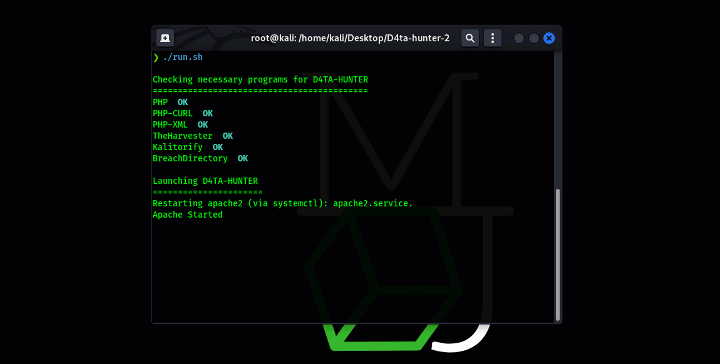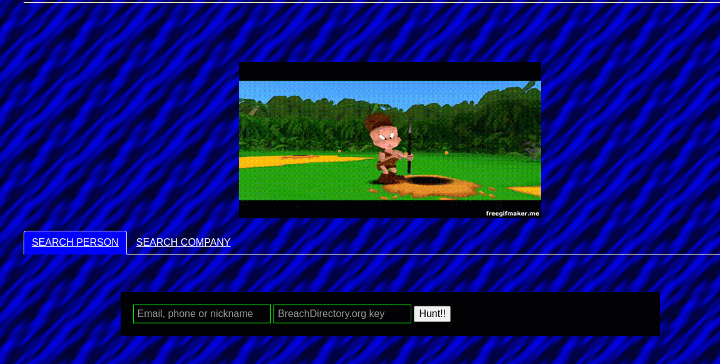 micro-joan/d4ta-hunter
Automated OSINT framework for ethical hacking audits. Collects employee emails, password hashes, subdomains, and IPs via BreachDirectory and…
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
 100daysofyara/2022
Daily YARA rule challenge and community collection where malware analysts share detection patterns, tips, and unconventional YARA uses to advance…
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 ternopil-te-te-t4p/cryptoquant-key-gen
Patcher utility that bypasses CryptoQuant premium tier restrictions to unlock advanced analytics and real-time data access, with a Python GUI for…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…