
CVE-2017-18349
 dungsocool/cve-2017-18349
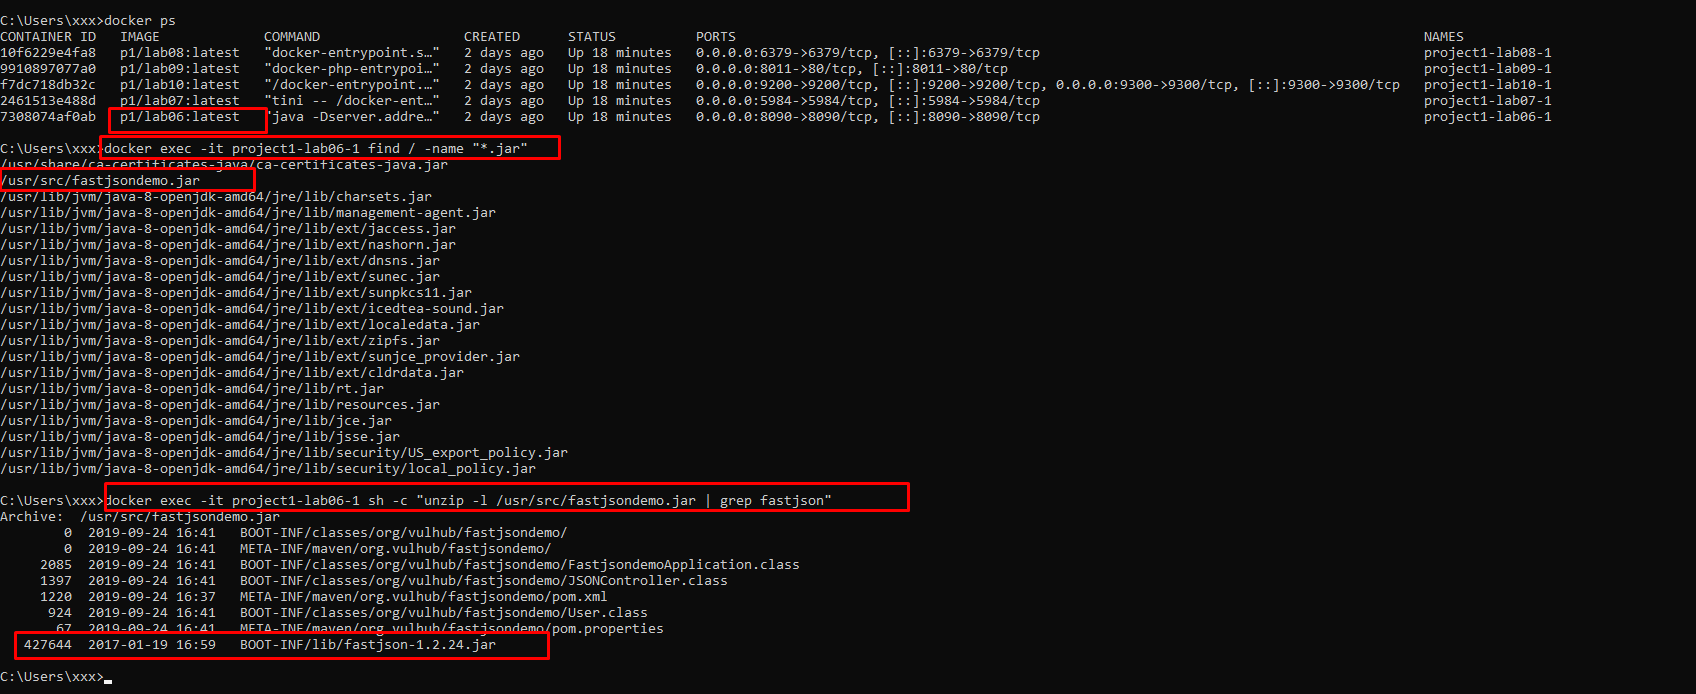
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
binary-exploitationeducationexploitation+6
dungsocool/cve-2017-18349Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
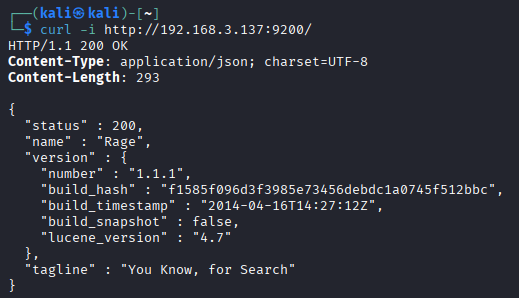 dungsocool/cve-2014-3120
Step-by-step lab guide demonstrating CVE-2014-3120 exploitation against Elasticsearch 1.1.1, covering vulnerability analysis, RCE via MVEL scripting,…
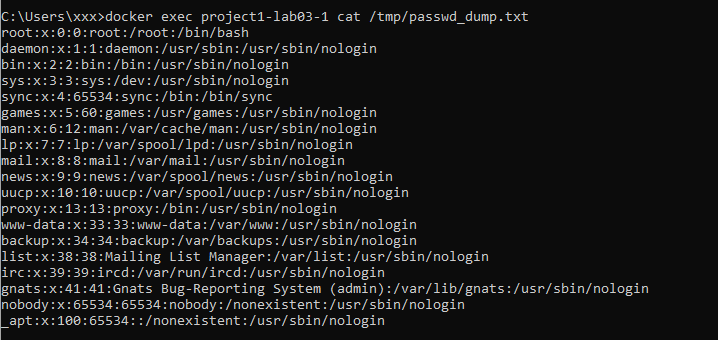 dungsocool/cve-2017-11610
Step-by-step exploit writeup for CVE-2017-11610 (Supervisord XML-RPC RCE) with attack surface analysis, namespace traversal discovery, and…
 cved-sources/cve-2018-15961
Docker container for CVE-2018-15961, part of the Cved framework for managing and testing vulnerable Docker environments in security labs.
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
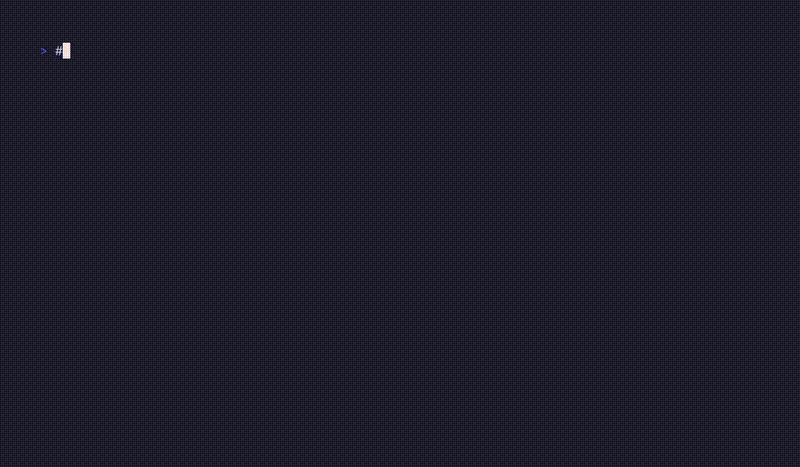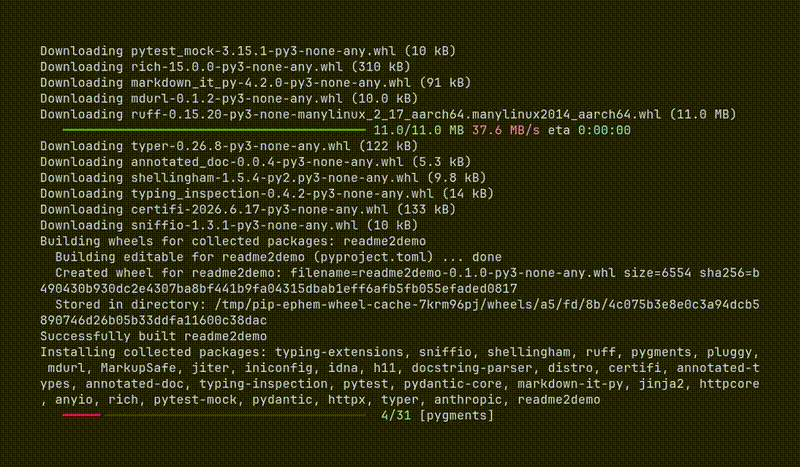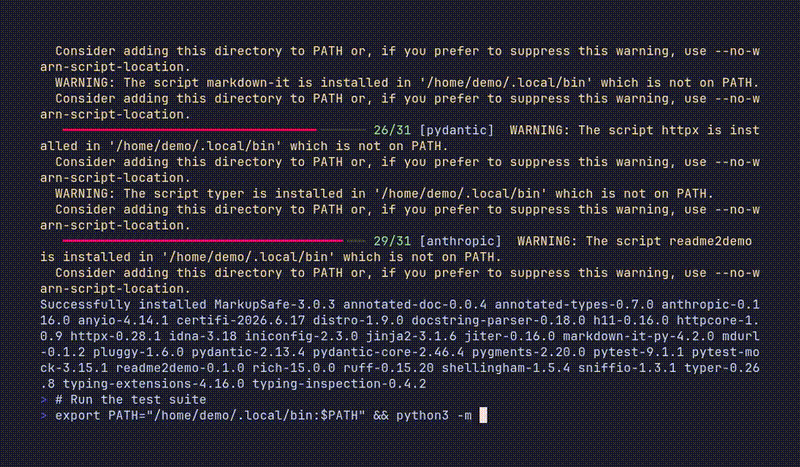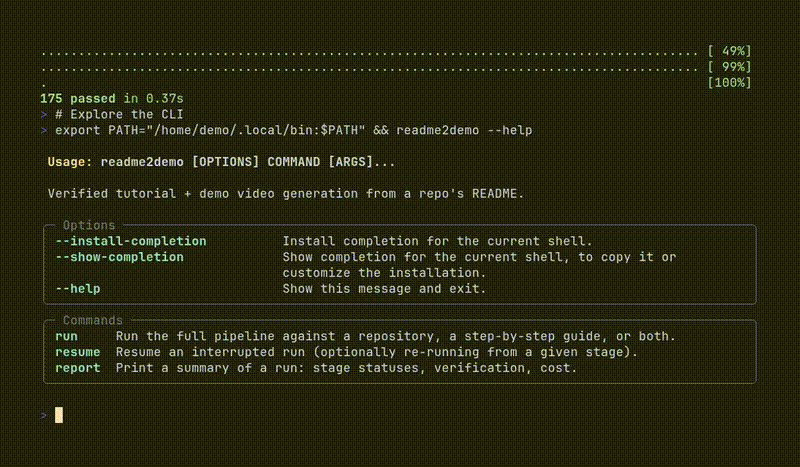 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 pedrorichil/cve-2025-49844
Educational lab environment demonstrating CVE-2025-49844 (RediShell) in Redis. Includes Docker setup, exploit PoC script, and security…
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…
 sidjaz/crushftp-cve-2024-4040-proof-of-concept
Proof-of-concept exploit for CVE-2024-4040, demonstrating unauthenticated SSTI and local file read in CrushFTP, with Docker lab and mitigation…
 ahmad.zaid/netsecdss
Decision Support System for Risk Assessing Network and System Security in Small and Medium Enterprises (SMEs), A graduation project.
 dinosn/givewp-cve-2026-82222-rce-lab
Authorized Docker lab and clean PoC for validating CVE-2026-82222 RCE in GiveWP 4.16.5.1 and the 4.16.7.2 fix.
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
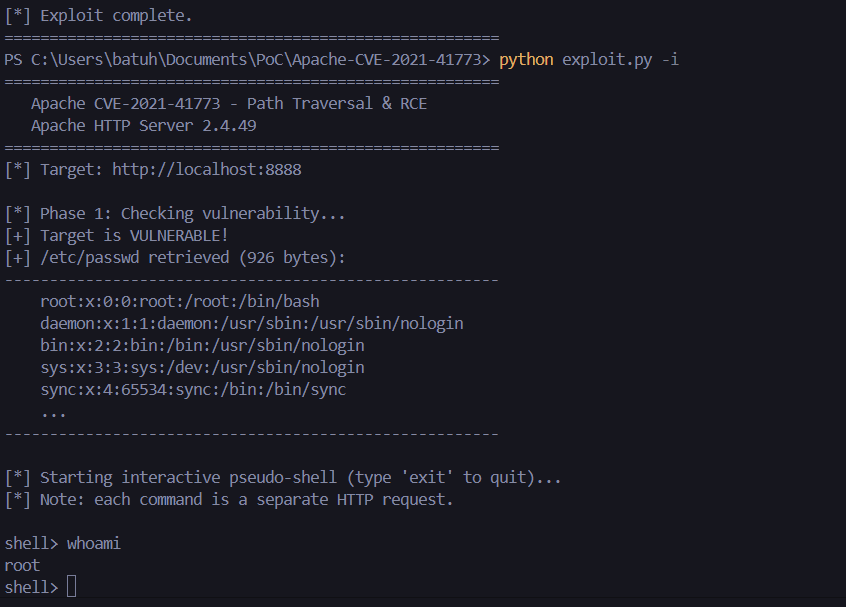 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 abds059/apache-path-traversal-rce-cve-2021-41773-
A comprehensive analysis of CVE-2021-41773 (Apache HTTP Server 2.4.49), featuring vulnerability research, controlled lab-based exploitation,…
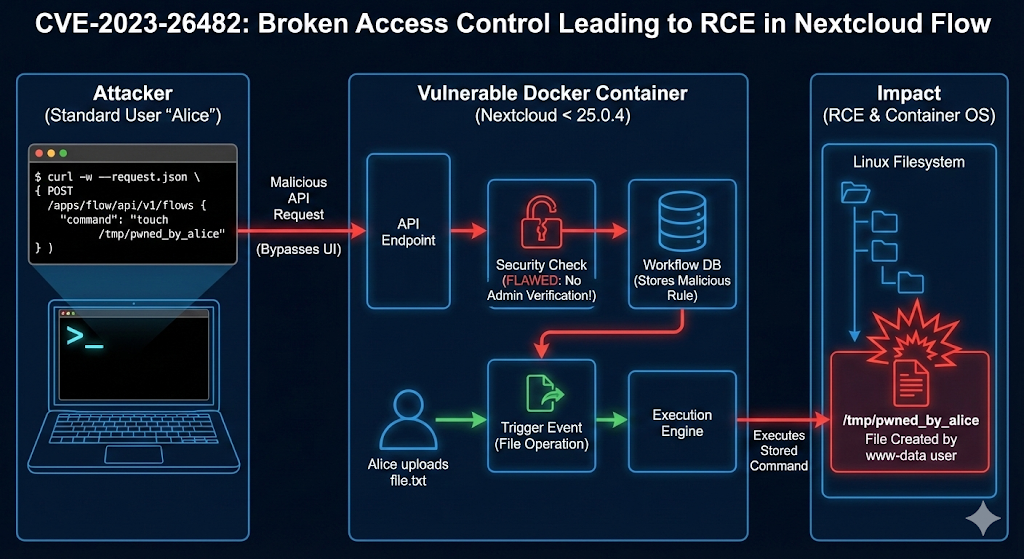 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…