Cusimanse
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
ai-securitydefensive-toolsdynamic-analysis-sandboxing+9
opposum0112/cusimanseComposable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 roshanrajbanshi/rocketcat-cve-2021-22911-exploit
CVE-2021-22911 Rocket.Chat NoSQL Injection RCE Exploit - Educational Purpose
 lucksi/mr.holmes
Modular OSINT framework for gathering intelligence on domains, usernames, phone numbers, and emails using public sources, Google dorks, and…
 furkankayapinar/cve-2025-14847-mongobleed-exploit
CVE-2025-14847 MongoBleed - MongoDB Memory Leak Vulnerability PoC
 thieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm
Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 adel2411/cve-2023-38408
An in-depth analysis of CVE 2023 38408, a critical OpenSSH vulnerability, including technical background, exploitation in controlled environments,…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 malvads/sqlmc
Official Kali Linux tool to check all urls of a domain for SQL injections :)
 hsw109/cve-2018-10933
Education purpose for CVE-2018-10933
 0dteam/cve-2024-22024
Check for CVE-2024-22024 vulnerability in Ivanti Connect Secure
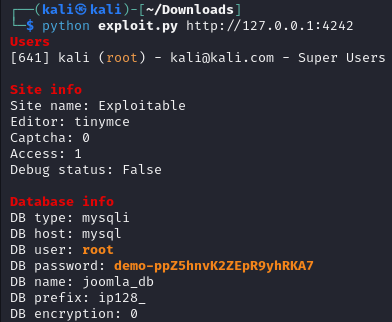 fernando-olv/joomla-cve-2023-23752
This Python implementation serves an educational purpose by demonstrating the exploitation of CVE-2023-23752. The code provides insight into the…
 stealyourcode/cve-2019-1663
Docs on the Vulnerability CVE-2019-1663 (Cisco Routers)
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 efchatz/quic-attacks
Educational scripts demonstrating QUIC protocol attacks including CVE-2022-30591 exploitation, flooding, and slowloris techniques against major…