

mastg
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
android-securitycryptographydynamic-analysis-sandboxing+9
13.1k
owasp/mastgComprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 owasp/securityshepherd
Web and mobile application security training platform
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 horkimhab/cve-2025-64702-more
Proof-of-concept code and research notes for QPACK/HTTP-3 vulnerabilities (CVE-2025-64702, CVE-2026-12523, CVE-2025-13945) for authorized lab testing.
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 ashishb/android-security-awesome
A collection of android security related resources
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 horkimhab/cve-2026-59265
Proof-of-concept and research material for CVE-2026-59265, a LibreOffice and OpenOffice vulnerability, intended for authorized lab testing and…
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
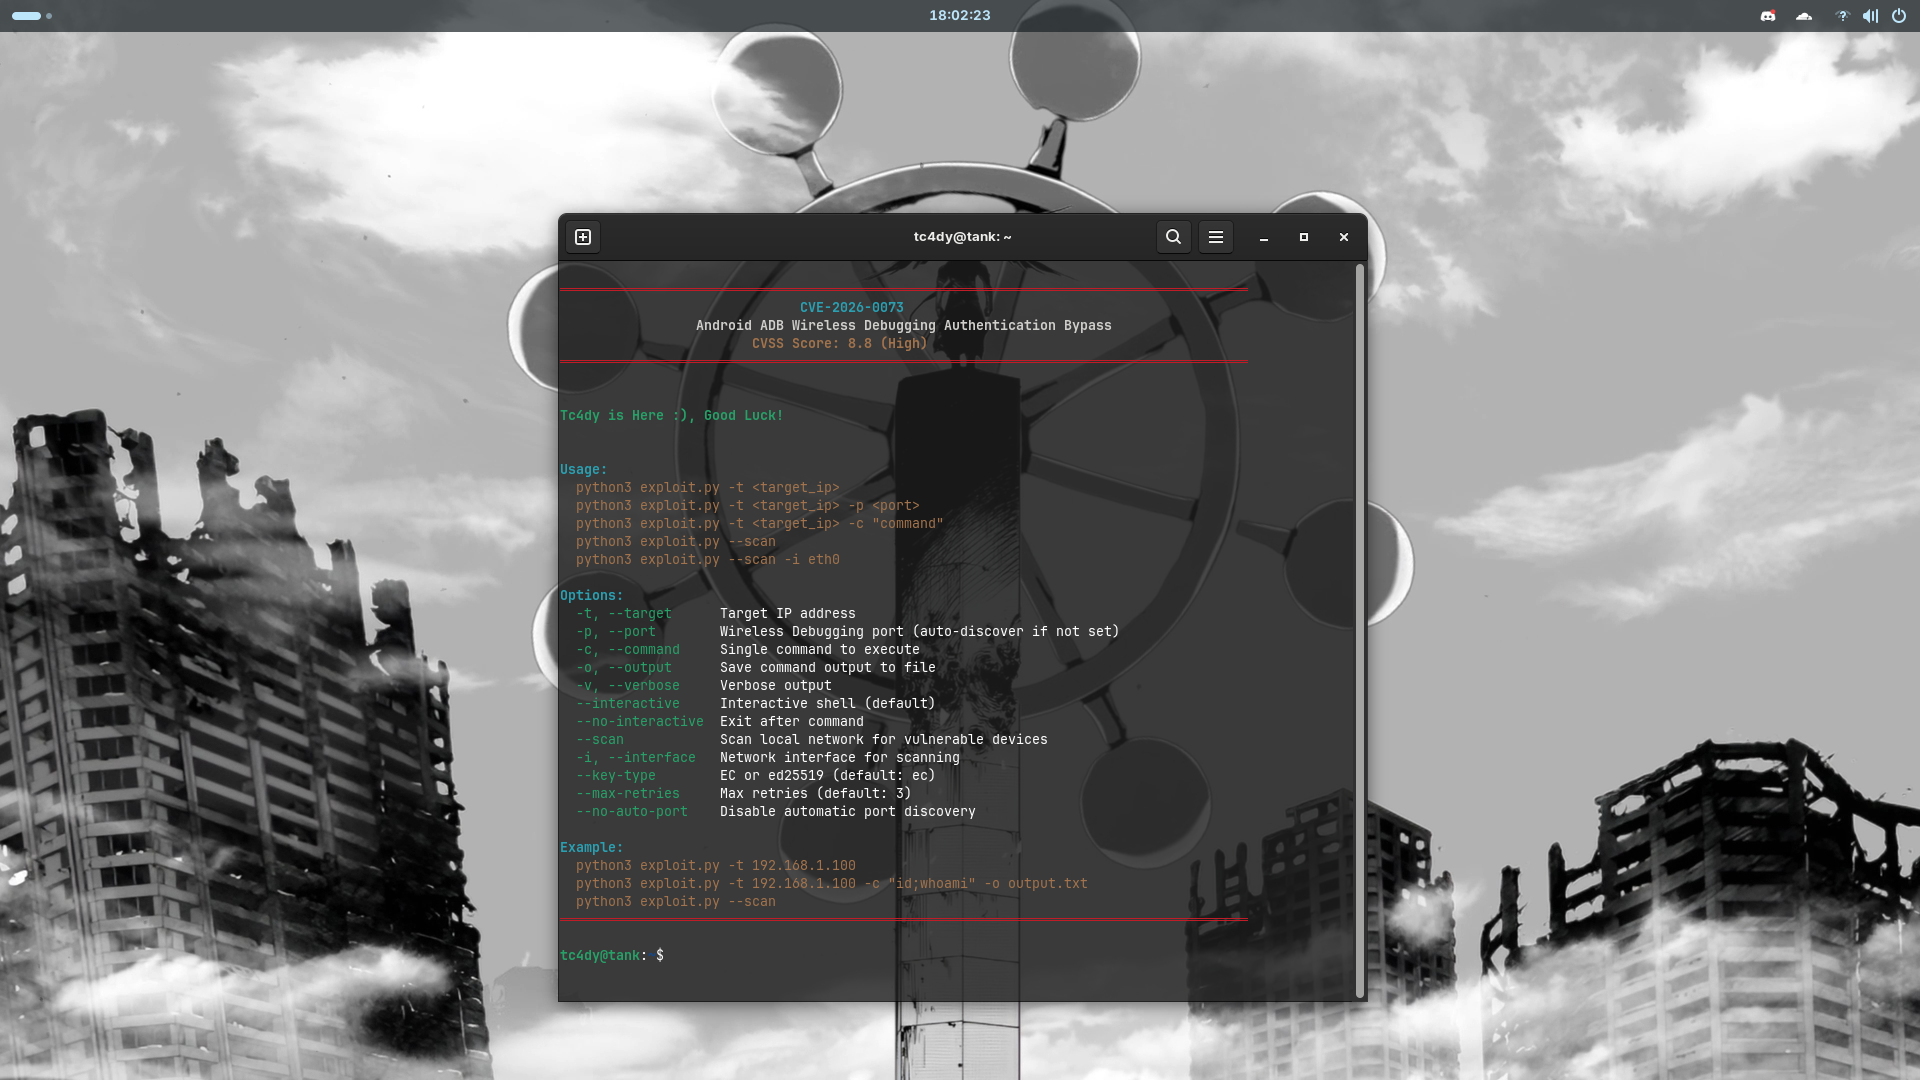 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
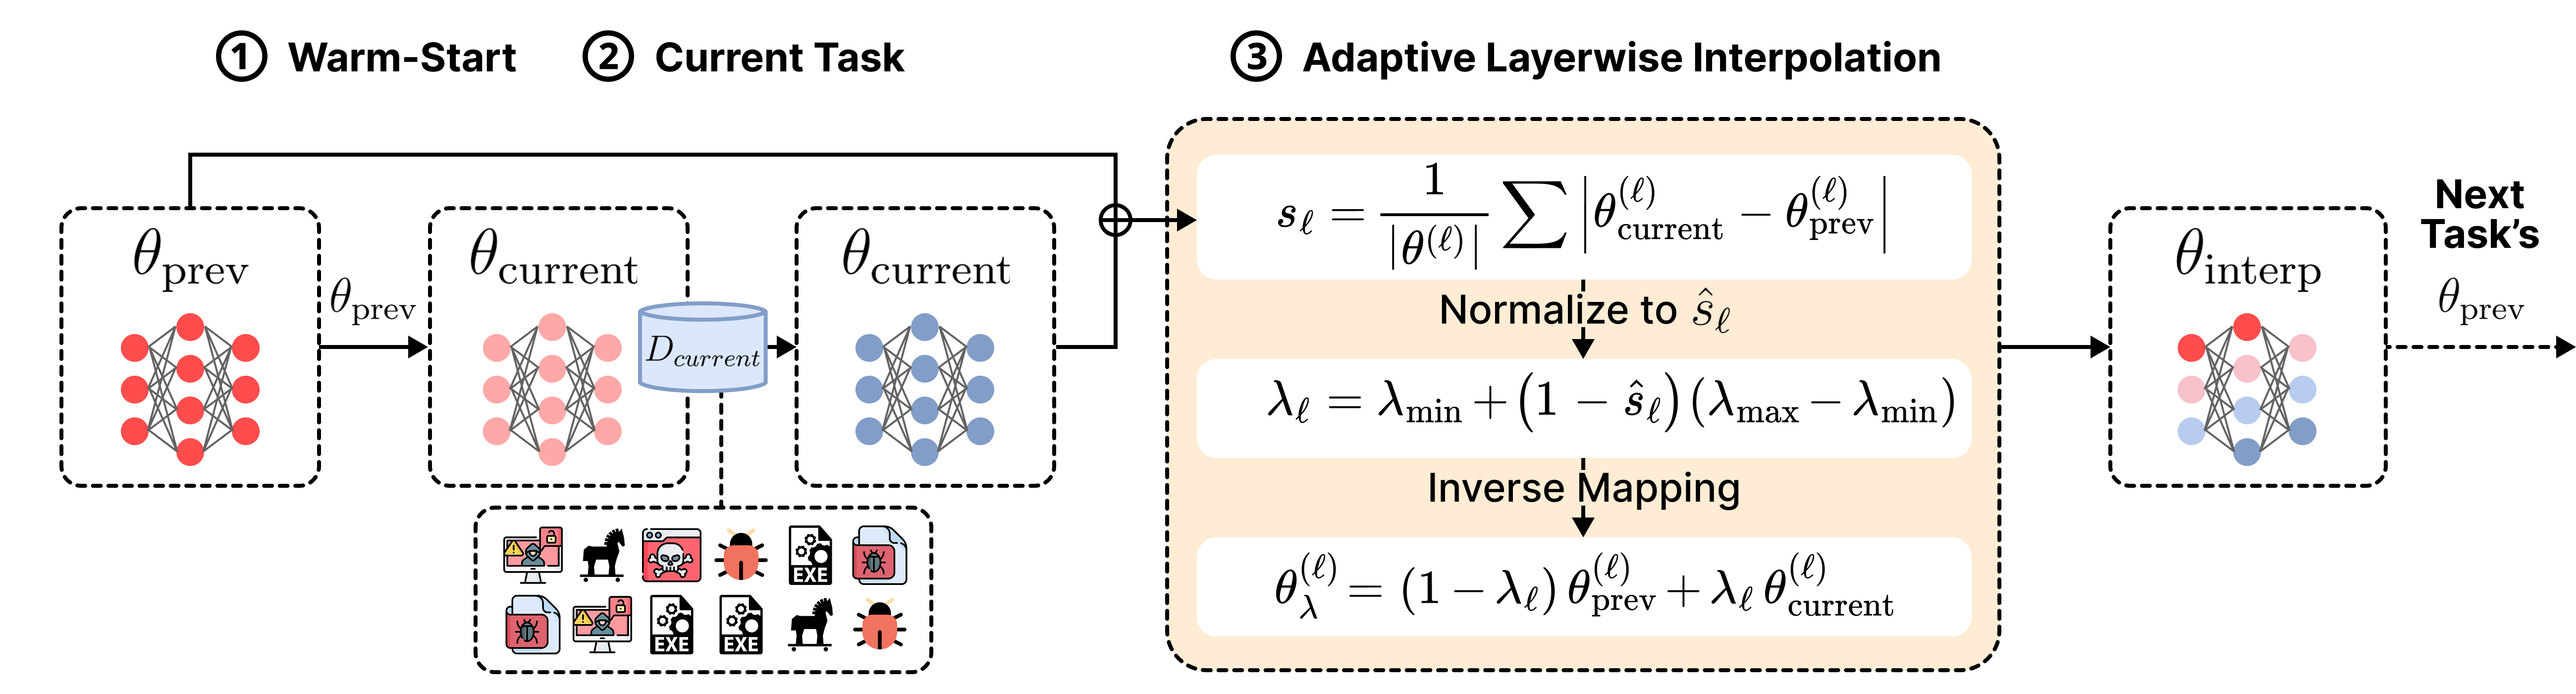 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10