
Azure-Sentinel
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
cloud-securitycurated-resourcesdefensive-tools+5
6.2k
azure/azure-sentinelCloud-native SIEM for intelligent security analytics for your entire enterprise.
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
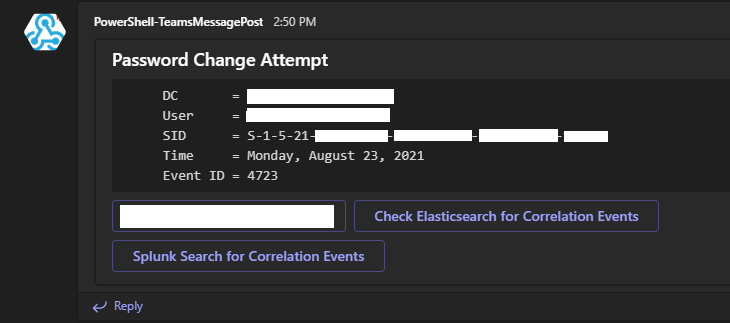 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.
 microsoft/security-101
8 Lessons, Kick-start Your Cybersecurity Learning.
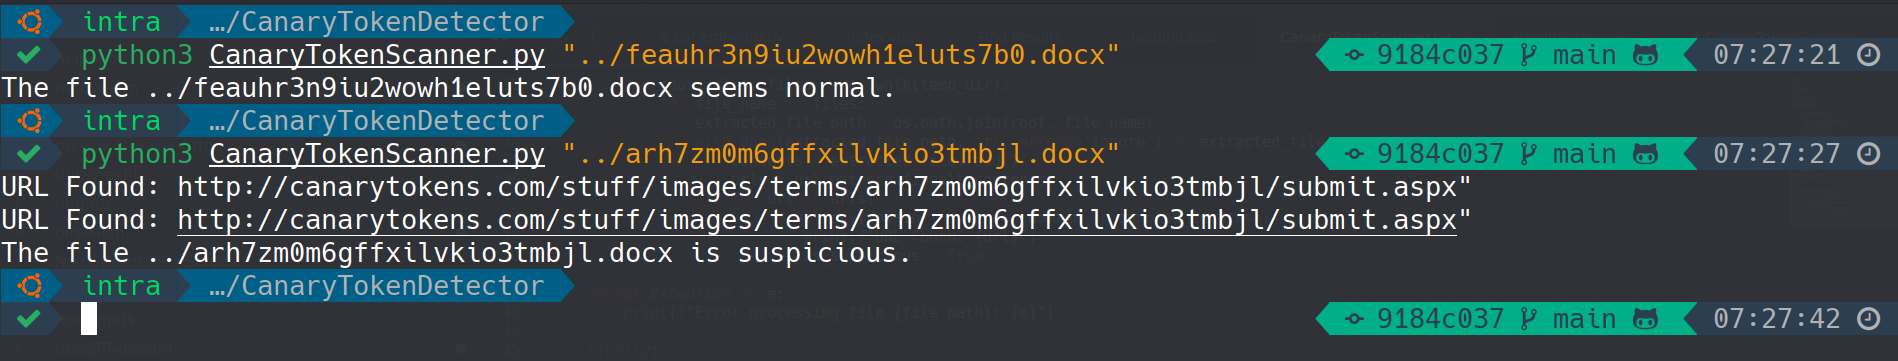 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
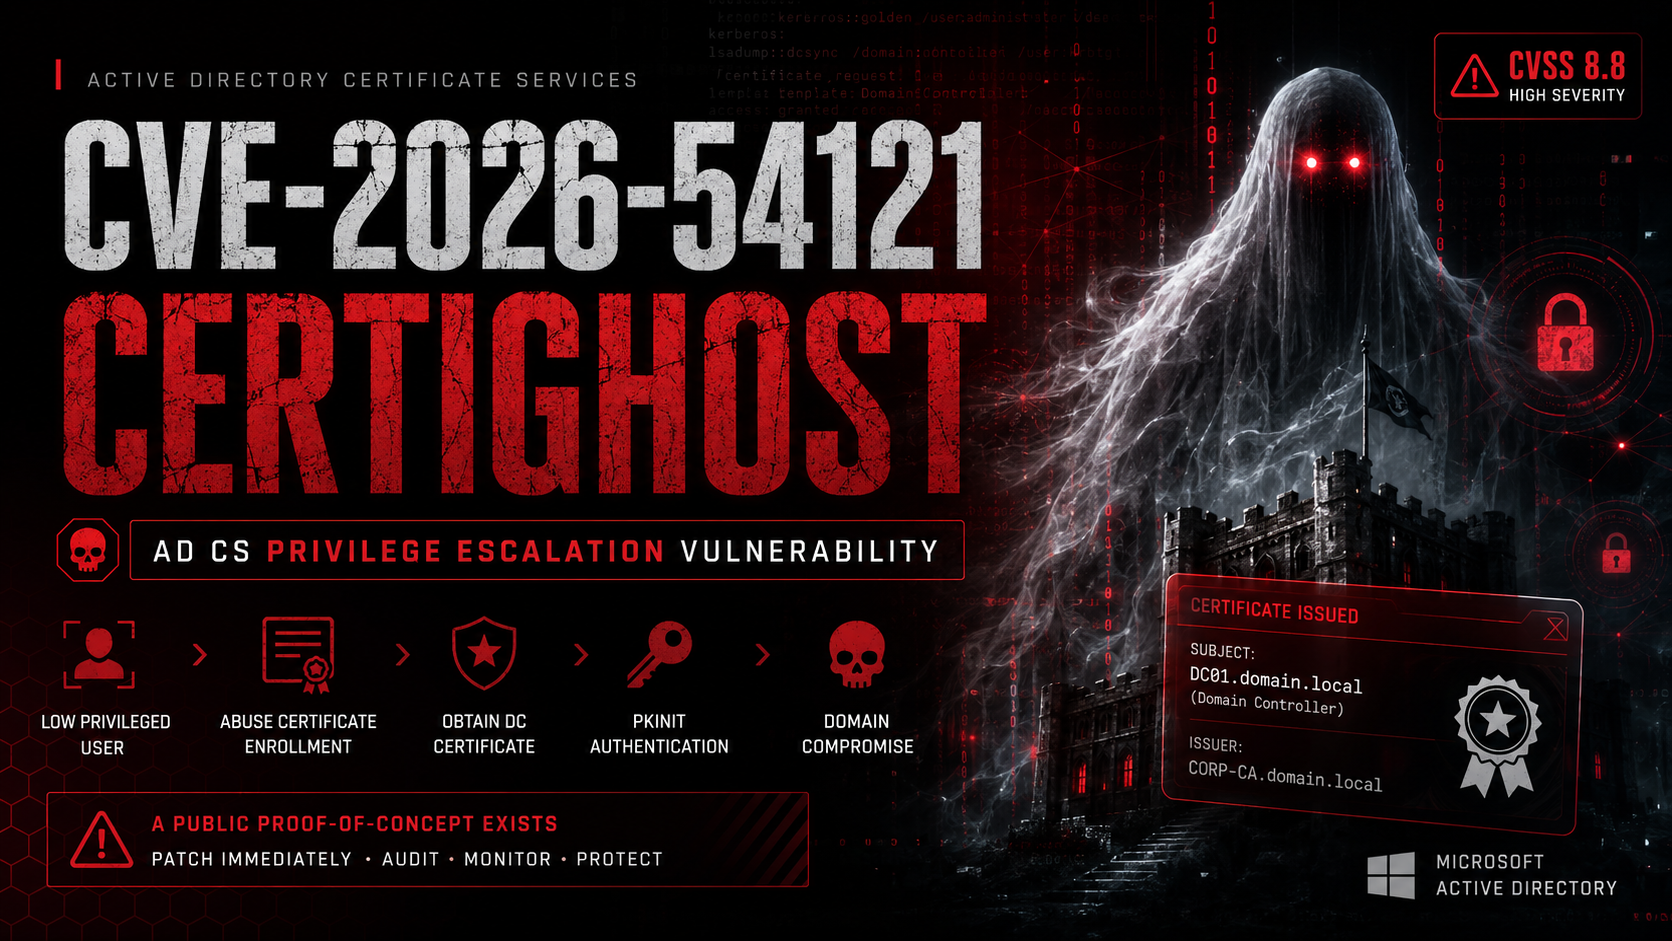 0xblackash/cve-2026-54121
CVE-2026-54121
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 davidcarliez/cve-2026-54992-poc
Proof of concept for CVE-2026-54992, an MSMQ remote-read integer overflow