
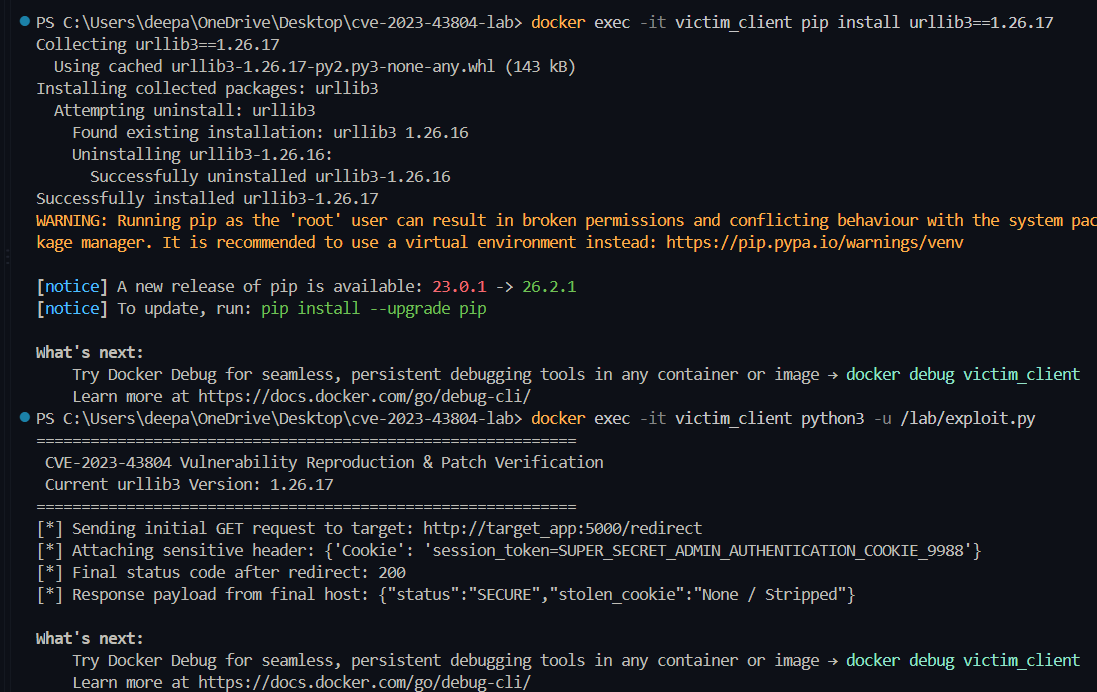
CVE-2023-43804
 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
container-securitydefensive-toolseducation+5
deepanshu-khurana/cve-2023-43804Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 eliot-code/cve-2026-52924
Technical analysis of CVE-2026-52924, a critical use-after-free in Linux kernel SCTP stale cookie handling, including root cause, attack flow, fix,…
 ghostpels/cve-2026-75865
Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC
 charanmv08/cve-2022-29117-assessment
CVE-2022-29117 (.NET Cookie-Handling DoS) Assessment, Understanding & Questions Framework
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 medaz-sploit/cve-2025-64714-privatebin-2.0.2-poc
Proof-of-concept exploit for PrivateBin Local File Inclusion (CVE-2025-64714) via template cookie path traversal, with detection and RCE chaining…
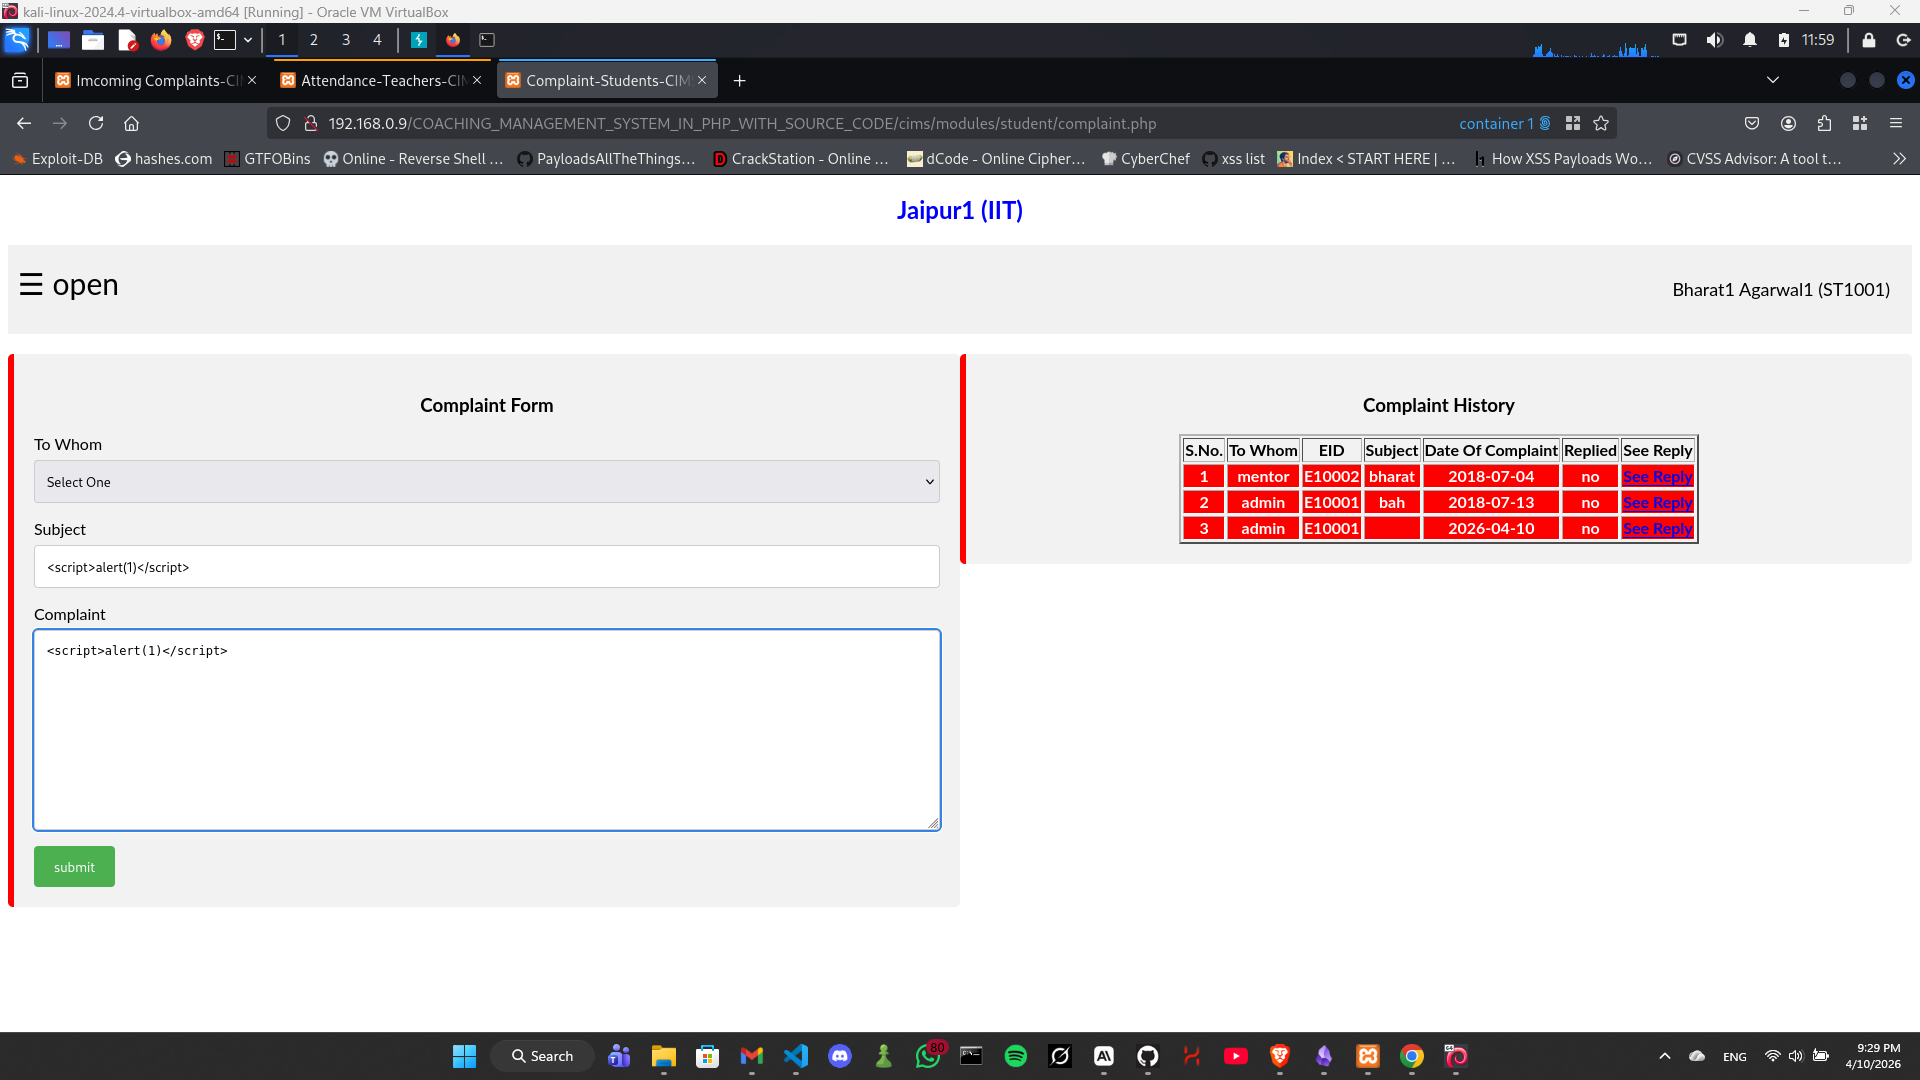 xmyronn/cve-2026-7222-xss
Proof-of-concept exploit for stored XSS (CWE-79) in a PHP coaching management system, demonstrating session hijacking and privilege escalation from…
 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 vigilante-1337/cve-2024-11635
The WordPress File Upload plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 4.24.12 via the…
 cavi-au/consent-o-matic
Browser extension that automatically fills out cookie popups based on your preferences
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
 kn0x0x/cve-2025-32756-poc
Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products.
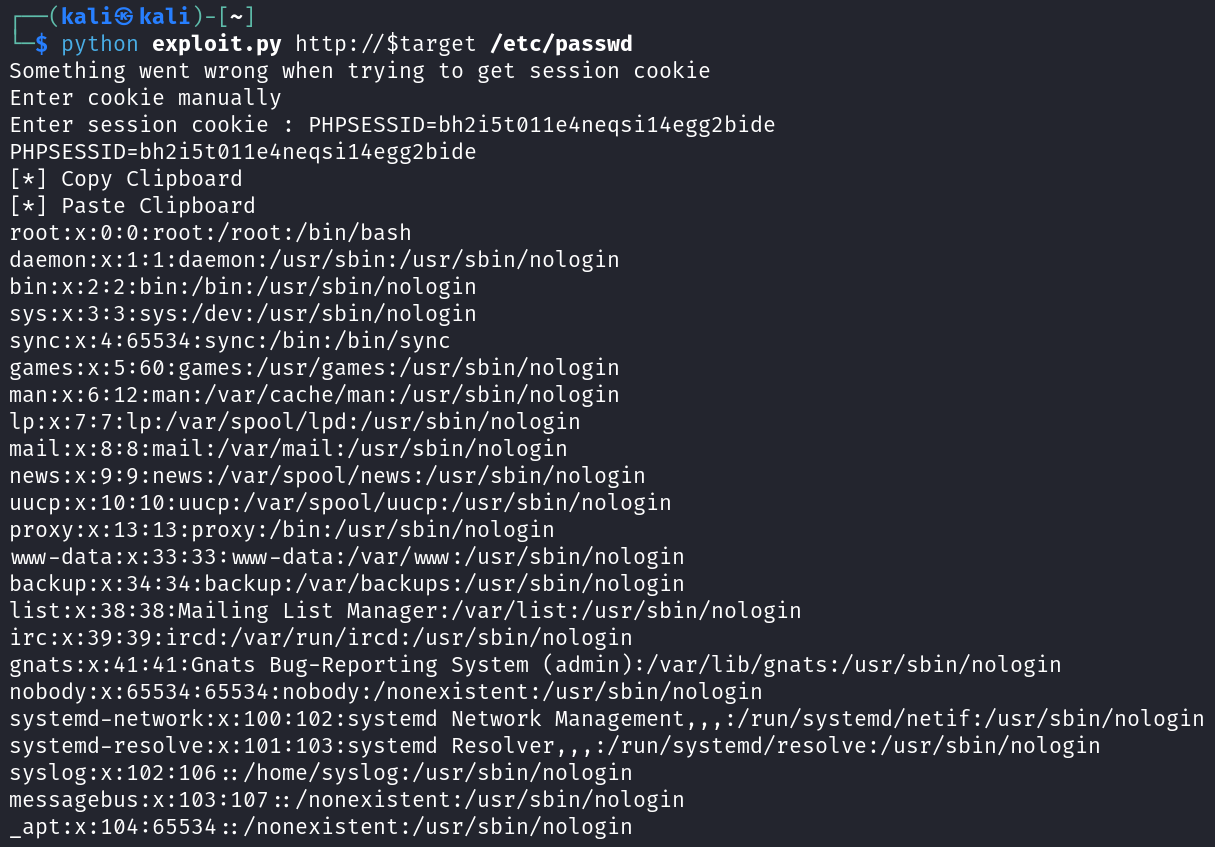 cyberquestor-infosec/cve-2022-46604-responsive-file-manager
Educational exploit for CVE-2022-46604 directory traversal in Responsive File Manager v9.13.4. Includes a modified Python script with automatic…
 alm6no5/cve-2025-32756-poc
Proof-of-concept exploit for a critical stack-based buffer overflow in Fortinet products, enabling unauthenticated remote code execution via the…
 yugo-eliatrope/test-cve-2025-29927
Demo app to exploit CVE-2025-29927: NextJS middleware bypass via proxy-injected headers for unauthorized /admin access. Includes vulnerable app and…