

recurse
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
295
recurse-labs/recurseAgentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 shinycolumn/cve-2025-56802
AES-CFB Key Generation and Management Vulnerability in Reolink Desktop Application
 shinycolumn/cve-2025-56801
AES-CFB IV Generation Vulnerability in Reolink Desktop Application
 mrk336/inside-cve-2026-20805-how-a-windows-dwm-flaw-exposed-sensitive-data
CVE‑2026‑20805: A Windows Desktop Window Manager flaw causing local information disclosure. Requires low privileges, no user interaction. Rated CVSS…
 alpinine/cve-2026-1312-testing
Reproduction environment for CVE-2026-1312 with Docker-based setup and automated execution script for vulnerability testing and analysis.
 thecybergeek/cve-2026-3888-snap-confine-systemd-tmpfiles-lpe
Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…
 fevar54/cve-2026-20805-poc
PoC de CVE-2026-20805: divulgacion de informacion en Desktop Window Manager (dwm.exe) de Windows.
 whenx/cve-2026-0776
Security research and proof-of-concept for CVE-2026-0776 affecting Discord Desktop Client.
 metnew/write-ups
Curated collection of technical write-ups detailing RCE vulnerabilities in GitHub Desktop, GitHub CLI, and Claude Code, with CVE references and…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
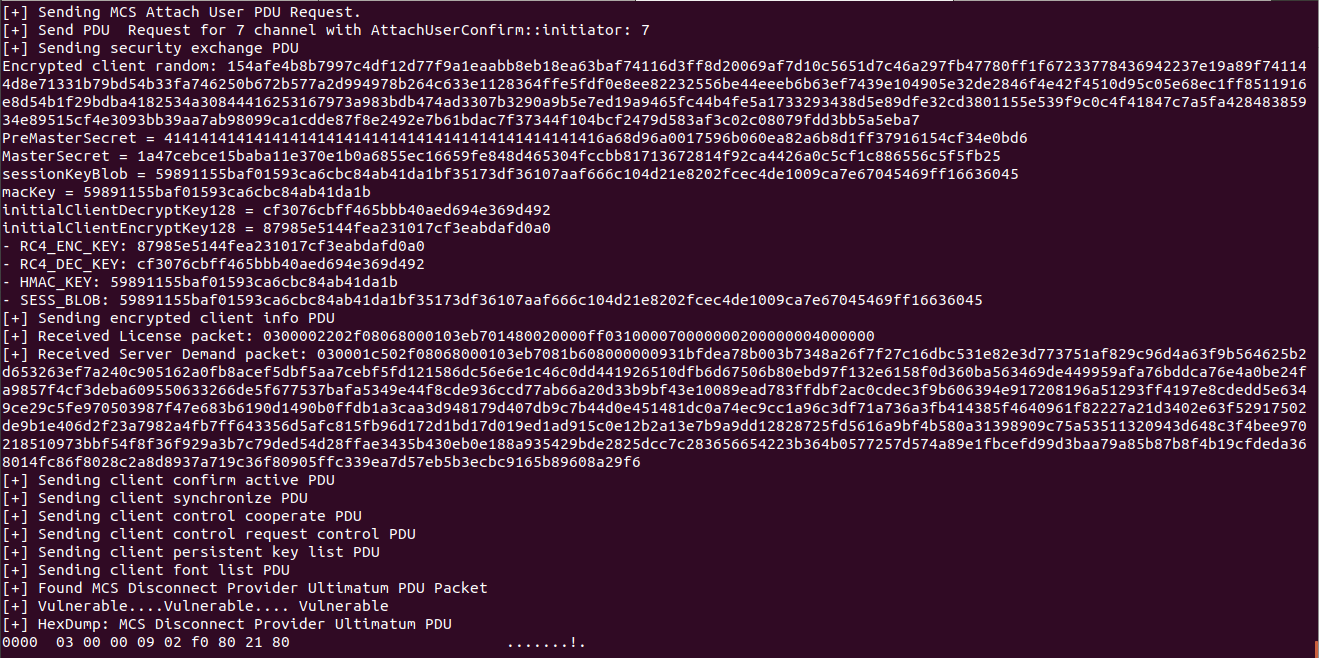 umarfarook882/cve-2019-0708
CVE-2019-0708 - BlueKeep (RDP)
 gopeshkachhadiya/windows-2
A hands-on Windows 7 lab designed to demonstrate the real-world impact of the BlueKeep (CVE-2019-0708) vulnerability through practical exploitation…
 thawkhant/viber-desktop-html-injection
Public writeup for CVE-2025-55996 (Viber Desktop HTML Injection)
 rootdirective-sec/cve-2026-55255-lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 rootdirective-sec/cve-2026-42647-lab
Docker-based lab for reproducing CVE-2026-42647, an unauthenticated time-based blind SQL injection in the JoomSport WordPress plugin via the sortf…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application