Windows-Kernel-Exploitation

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Lord Of Active Directory - automatic vulnerable active directory on AWS

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250

Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943

proof of concept for CVE-2020-0601

This exploit is based on CVE-2023-26360 (https://nvd.nist.gov/vuln/detail/CVE-2023-26360) and was built on top of the Metasploit module and the…

Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.

This is a PoC for the CVE-2025-24813 and tested in different environments.

End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis

Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

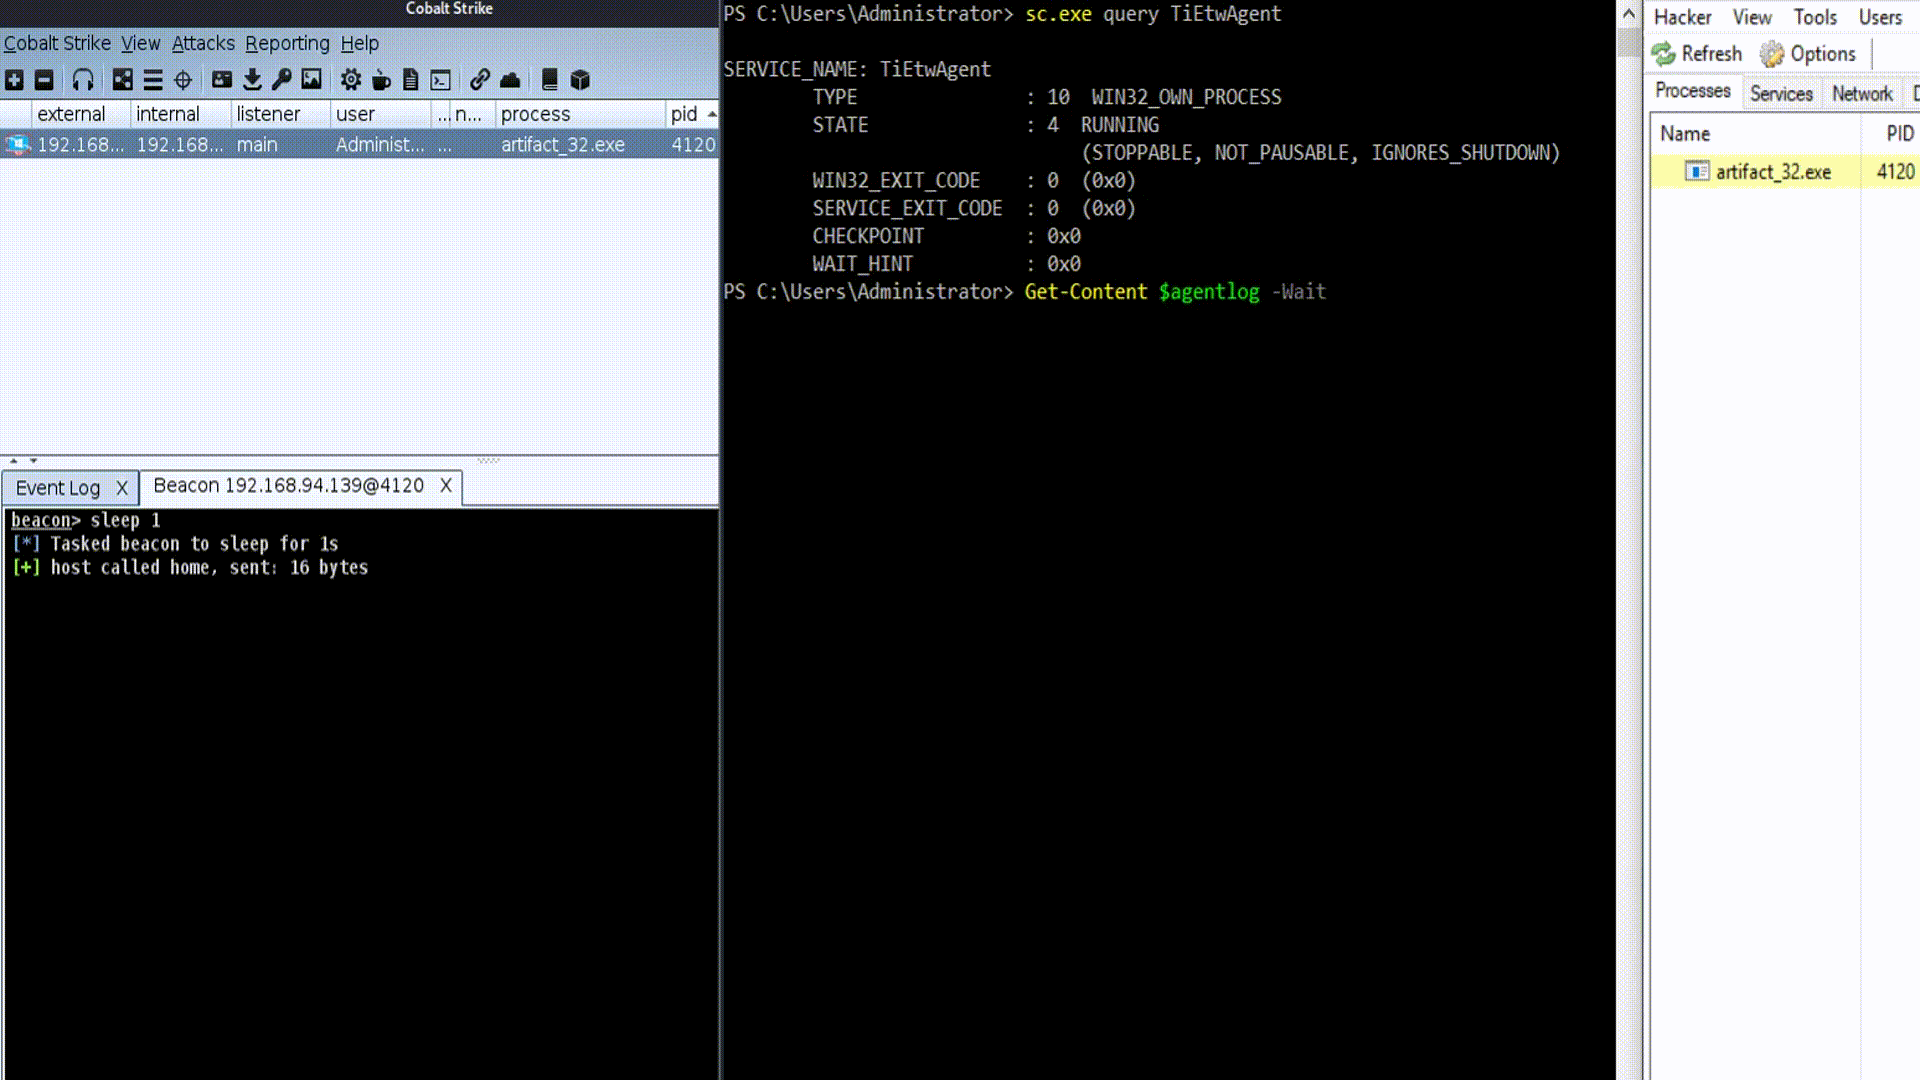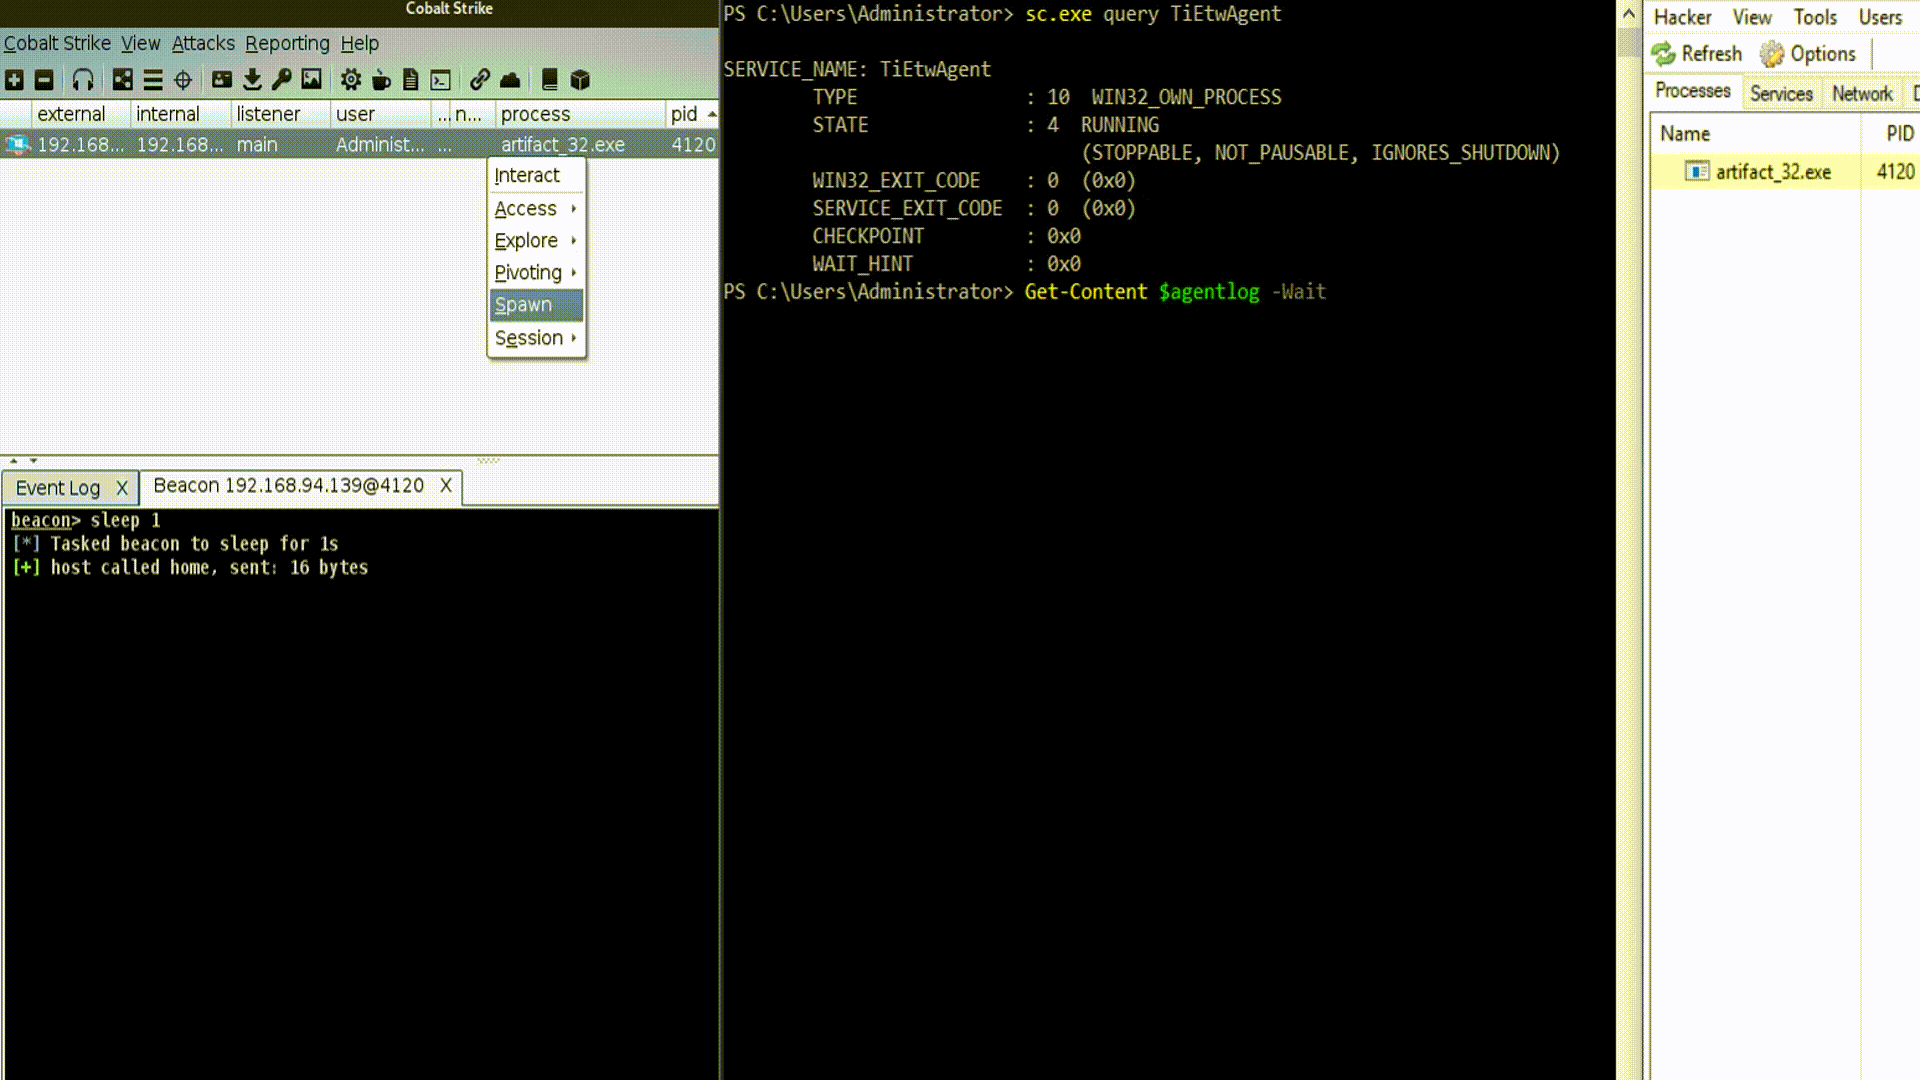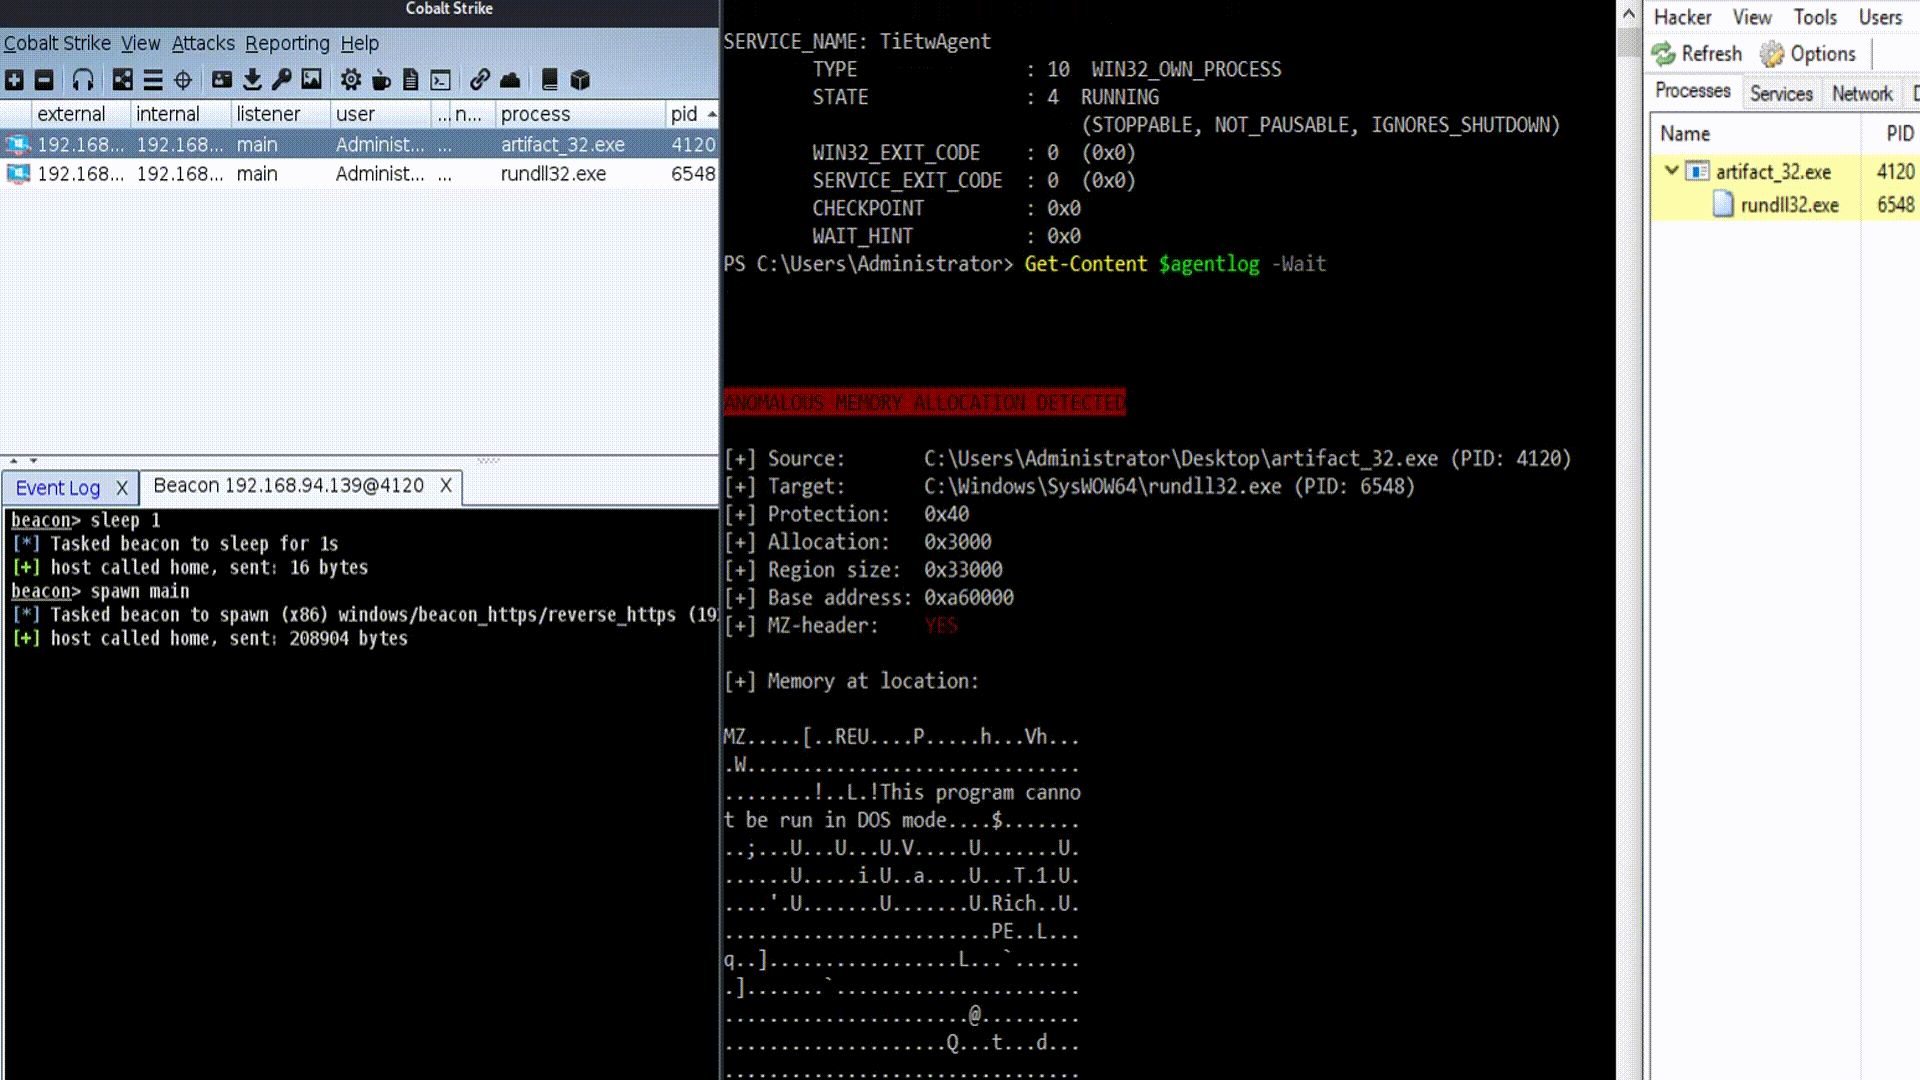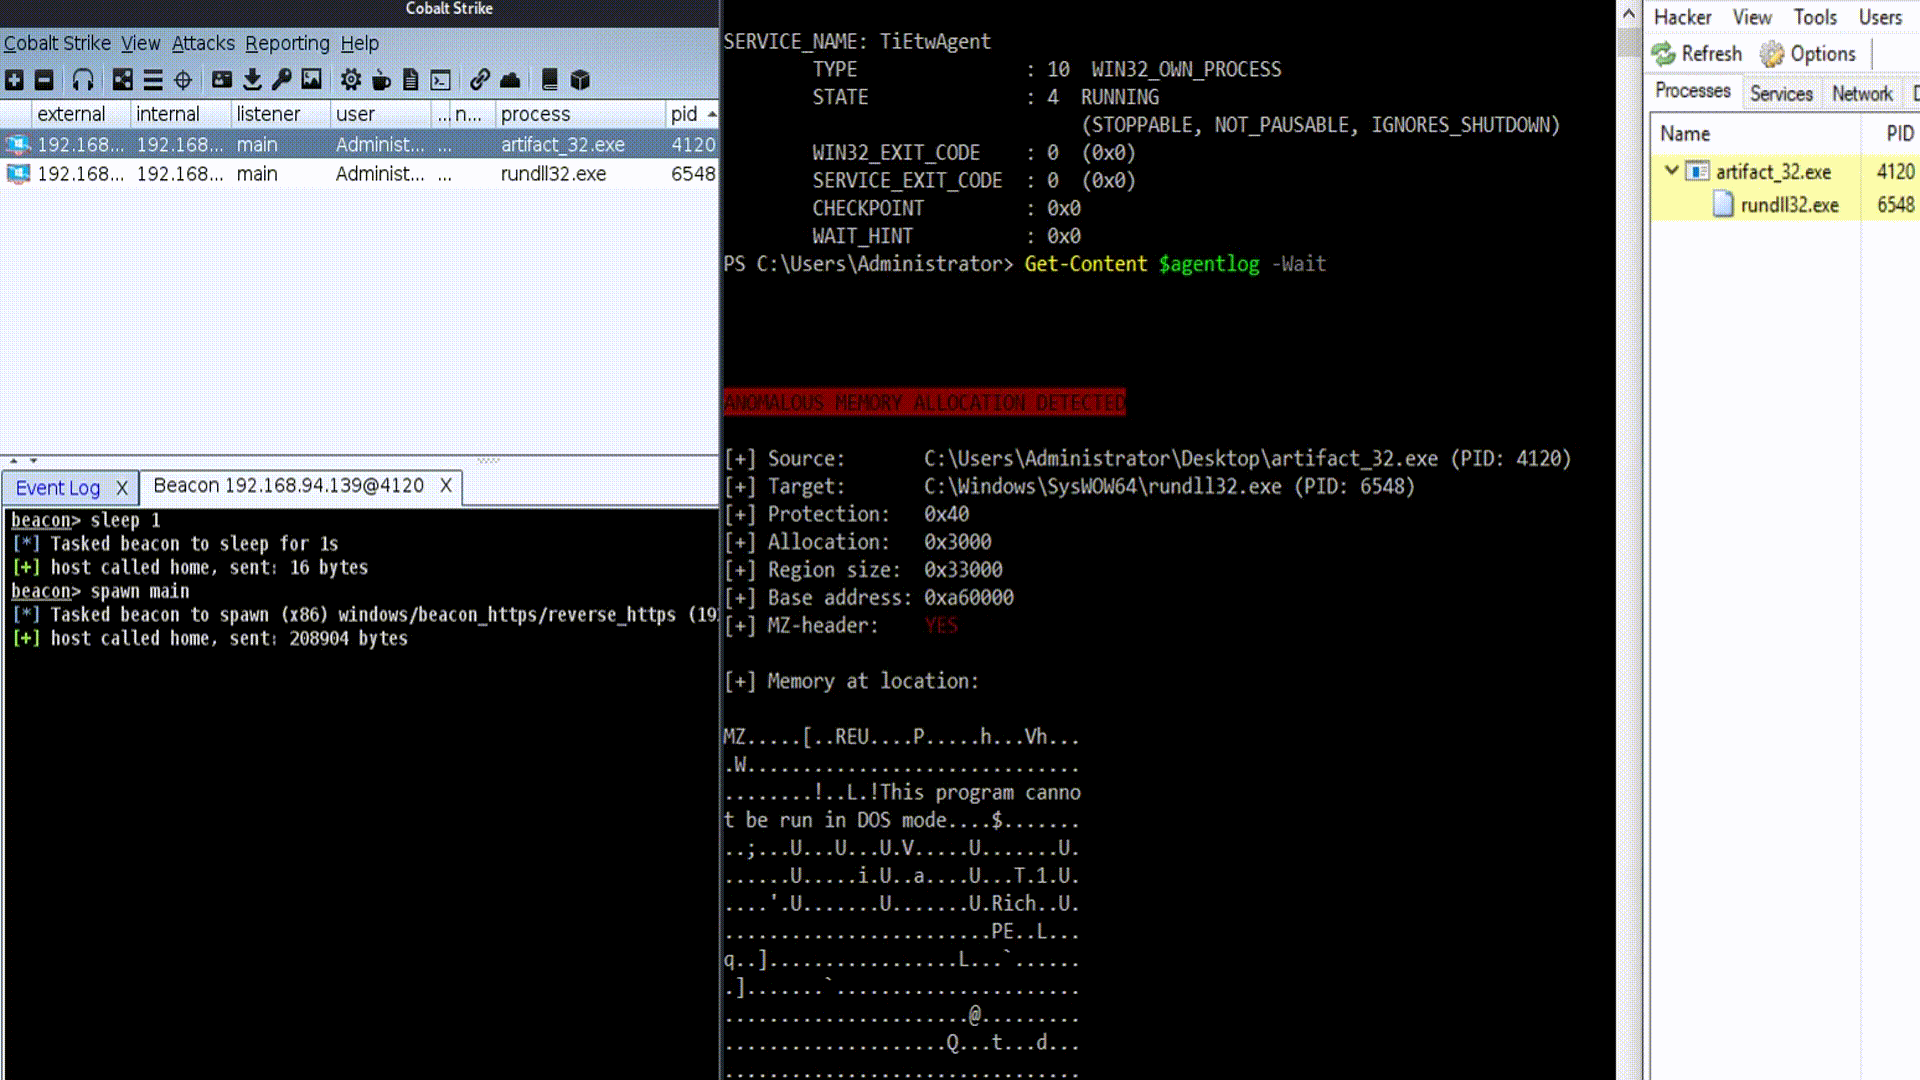
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes

Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…

PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…