Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
binary-analysiscommand-and-controleducation+6
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

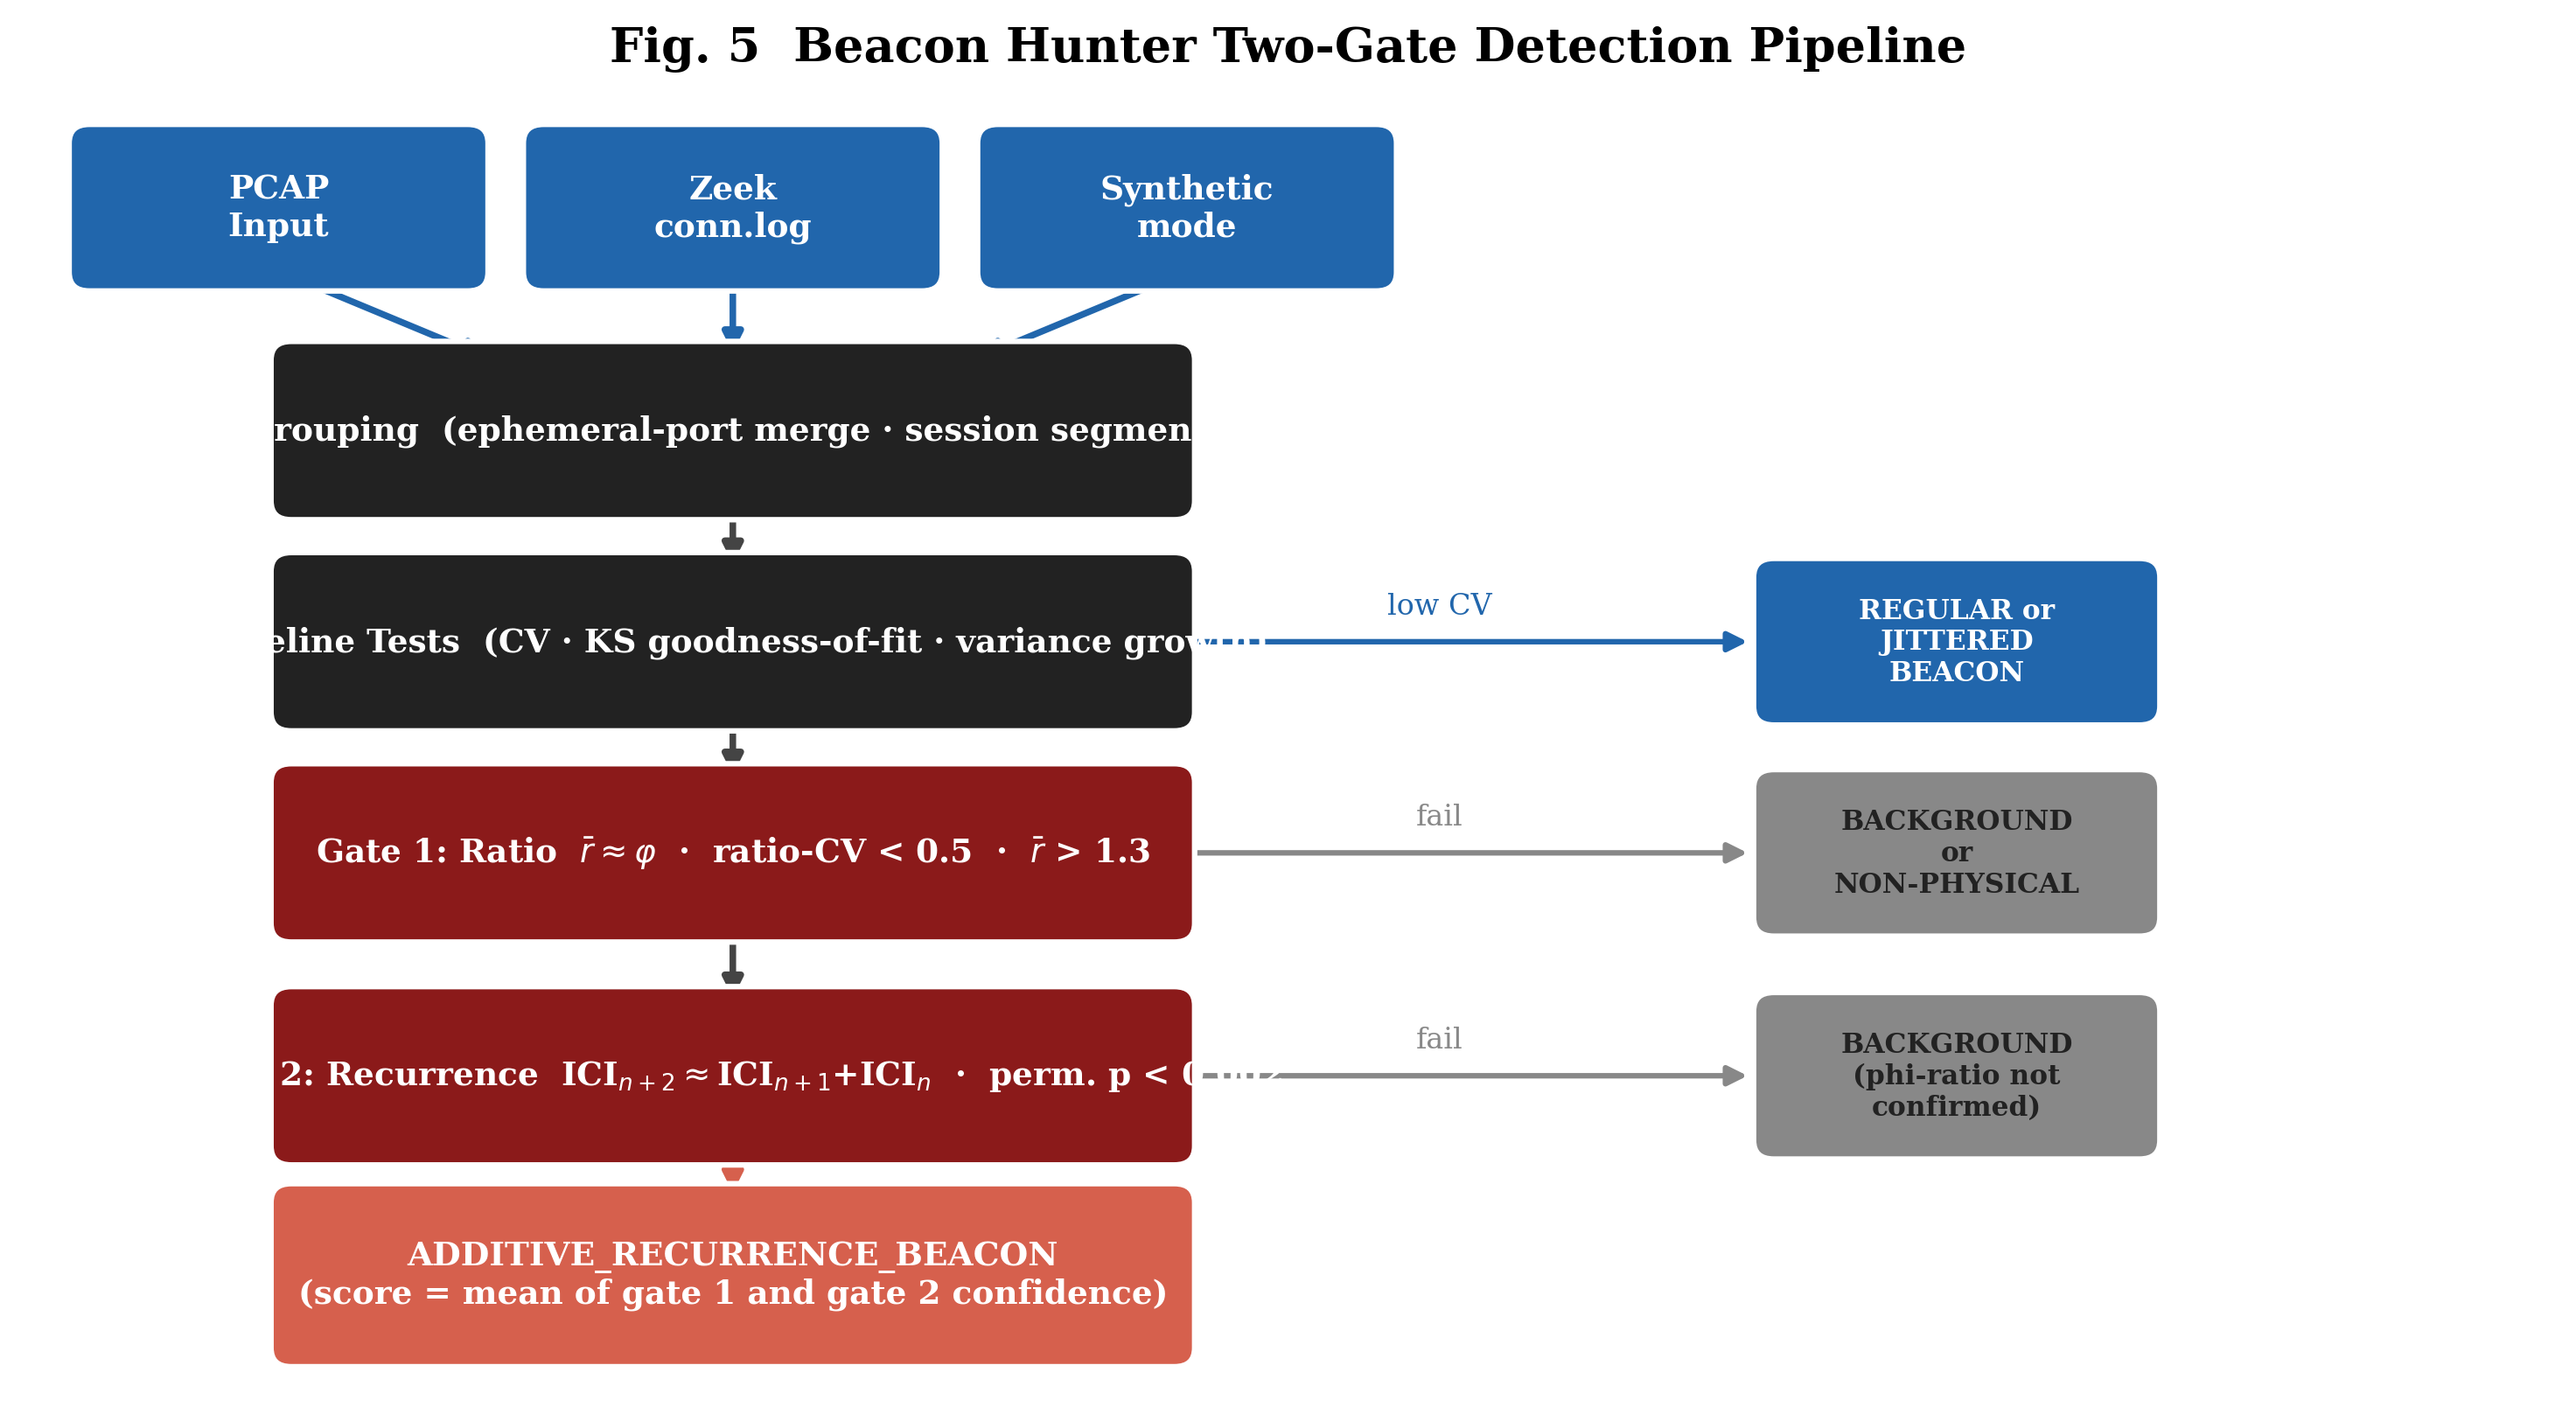
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors

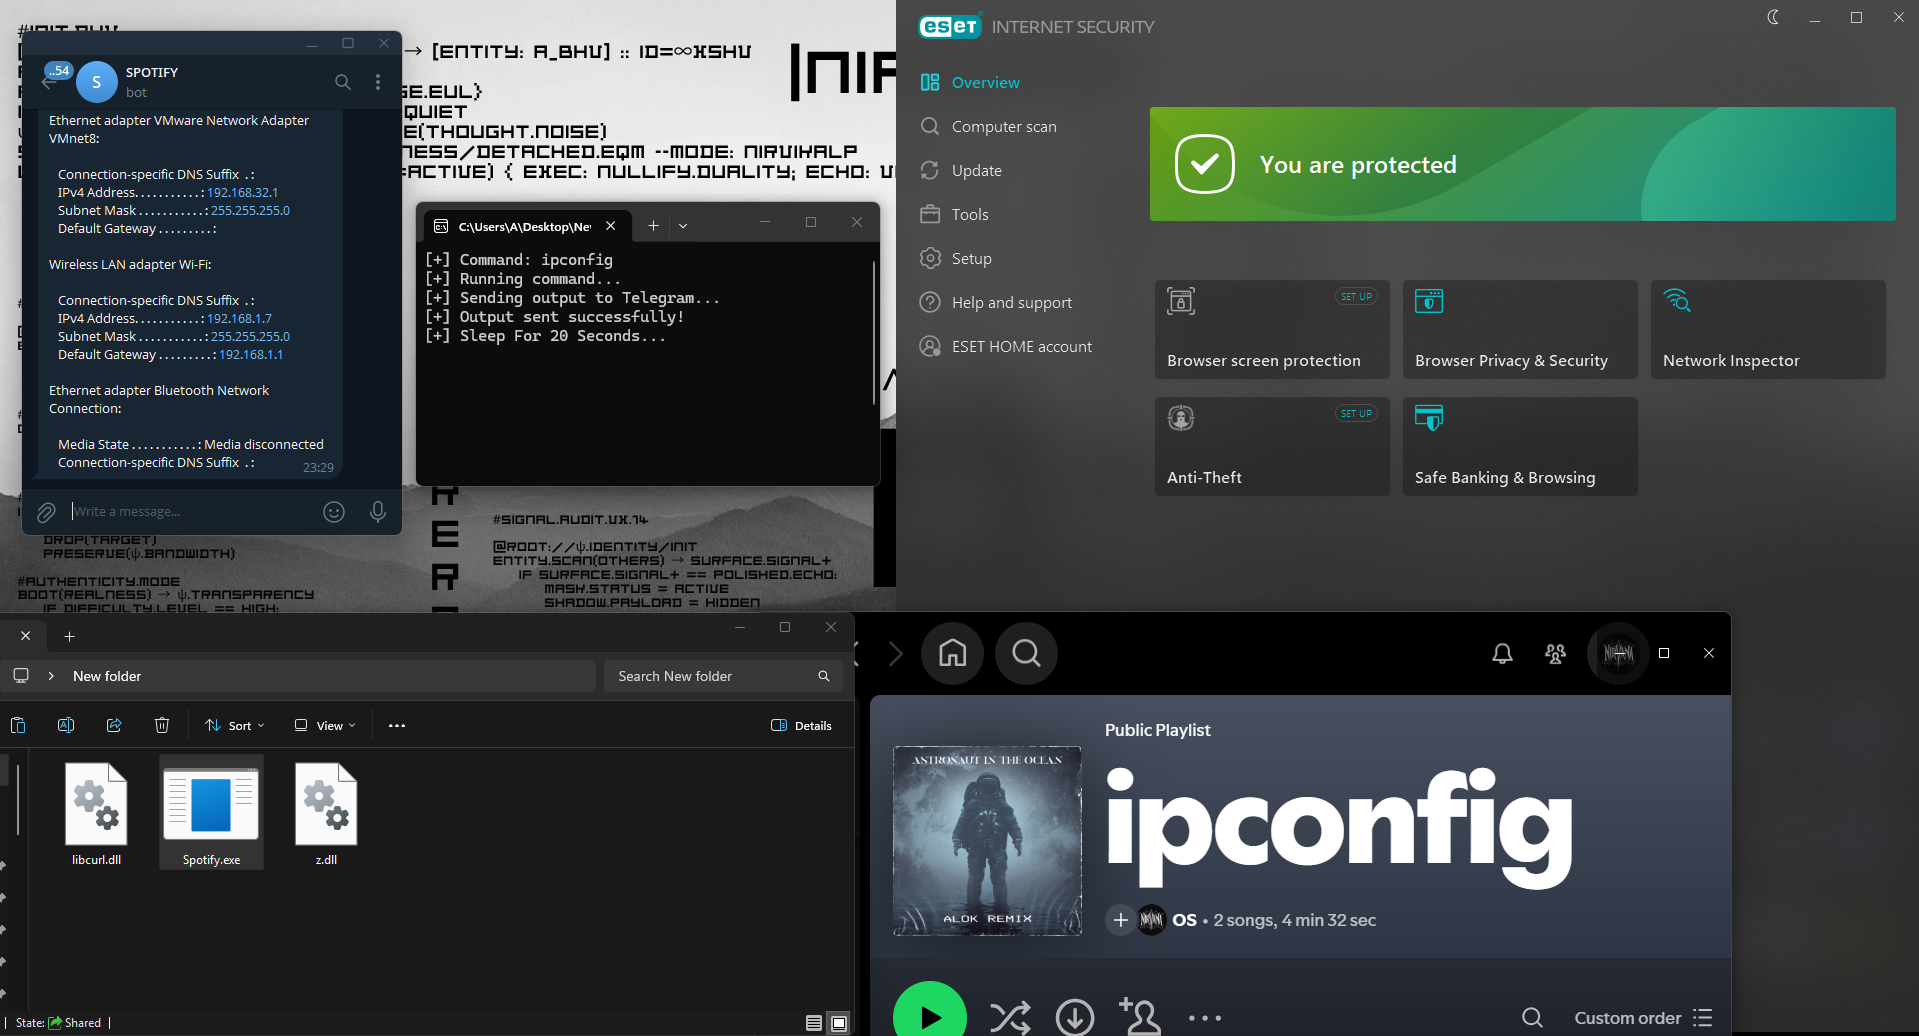
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…

Collection of beacon BOF written to learn windows and cobaltstrike